
lxancephisher
 lxance-hacker/lxancephisher
Automated phishing simulation tool with 30+ login page templates, URL masking, and multiple tunneling options (Ngrok, Cloudflared, Serveo) for…
educationphishingphishing-tools+1
29
lxance-hacker/lxancephisherAutomated phishing simulation tool with 30+ login page templates, URL masking, and multiple tunneling options (Ngrok, Cloudflared, Serveo) for…
 hacksider/deep-live-cam
real time face swap and one-click video deepfake with only a single image
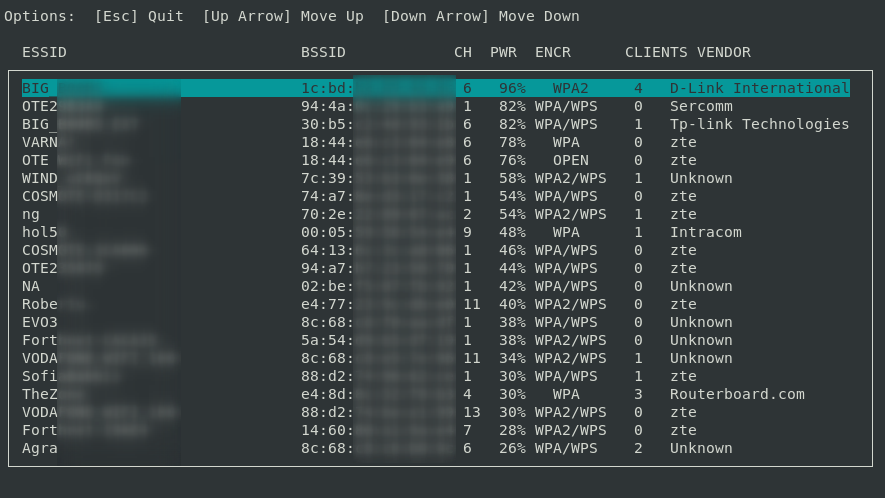 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
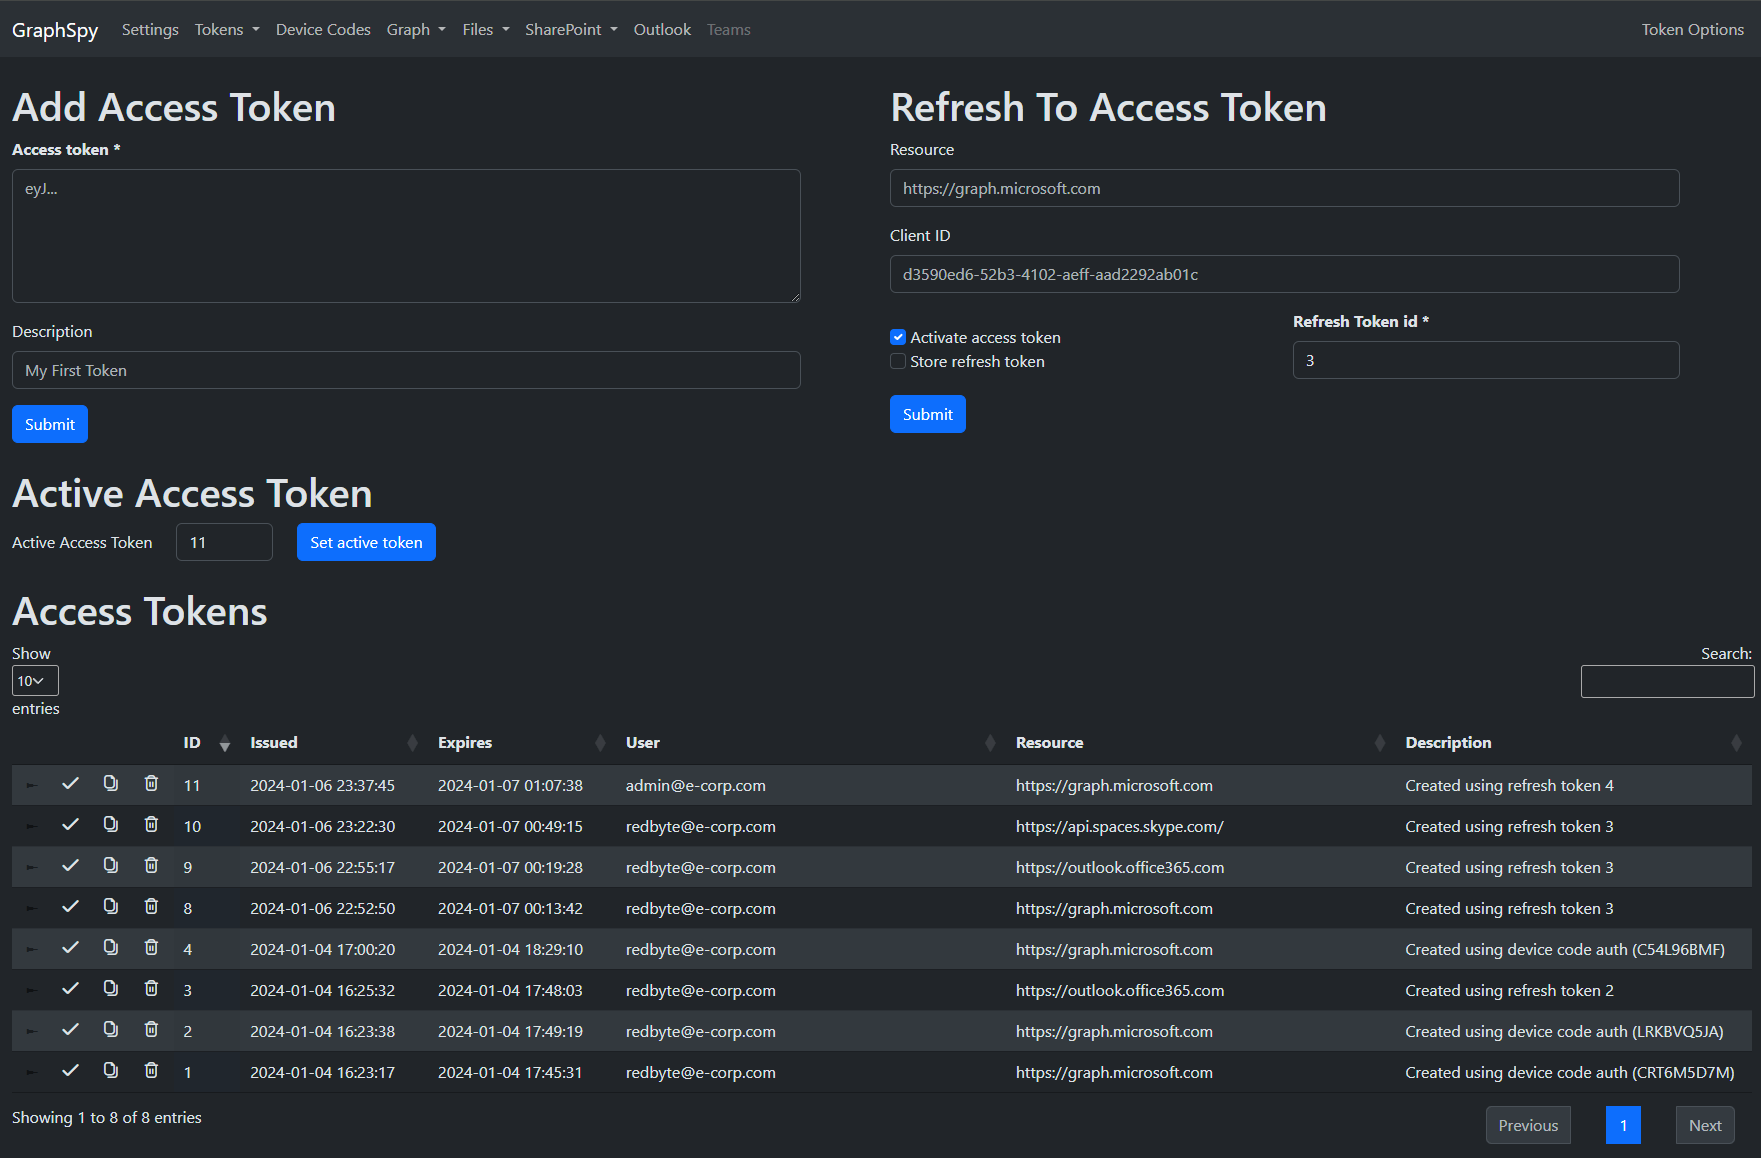 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 simplerhacking/evilginx3-phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…
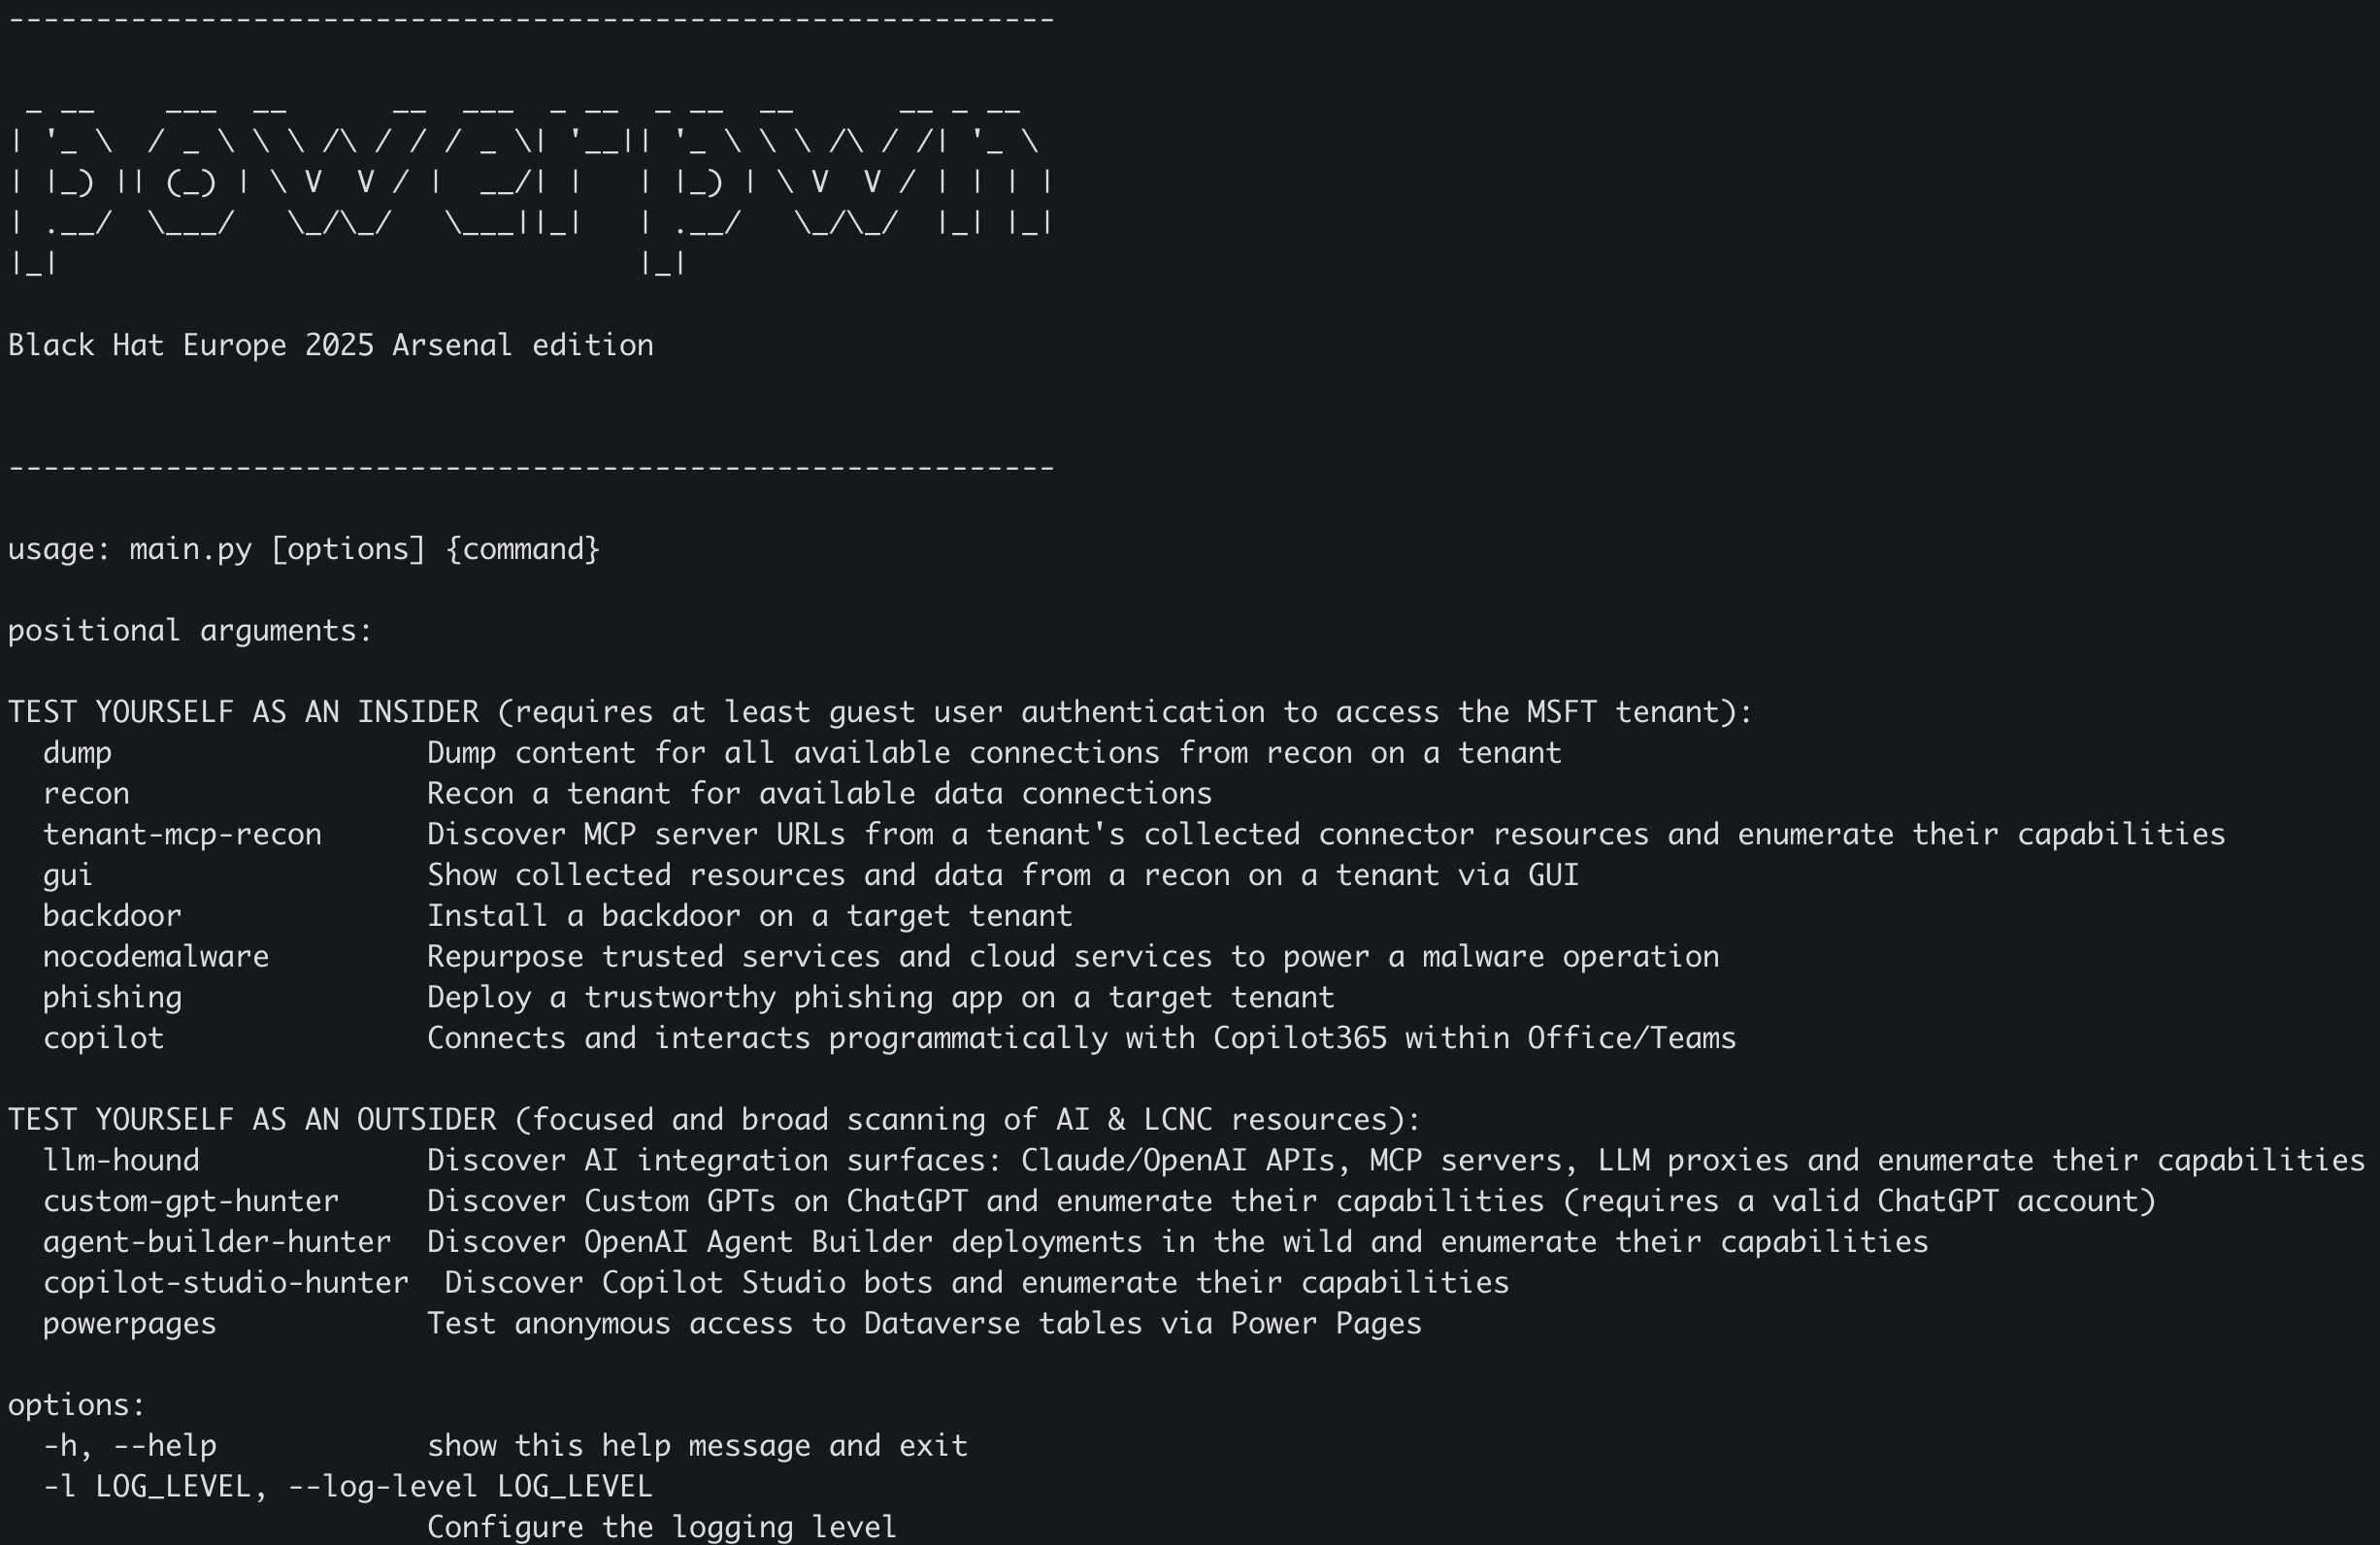 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 mrprogrammer2938/black-tool
Install the tools and start Attacking , black-tool v5.5.5 ! ⬛
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
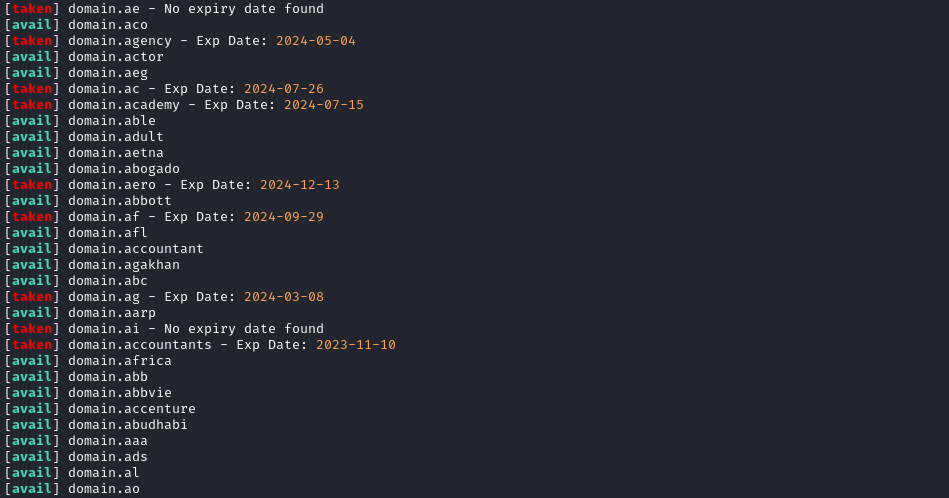 yuyudhn/tldhunt
Bash-based domain availability checker that scans WHOIS records across multiple TLDs to find unregistered domains for red teaming and phishing…
 wavvs/doctrack
Tool to manipulate and weaponize Office Open XML documents.
 makdosx/wifi-agent
Rogue access point tool for creating captive portals, phishing credentials via cloned login pages, and injecting malware downloads for educational…
 cisc0-gif/kitt
Python-Based Pentesting Framework
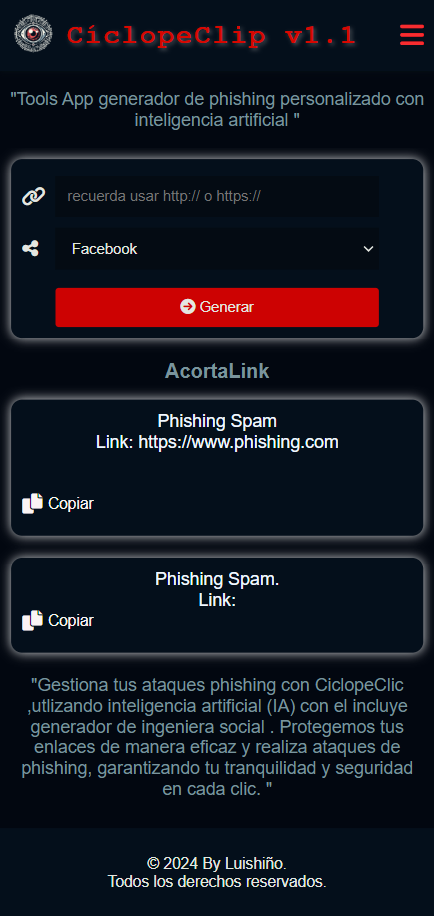 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…