EvilSelenium
 mrd0x/evilselenium
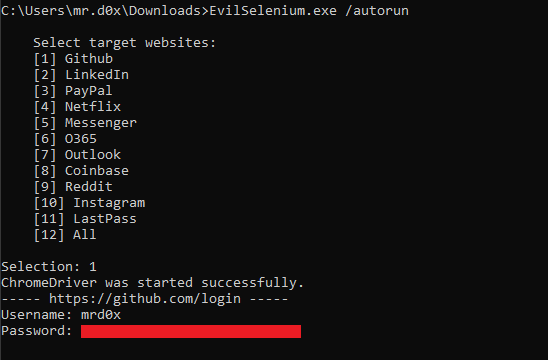
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
data-exfiltrationinformation-gatheringphishing-tools+3
608
mrd0x/evilseleniumWeaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
 puliczek/cve-2021-21123-poc-google-chrome
🐱💻 👍 Google Chrome - File System Access API - vulnerabilities reported by Maciej Pulikowski | Total Bug Bounty Reward: $5.000 | CVE-2021-21123…
 jasmoon99/embedded-pdf
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 omarothmann/embedded-backdoor-connection
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 cscli/cve-2017-5223
Proof-of-concept exploit for CVE-2017-5223 demonstrating arbitrary file read via PHPMailer's attachment and email content injection.
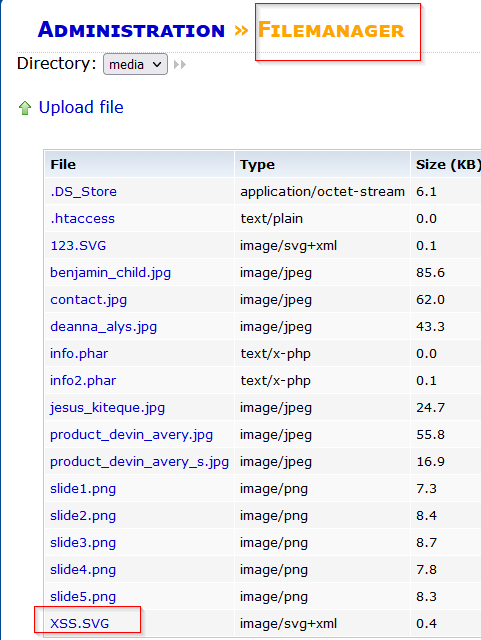 sromanhu/cve-2023-44767_ritecms-file-upload--xss---filemanager
RiteCMS 3.0 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will…
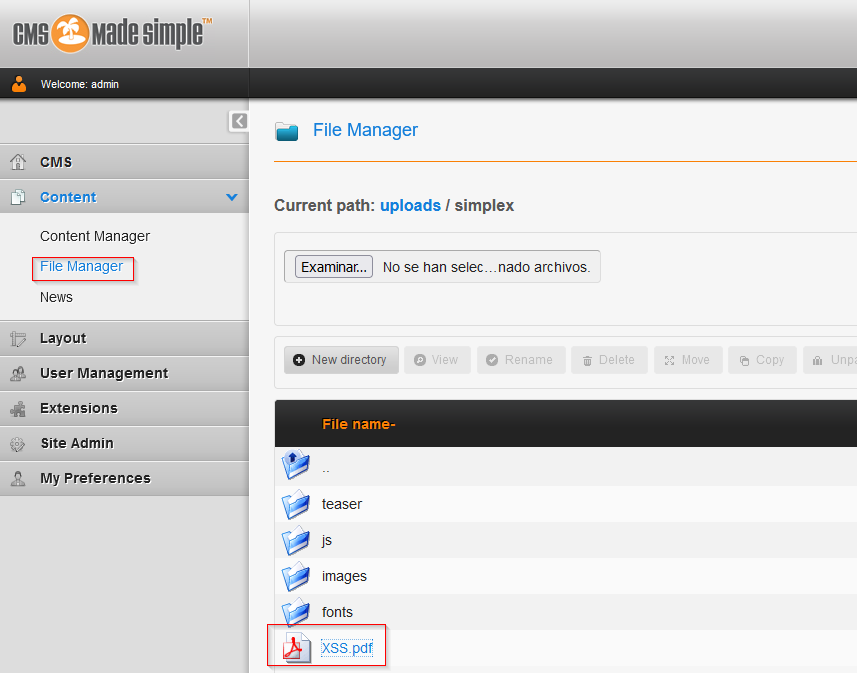 sromanhu/cve-2023-43872-cmsmadesimple-arbitrary-file-upload--xss---file-manager
CMSmadesimple 2.2.18 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed…
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
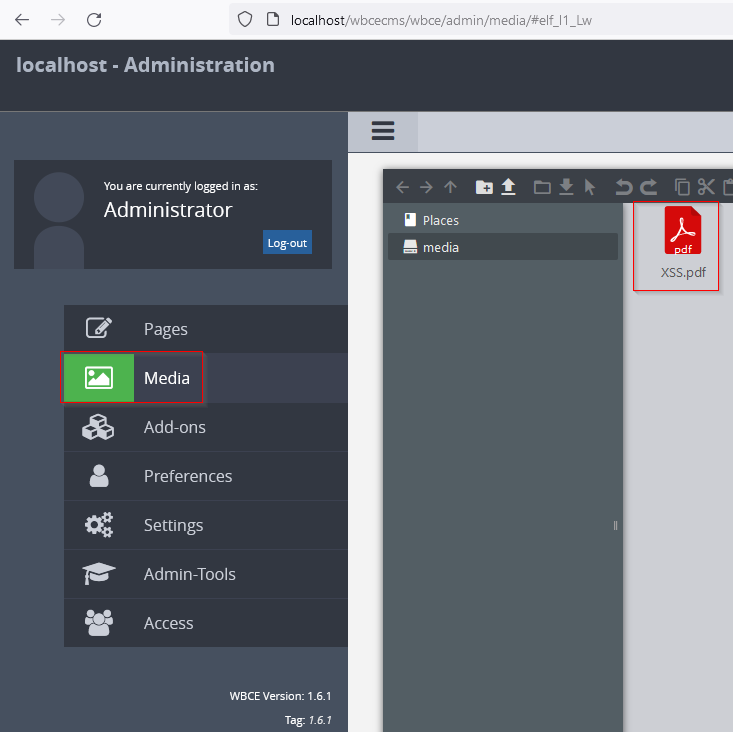 sromanhu/cve-2023-43871-wbce-arbitrary-file-upload--xss---media
WBCE 1.6.1 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will launch…
 beefproject/beef
The Browser Exploitation Framework Project
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 kaihaochen04/monikerlinktest
cve-2024-21413
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC