
CVE-2021-43032
 sakurasamuraii/cve-2021-43032
Post authenticated stored-xss in XenForo versions ≤ 2.2.7
exploitationpenetration-testingphishing-tools+3
2
sakurasamuraii/cve-2021-43032Post authenticated stored-xss in XenForo versions ≤ 2.2.7
 catatonicprime/cve-2020-3580
Additional exploits for XSS in Cisco ASA devices discovered by PTSwarm
 the-girl-who-lived/cve-2020-25498
Stored XSS via CSRF in Beetel 777VR1 Router
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 s1lkys/cve-2021-40101
Survey XSS combined with CSRF leads to Admin Account Takeover in Concrete5 8.5.4
 zumiyumi/cve-2024-50677
This repository presents a proof-of-concept of CVE-2024-50677
 ayato-shitomi/cve-2024-46278-teedy_1.11_account-takeover
【Teedy 1.11】Account Takeover via XSS
 oscarakaelvis/cve-2018-8062
Persistent XSS on Comtrend AR-5387un router
 minotauro2020/cve-2023-40869
Cross Site Scripting vulnerability in mooSocial mooSocial Software v.3.1.6 allows a remote attacker to execute arbitrary code via a crafted script to…
 openxp-research/cve-2022-2546
All-in-One WP Migration < 7.63 - Unauthenticated Reflected XSS + CSRF
 0pts/cve-2023-0214
Secure Web Gateway 10.2.11 - Cross-Site Scripting (XSS)
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
 b0marek/cve-2023-4549
Repository for CVE-2023-4549 vulnerability.
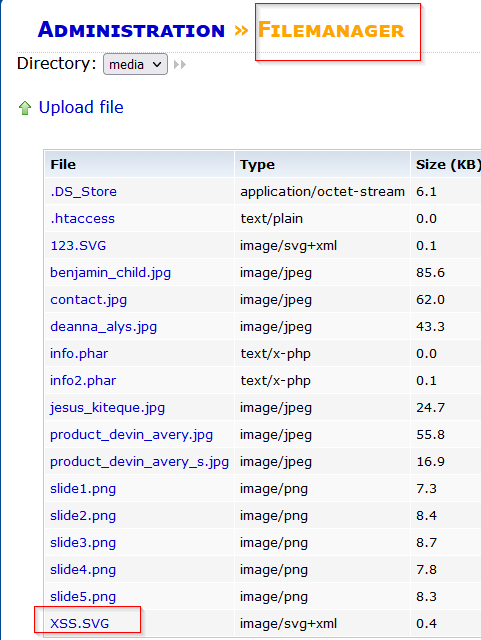 sromanhu/cve-2023-44767_ritecms-file-upload--xss---filemanager
RiteCMS 3.0 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing