
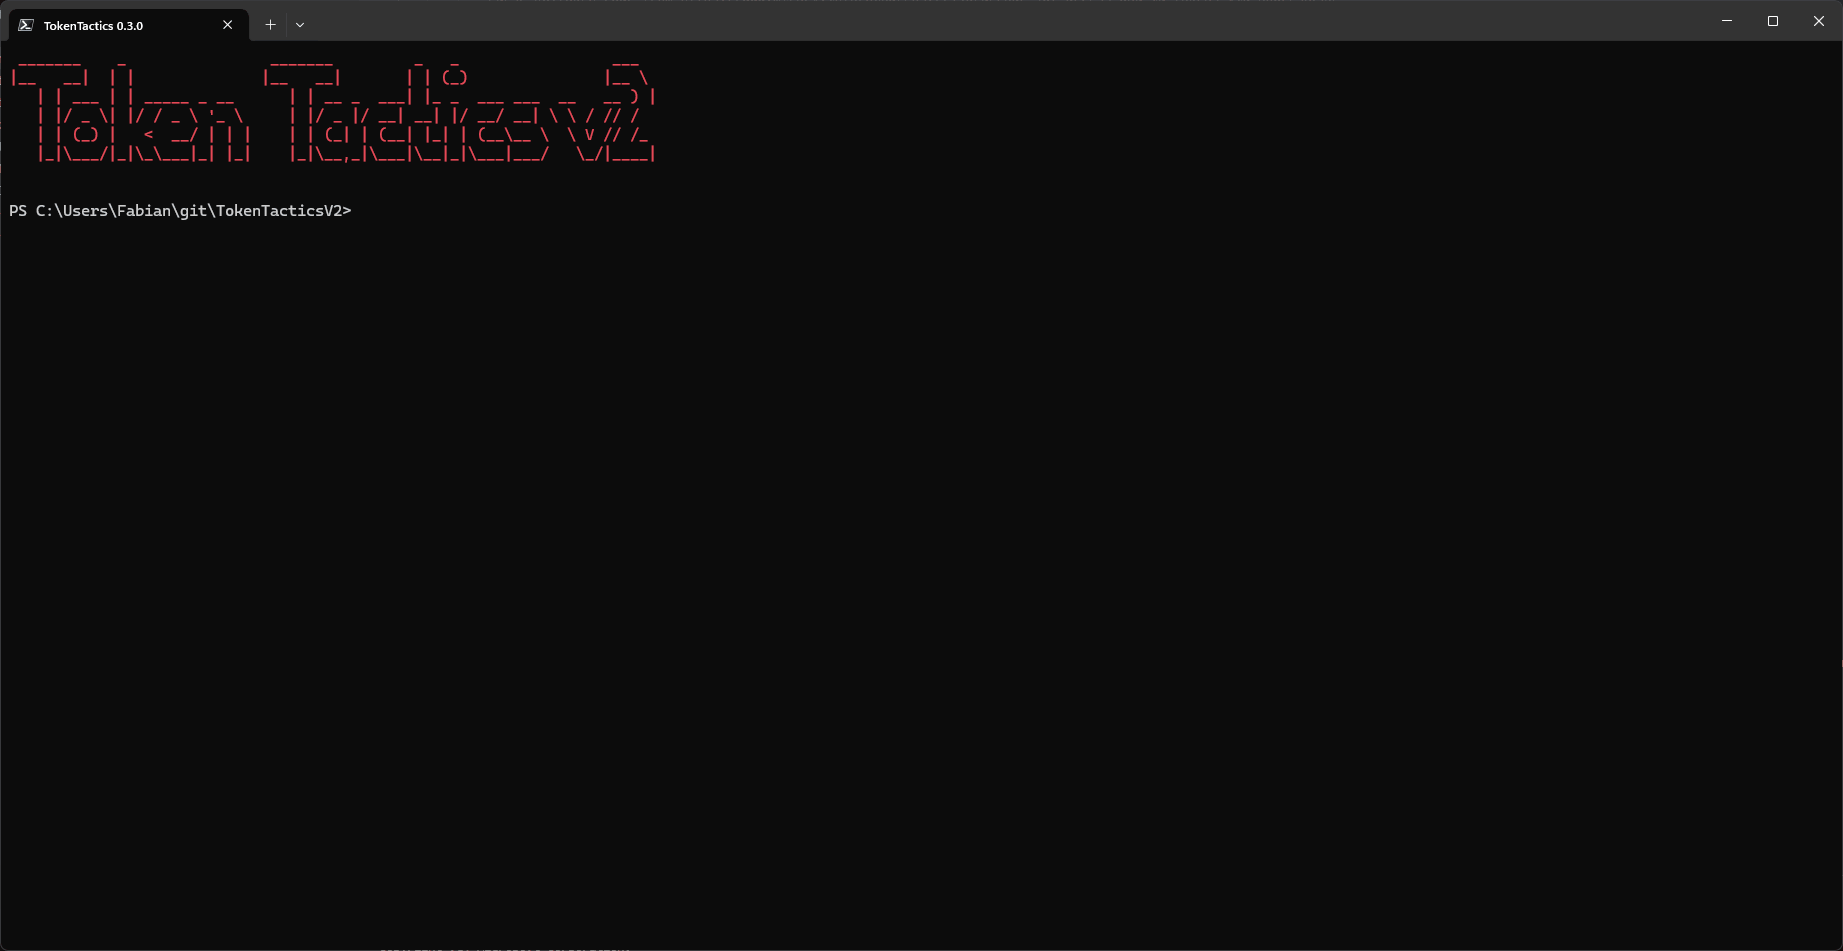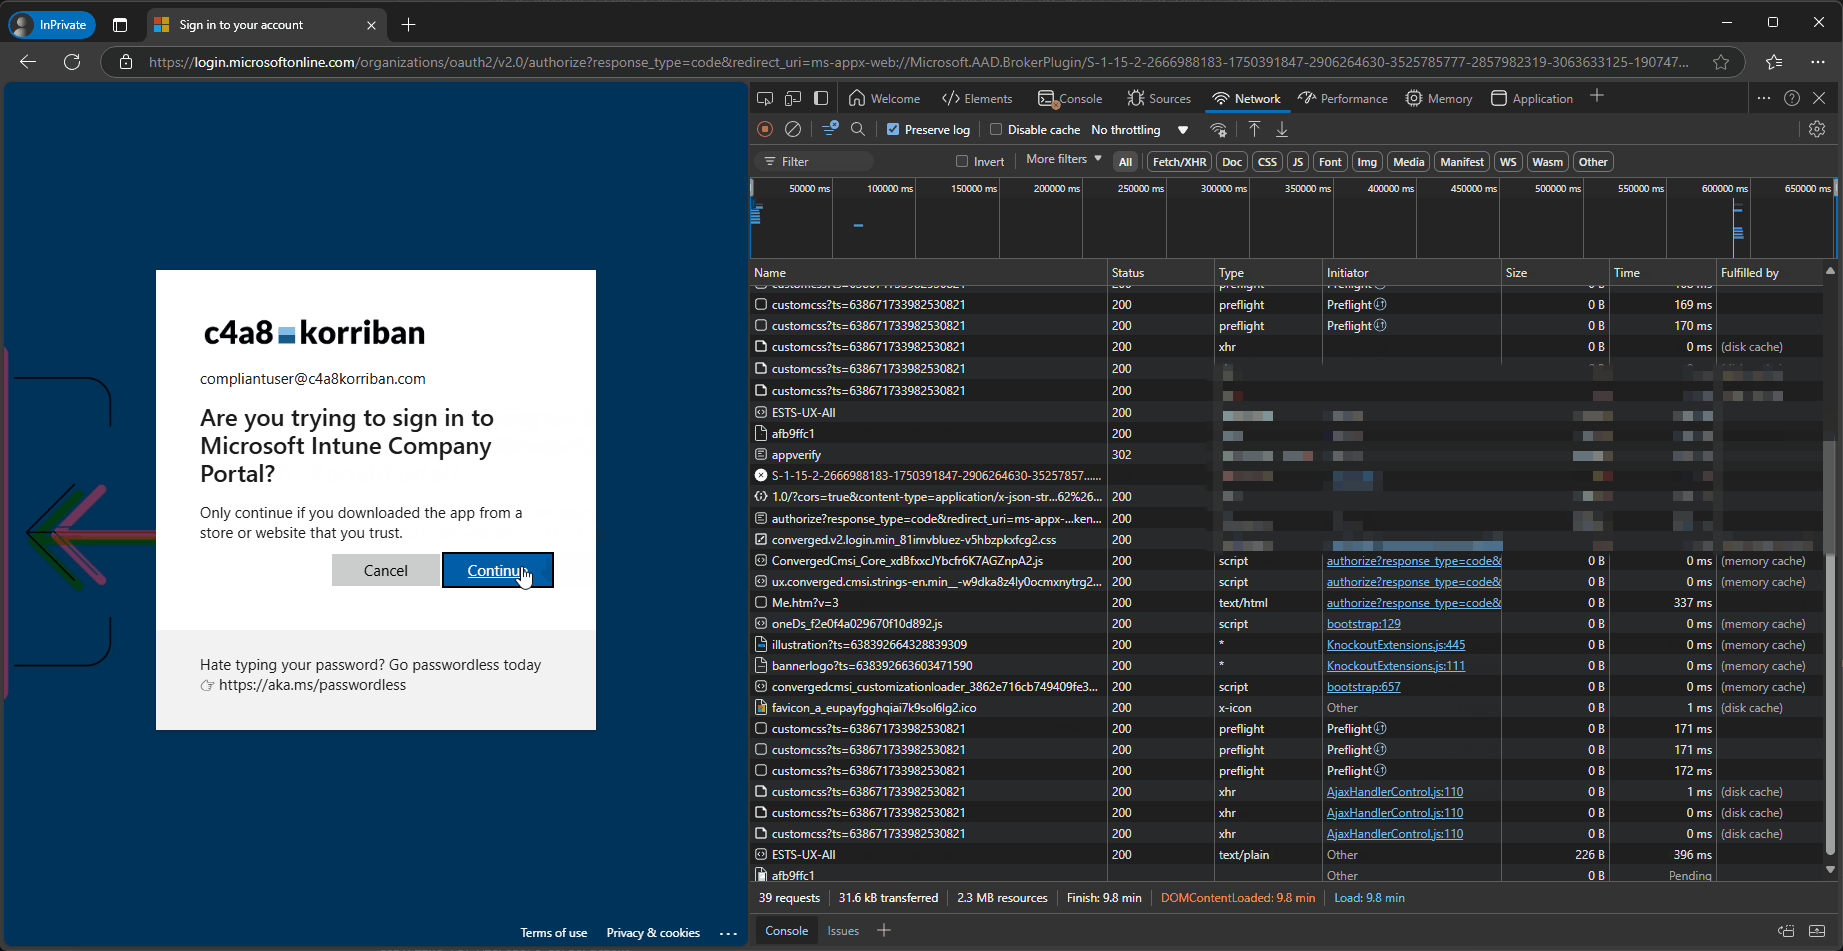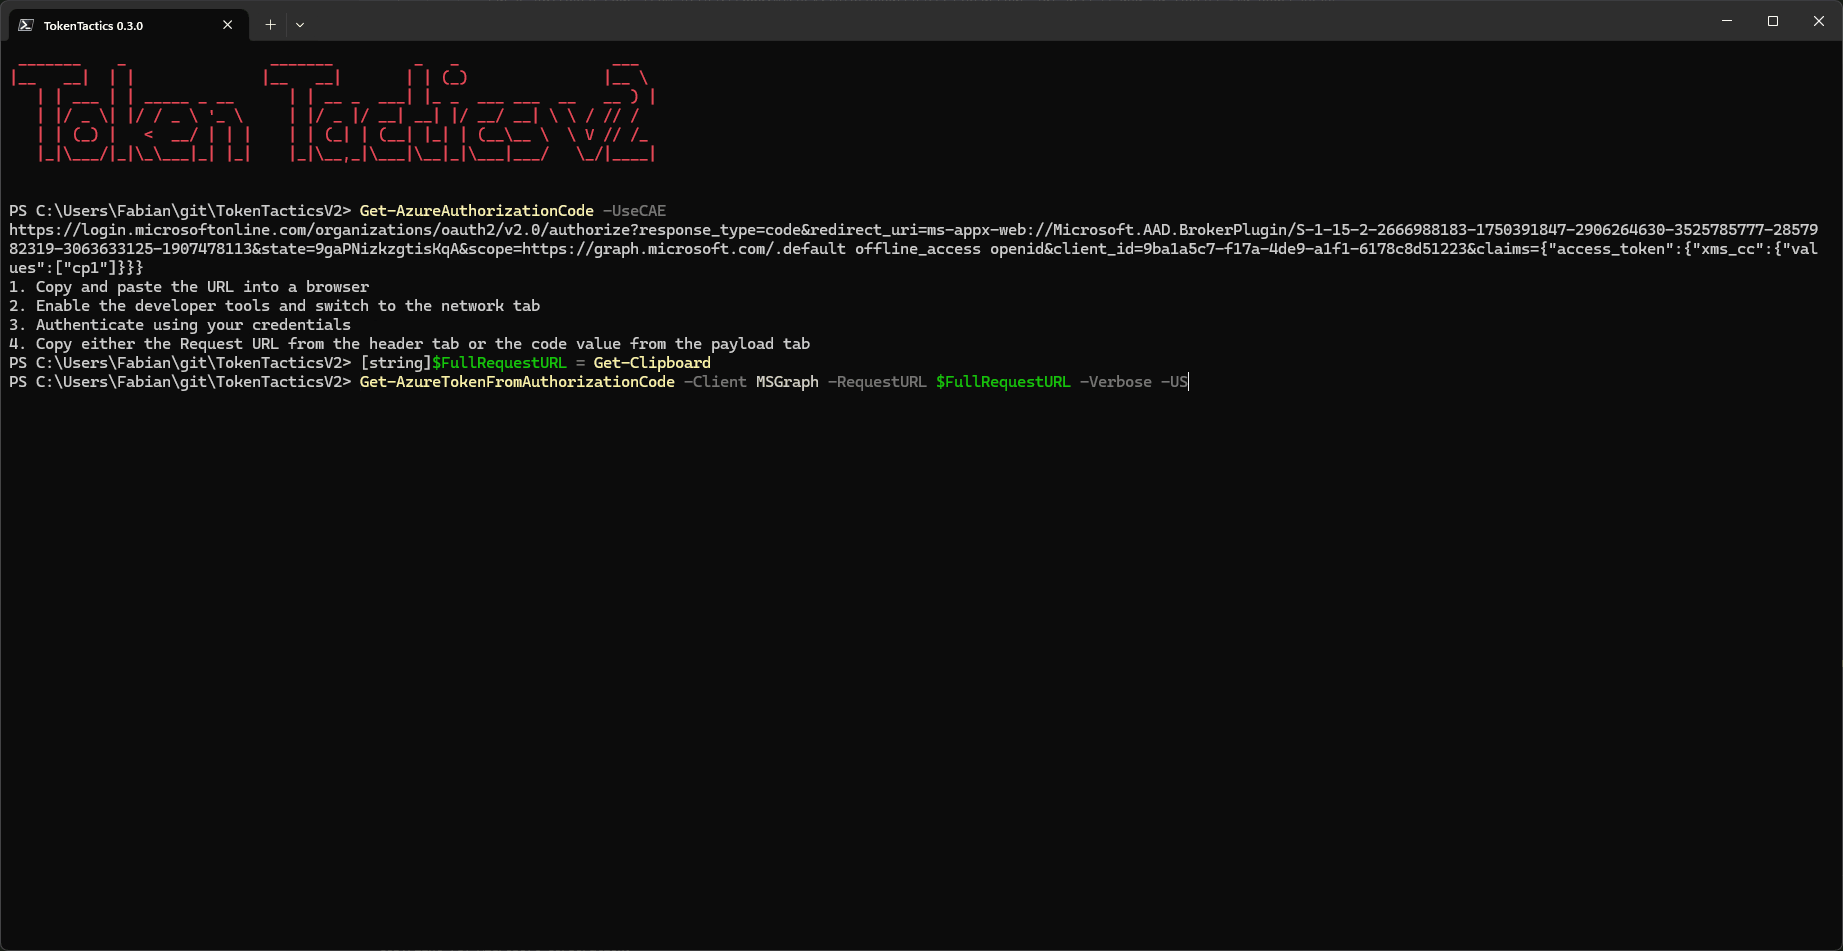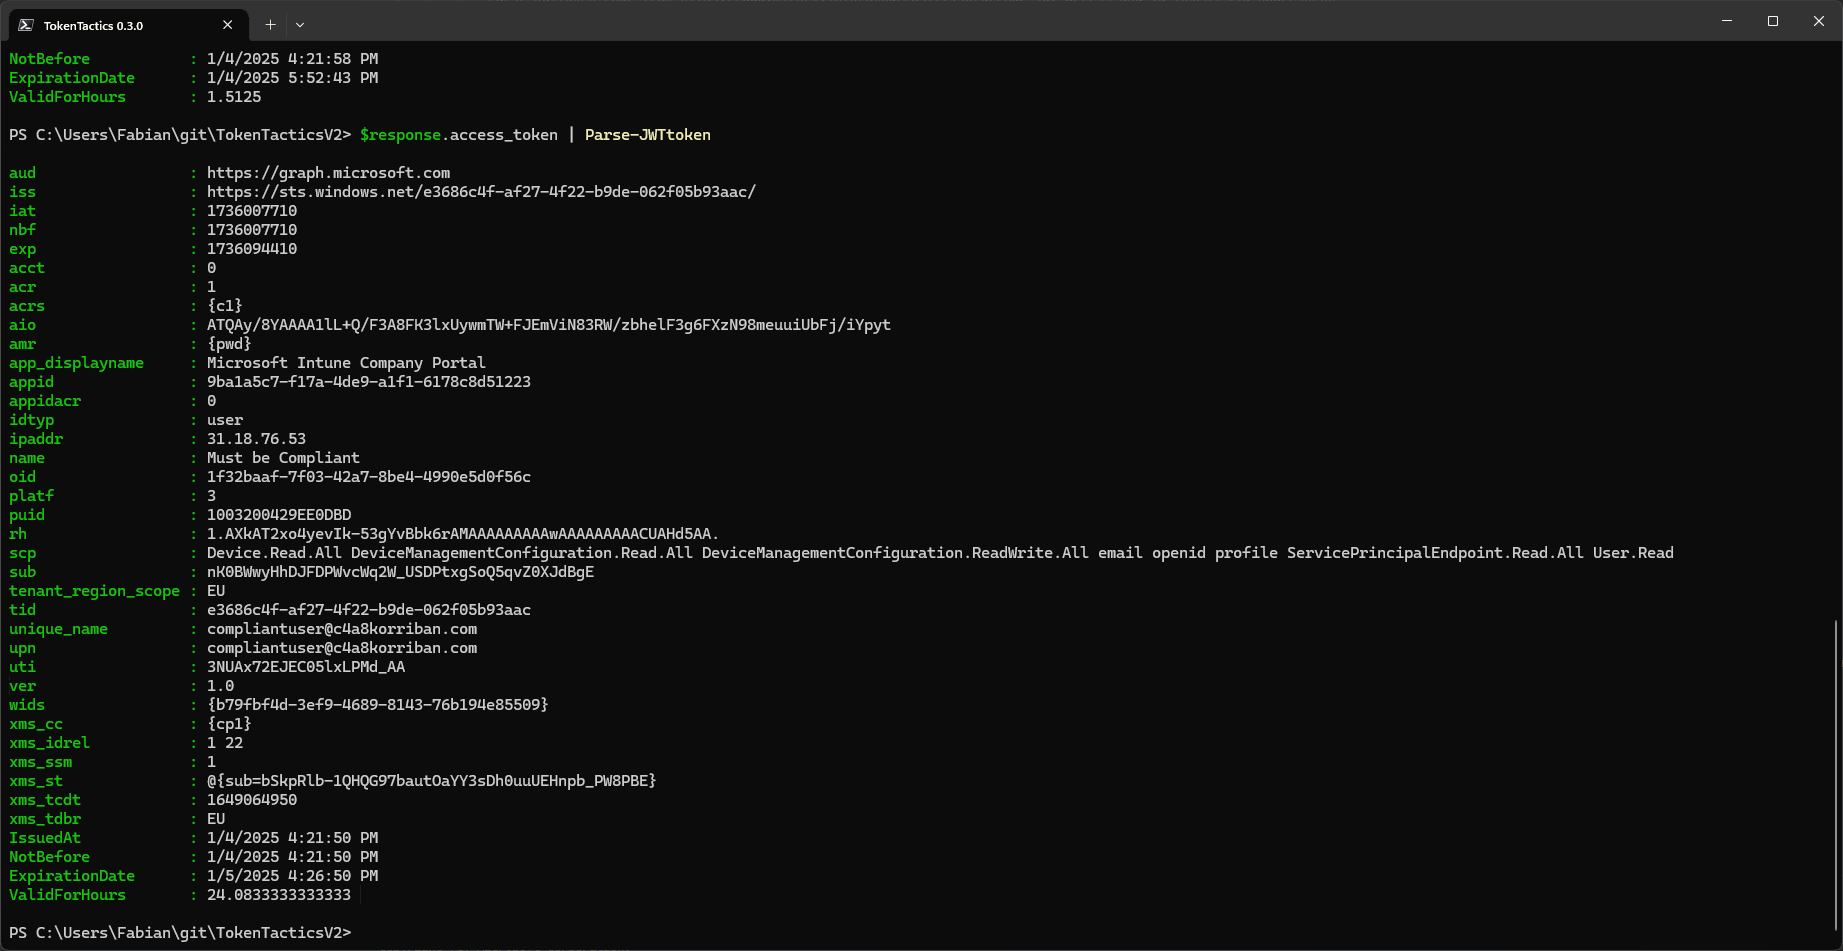
TokenTacticsV2
 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
authenticationcloud-securityidentity-access-management+3
455
f-bader/tokentacticsv2A fork of the great TokenTactics with support for CAE and token endpoint v2
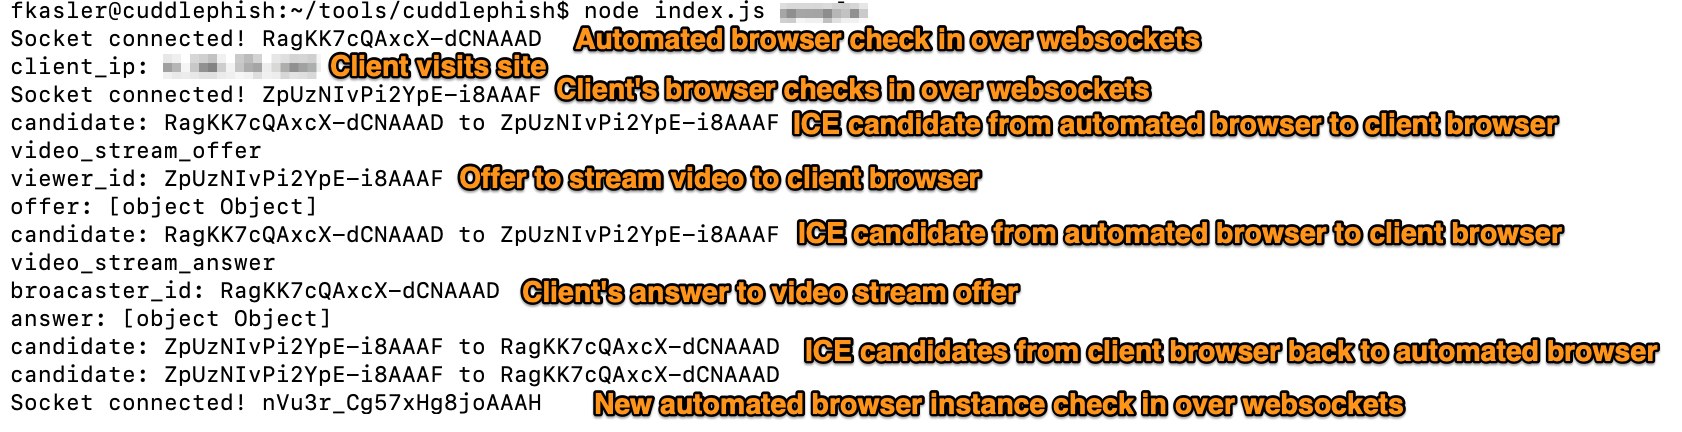 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 dviros/credsleaker
Credsleaker allows an attacker to craft a highly convincing credentials prompt using Windows Security, validate it against the DC and in turn leak it…
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 nickvourd/rti-toolkit
PowerShell toolkit for remote template injection attacks and defense. Injects malicious links into Office Word documents for phishing, with…
 v35hr4j/cve-2022-1597
The plugin, used as a companion for the Discy and Himer themes, does not sanitise and escape a parameter on its reset password form which makes it…
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 minotauro2020/cve-2023-40869
Cross Site Scripting vulnerability in mooSocial mooSocial Software v.3.1.6 allows a remote attacker to execute arbitrary code via a crafted script to…
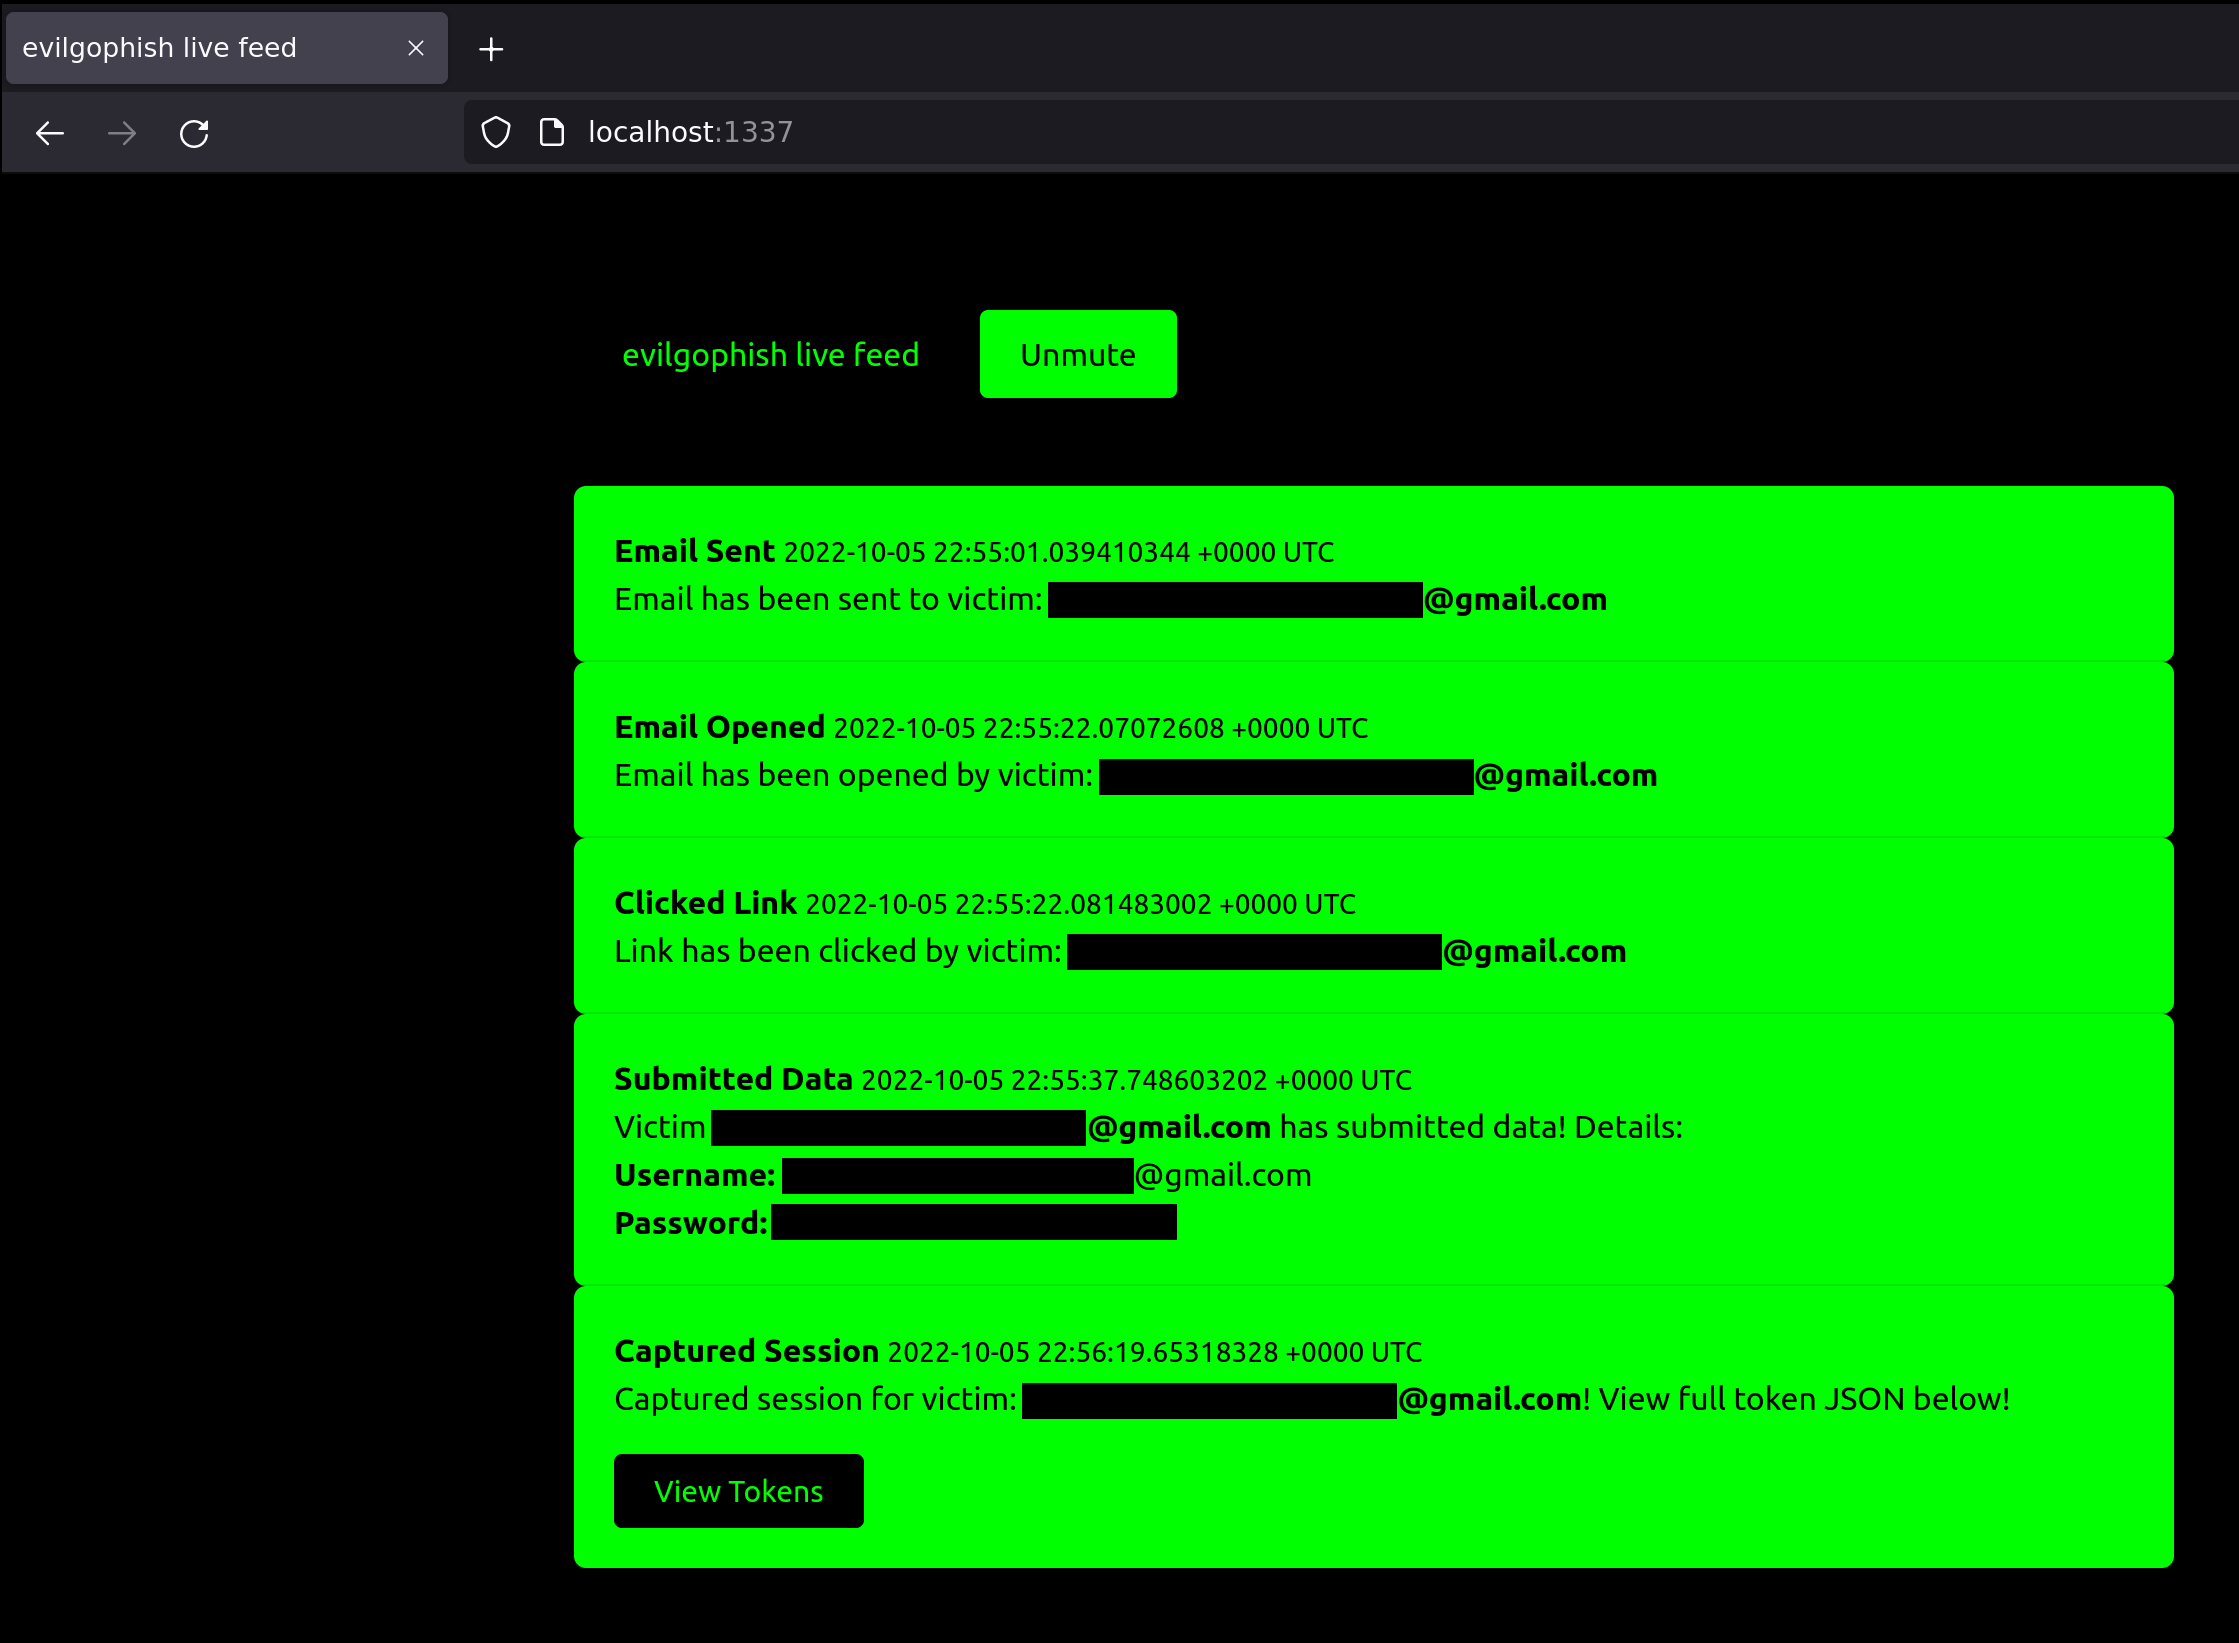 fin3ss3g0d/evilgophish
evilginx3 + gophish
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 the-girl-who-lived/cve-2020-25498
Stored XSS via CSRF in Beetel 777VR1 Router
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 openxp-research/cve-2022-2546
All-in-One WP Migration < 7.63 - Unauthenticated Reflected XSS + CSRF
 b0marek/cve-2023-4549
Repository for CVE-2023-4549 vulnerability.
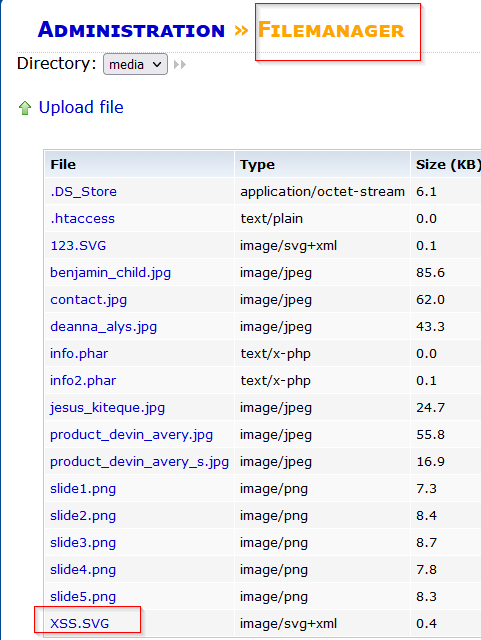 sromanhu/cve-2023-44767_ritecms-file-upload--xss---filemanager
RiteCMS 3.0 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will…
 rvrsh3ll/tokentactics
Azure JWT Token Manipulation Toolset
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.