

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.8k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 hunt-benito/cve-2026-41200-stig-manager-oidc-reflected-xss
Proof-of-concept exploit generator for reflected XSS in STIG Manager OIDC authentication, enabling session token theft via crafted callback URLs and…
 dharmstm/cve-2026-30502-openkm-6.3.12-reflected-xss
Documentation and proof-of-concept for CVE-2026-30502, a reflected XSS vulnerability in OpenKM v6.3.12. Includes technical analysis, root cause,…
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
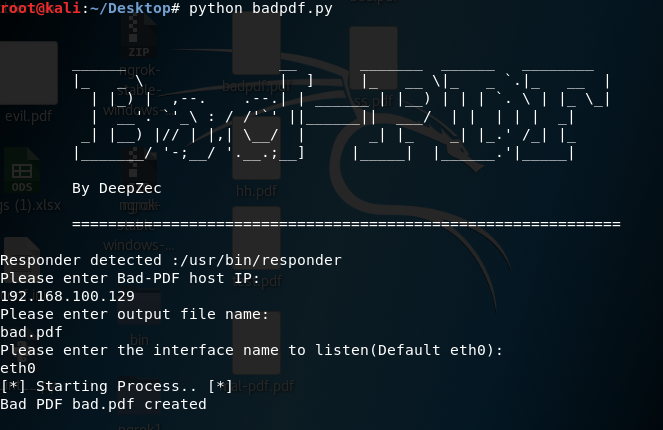
 roj1py/cve-2024-47875-phpspreadsheet-xss-poc
This is a PoC/Exploit for the CVE-2024-47875 PhpSpreadsheet XSS Vuln
 secsys-fdu/cve-2025-51863
Proof-of-concept for a Self-XSS vulnerability in ChatGPTUtil, demonstrating cookie theft and account hijacking via crafted SVG payloads pasted into…
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 nxploited/cve-2025-1306
Newscrunch <= 1.8.4 - Cross-Site Request Forgery to Arbitrary File Upload