
CVE-2026-64638
 dungsocool/cve-2026-64638
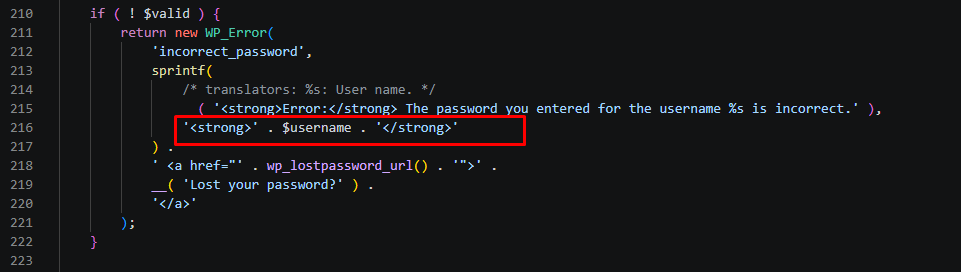
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
code-analysisexploitationpayload-development+4
dungsocool/cve-2026-64638Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 jun2e0/cve-2025-26788
Proof-of-concept exploit for CVE-2025-26788 demonstrating WebAuthn credential ID manipulation via JavaScript hooking to bypass authentication in…
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 cesarbtakeda/7-zip-cve-2025-0411-poc
Proof-of-concept exploit for CVE-2025-0411, demonstrating Mark-of-the-Web bypass in 7-Zip to enable arbitrary code execution via crafted archives…
 stmcyber/boobsnail
Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…
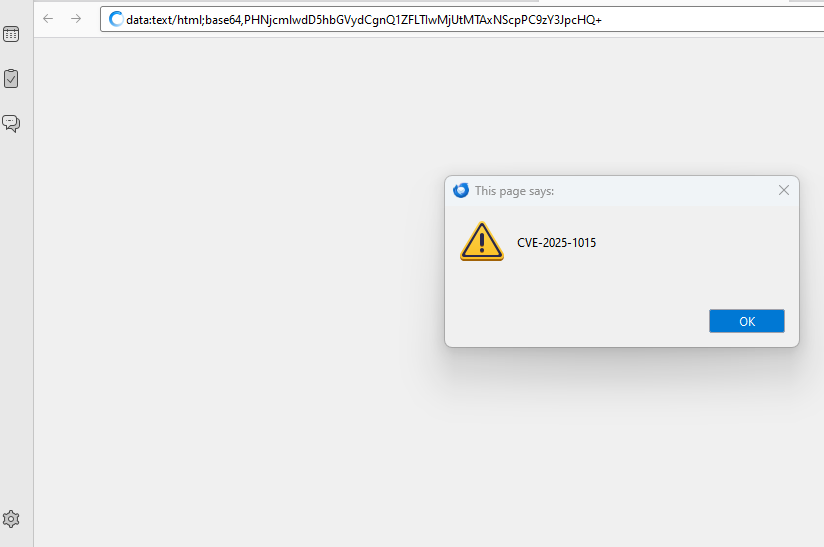 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
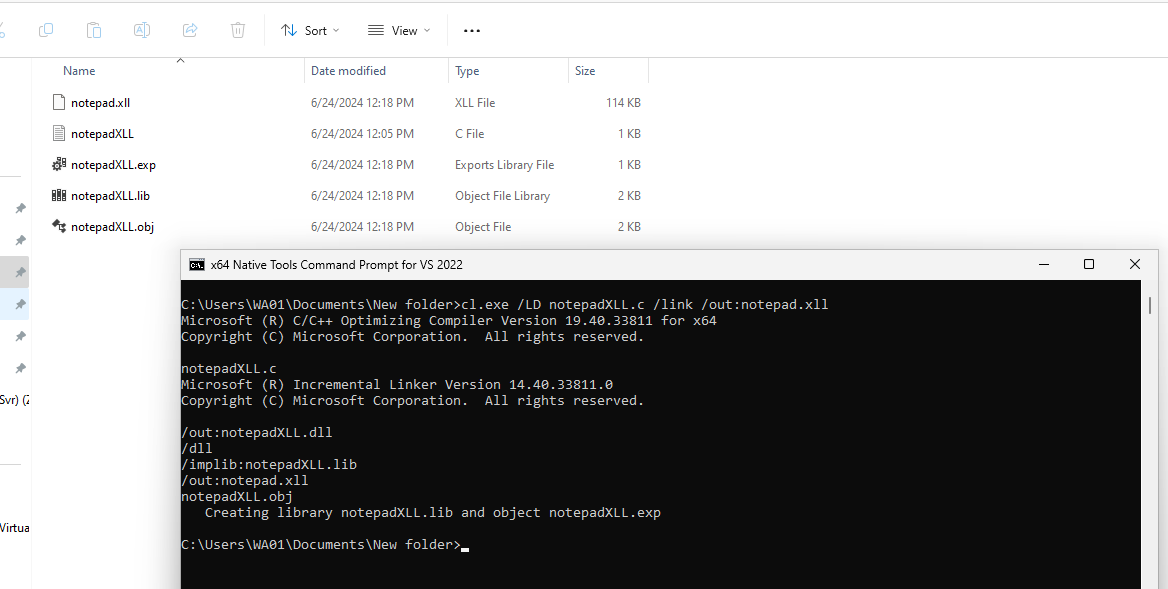 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
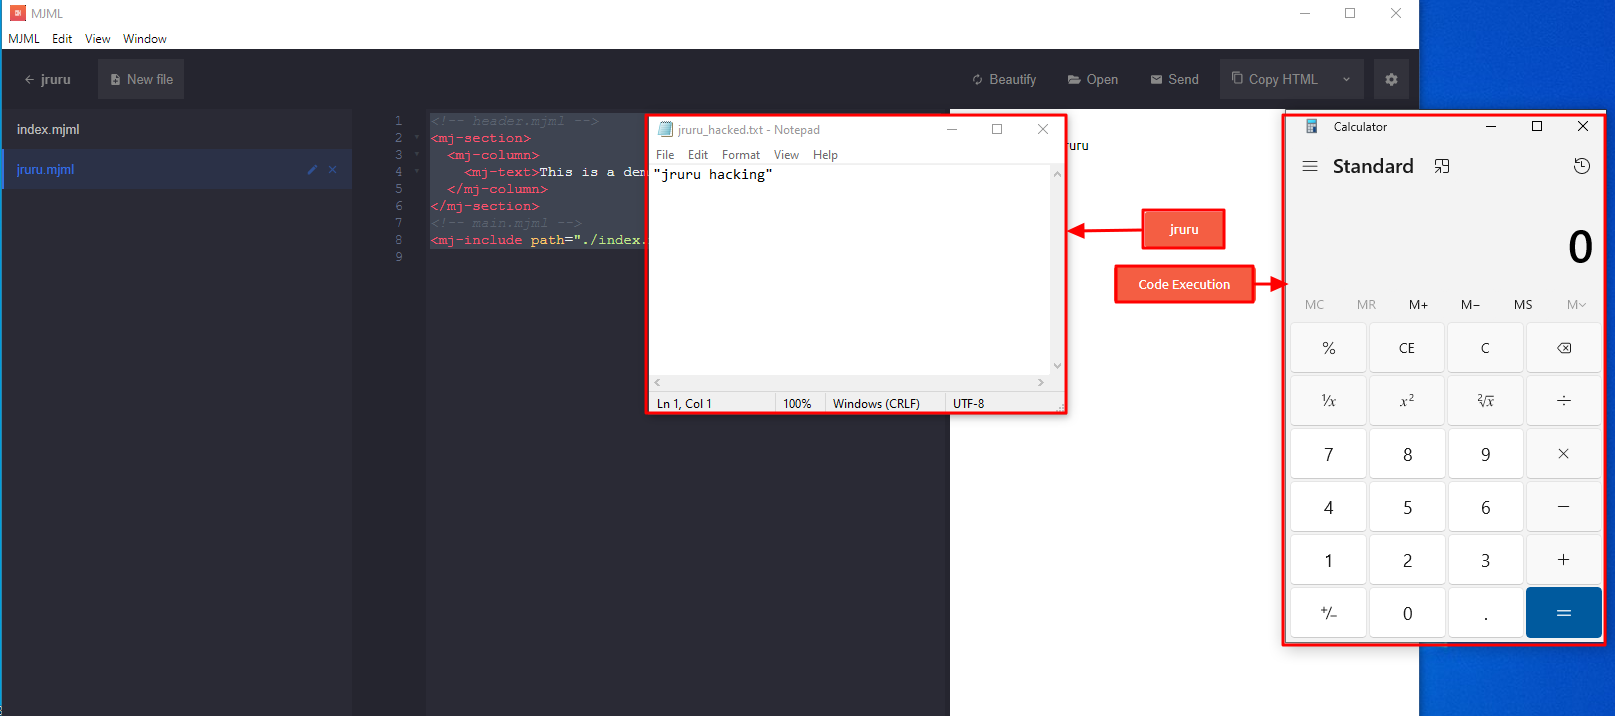 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE exploit
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.
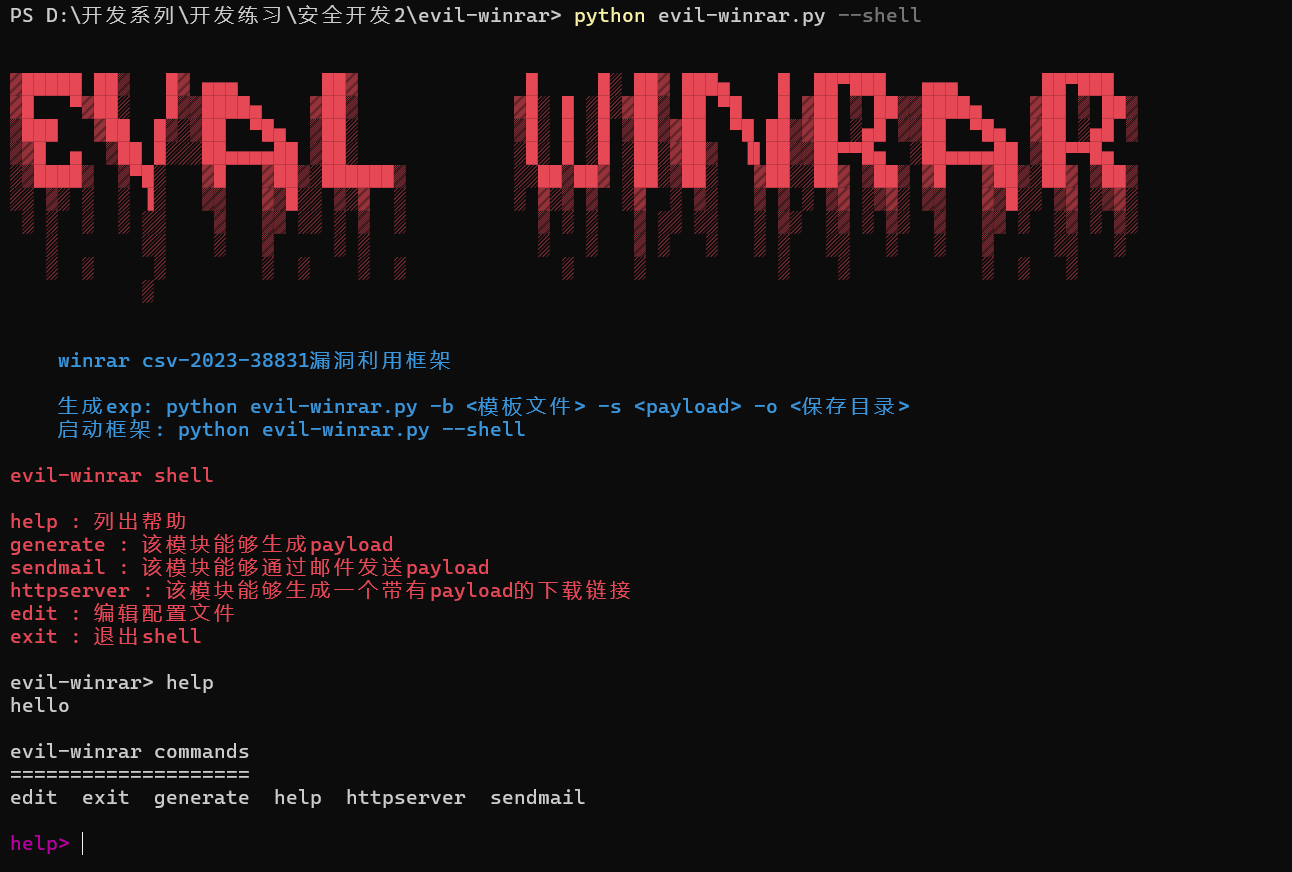 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 d00mfist/mystikal
macOS Initial Access Payload Generator
 rvrsh3ll/azure-app-tools
Collection of tools to use with Azure Applications
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
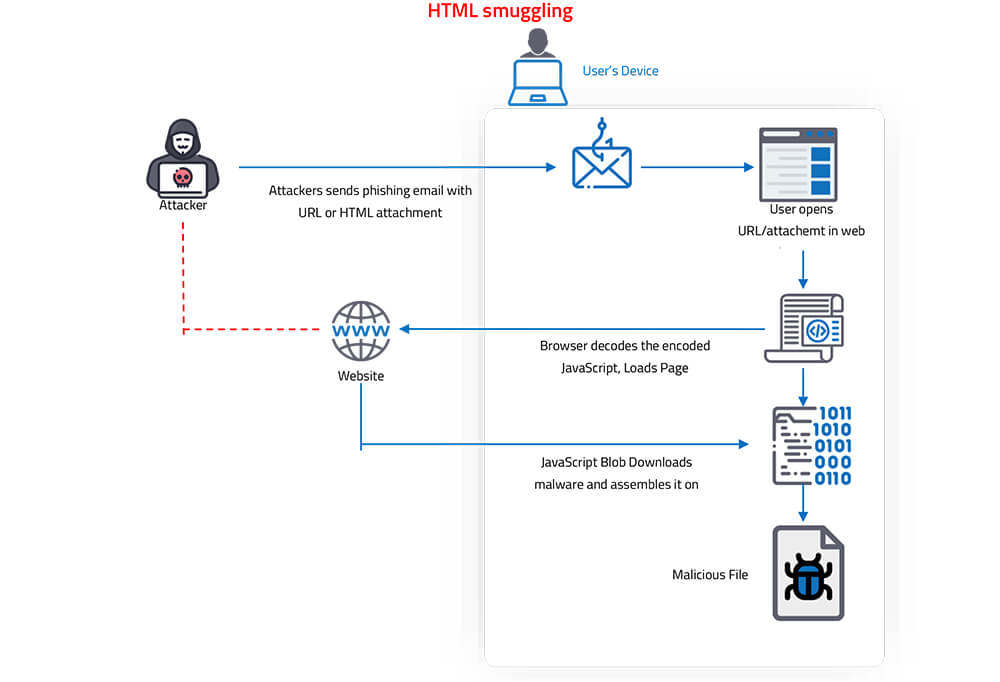 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page