SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

Collection of tools to use with Azure Applications

macOS Initial Access Payload Generator

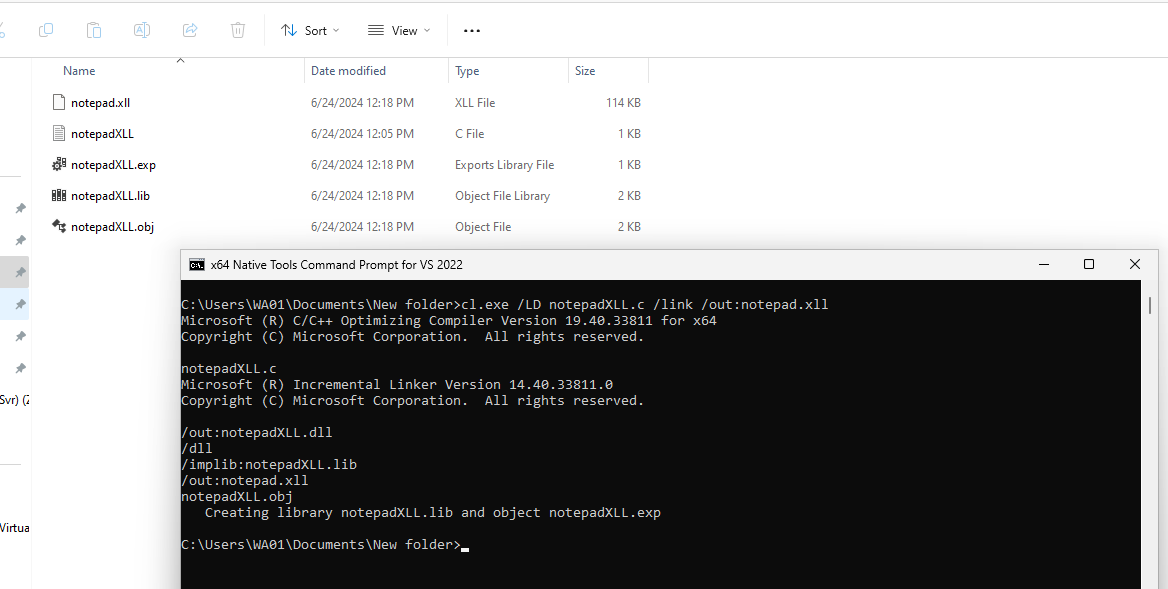
xll windows reverse shell


ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.

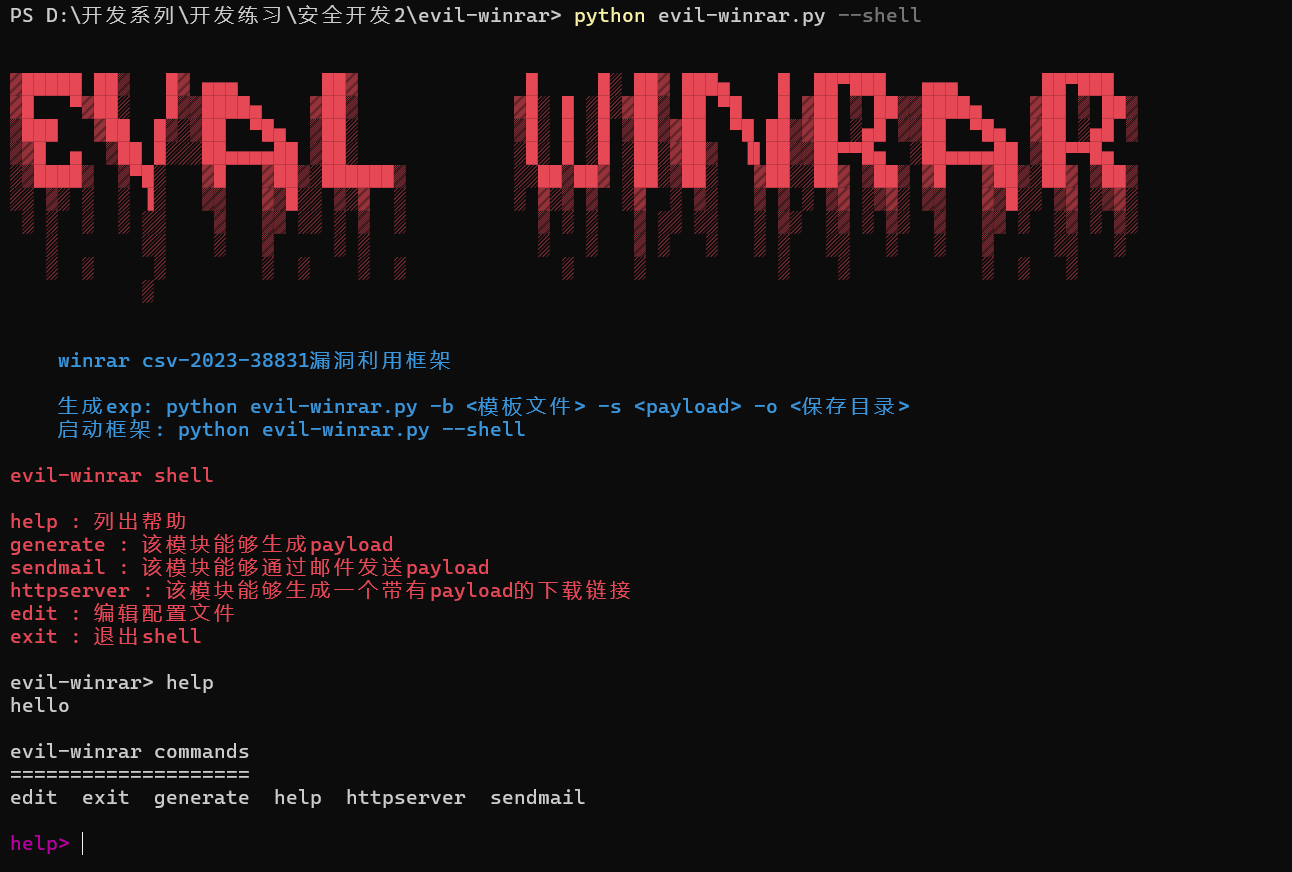
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)

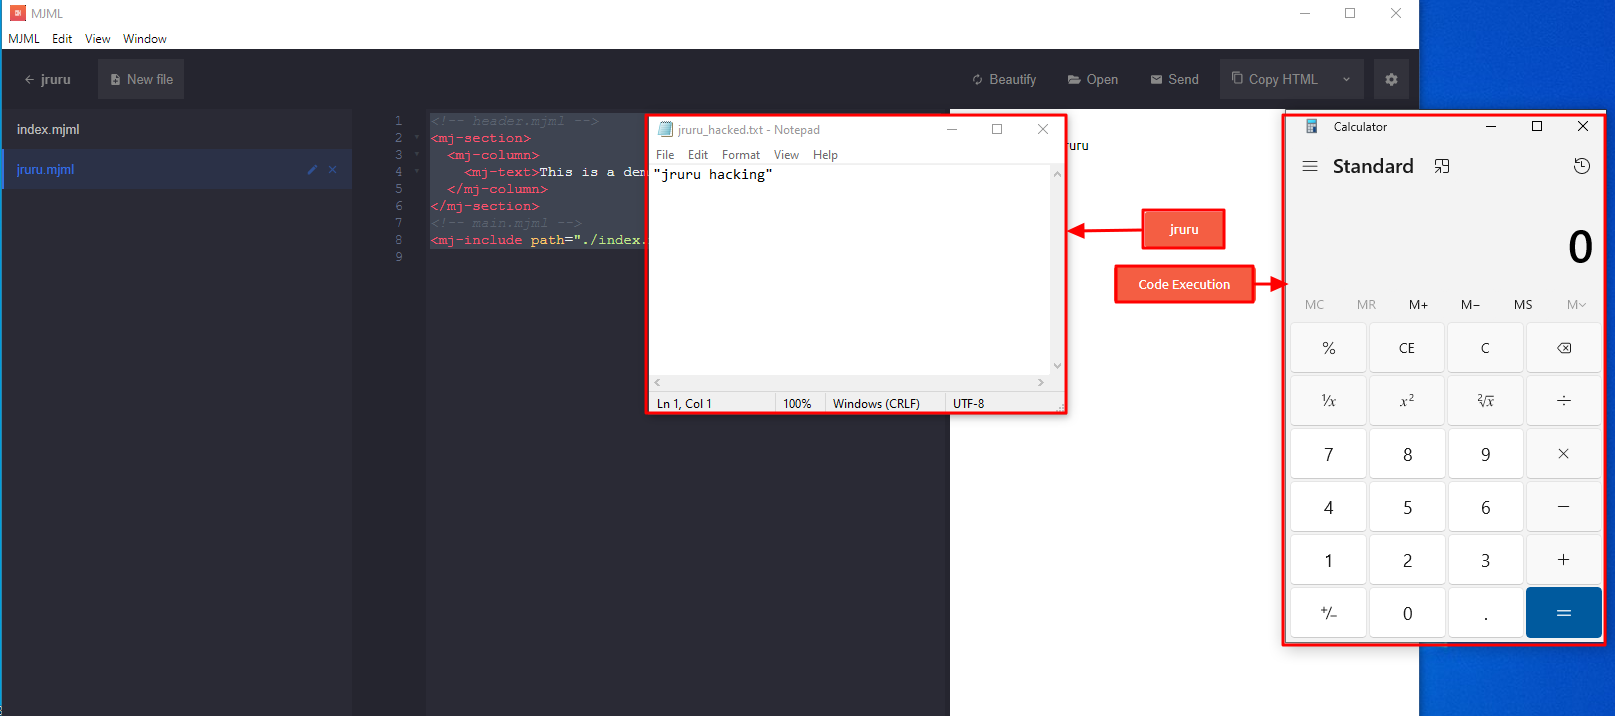
mjml-app v3.0.4 & 3.1.0-beta RCE exploit

an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…

Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…

Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…

Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…

Proof-of-concept exploit for CVE-2025-0411, demonstrating Mark-of-the-Web bypass in 7-Zip to enable arbitrary code execution via crafted archives…

PoC for CVE-2025-22131

CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC