
CVE-2023-23397
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
email-securityexploitationpassword-attacks+3
132
trackflaw/cve-2023-23397Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
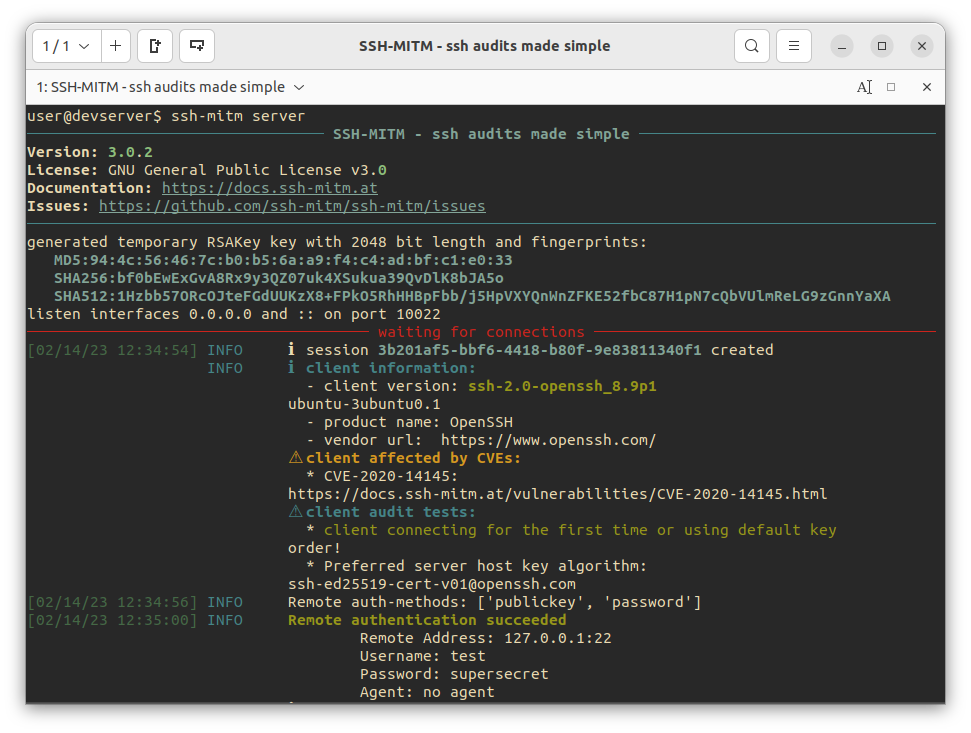 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
 perezmascato/urlcadiz
A simple script to generate a hidden url for social engineering.
 lunarca/simpleemailspoofer
A simple Python CLI to spoof emails.
 g4lb1t/pstf2
Passive Security Tools Fingerprinting Framework
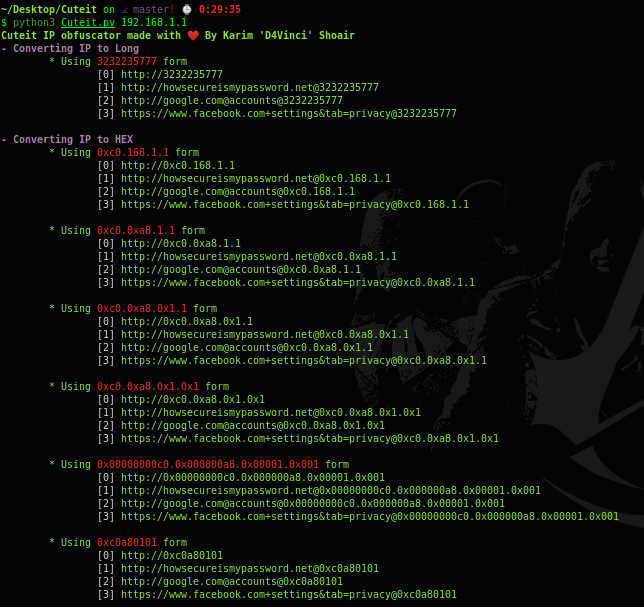 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
 nicholasadamou/minipwner
A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".
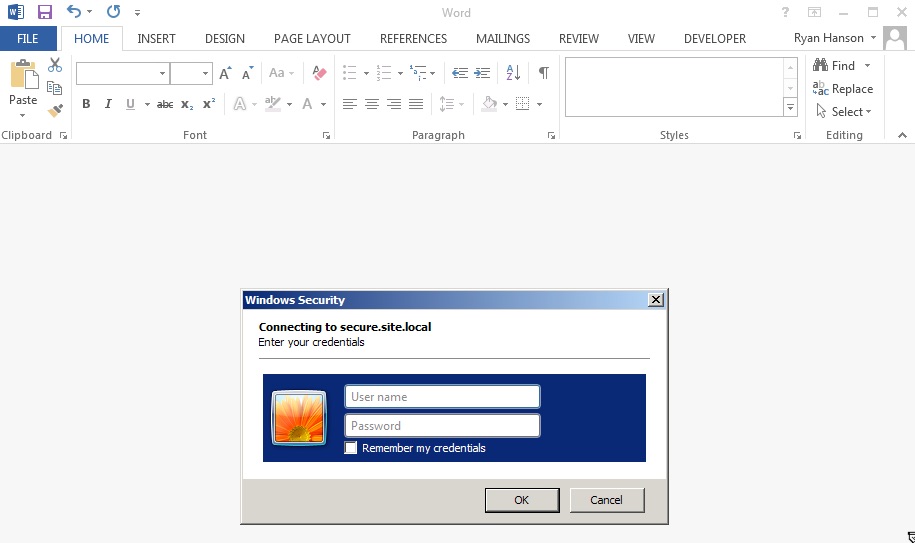 ryhanson/phishery
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector
 mr-un1k0d3r/maliciousmacrogenerator
Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.
 anupam2808/spy-masker
It is a simple Python Script to hide phishing URL under a normal looking URL (google.com or facebook.com). It can be integrated into Phishing tools…
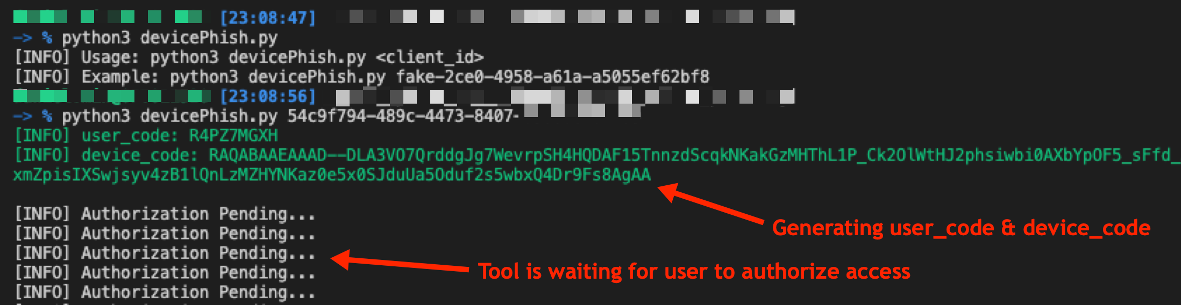 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 geozin/poc-cve-2018-25031
Proof-of-concept exploit for CVE-2018-25031 (Swagger UI XSS) that exfiltrates authorization codes via crafted configUrl/url parameters.
 elamani-drawing/cve-2024-4367-poc-pdfjs
PoC (Proof of Concept) de la CVE-2024-4367 - Vulnérabilité RCE dans libwebp. Démonstration complète incluant : création de payloads, scénarios…