
tirith
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
curated-resourcesdata-exfiltrationdevsecops+8
2.7k
sheeki03/tirithTerminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
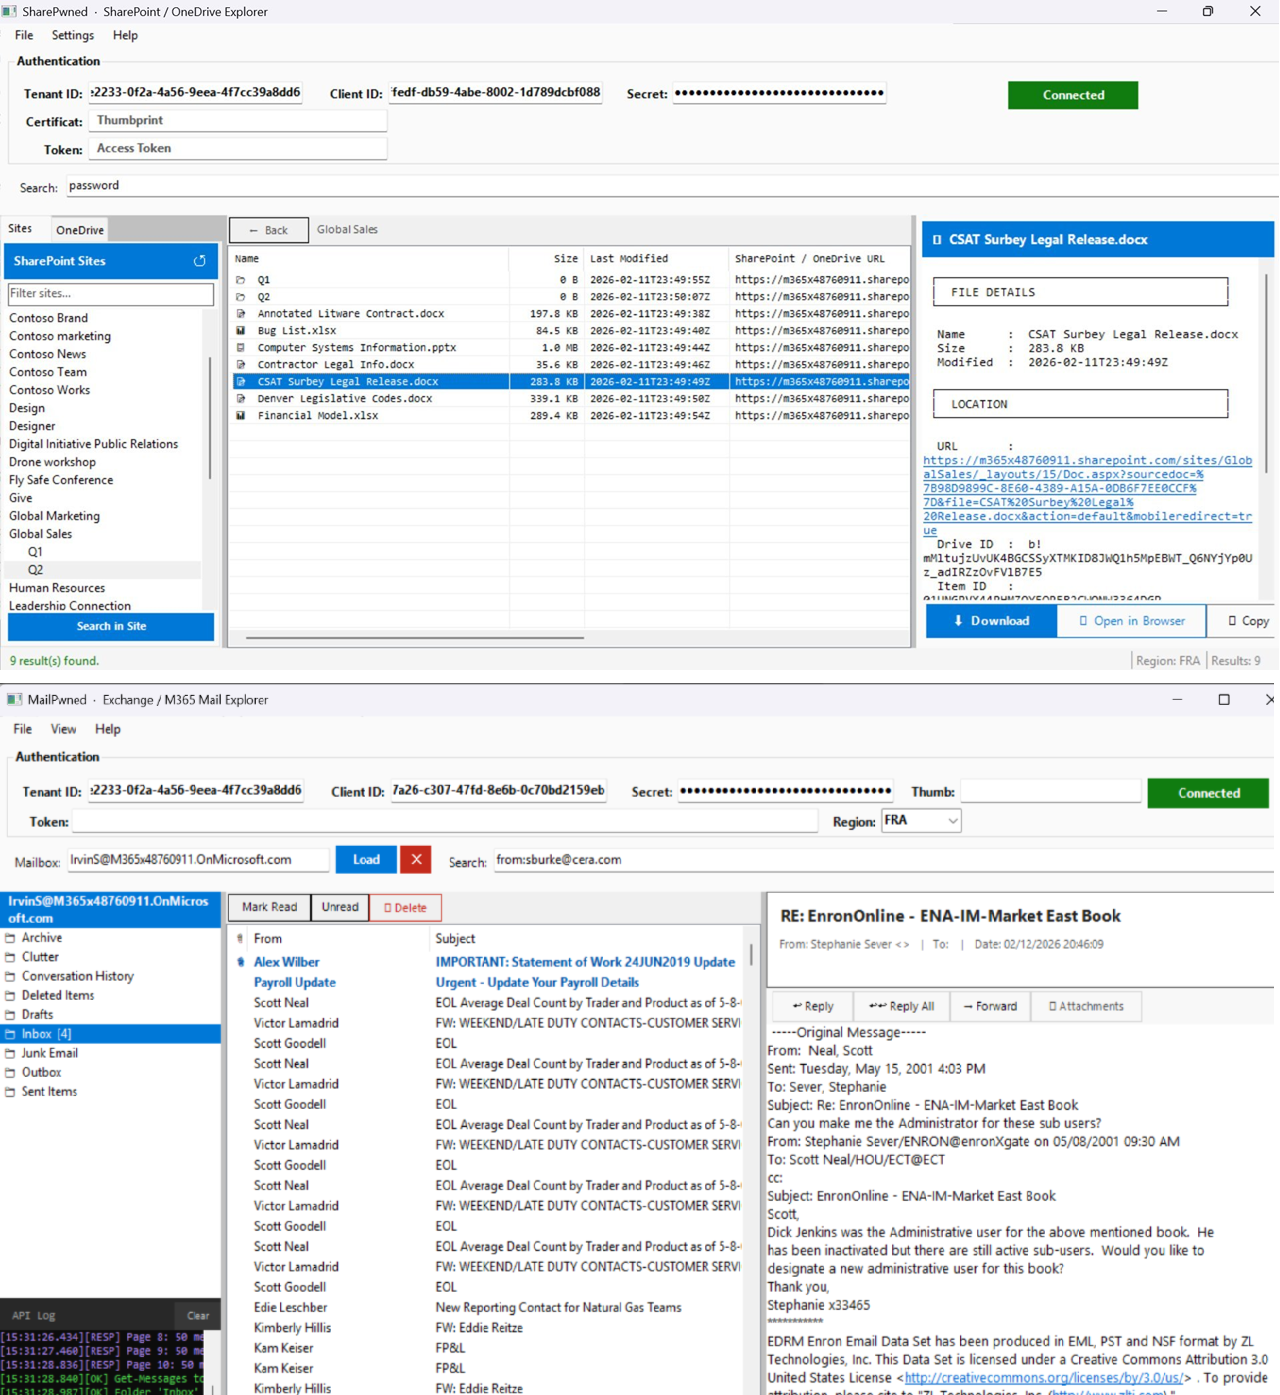 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
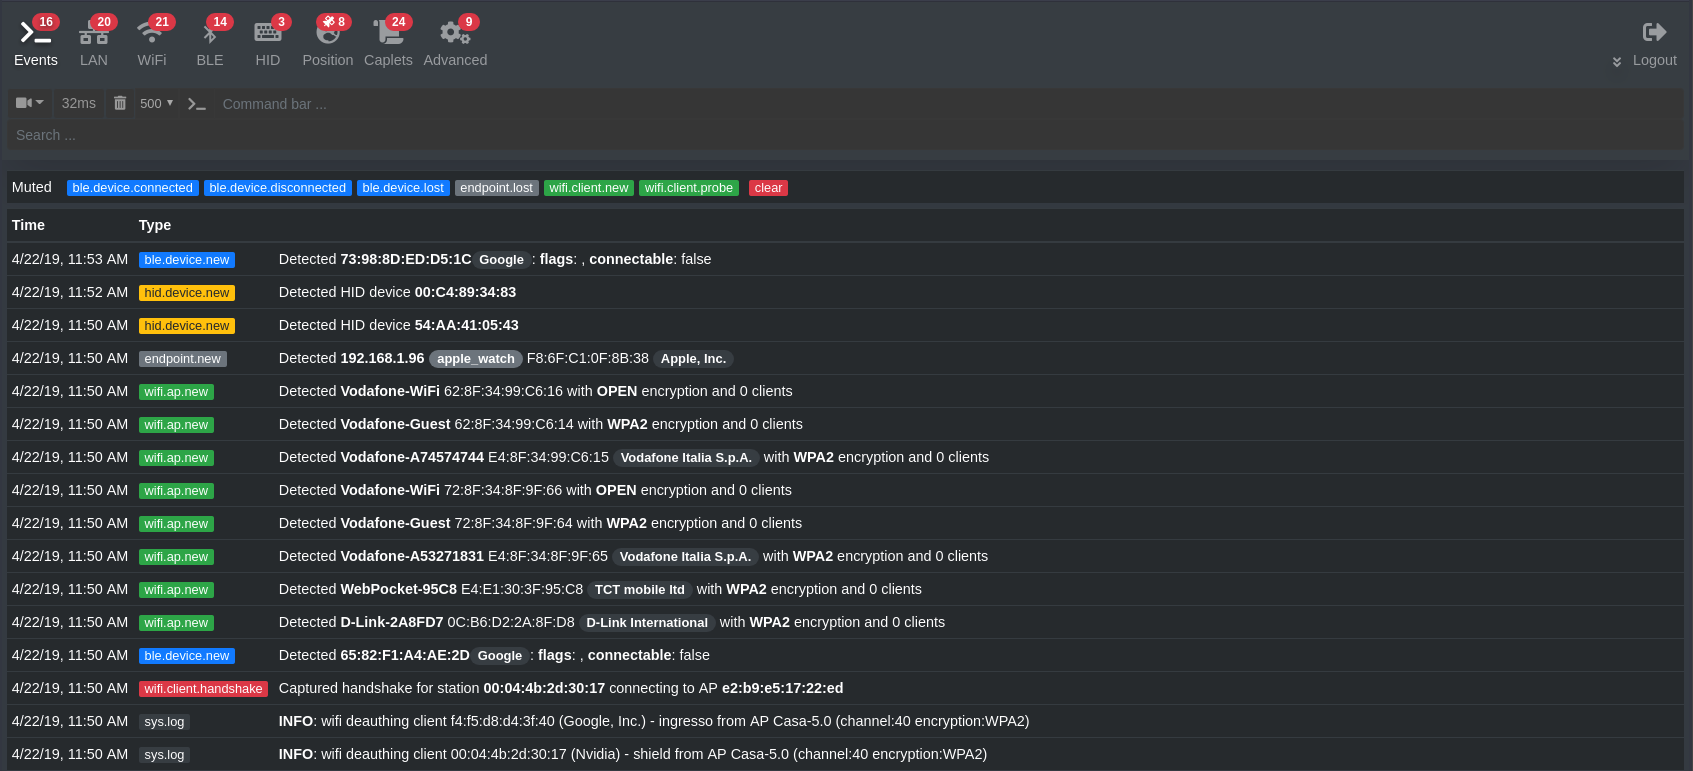 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
 4w4k3/beelogger
Generate Gmail Emailing Keyloggers to Windows.
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
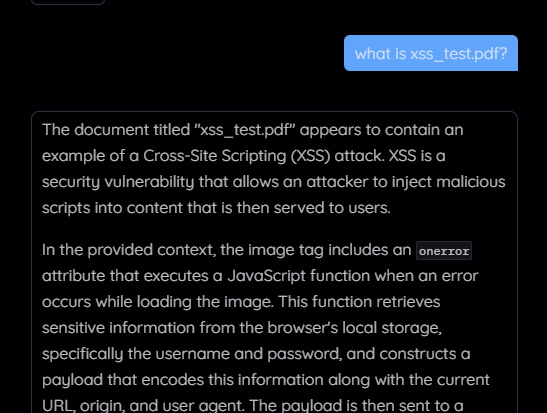 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
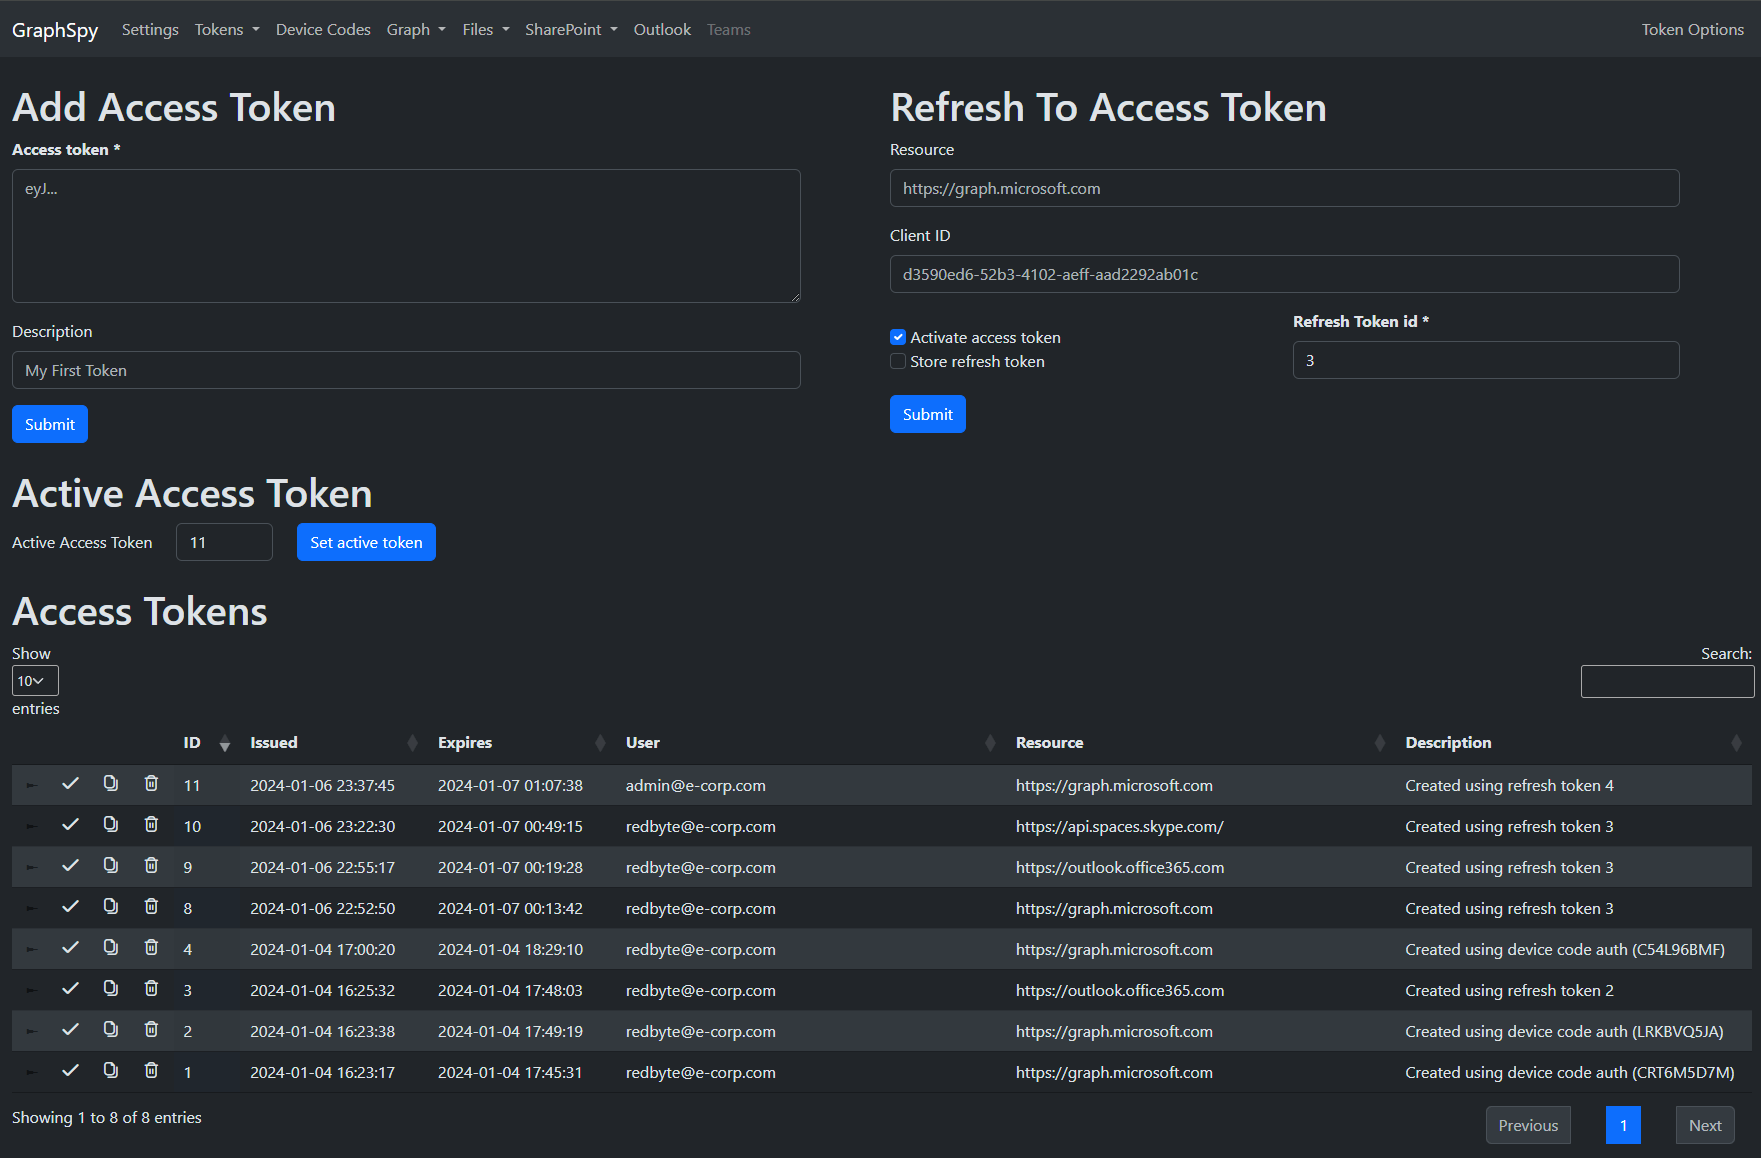 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
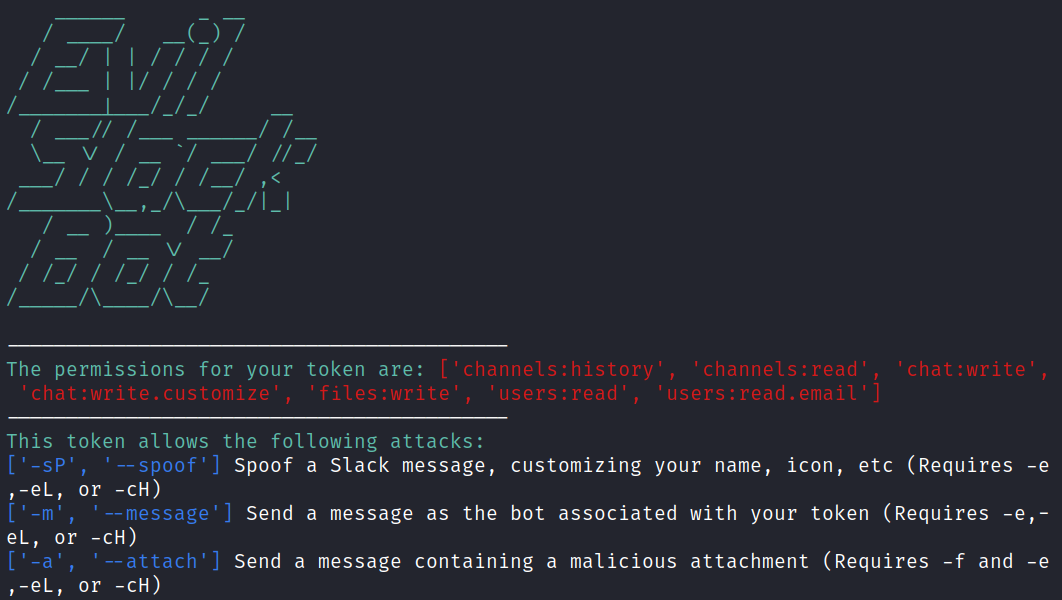 drew-sec/evilslackbot
A Slack bot phishing framework for Red Teaming exercises