

goshs
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
command-and-controlctfdns-analysis+5
976
goshs-labs/goshsFeature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 kgretzky/pwndrop
Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV.
 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
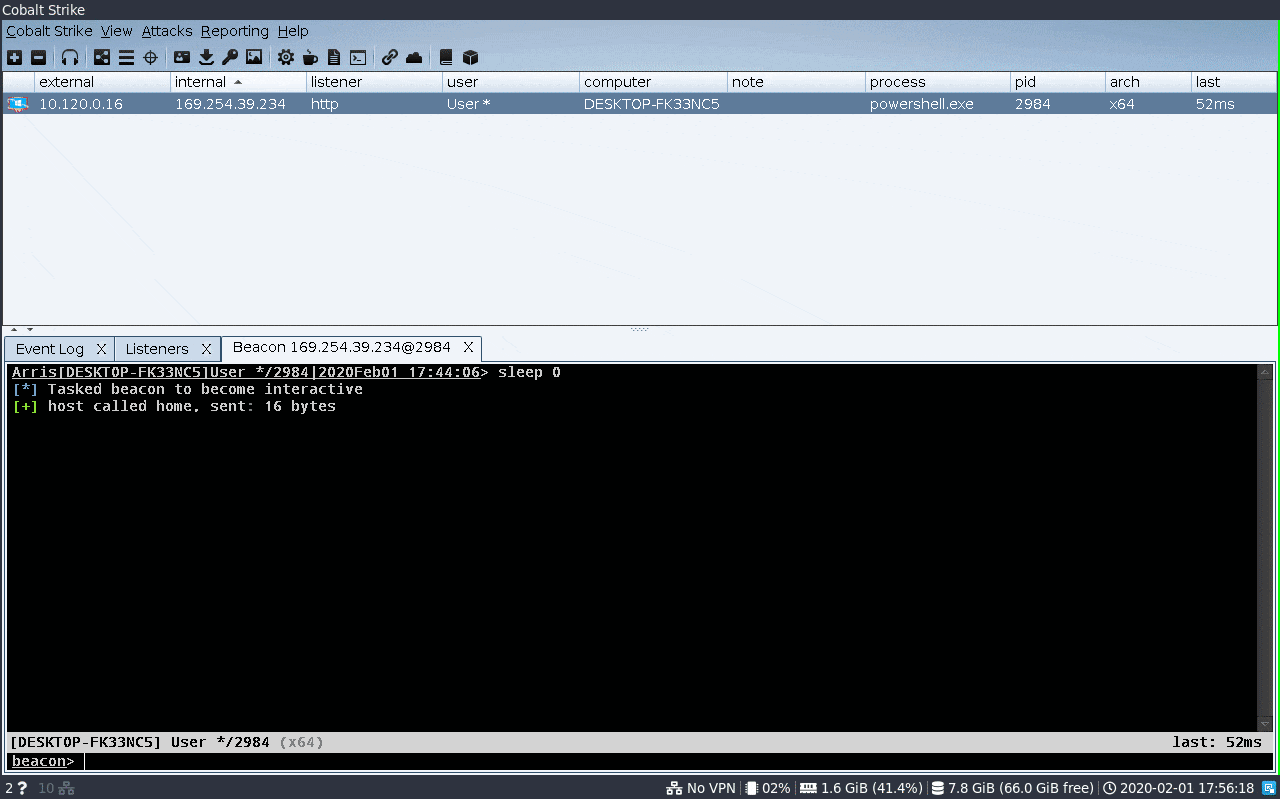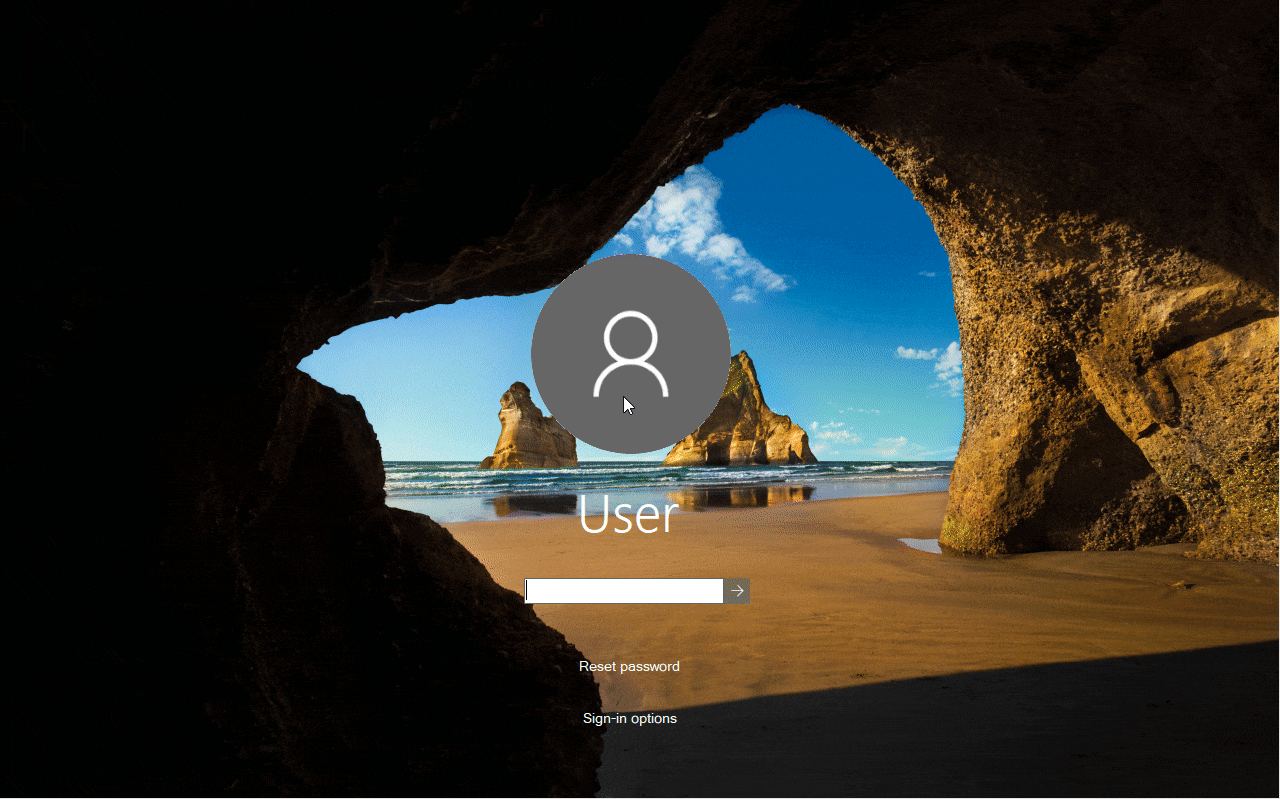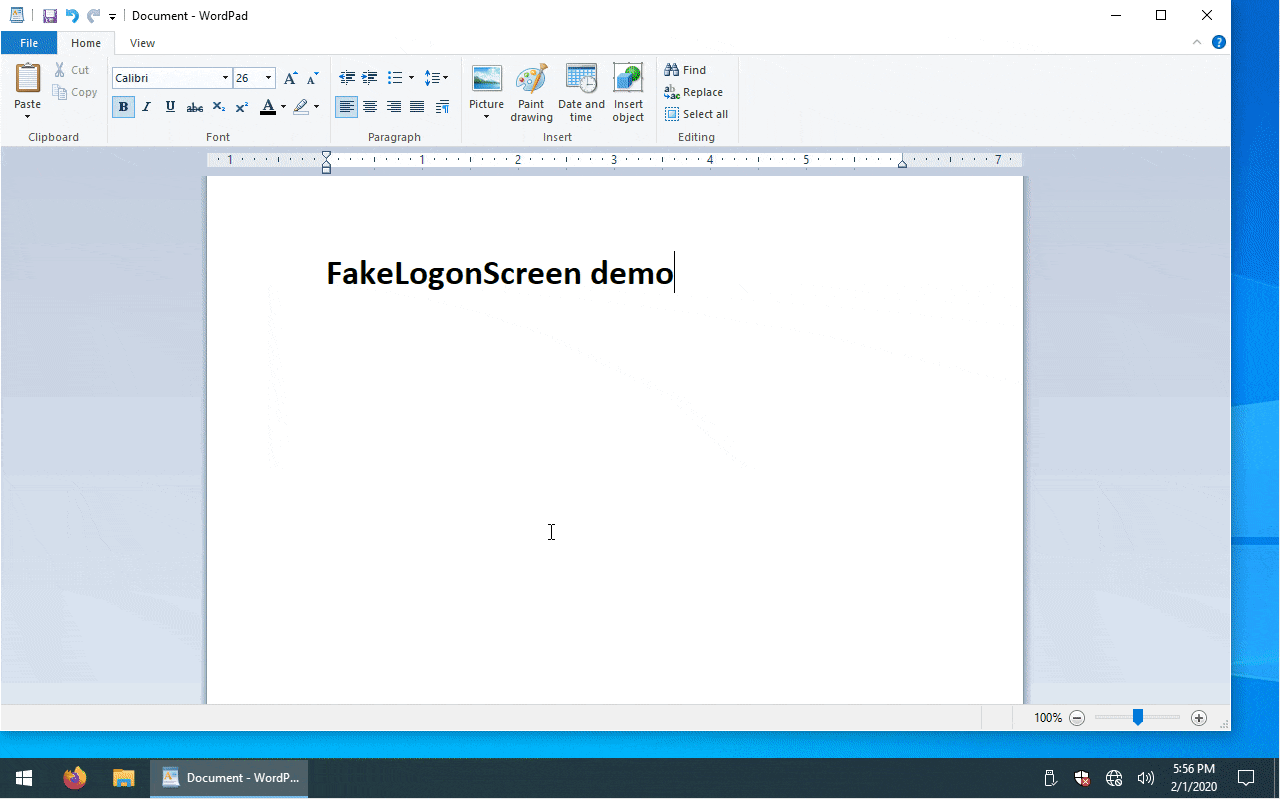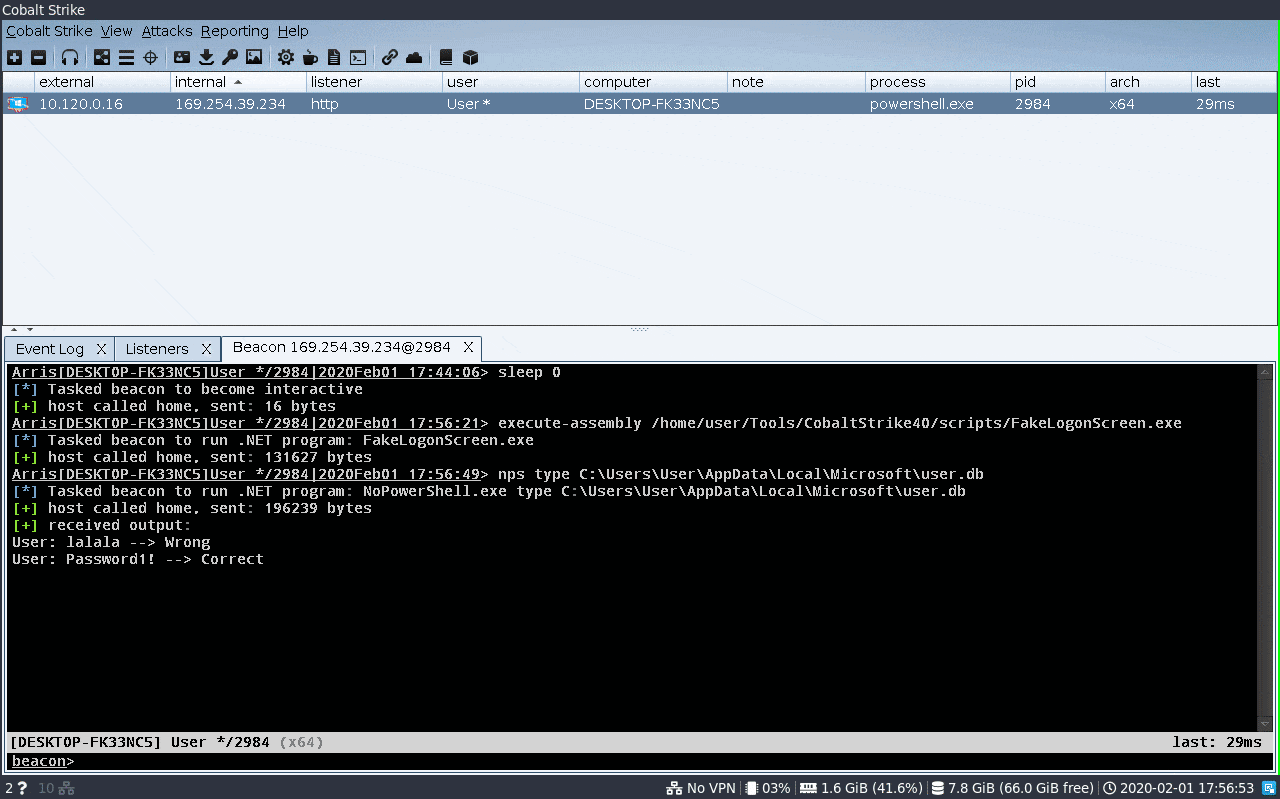 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
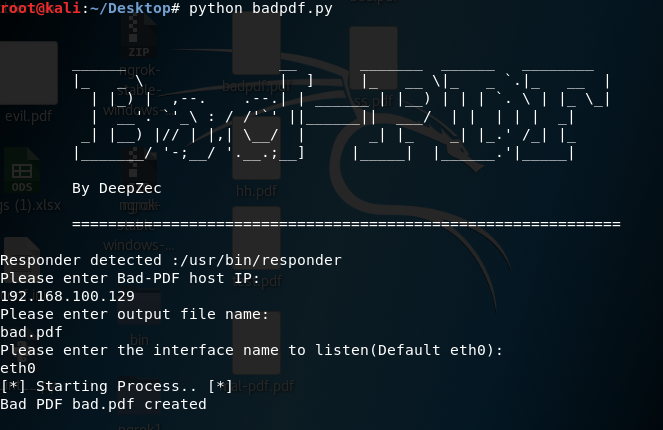
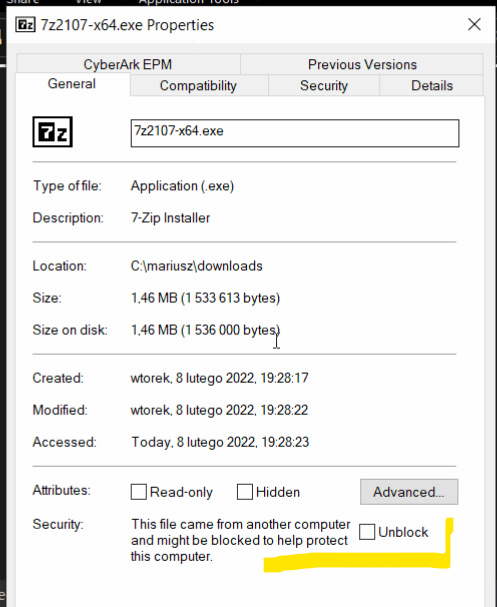 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 beefproject/beef
The Browser Exploitation Framework Project
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
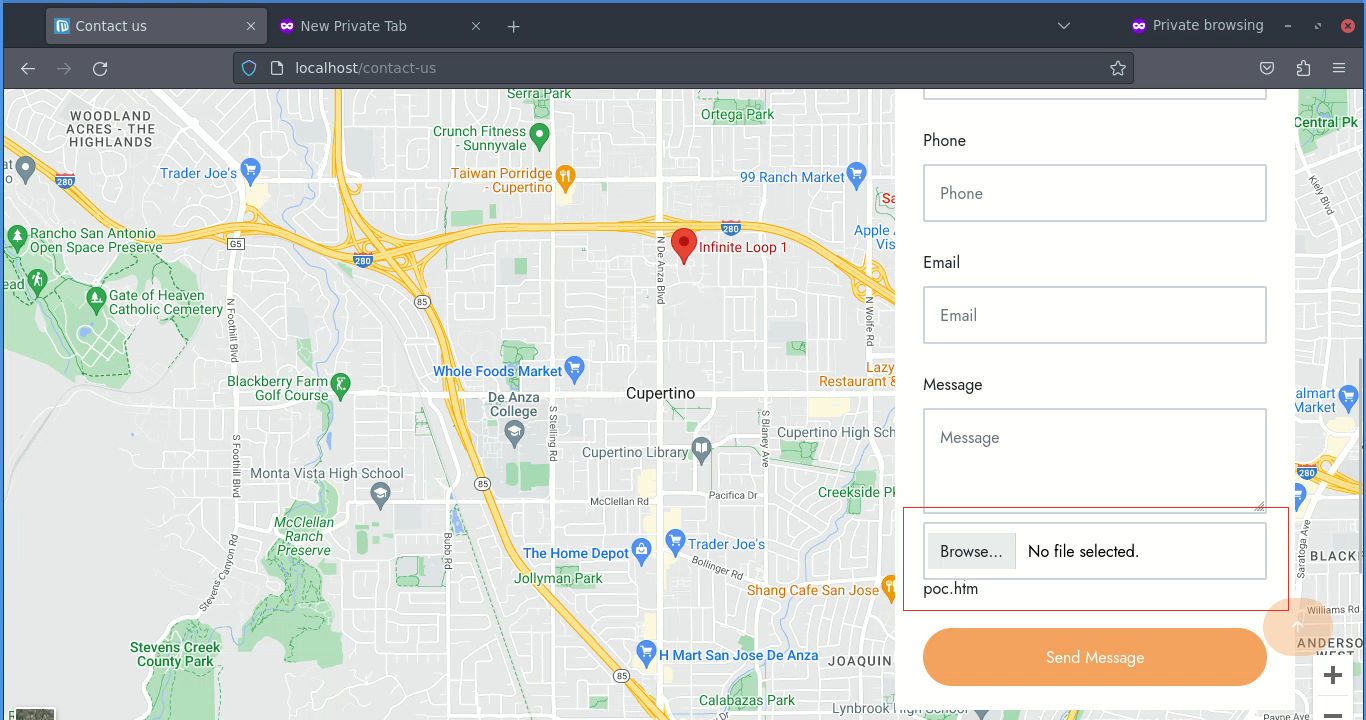 cyber-wo0dy/cve-2023-49052
Microweber version 2.0.4 vulnerable to "Uploading Malicious Files"
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 natasaka/cve-2025-30349
Horde IMP (through 6.2.27) vulnerability – obfuscation via HTML encoding – XSS payload
 cscli/cve-2017-5223
Proof-of-concept exploit for CVE-2017-5223 demonstrating arbitrary file read via PHPMailer's attachment and email content injection.
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
 themehackers/cve-2024-21413
CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC