

SpoofThatMail
 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
dns-analysisemail-securityphishing-tools+1
3364 years ago
v4d1/spoofthatmailBash script to check if a domain or list of domains can be spoofed based in DMARC records
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 arjunindia/fb-phisher-python
A python server tool based on flask , this tool can phish some Facebook credentials!
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 am0nt31r0/password-analysis
Script in Go that analyzes a list of passwords based on in its entropy and weak passwords from a dictionary. Useful for penetration tests and…
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 ceramicskate0/sharpexchange
C# Tool to interact with MS Exchange based on MS docs
 jimywork/certstreamcatcher
This tool is based on regex with effective standards for detecting phishing sites in real time using certstream and can also detect punycode (IDNA)…
 curi0usjack/luckystrike
A PowerShell based utility for the creation of malicious Office macro documents.
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
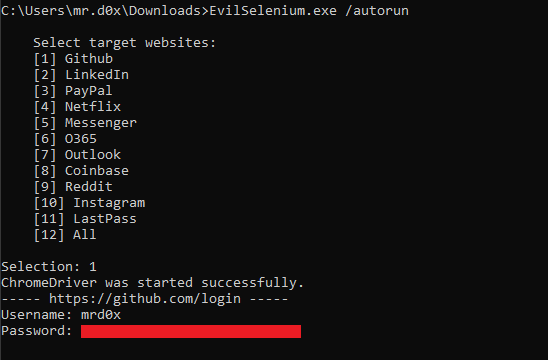 mrd0x/evilselenium
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
 absholi7ly/microsoft-edge-information-disclosure
CVE-2024-30056 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability