SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

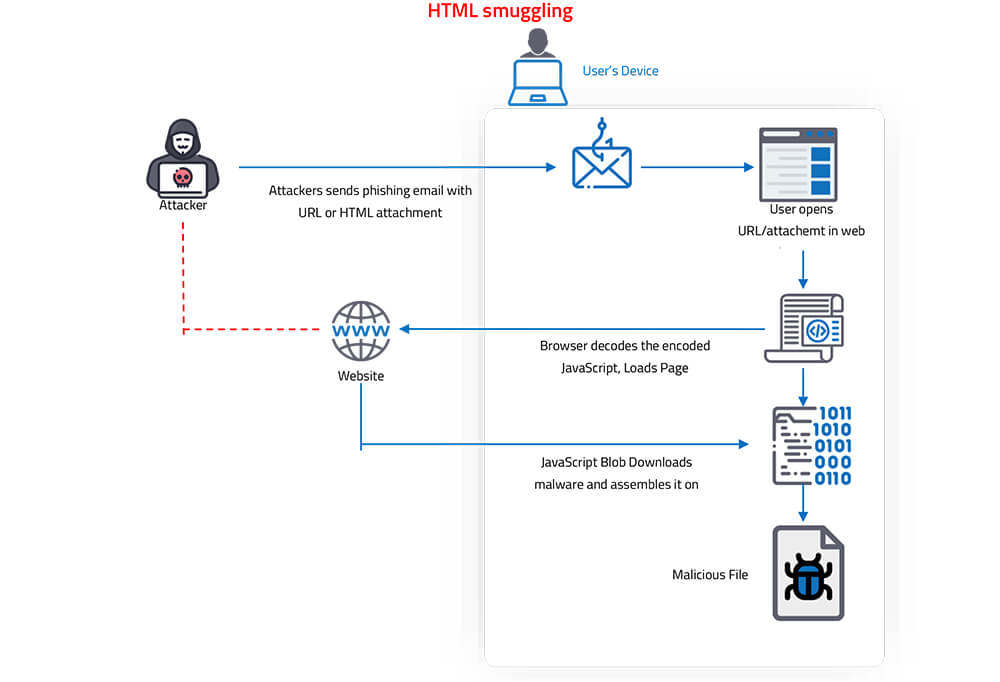
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

a CLI for ephemeral penetration testing

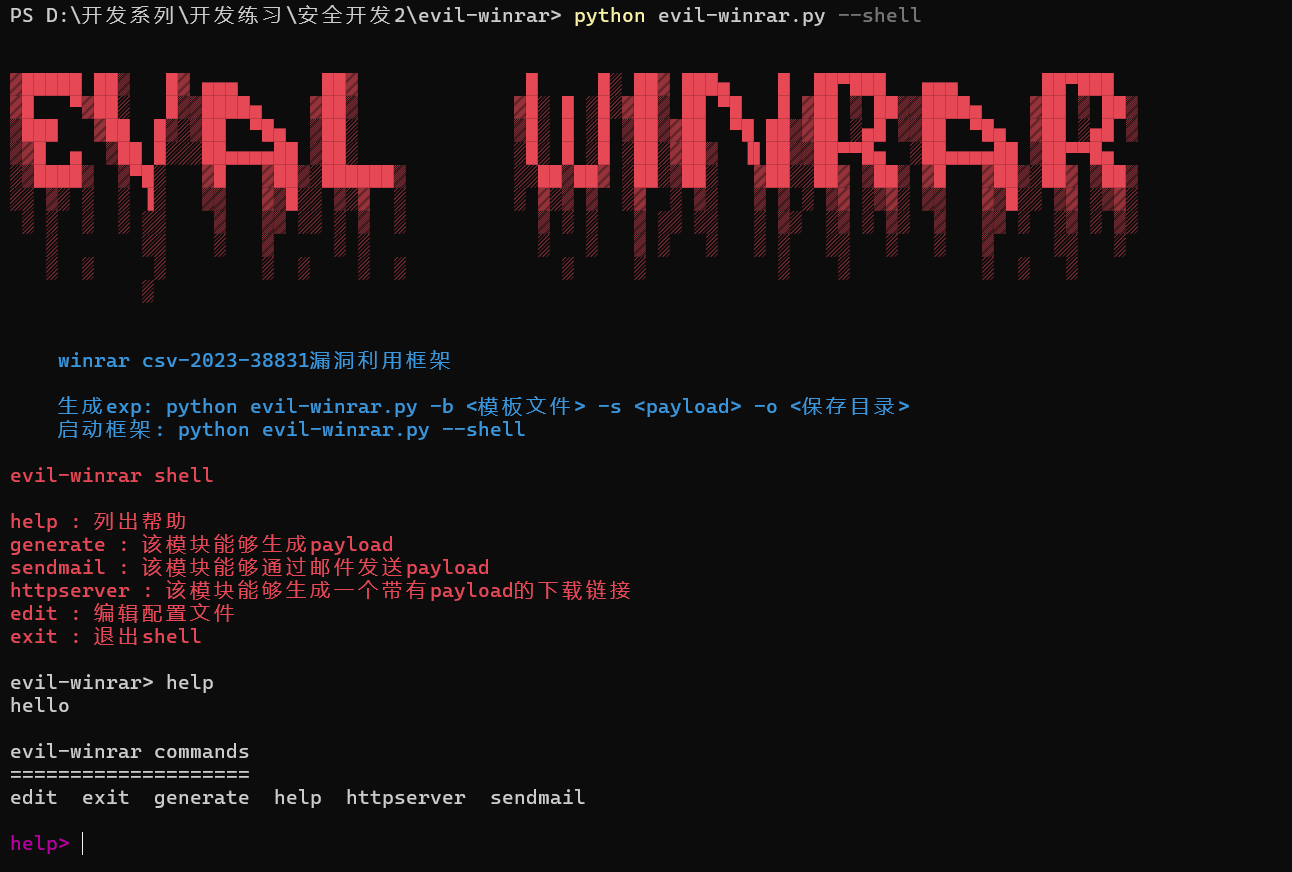
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)

macOS Initial Access Payload Generator

Collection of tools to use with Azure Applications

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.

Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.

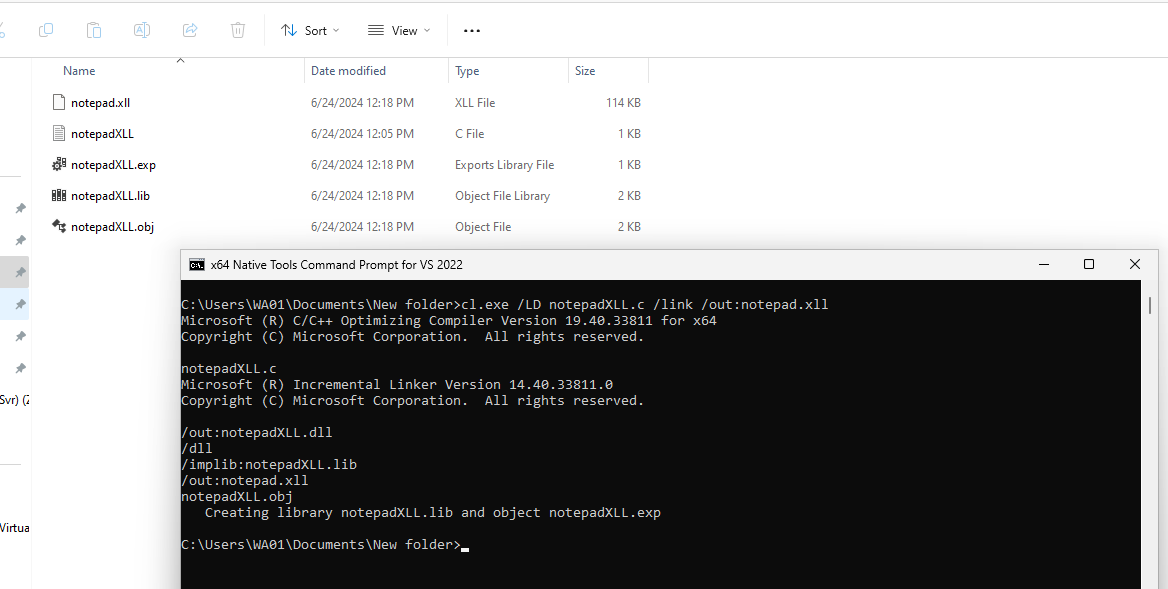
xll windows reverse shell

Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…

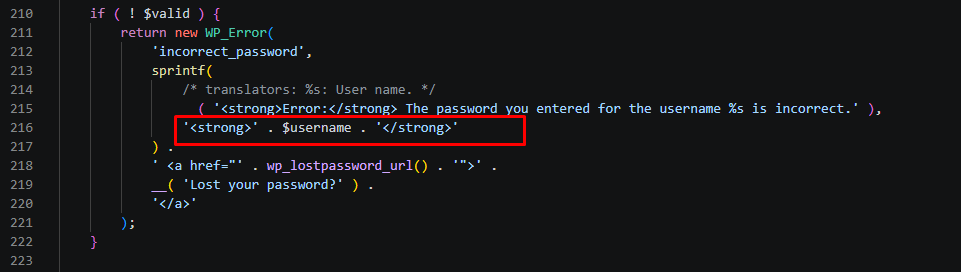
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…

Embed and hide any file in an HTML file

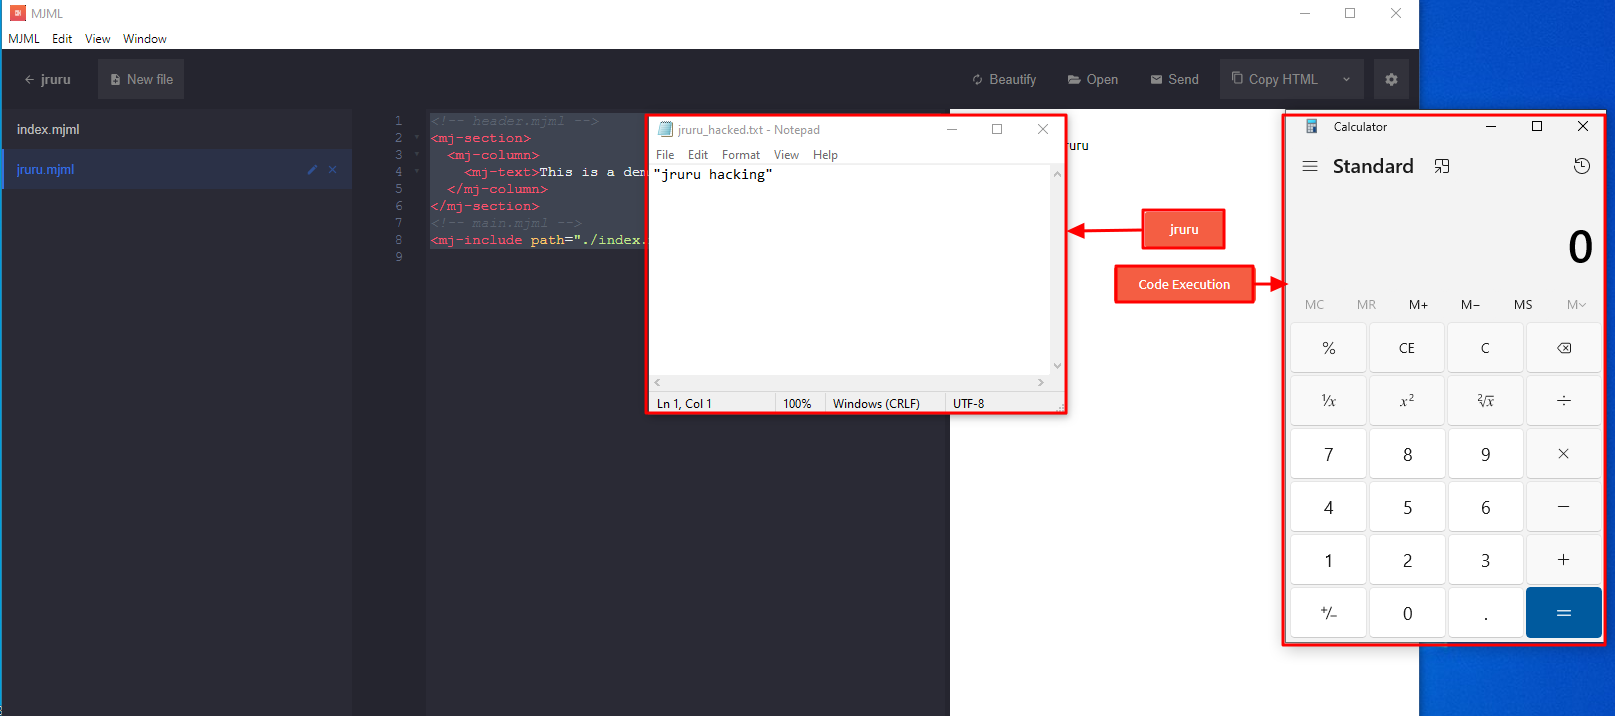
mjml-app v3.0.4 & 3.1.0-beta RCE exploit

Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.

If an authenticated user who is able to edit Wordpress PHP code in any kind, clicks a malicious link, PHP code can be edited through XSS in…