

Facad1ng
 spyboy-productions/facad1ng
Open-source URL masking & analysis tool for security research, phishing awareness, and defensive testing. Demonstrates adversary techniques used to…
defensive-toolseducationphishing+3
529
spyboy-productions/facad1ngOpen-source URL masking & analysis tool for security research, phishing awareness, and defensive testing. Demonstrates adversary techniques used to…
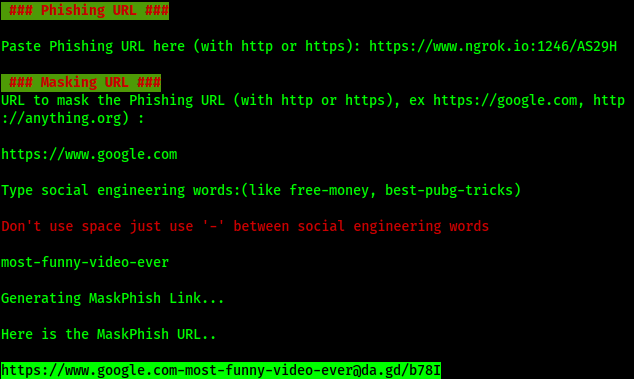 jaykali/maskphish
Introducing "URL Making Technology" to the world for the very FIRST TIME. Give a Mask to Phishing URL like a PRO.. A MUST have tool for Phishing.
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 lxance-hacker/lxancephisher
Automated phishing simulation tool with 30+ login page templates, URL masking, and multiple tunneling options (Ngrok, Cloudflared, Serveo) for…
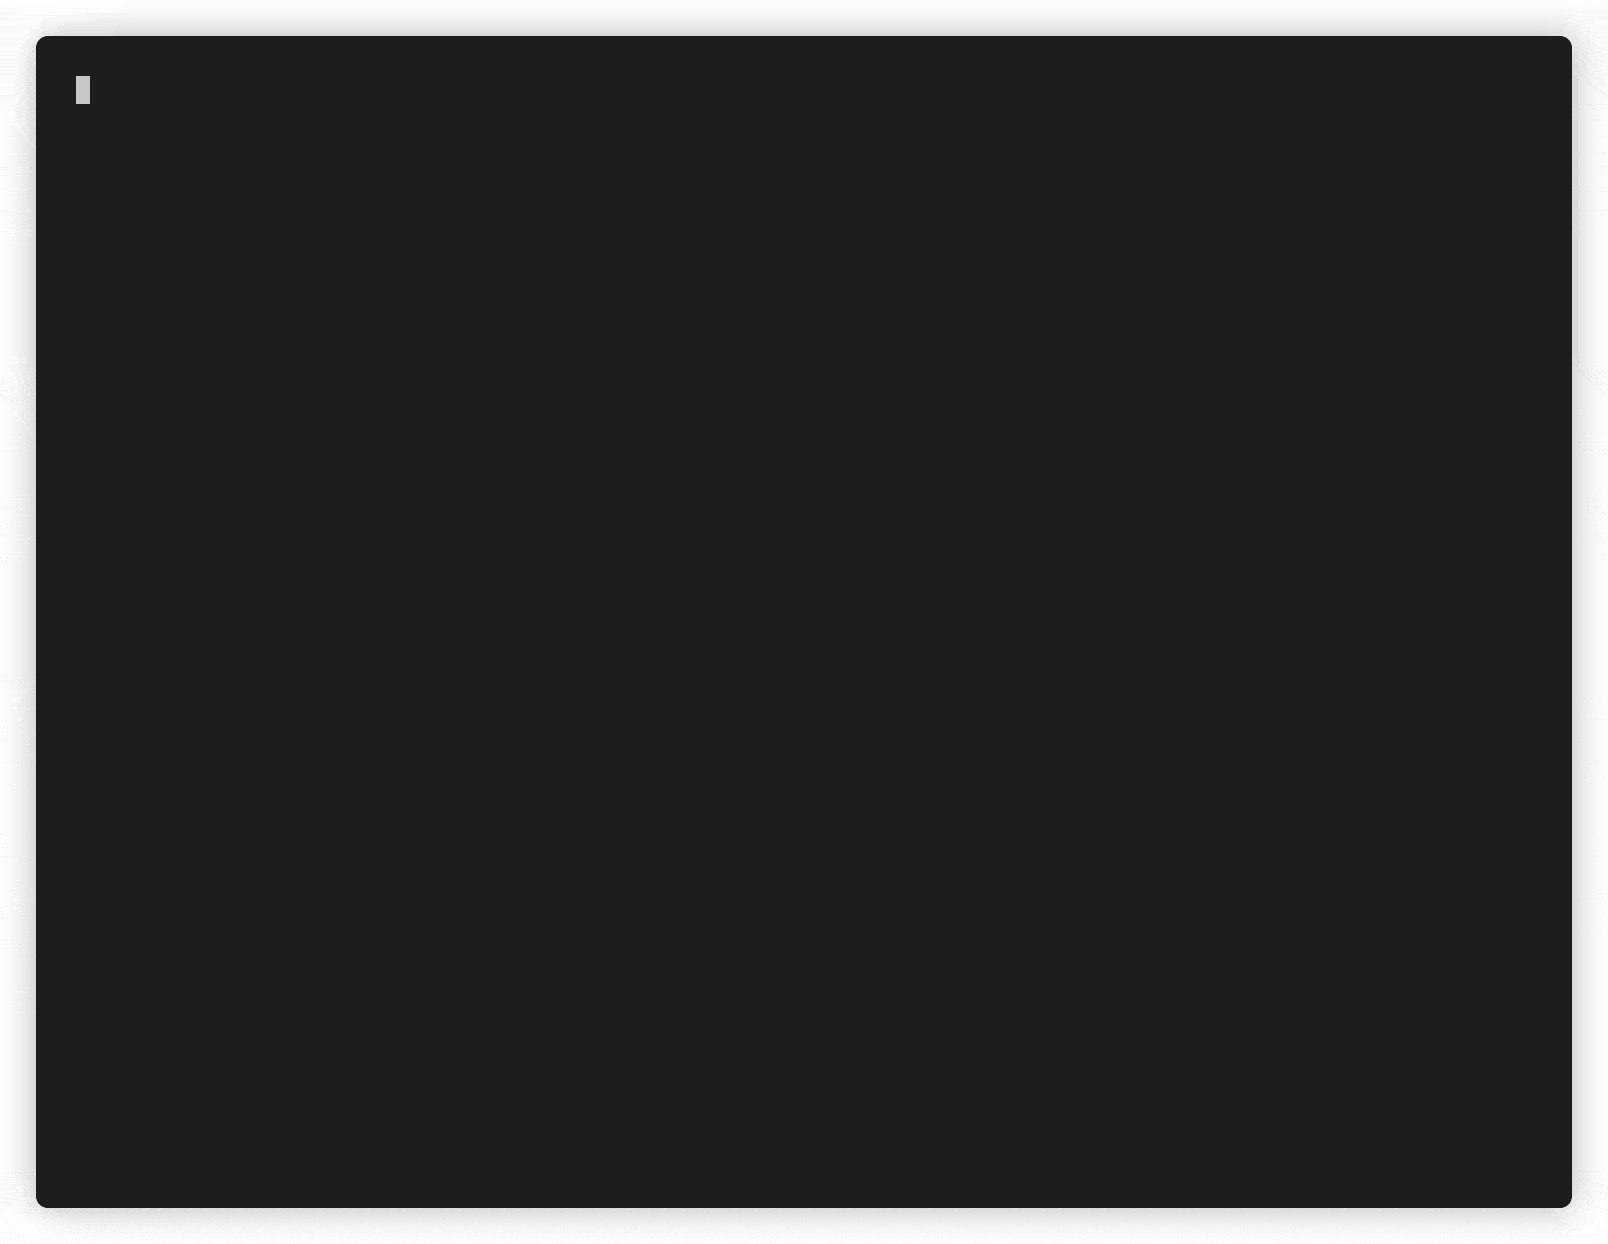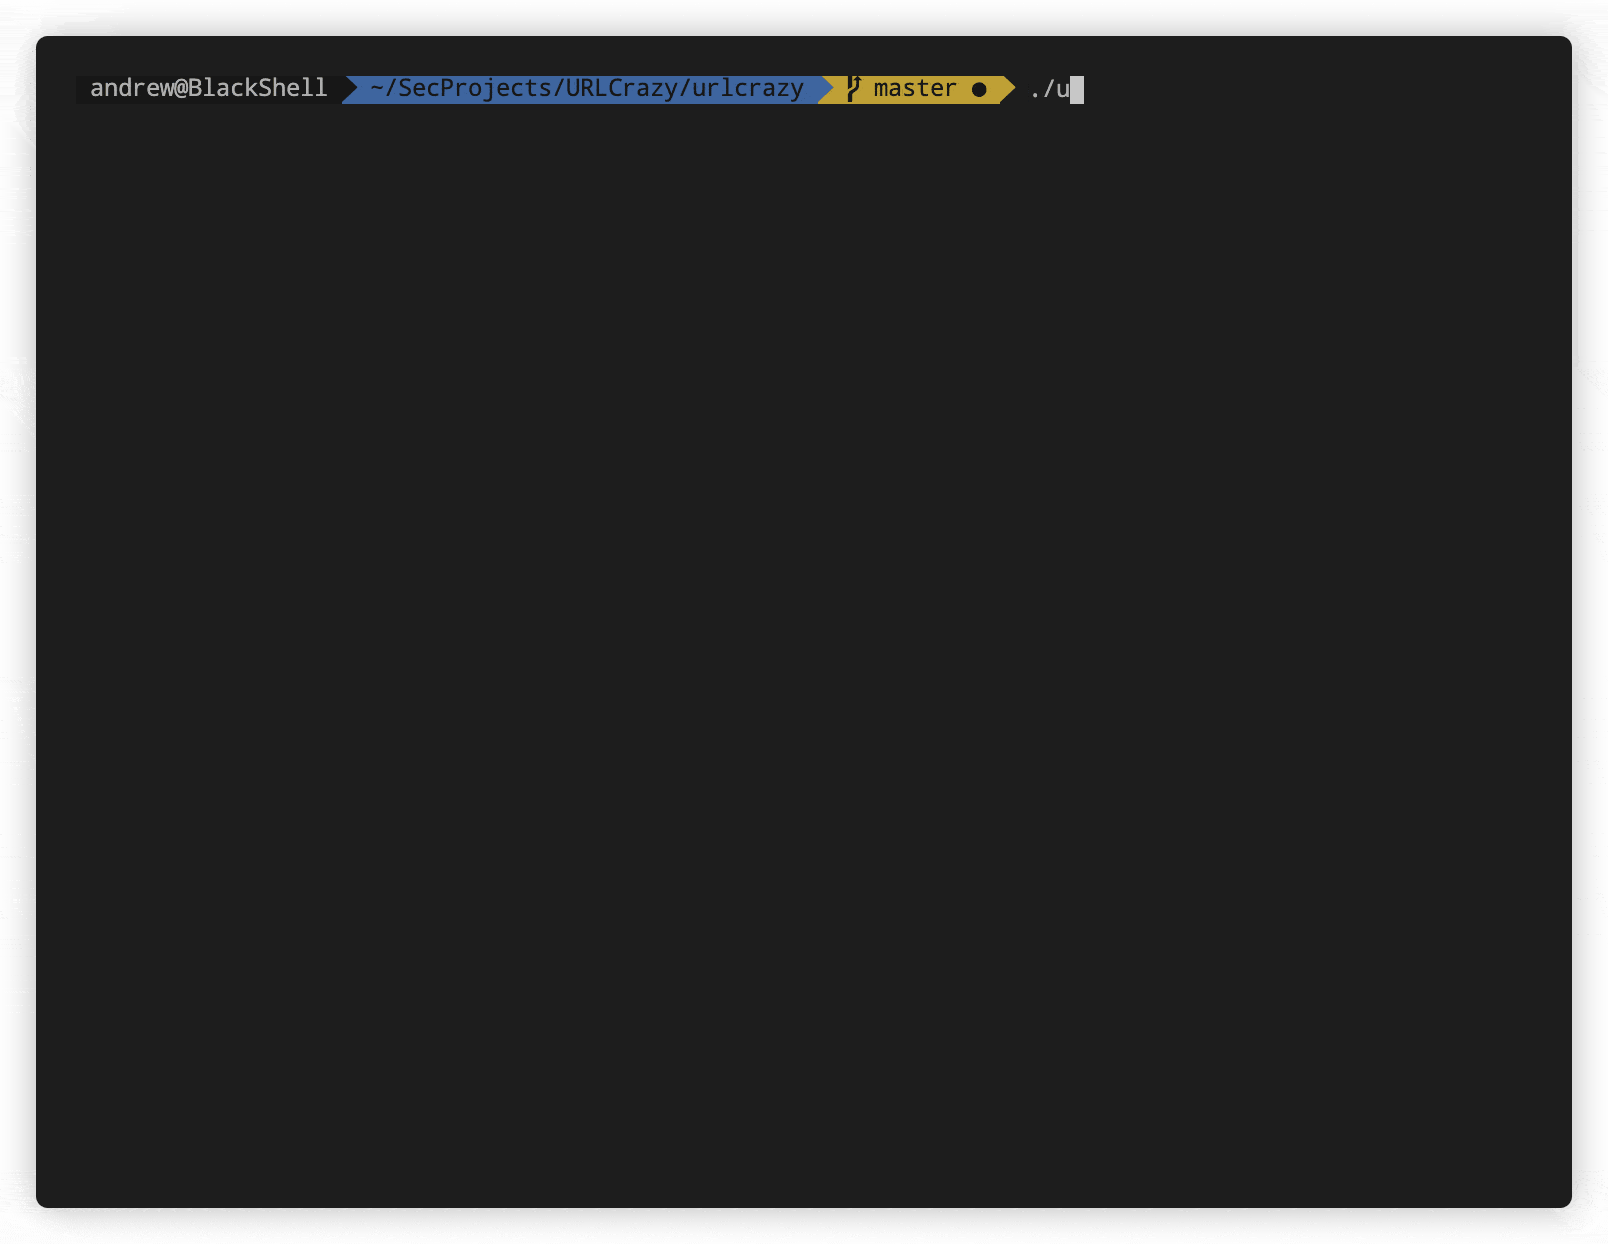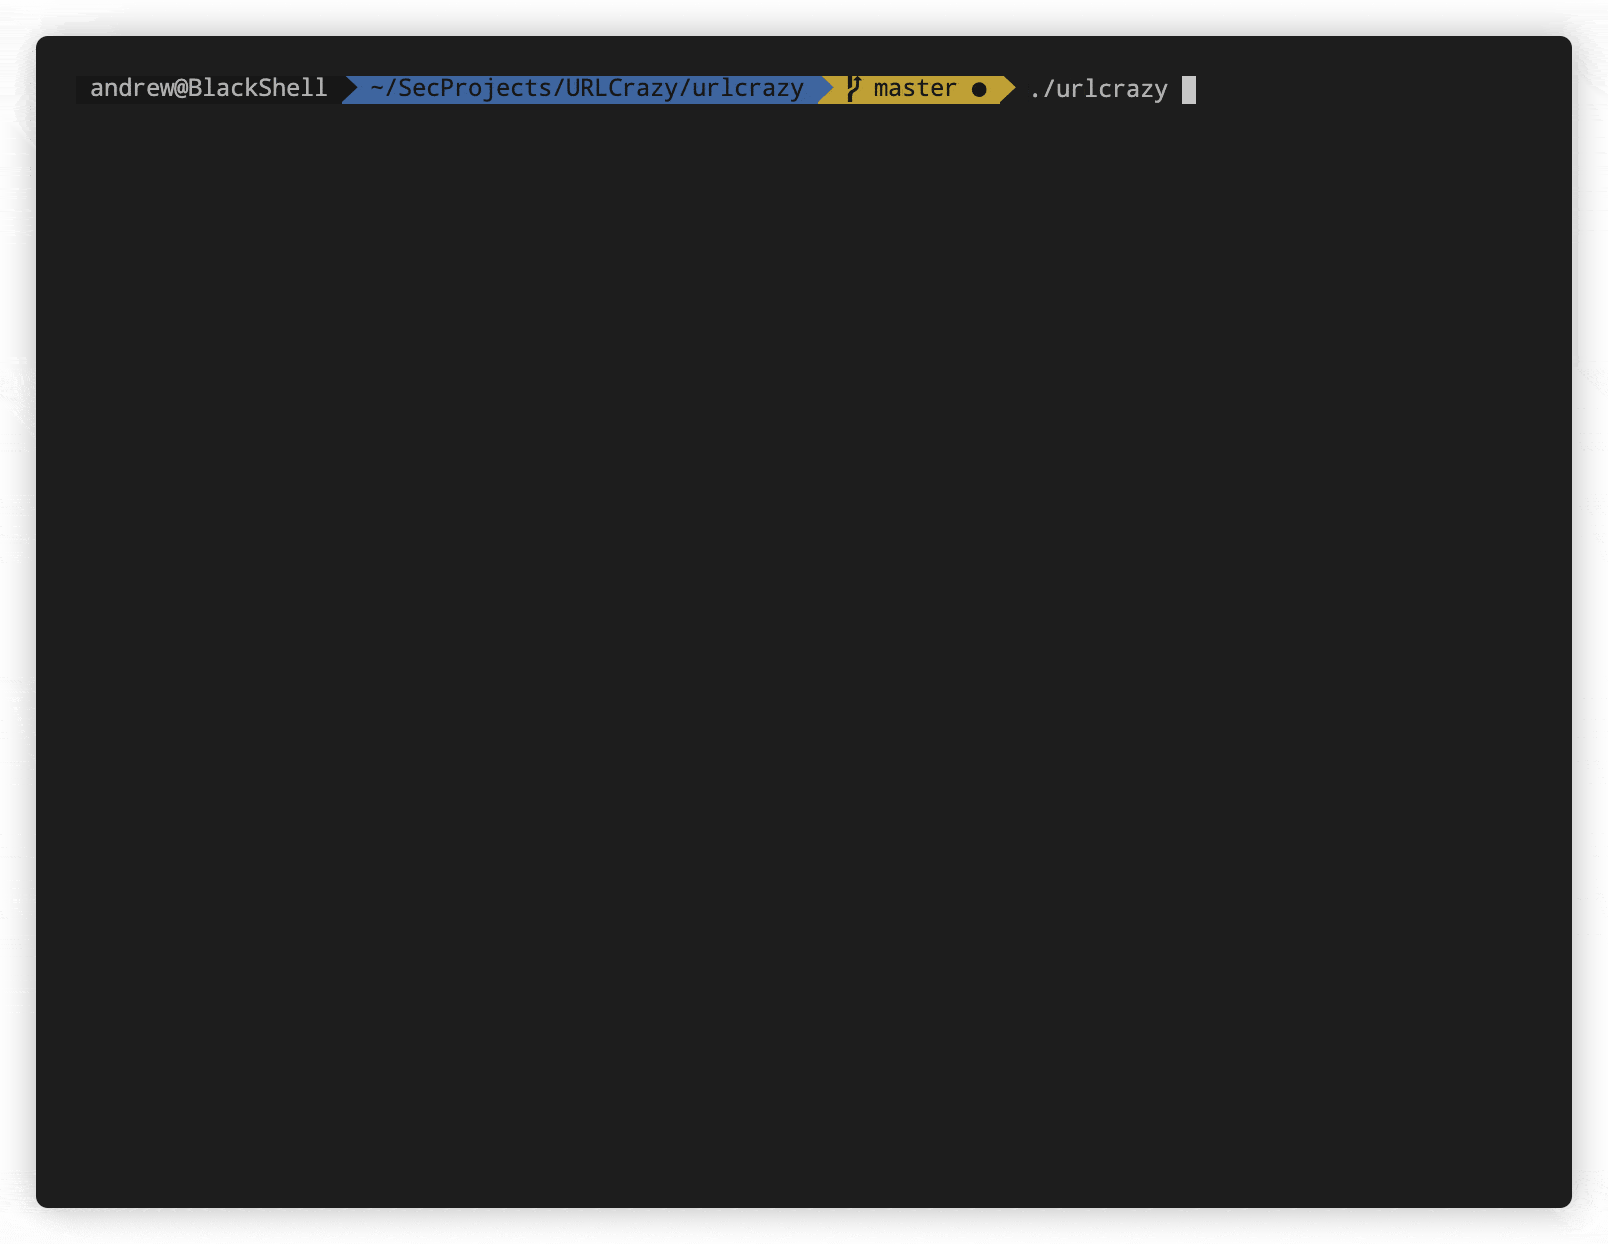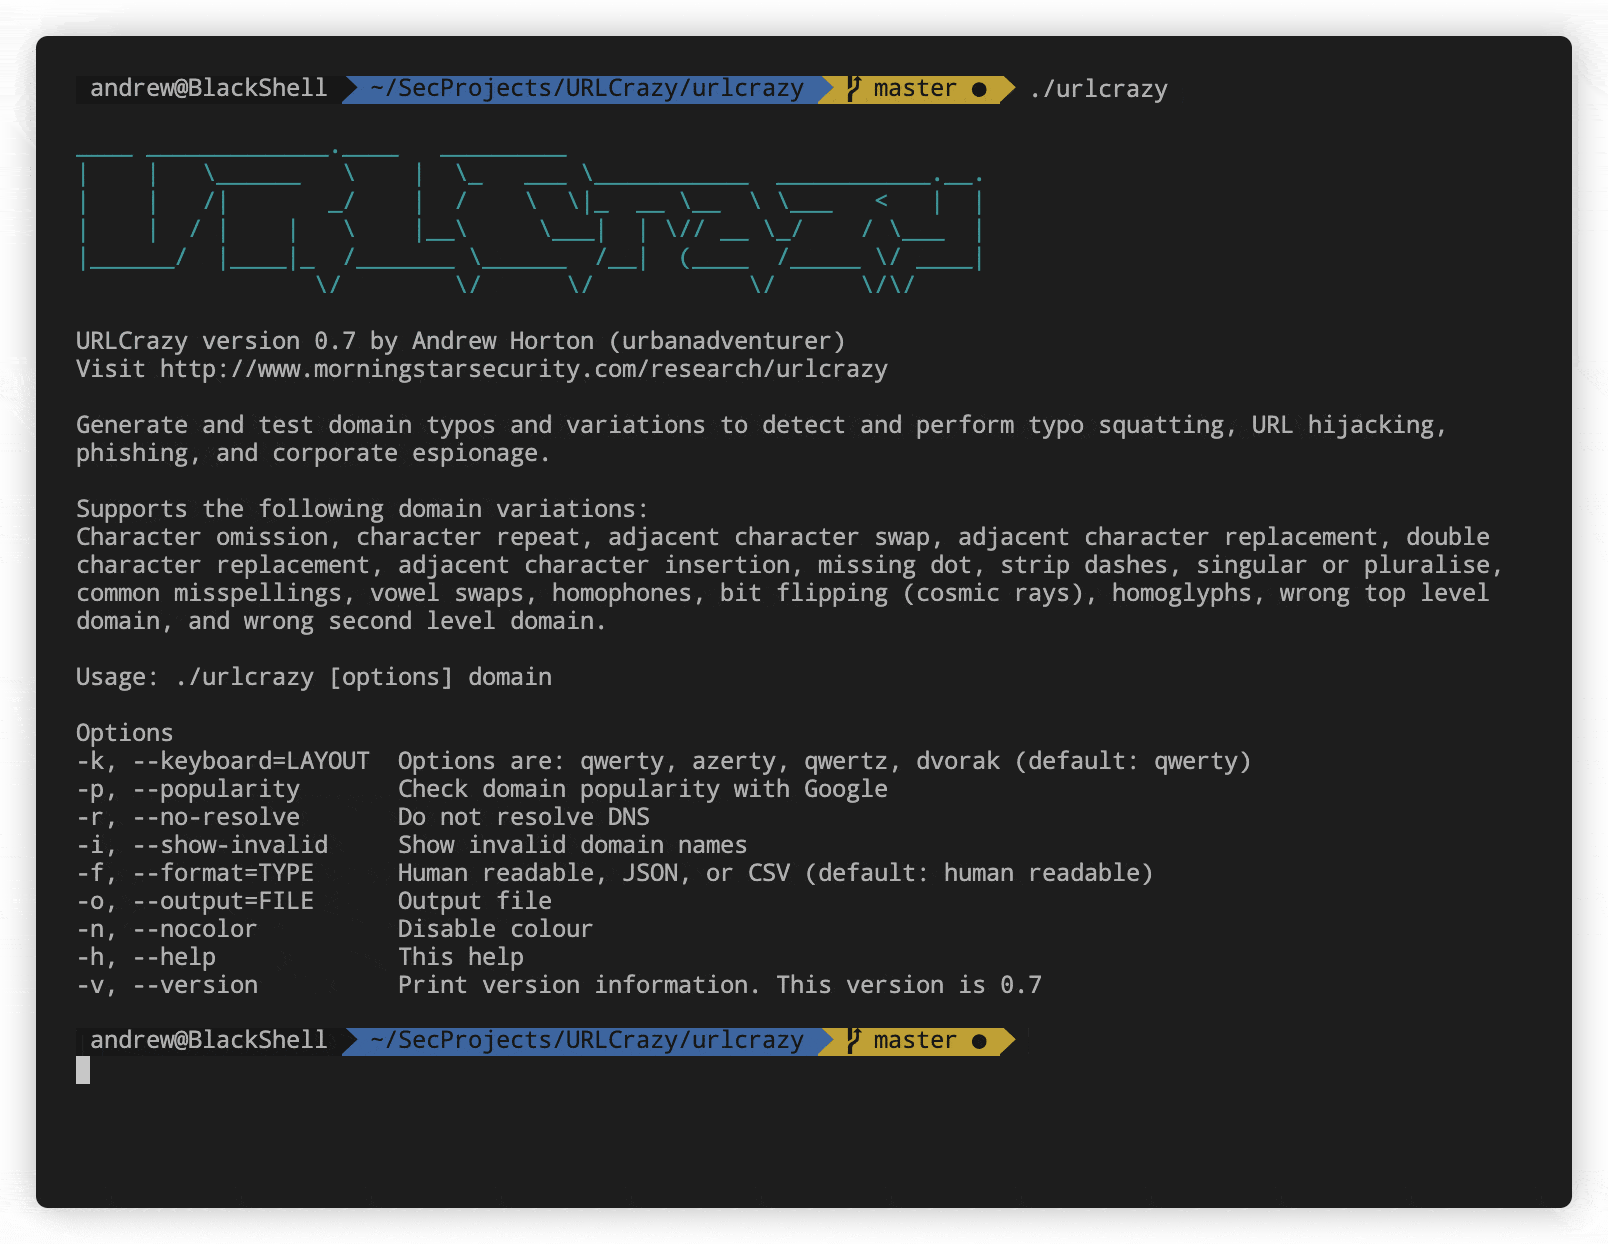 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.
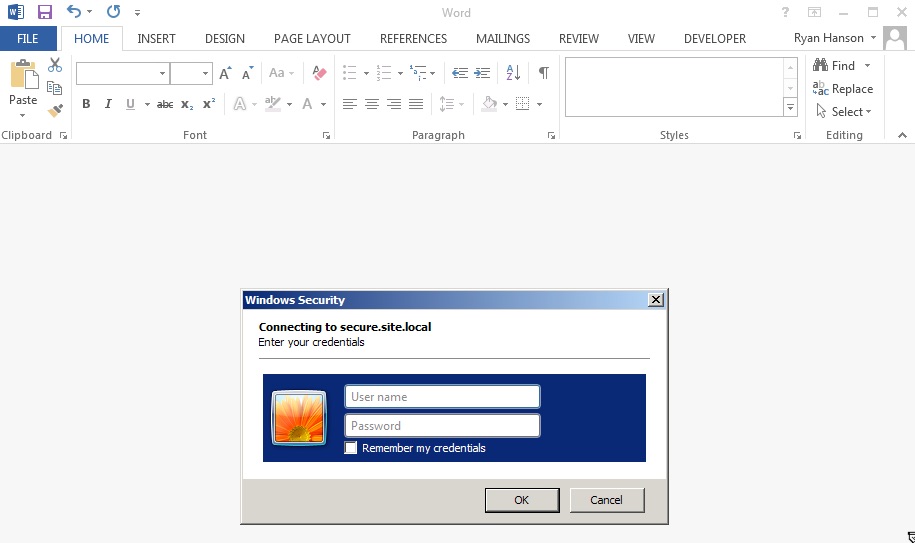 ryhanson/phishery
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector
 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 rat5ak/cve-2025-59382-qnap-password-reset-account-takeover
Proof-of-concept and technical writeup for CVE-2025-59382, an unauthenticated password reset URL injection in QNAP NAS that enables a…
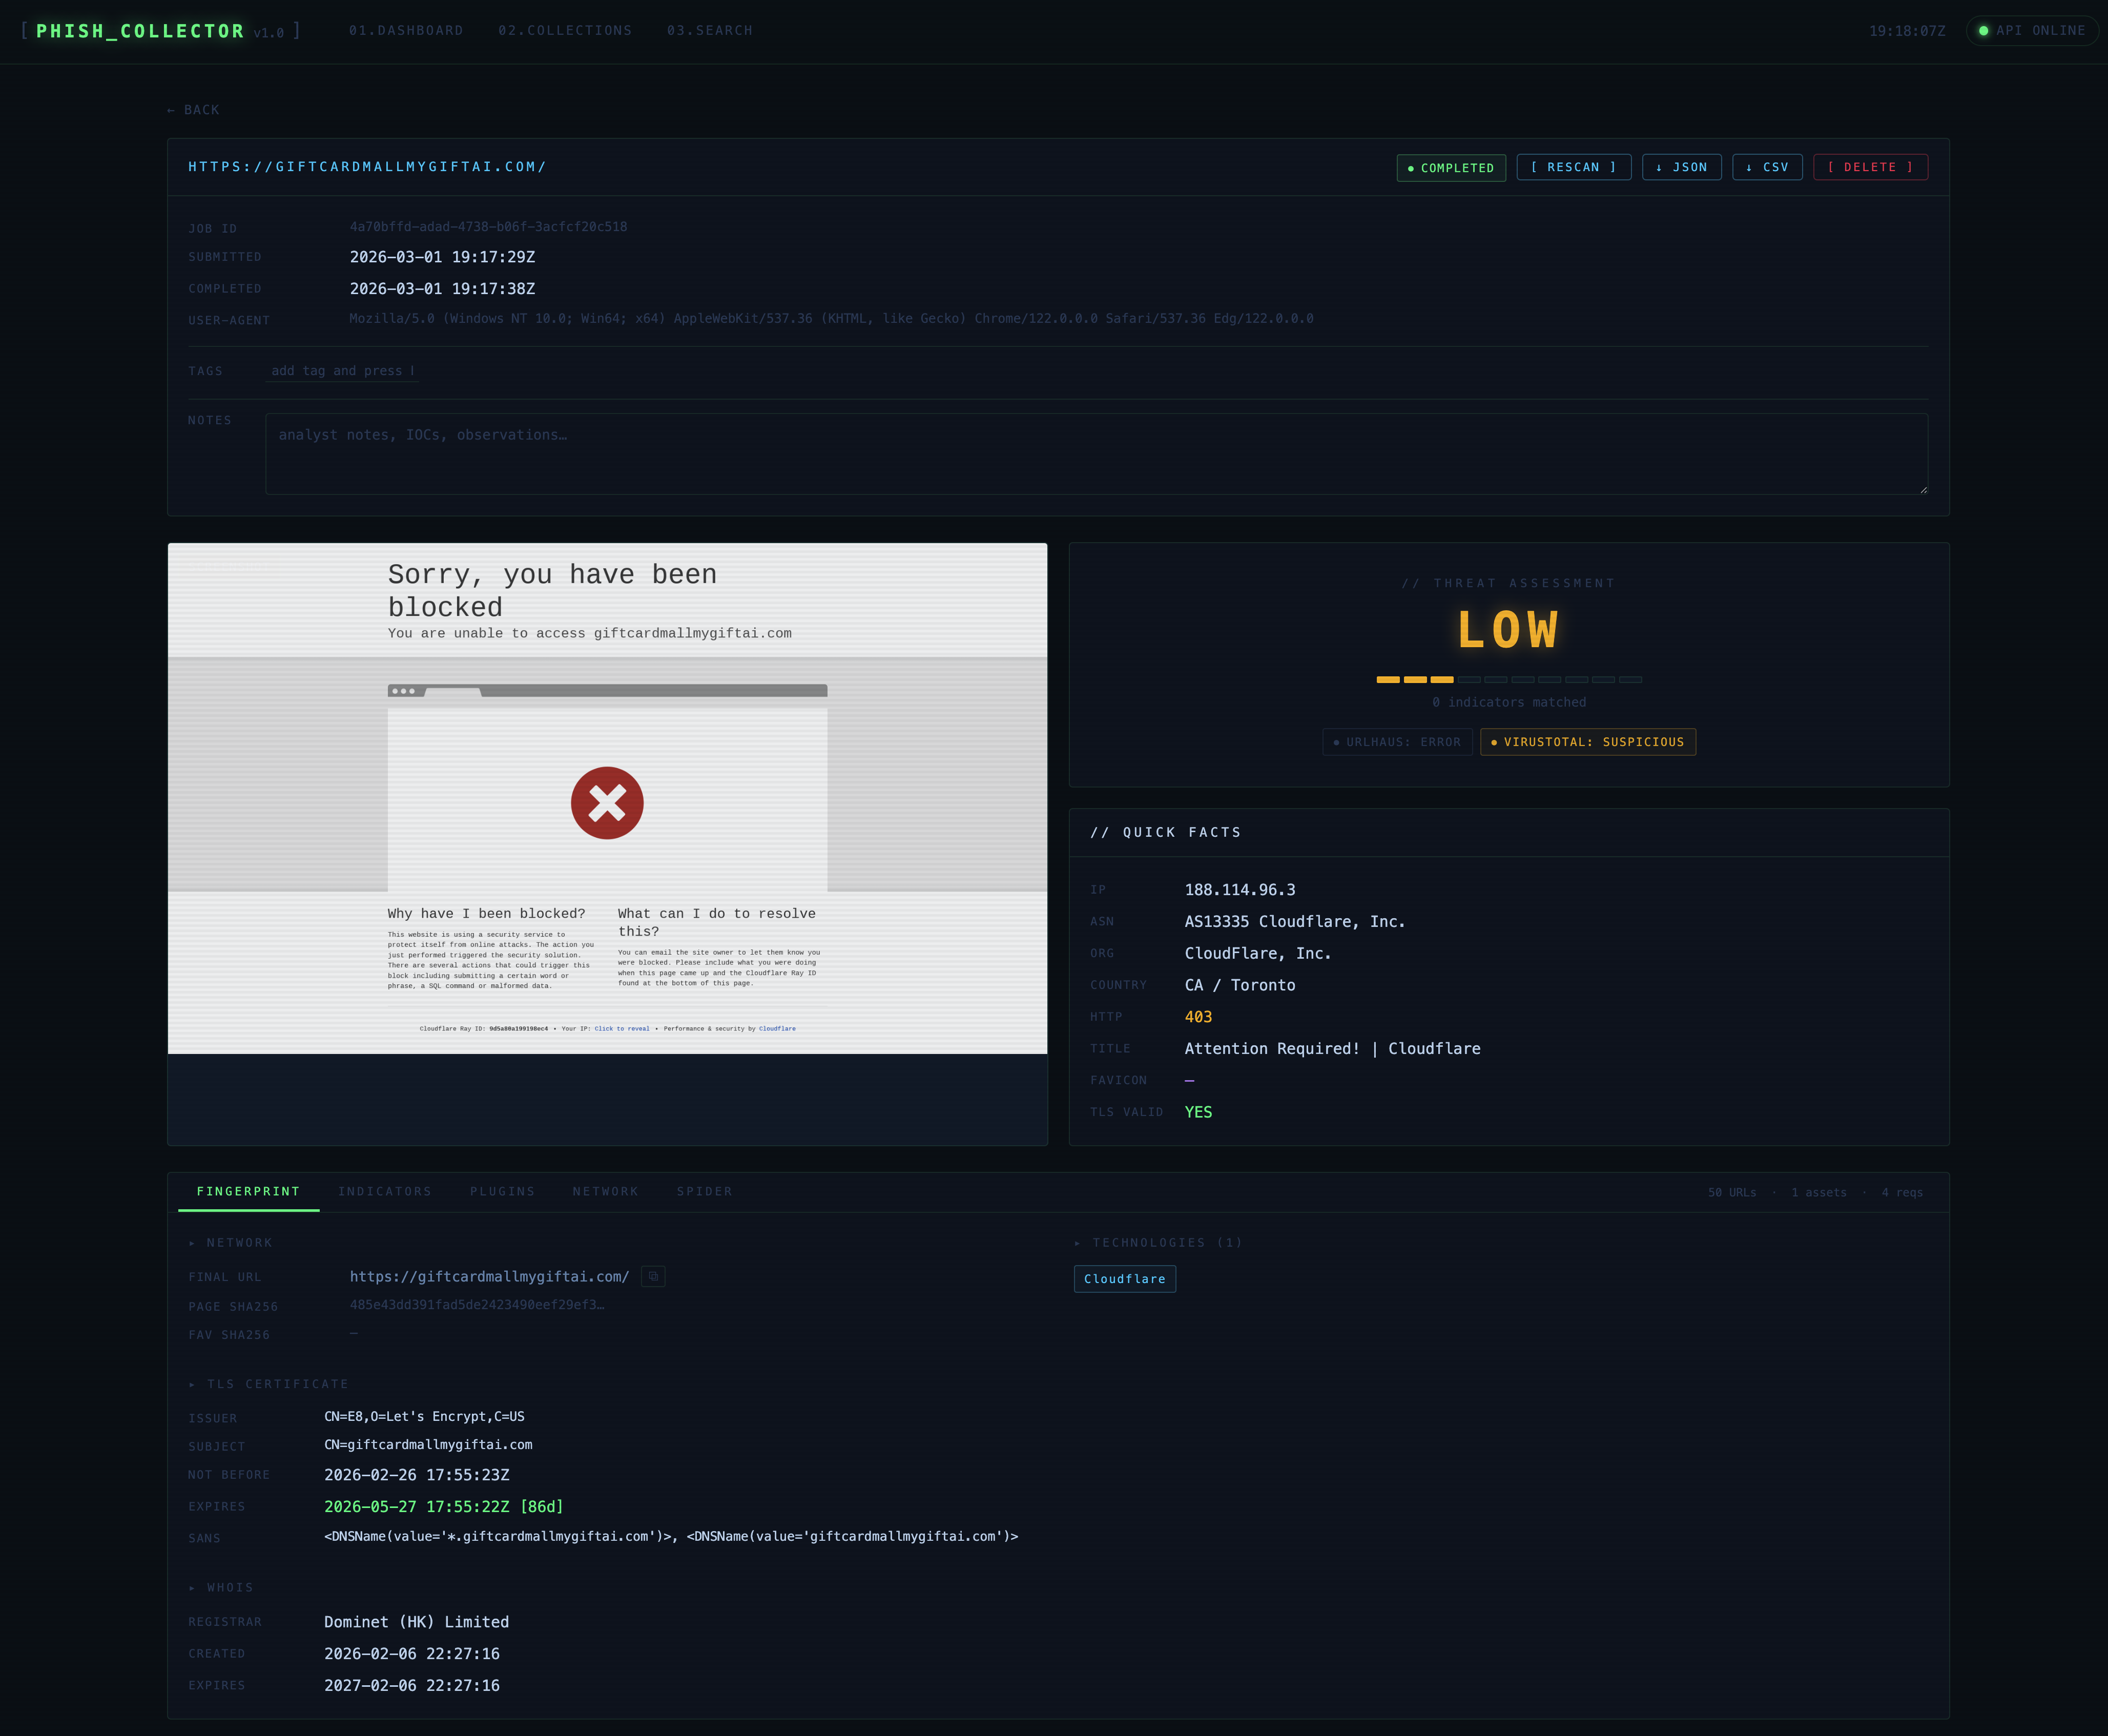 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 makdosx/mip22
Advanced phishing framework with 83 pre-built cloned websites, manual site cloning, URL masking, and real-time credential capture with audio…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 1h3ll/cve-2025-50363_bxss_cve
Proof-of-concept for a blind XSS vulnerability in Maid Hiring Management System v1.0, capturing admin session cookies via a crafted application form…
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 649/cve-2017-5415
Addressbar spoofing through blob URL (Firefox browser). An attack can use a blob URL and script to spoof an arbitrary addressbar URL prefaced by…