
CVE-2021-24563
 v35hr4j/cve-2021-24563
The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…
exploitationpenetration-testingphishing+2
1
v35hr4j/cve-2021-24563The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…
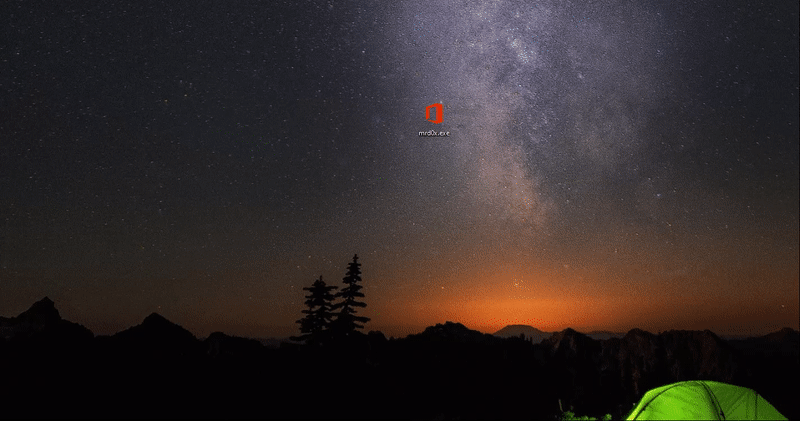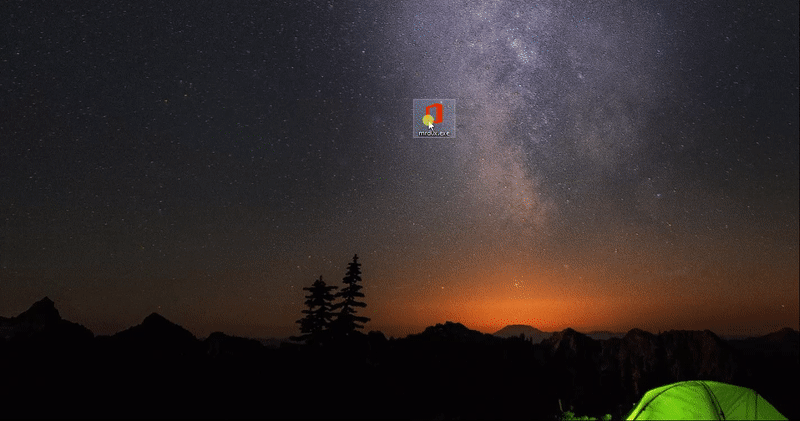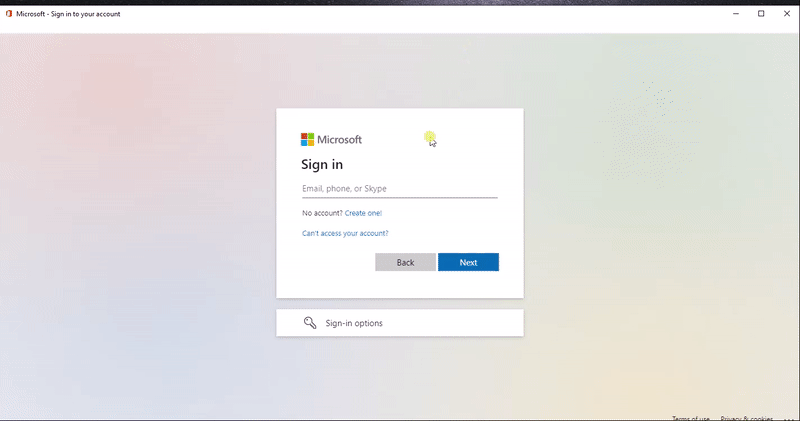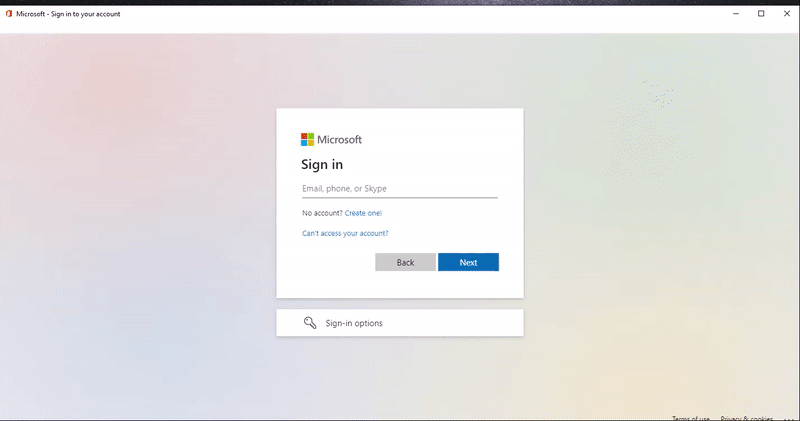 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 techchipnet/camphish
Grab cam shots & GPS location from target's phone front camera or PC webcam just sending a link.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 d4rks3c-group/hiddeneyereborn
HiddenEye Reborn in better shape than ever, rewritten from scratch and adapted to modern world
 jpcertcc/phishurl-list
Phishing URL dataset from JPCERT/CC
 ghost-otpbot/smsotpbot
OTP BOT Bypass SMS verifications from Paypal, Instagram, Snapchat, Google, 3D Secure, and many others...
 chrismaddalena/goreport
A Python script to collect campaign data from Gophish and generate a report
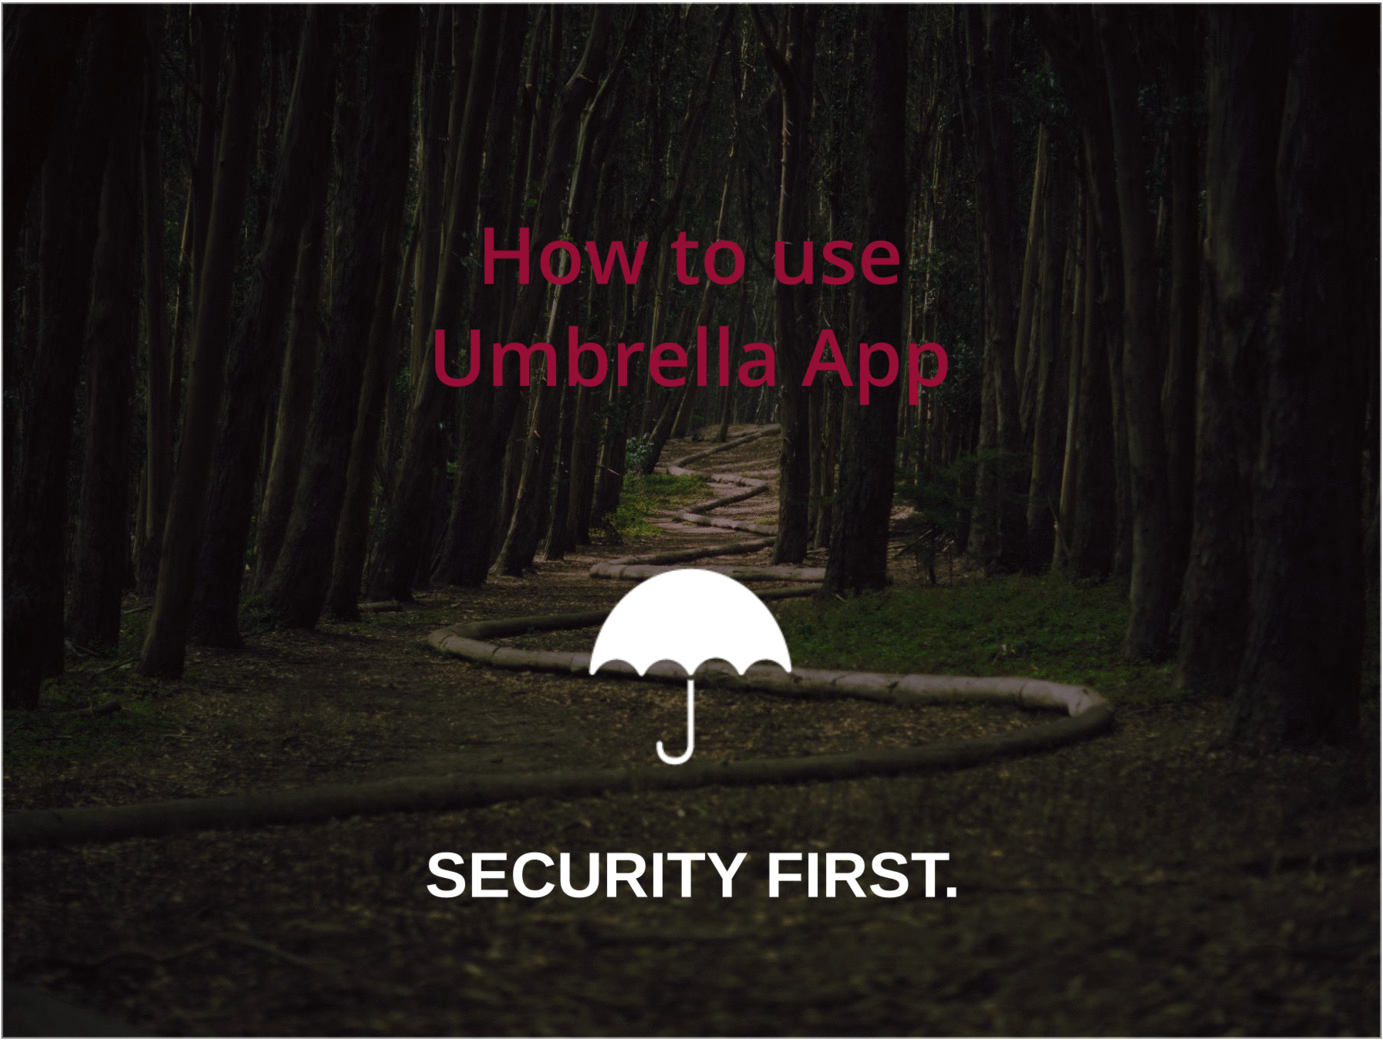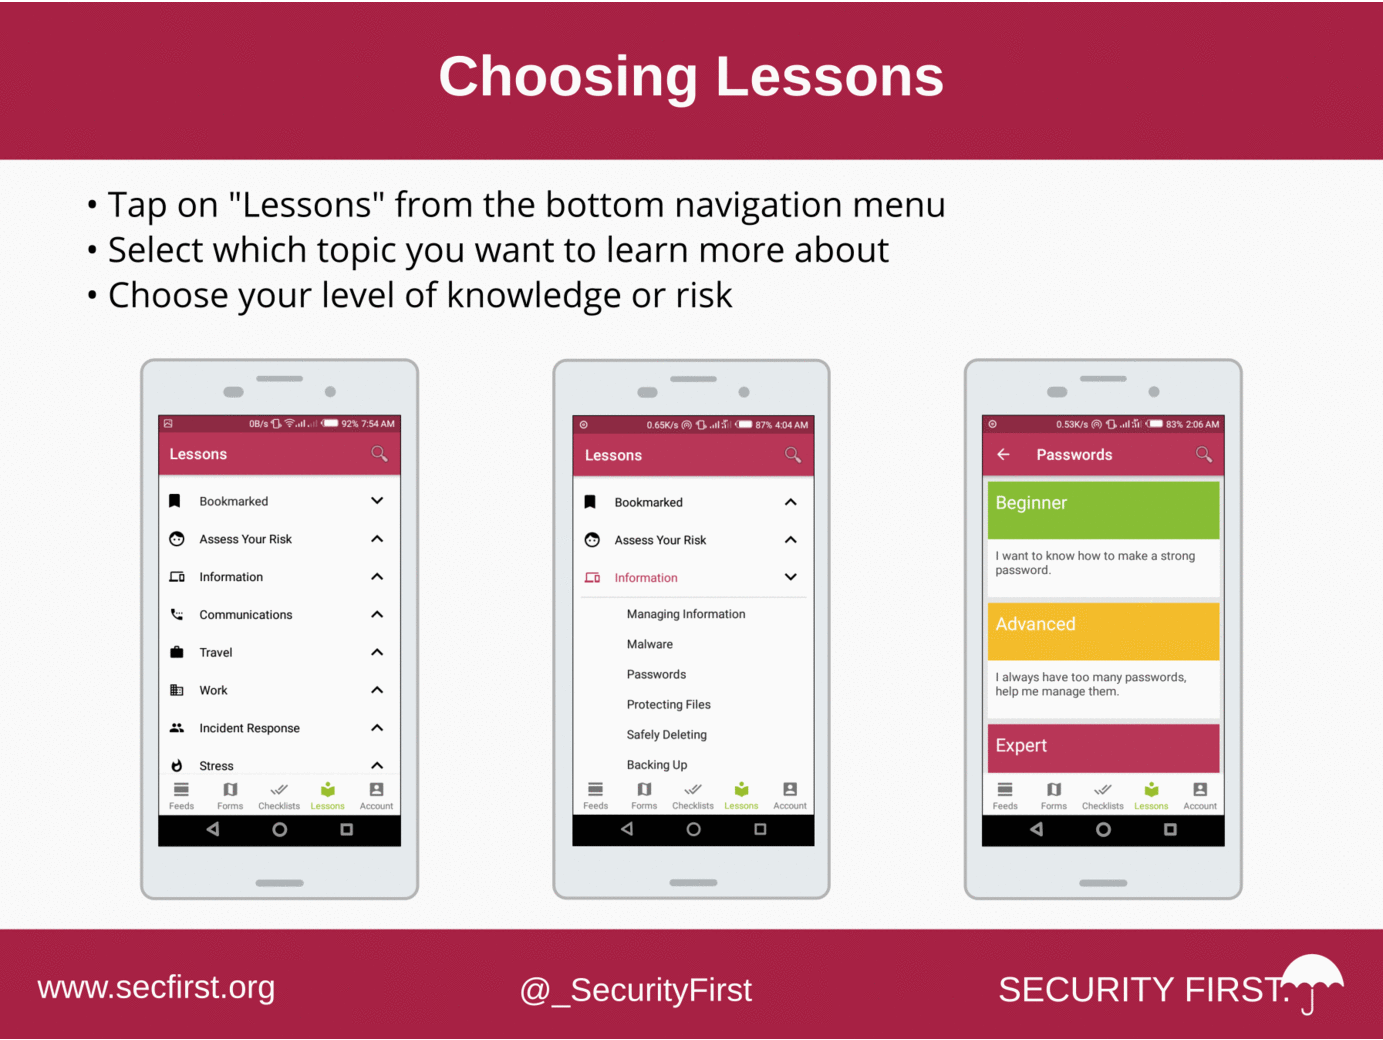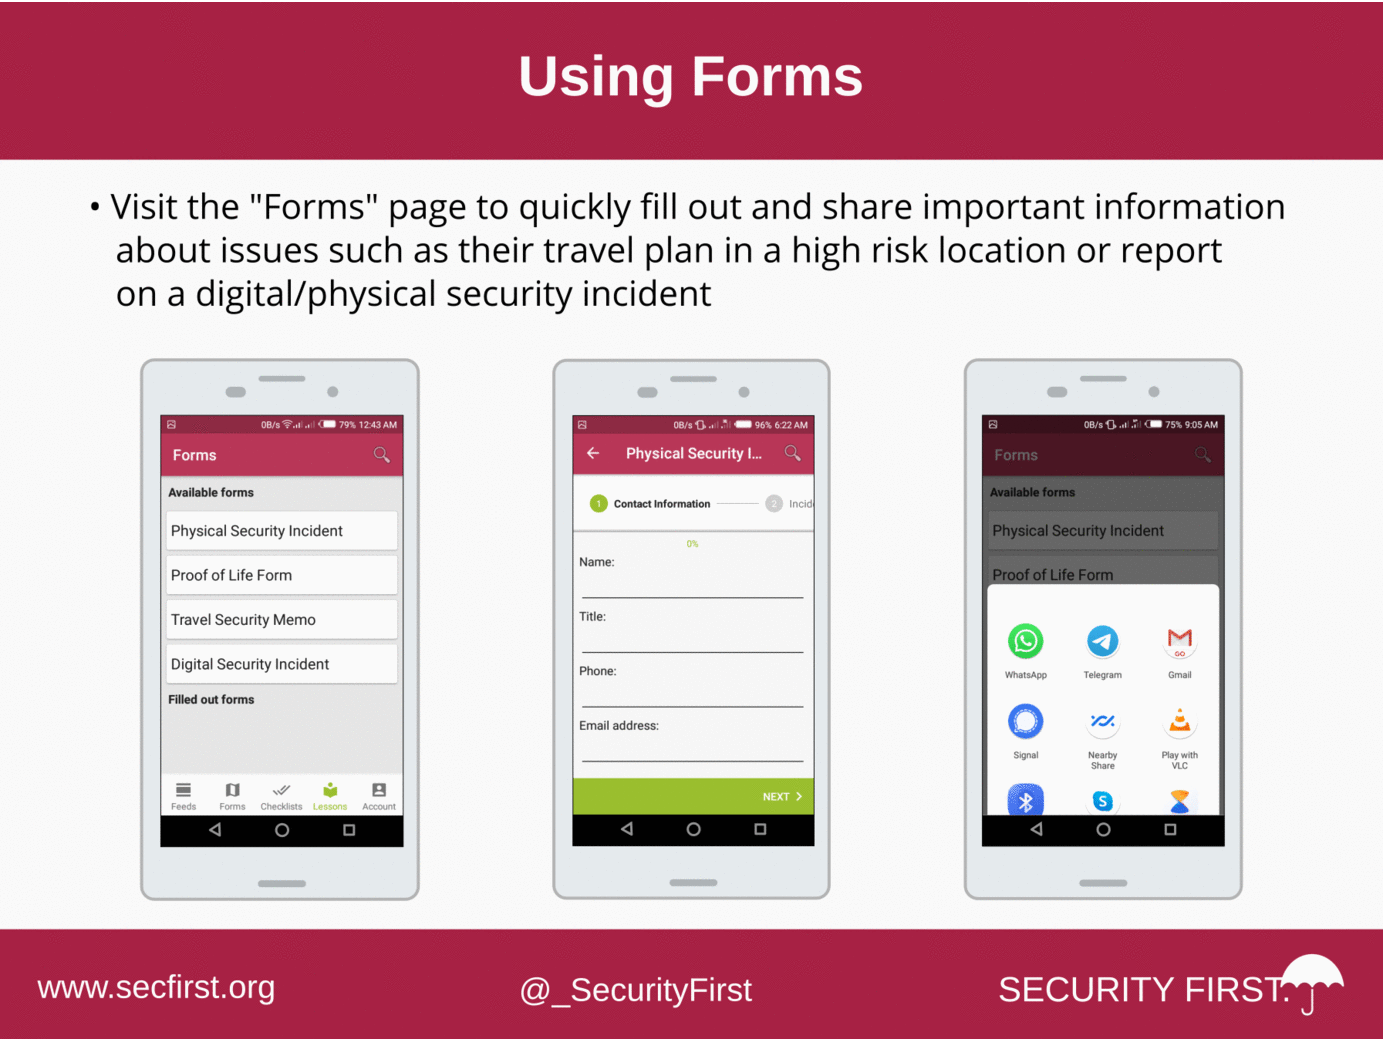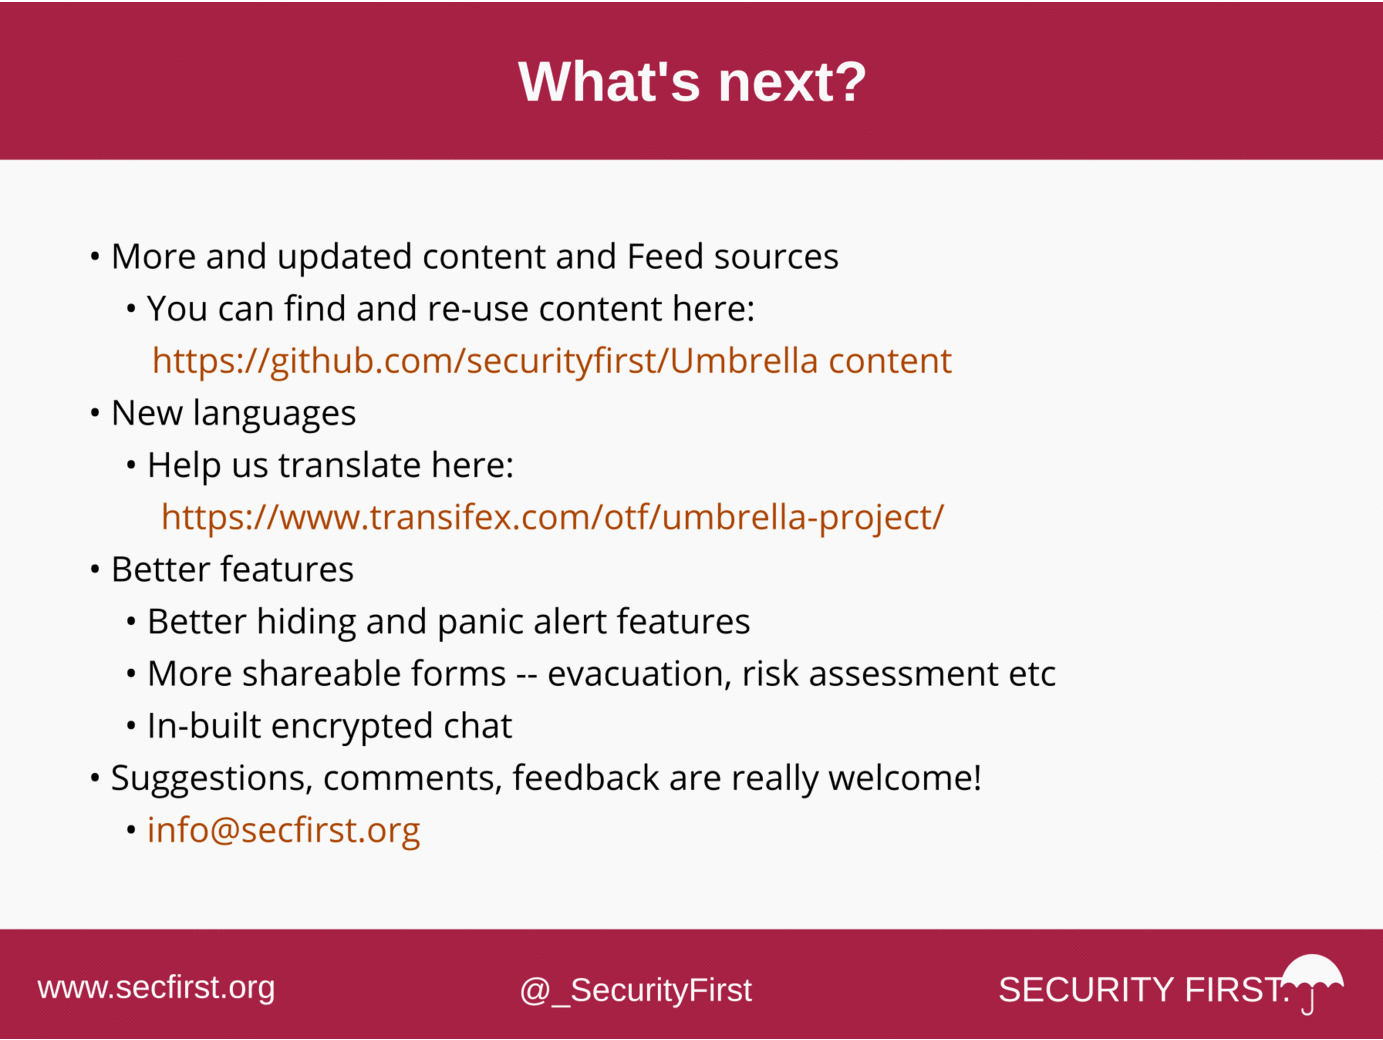 securityfirst/umbrella_android
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…
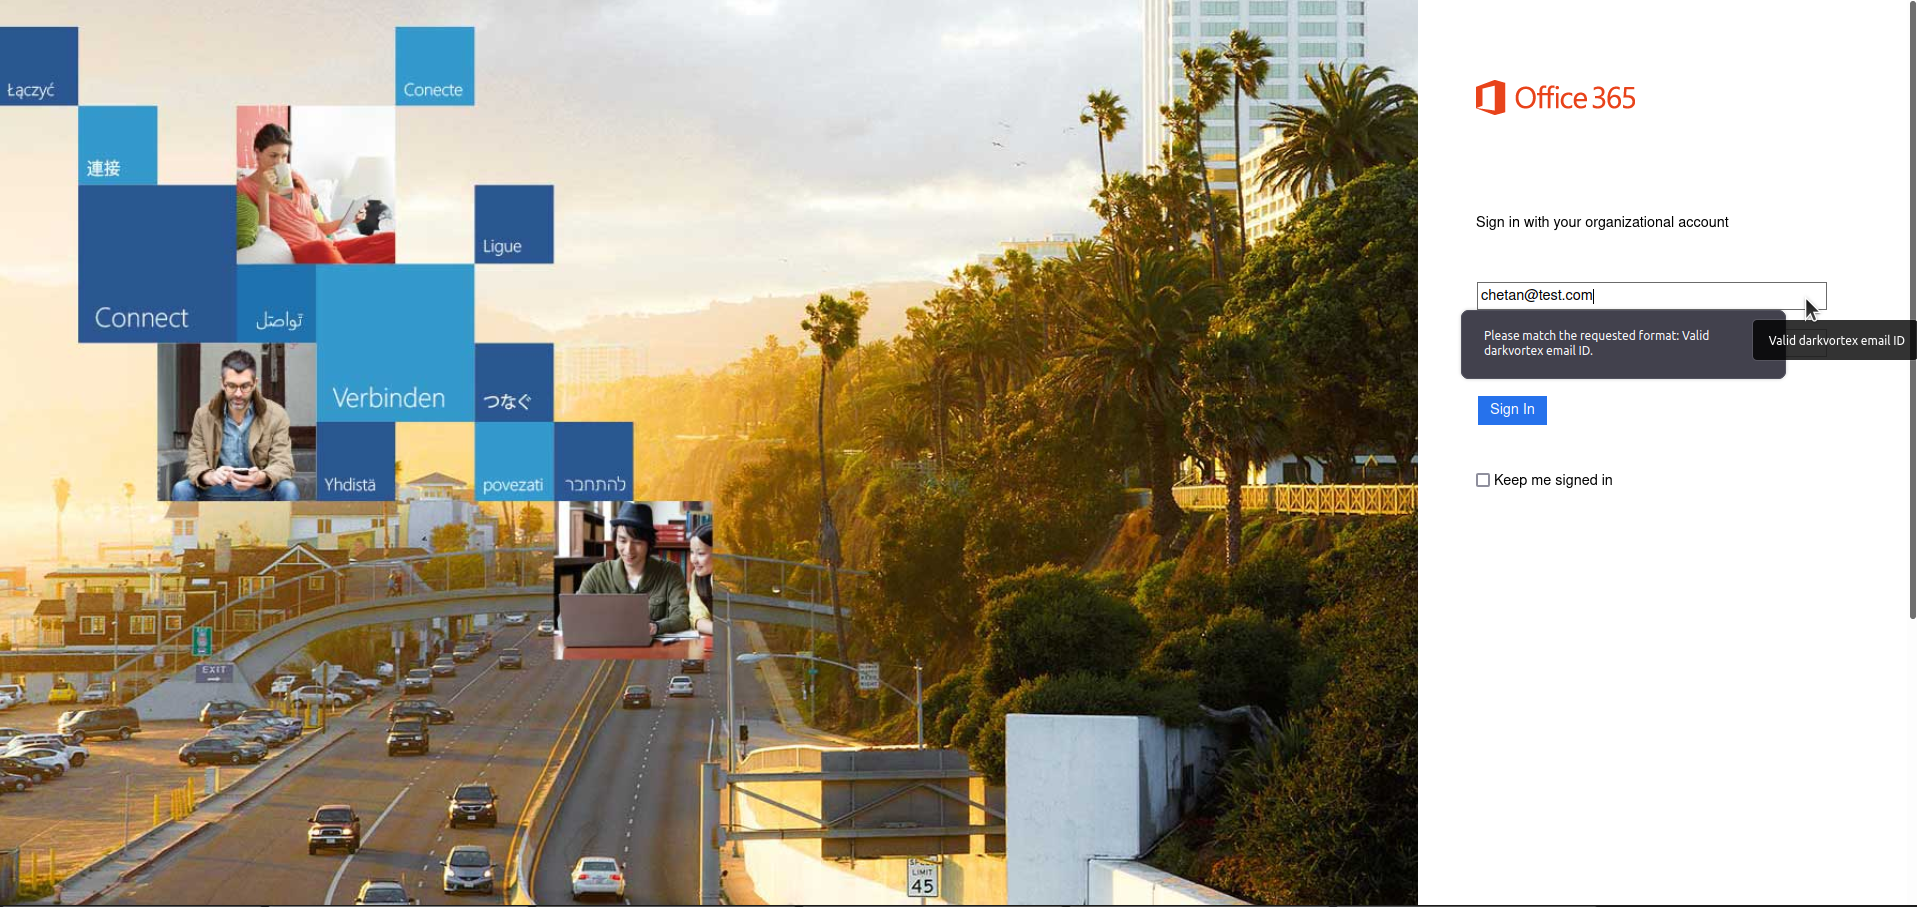 paranoidninja/o365-doppelganger
A quick handy script to harvest credentials off of a user during a Red Team and get execution of a file from the user
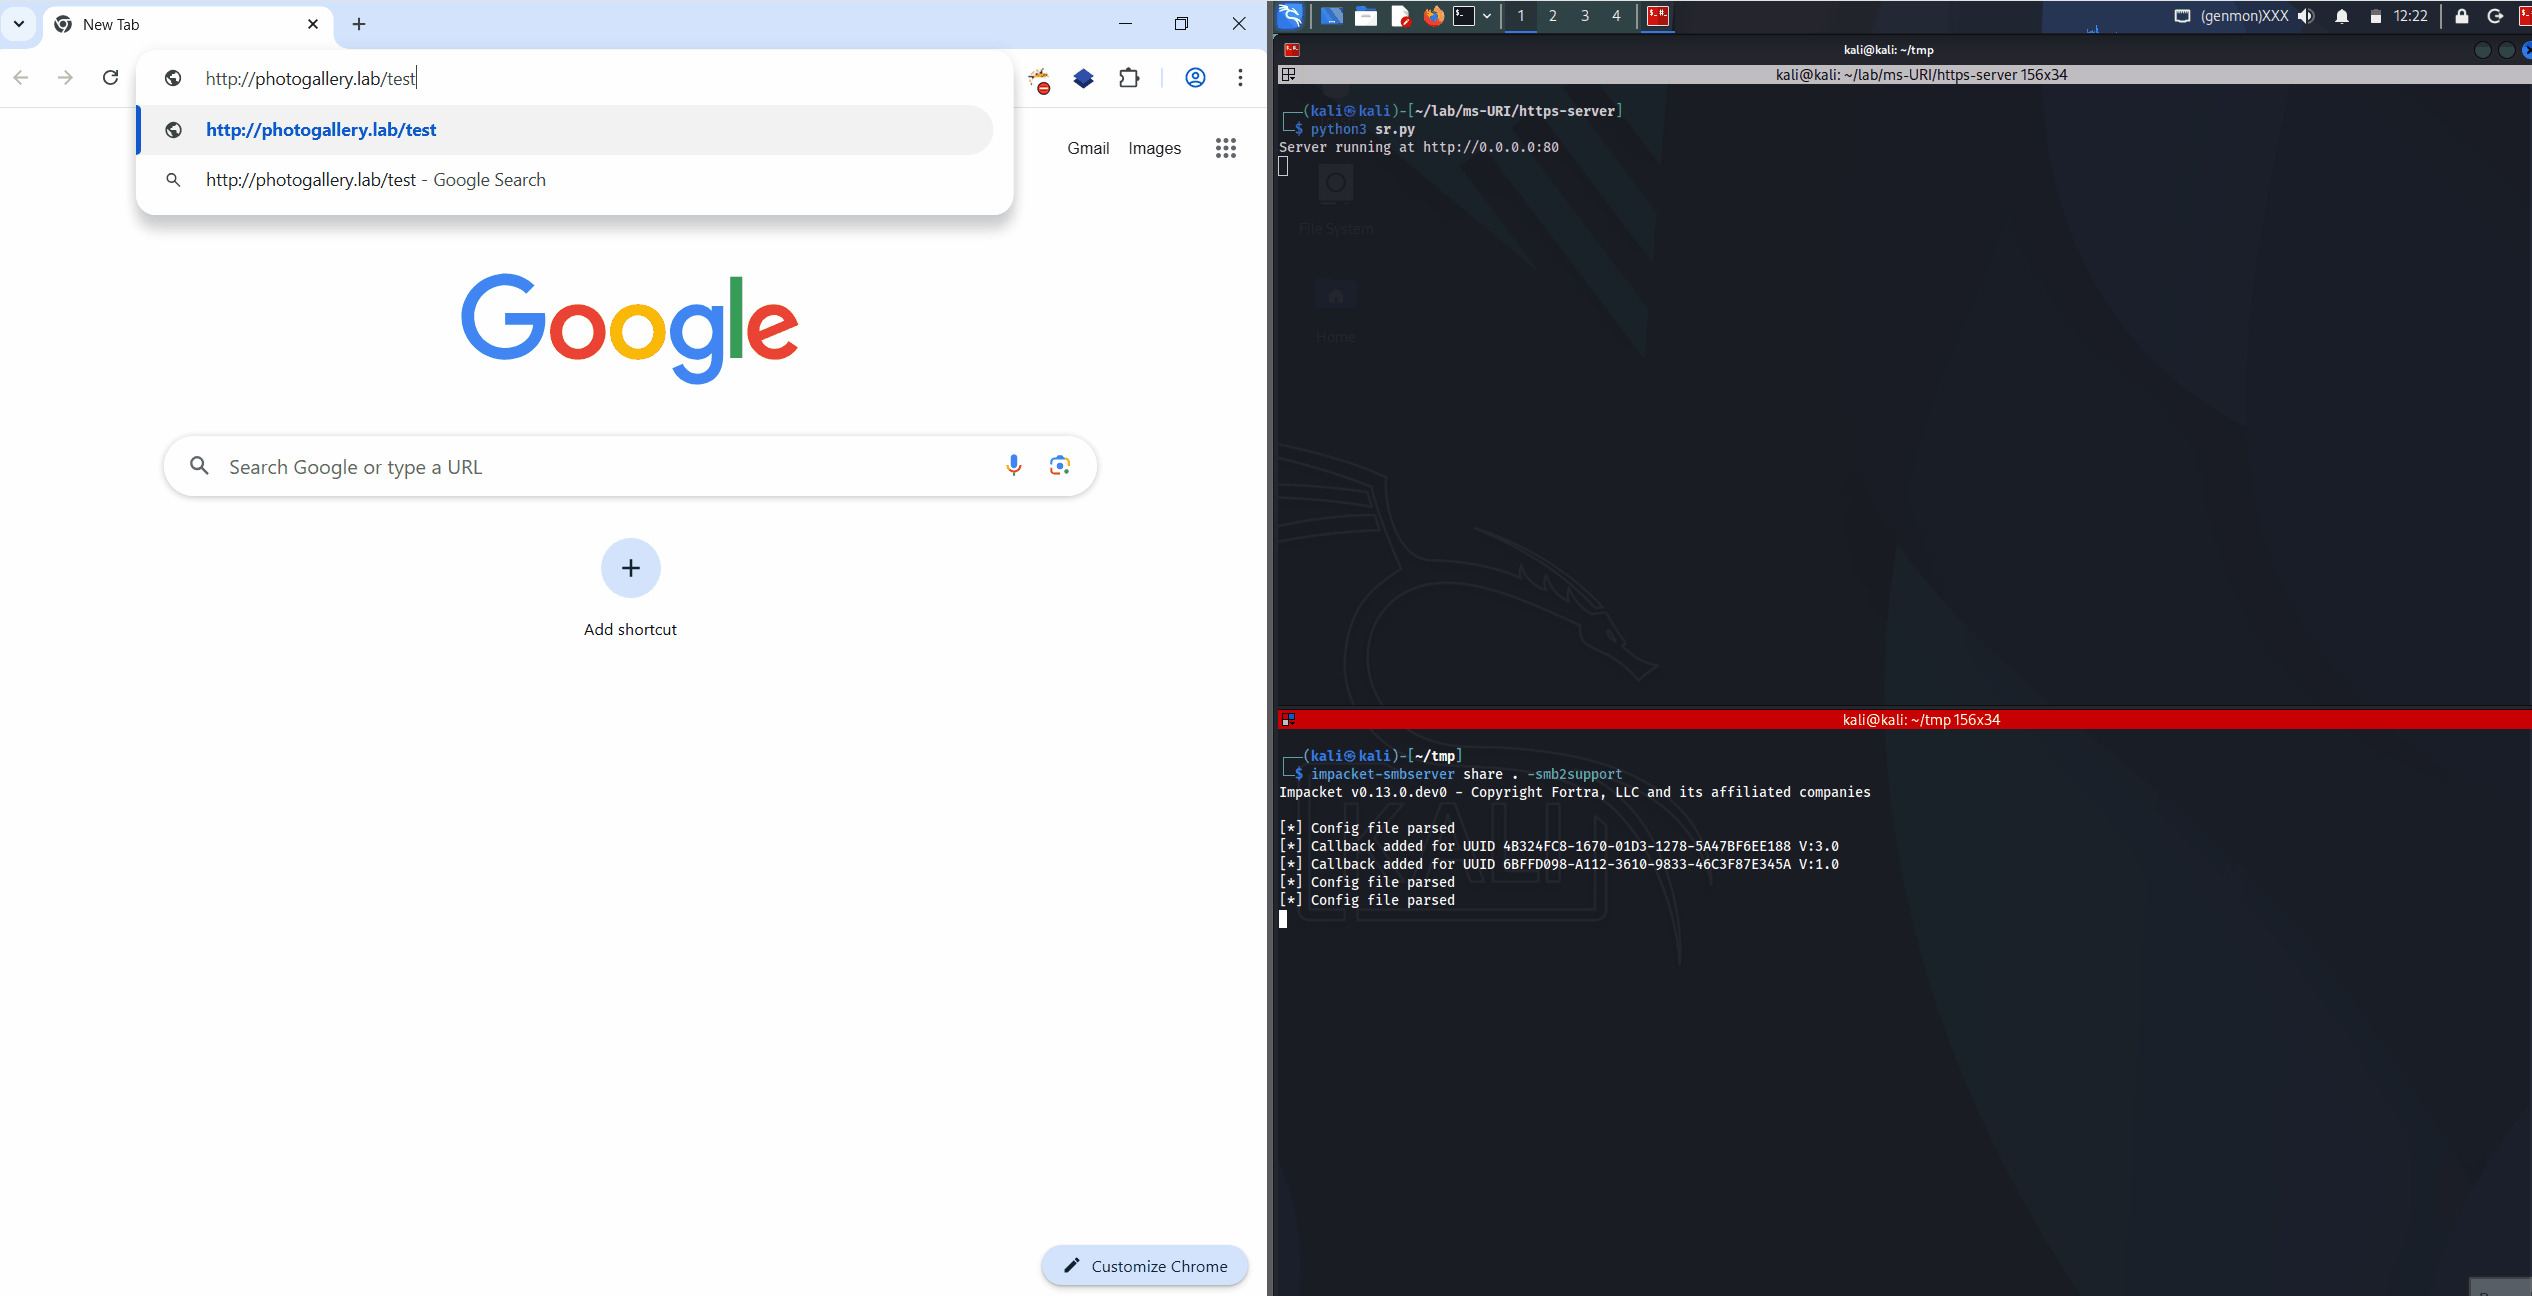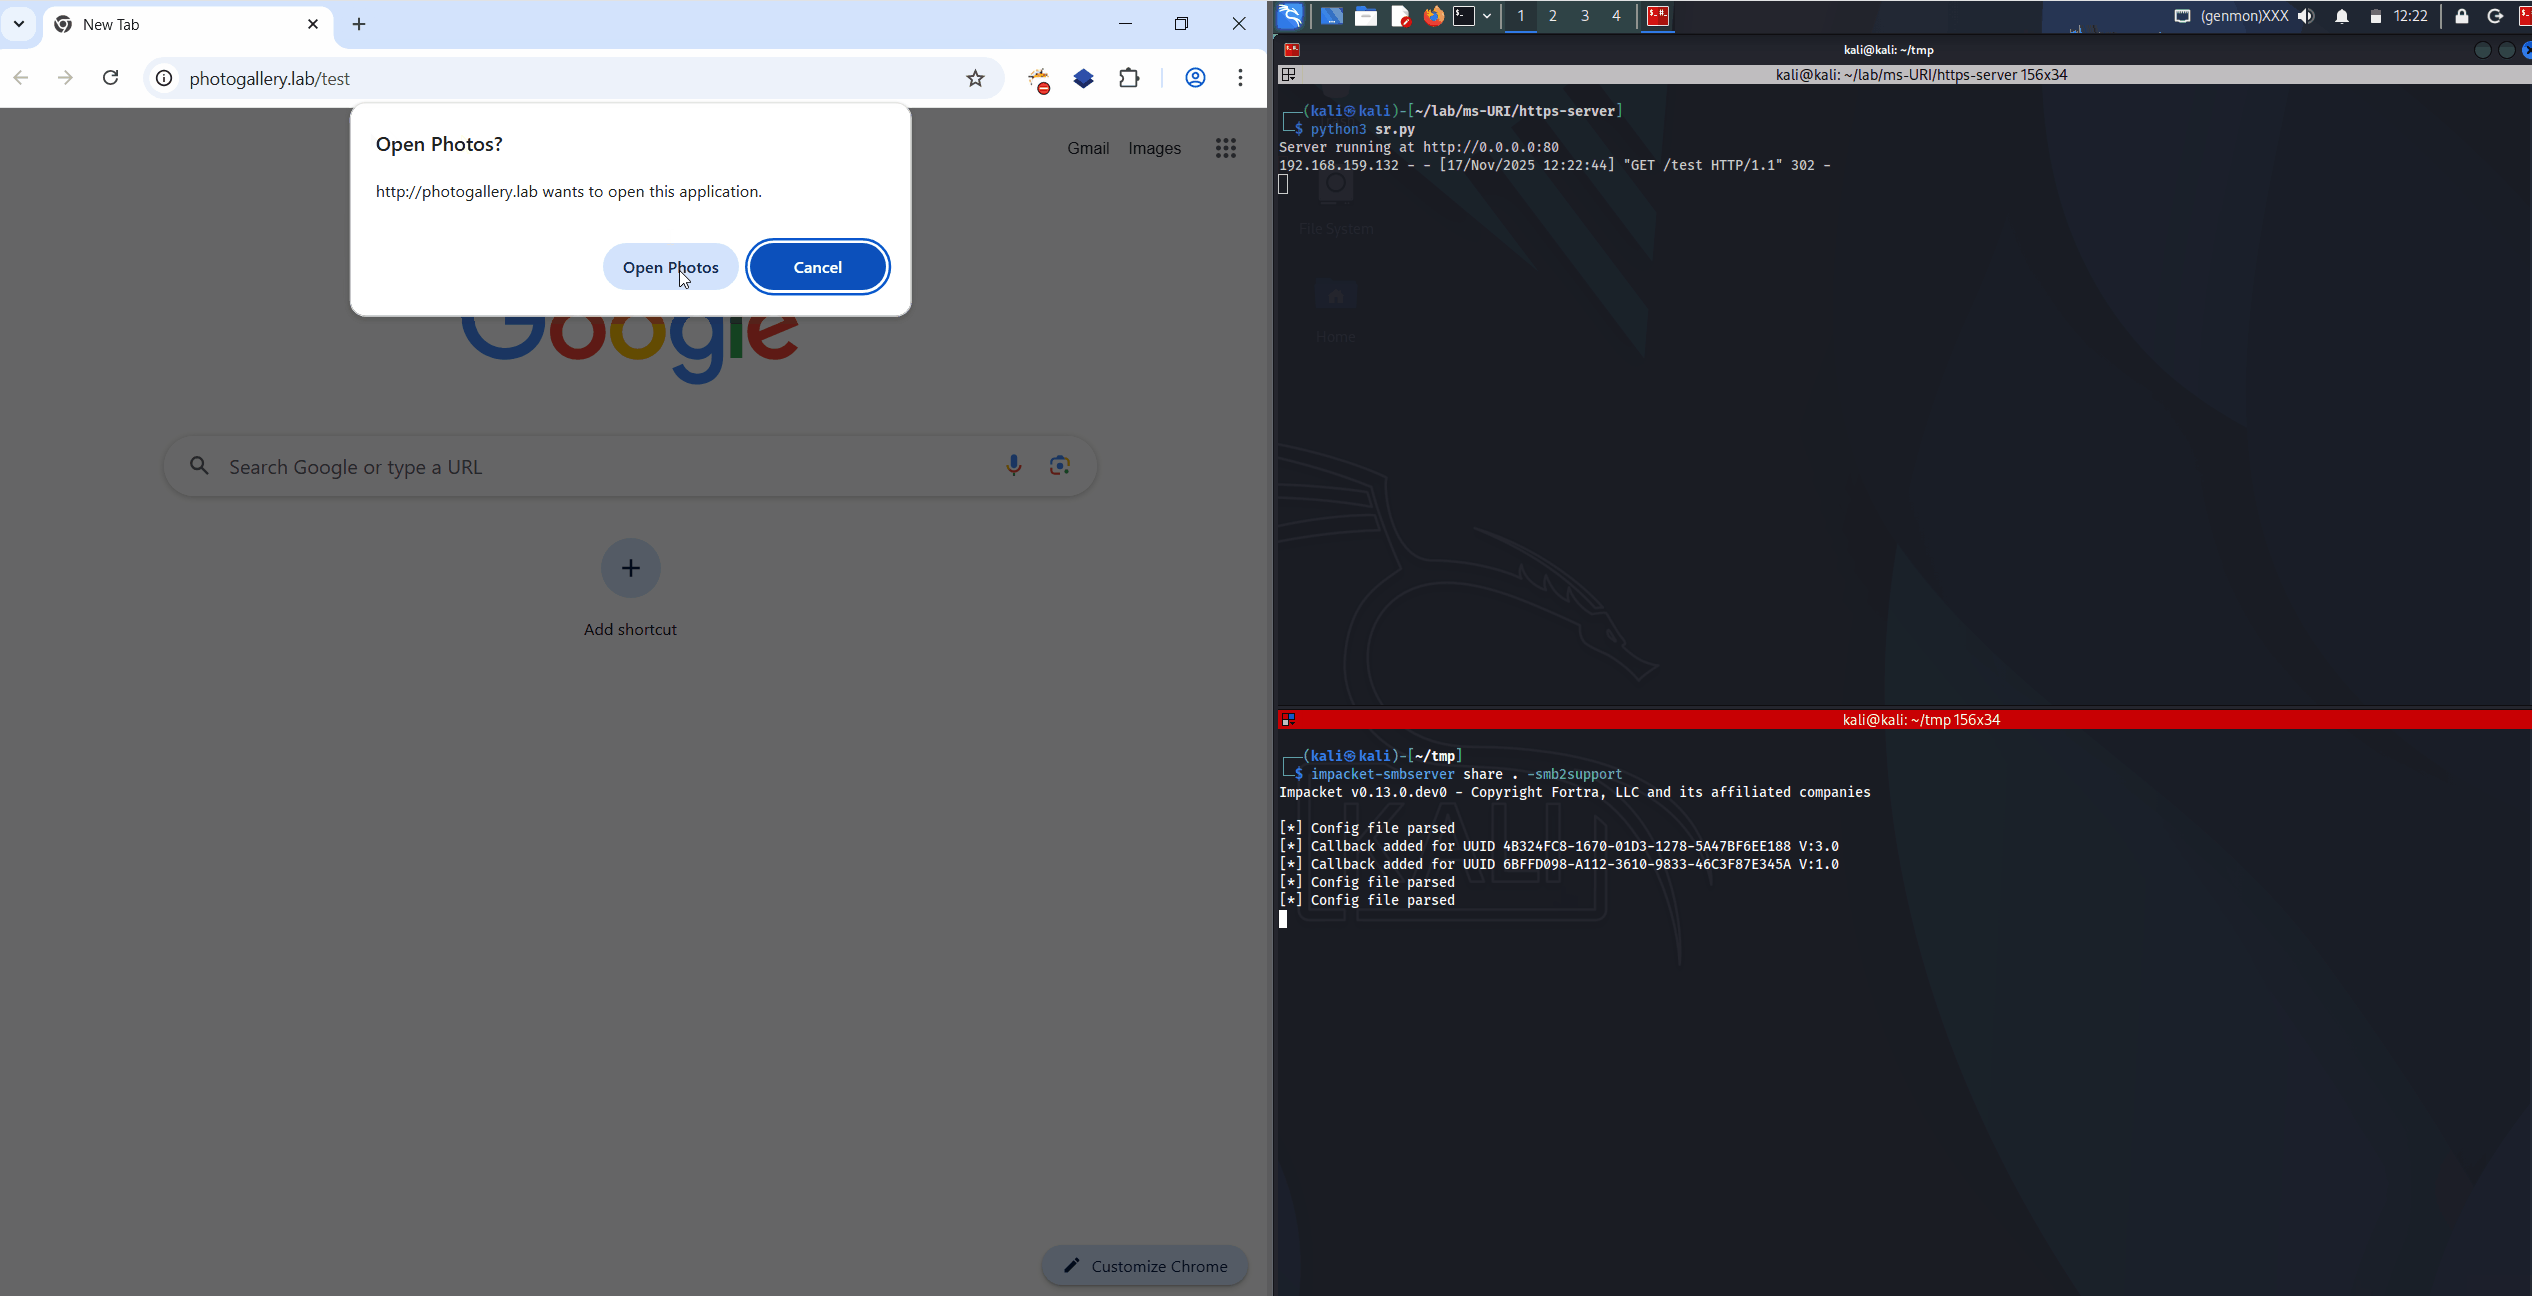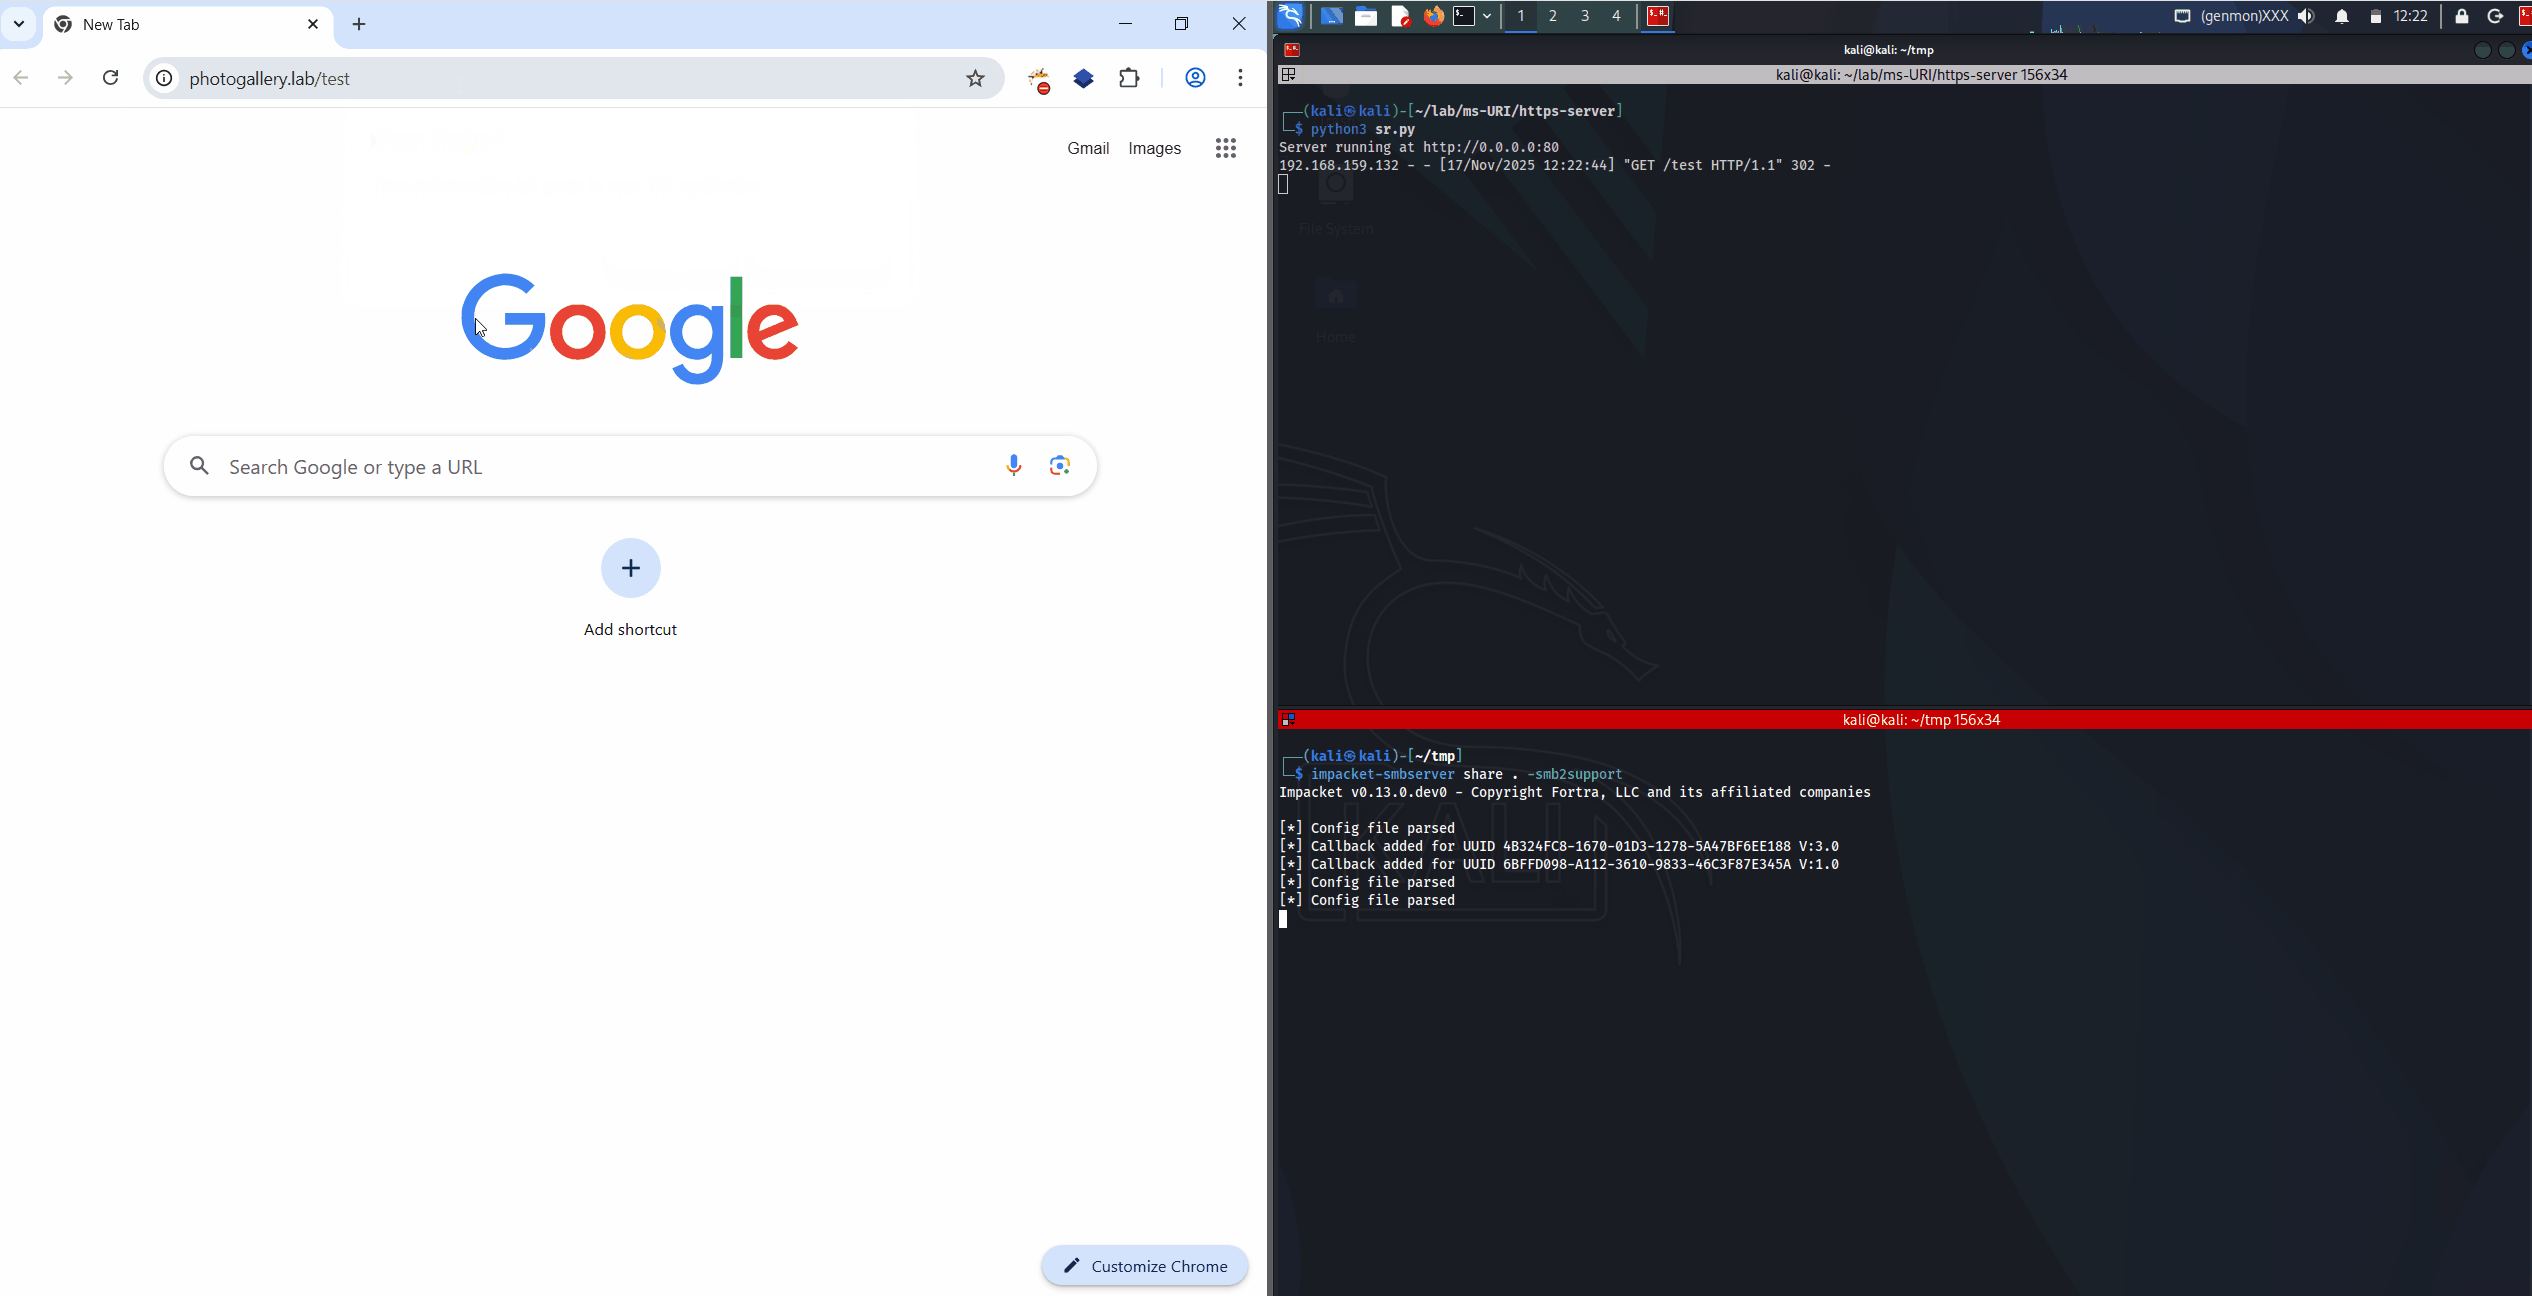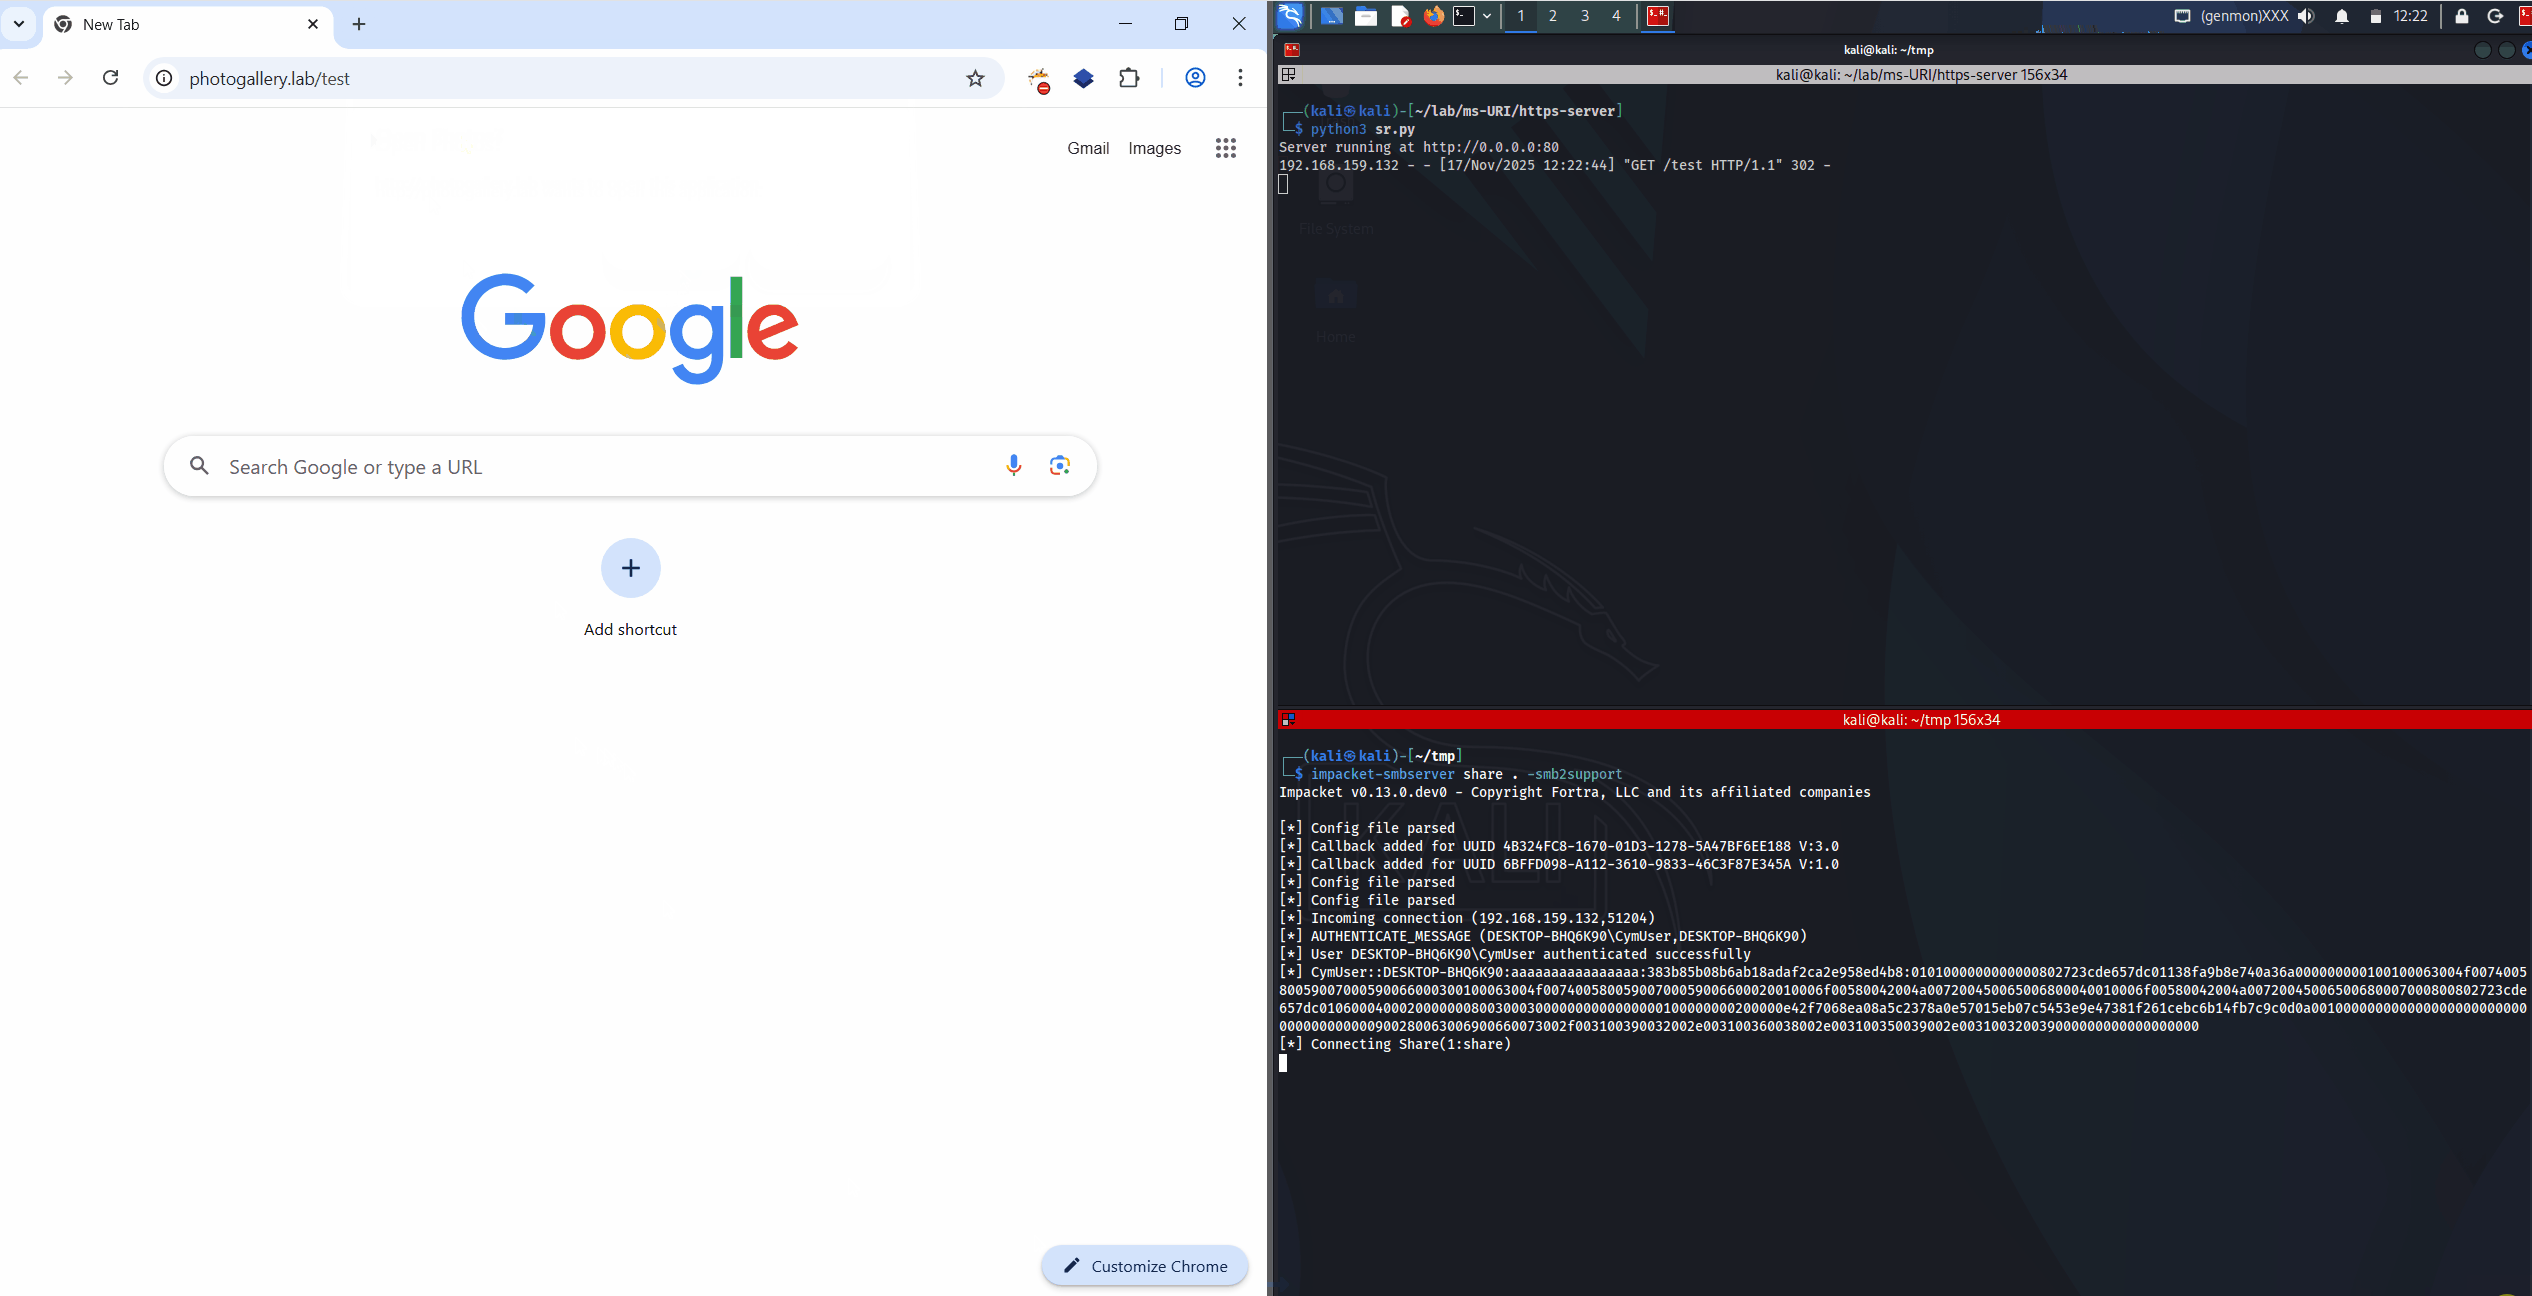 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
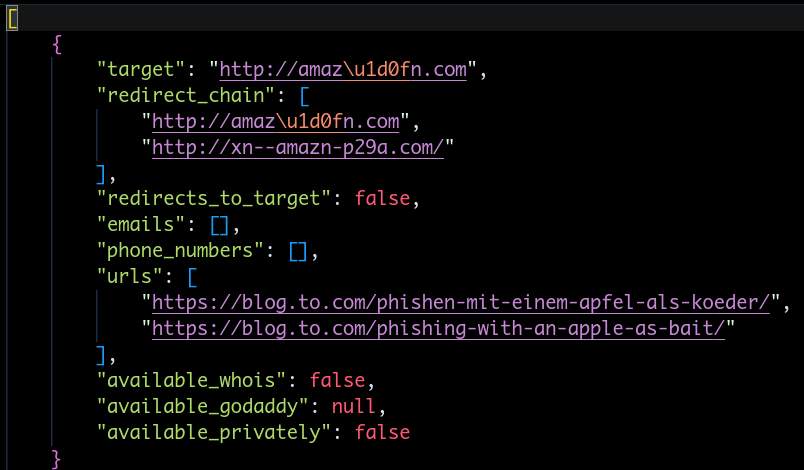 redhuntlabs/antisquat
AI-powered typosquatting and phishing domain detector using NLP and ChatGPT to generate domain permutations and extract contact information from…
 mthbernardes/houseproxy
Protect your parents from phishing
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 ahrixia/cve-2024-57428
CVE-2024-57428: PHPJabbers Cinema Booking System v2.0 suffers from stored XSS, enabling persistent JavaScript injection for phishing and malware…
 mandiant/reelphish
Real-time two-factor phishing tool that automates credential harvesting by intercepting credentials from a phishing site and submitting them to the…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…