
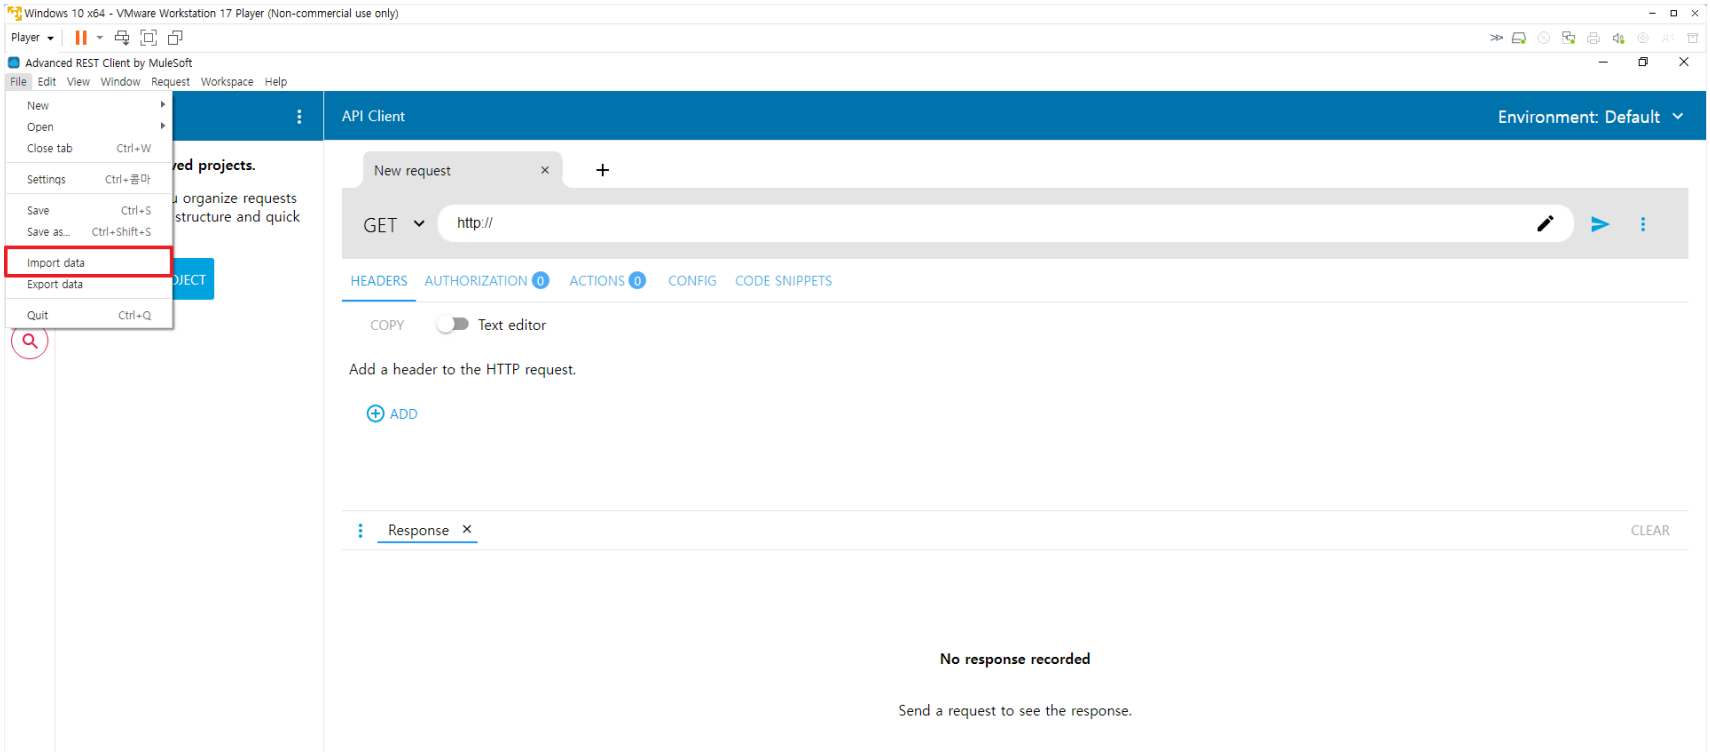
CVE-2024-25503
 eqstlab/cve-2024-25503
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
exploitationinformation-gatheringpenetration-testing+3
eqstlab/cve-2024-25503Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
 muhammad-ali007/outlookntlm_cve-2023-23397
Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 0xsu3ks/cve-2024-34328
Proof-of-concept for open redirection via Host header manipulation in Sielox AnyWare 2.1.2 (CVE-2024-34328), with exploit steps, impact, and…
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 echo-devim/cve-2022-48429_poc
Proof-of-concept exploit for CVE-2022-48429, a stored cross-site scripting vulnerability in JetBrains YouTrack dashboards enabling low-privileged…
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 hau2212/moniker-link-cve-2024-21413-
Educational exploit for CVE-2024-21413 (Moniker Link) demonstrating Outlook RCE and NTLM credential leak via crafted hyperlinks, with detection and…
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
 sybelle03/cve-2021-43617
This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
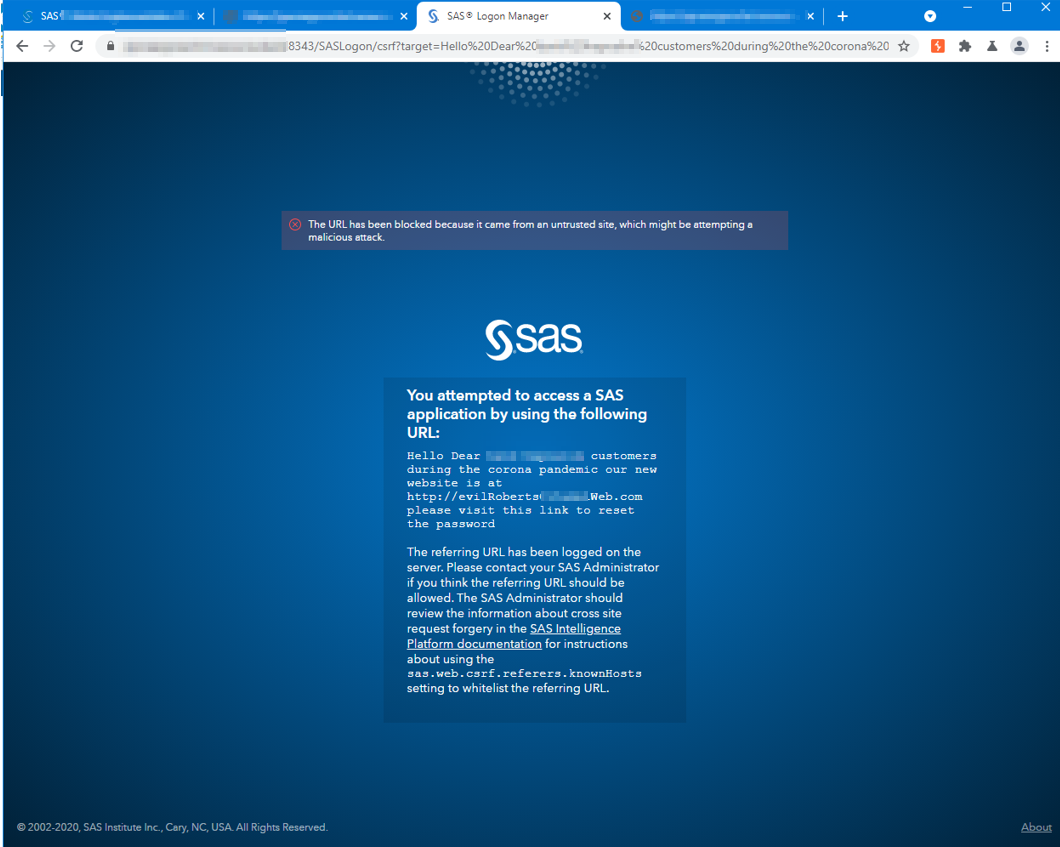 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
 mlniumm/cve-2025-28073
Proof-of-concept for a reflected XSS vulnerability in phpList 3.6.15 via the /lists/dl.php endpoint, enabling session hijacking and arbitrary…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 dhmosfunk/7-zip-cve-2025-0411-poc
This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.