Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413

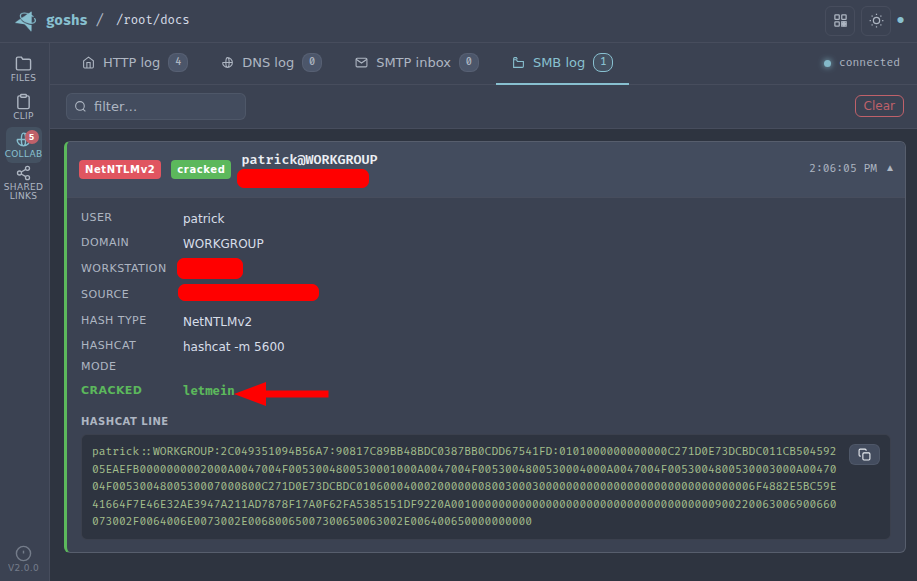
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Tools and Techniques for Red Team / Penetration Testing

Checks expired domains for categorization/reputation and Archive.org history to determine good candidates for phishing and C2 domain names

Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.

CATPHISH project - For phishing and corporate espionage. Perfect for RED TEAM.

Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.

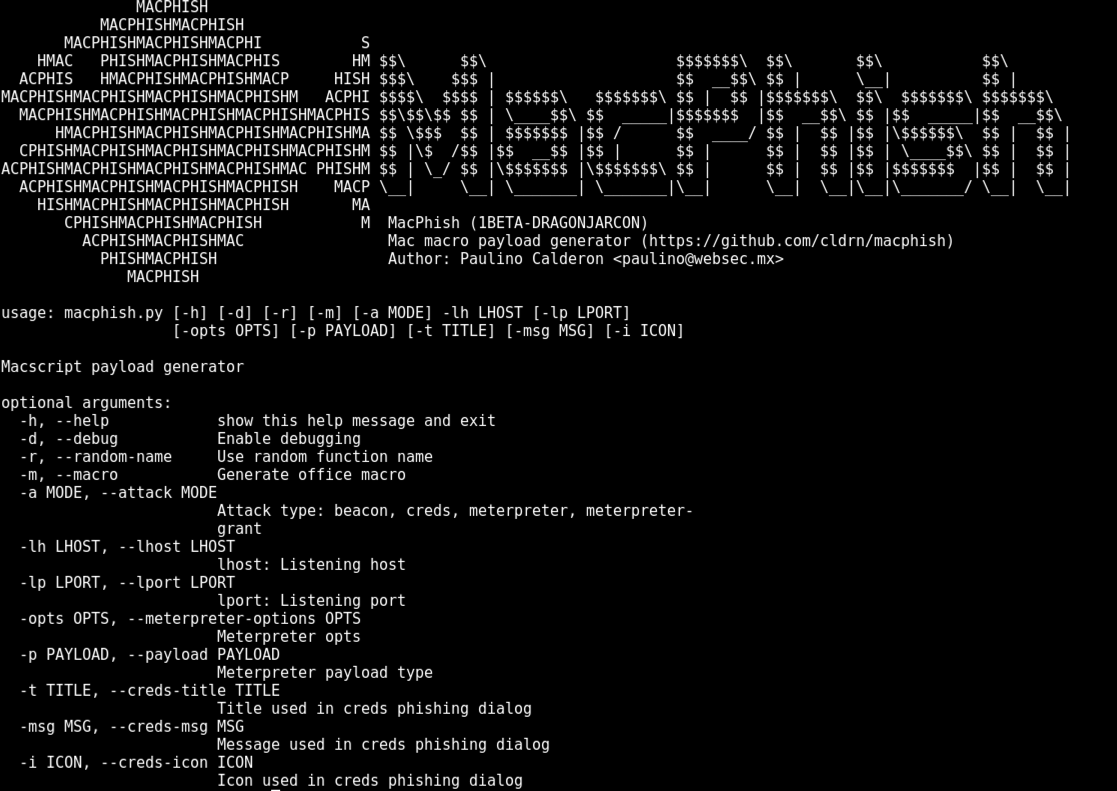
Generates malicious Office for Mac macros with beacon, credential harvesting, and meterpreter payloads for phishing and exploitation testing on macOS.

abusing windows toast notifications for fun and user manipulation

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…

Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…

Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…

CVE-2024-57428: PHPJabbers Cinema Booking System v2.0 suffers from stored XSS, enabling persistent JavaScript injection for phishing and malware…

Sublime rules for email attack detection, prevention, and threat hunting.

FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…

Automated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…


Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups