
Evilginx3-Phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…

Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…

Proof of concept for a blind/persistent XSS vulnerability in Blinger.io helpdesk, demonstrating remote code execution in admin panels via crafted…

A Proof of Concept for the CVE-2021-46398 flaw exploitation

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…

POC exploit for CVE-2025-33053 (external control of file execution path in URL file)

Proof-of-concept scripts demonstrating reflected XSS in the Ultimate Classified Listings WordPress plugin and admin cookie theft via crafted payloads…

PhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test

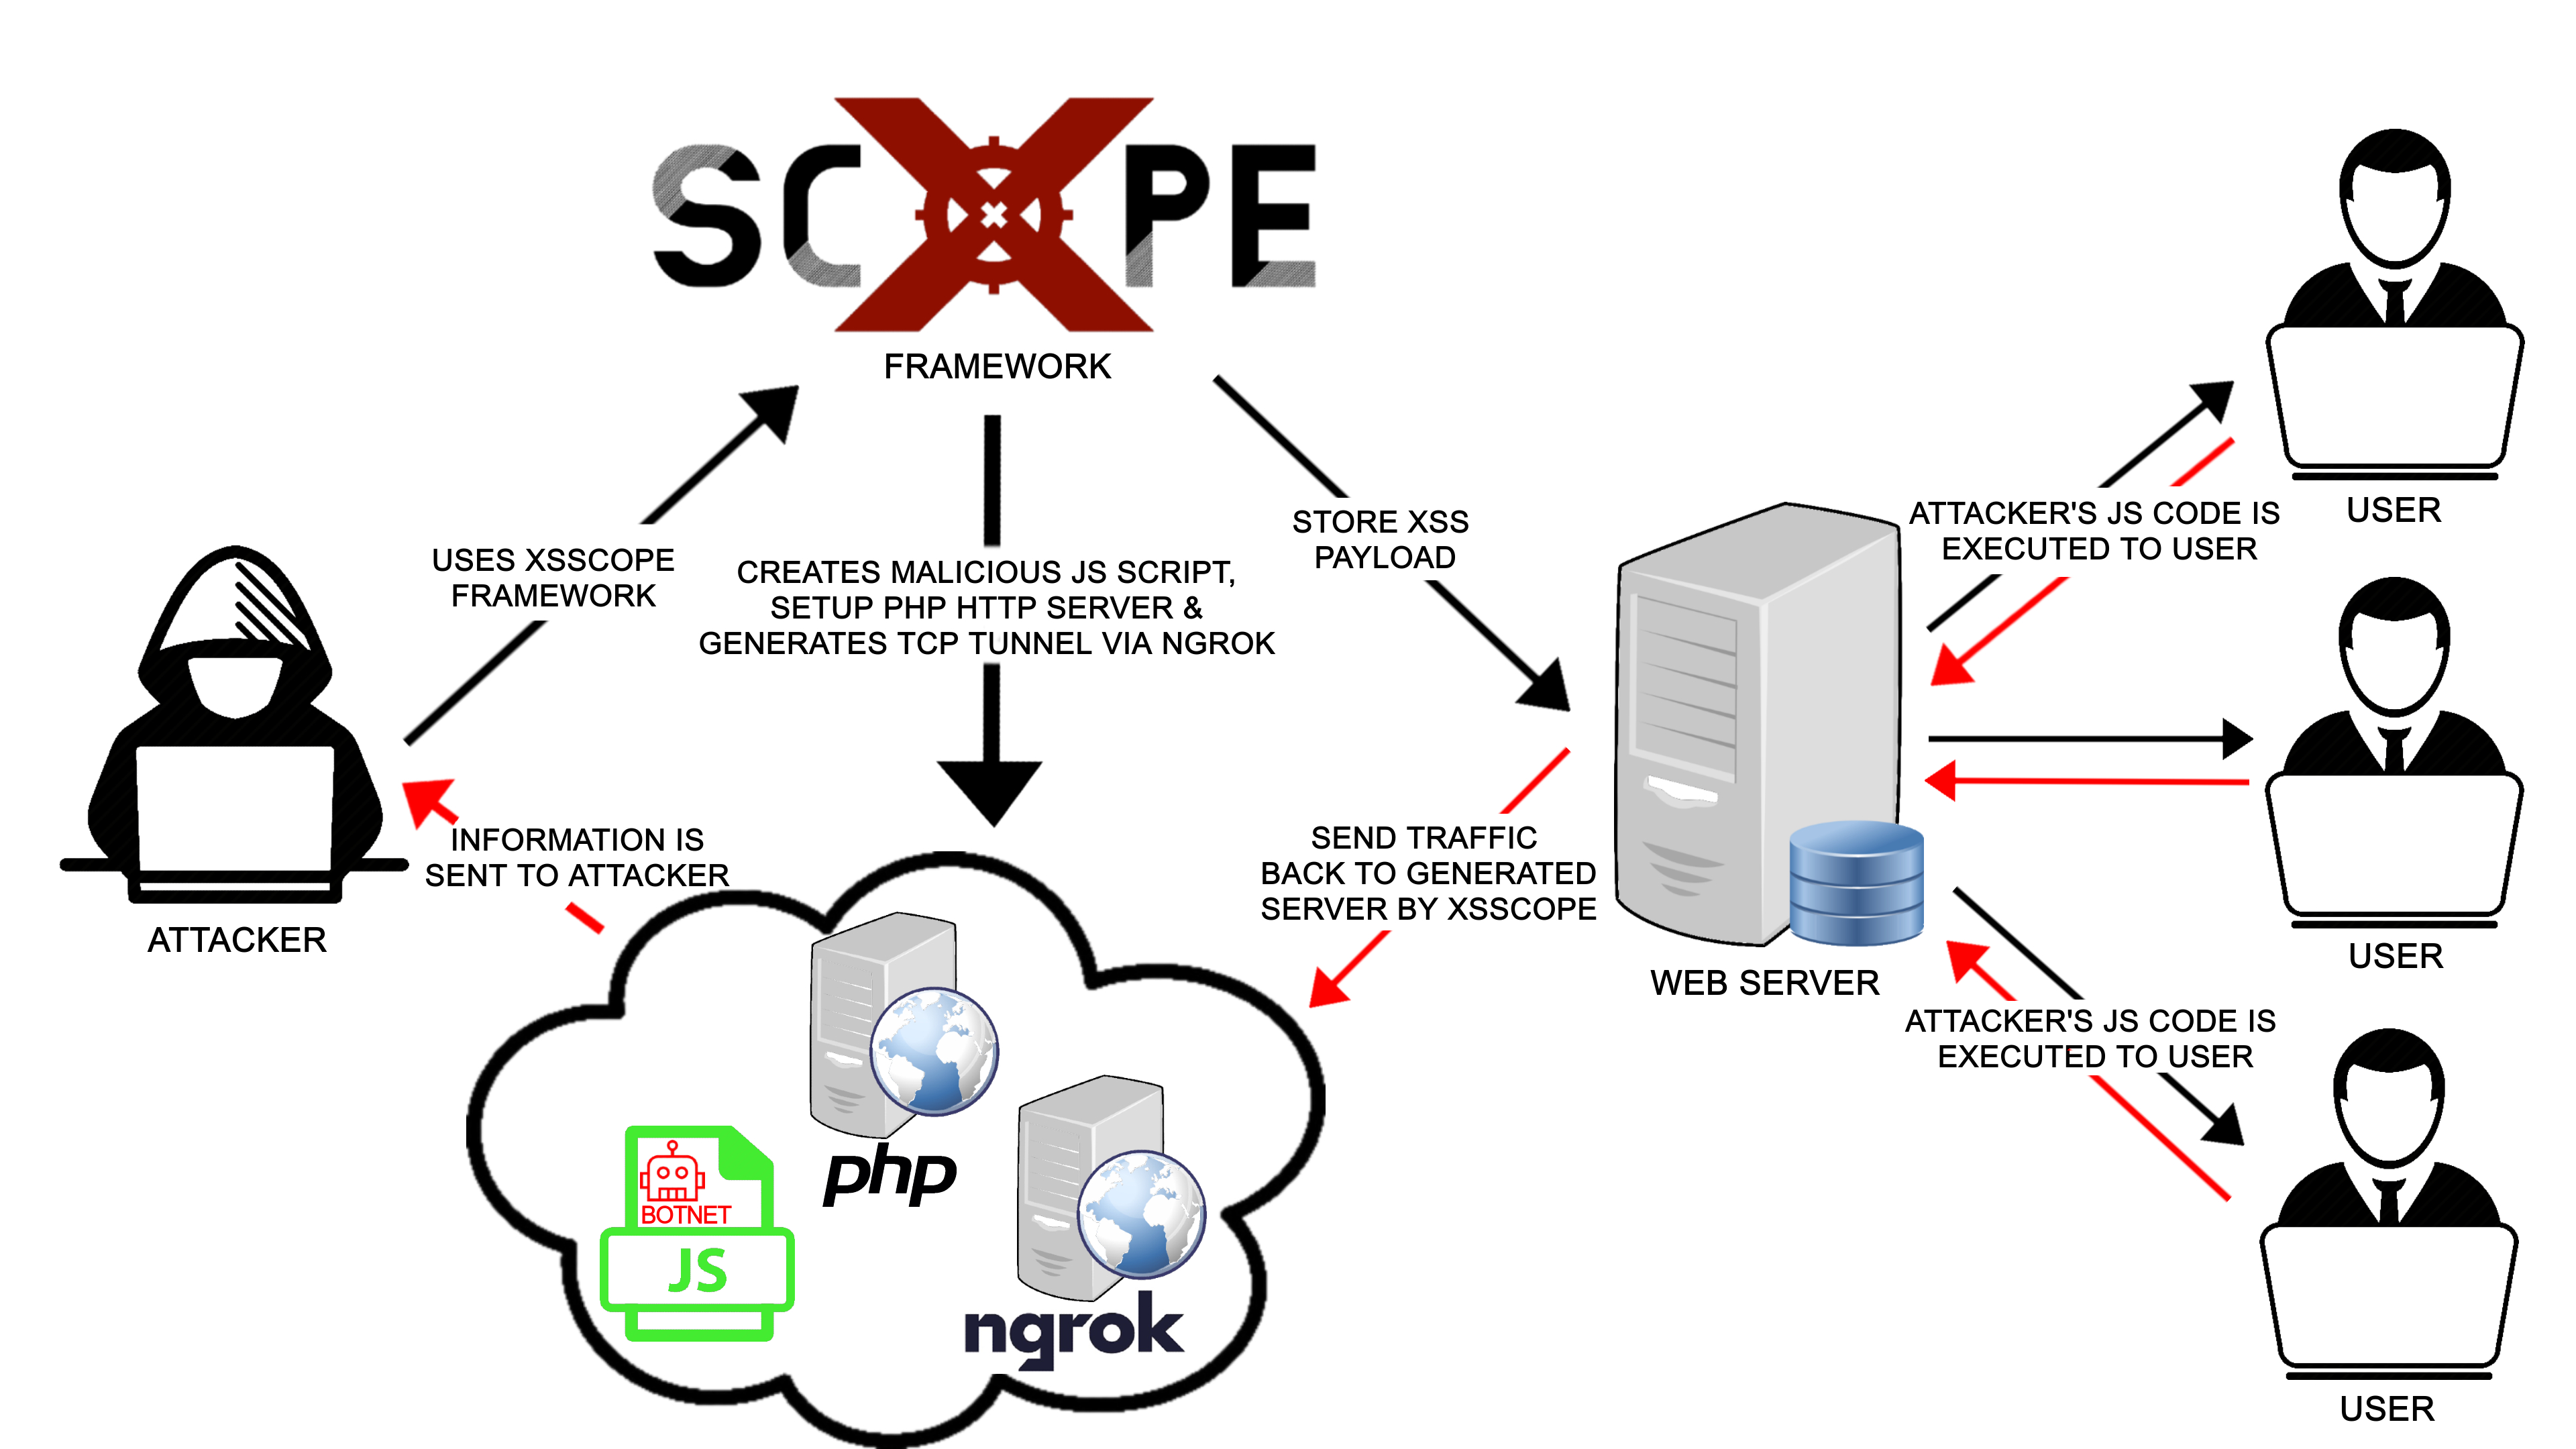
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.

XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.

Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…

Proof-of-concept exploit for stored XSS and insecure permissions in Collabora CODE <= 4.2.2 via the Vereign WOPI API, enabling account hijacking and…

Proof-of-concept for CVE-2020-16270, an XSS vulnerability in OLIMPOKS under 3.3.39, demonstrating remote injection of malicious JavaScript to steal…

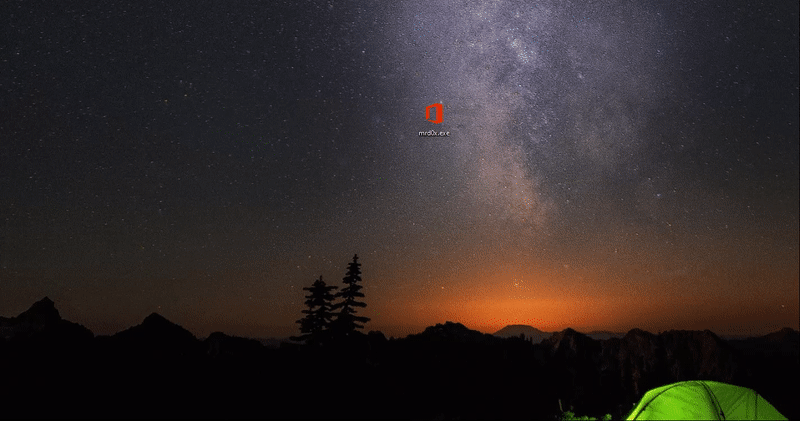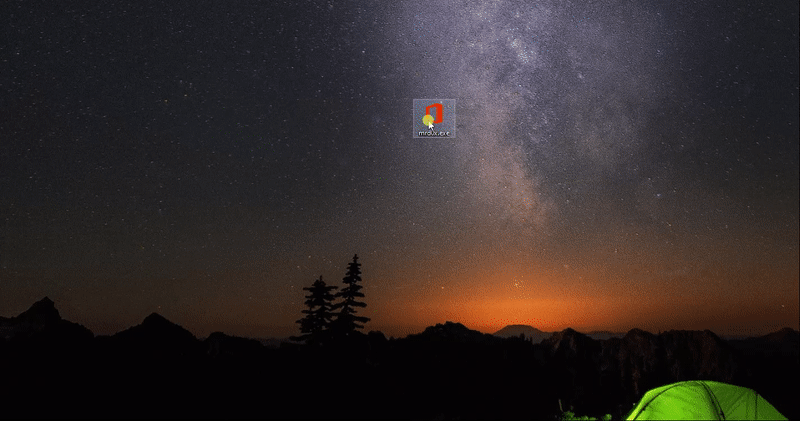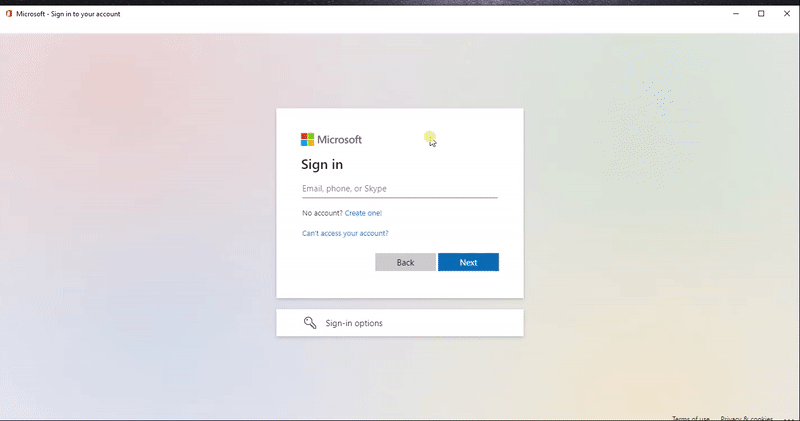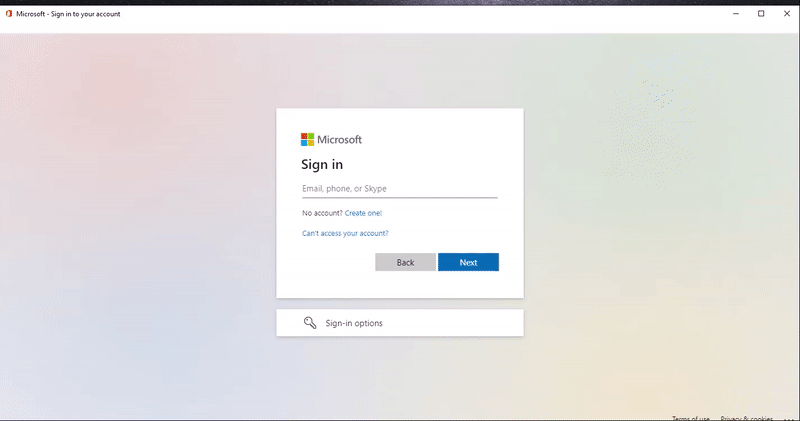
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…

Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit

CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS