SOGo_web_mail-vulnerability-CVE-2025-50340

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Windows active user credential phishing tool

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

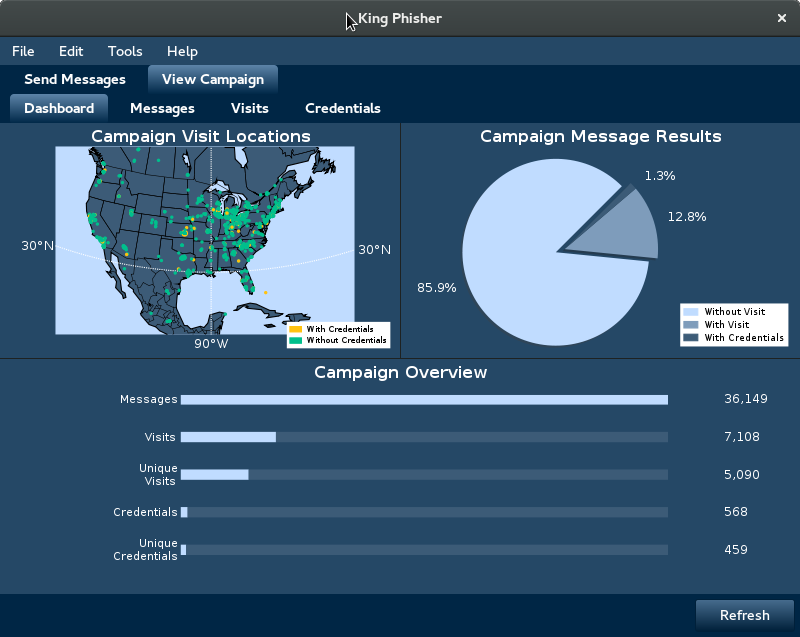
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…

Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…

Tools and Techniques for Red Team / Penetration Testing

Modular phishing framework with CLI for cloning sites, sending templated emails, and launching phishing campaigns via email, SMS, iMessage, and…

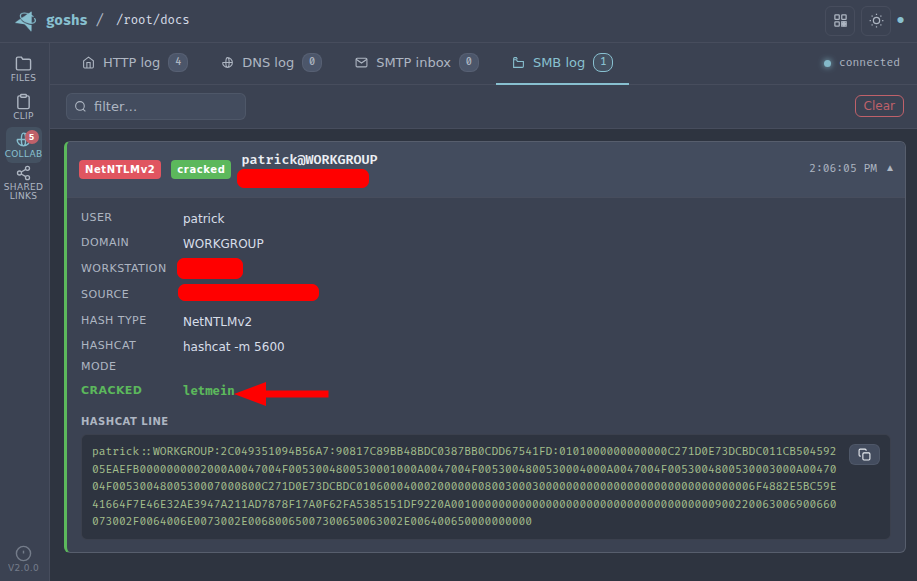
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…