

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
39 results
zaproxy preview

zaproxy

GitHubzaproxy/zaproxy

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…


android-securityapi-securityapi-security-testing+15
16.1k
16h 5m ago
threatripper preview

threatripper

GitLabmevislobo2006/threatripper

Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
api-securitydefensive-toolseducation+4
126 days ago
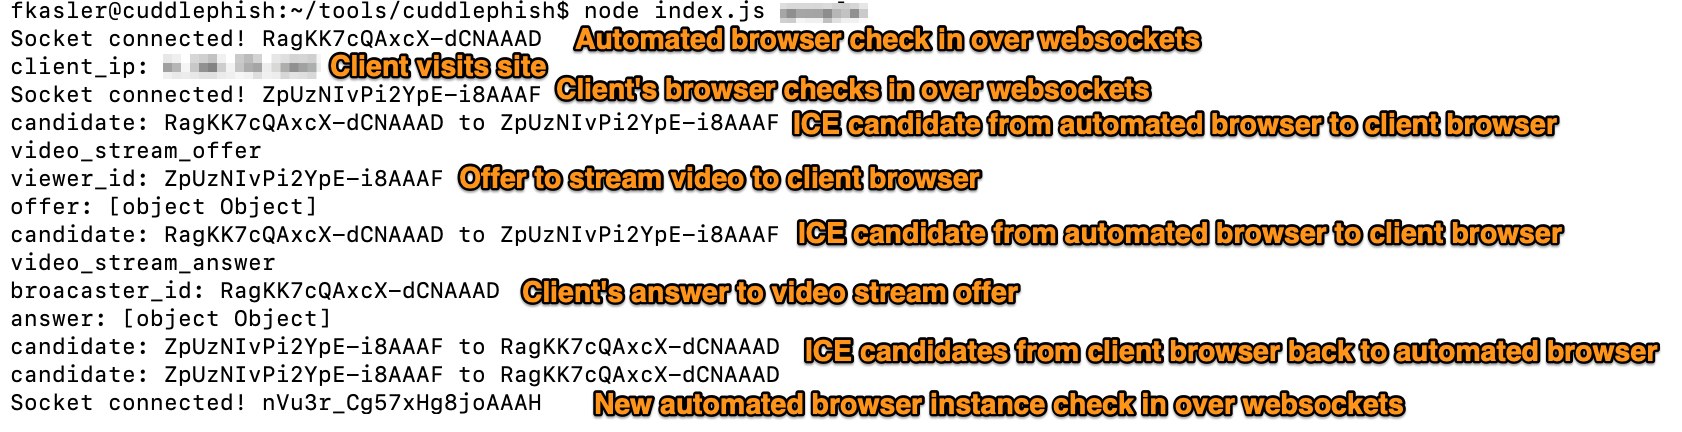
cuddlephish preview

cuddlephish

GitHubfkasler/cuddlephish

Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
penetration-testingphishingphishing-tools+3
6901 month ago
Yordam-Kutuphane-Otomasyonunda-Coklu-HTML-Enjeksiyonu preview

Yordam-Kutuphane-Otomasyonunda-Coklu-HTML-Enjeksiyonu

GitHubalkimcoskun/yordam-kutuphane-otomasyonunda-coklu-html-enjeksiyonu

CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…
exploitationphishingvulnerability-analysis+2
1 month ago
CVE-2026-26897-EcoOnline-DeepLink preview

CVE-2026-26897-EcoOnline-DeepLink

GitHubiwallplace/cve-2026-26897-ecoonline-deeplink

Public advisory & PoC for CVE-2026-26897 — Deep Link Bypass in EcoOnline EHS Android (com.airsweb.v10), fixed in 0.2.500

android-securityeducationexploitation+5
4 months ago
wifiphisher preview

wifiphisher

GitHubwifiphisher/wifiphisher

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
impersonation-toolsmalware-analysisphishing+6
14.9k5 months ago
CVE-2024-34568 preview

CVE-2024-34568

GitHubsanupl/cve-2024-34568

In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
exploitationphishingvulnerability-analysis+2
15 months ago
CVE-2026-33149-PoC preview

CVE-2026-33149-PoC

GitHubfilipegaudard/cve-2026-33149-poc

Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
exploitationpenetration-testingphishing+3
6 months ago
URL_CHECKER preview

URL_CHECKER

GitHubmannansainicyber/url_checker

Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
api-security-testingeducationmachine-learning+3
17 months ago
pegasus-neo preview

pegasus-neo

GitHubsobri3195/pegasus-neo

PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
exploitationforensicsosint+9
1307 months ago
phishcollector preview

phishcollector

GitHubolizimmermann/phishcollector

PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.

crawlereducationinformation-gathering+8
238 months ago
PoC-CVE-2026-20841 preview

PoC-CVE-2026-20841

GitHubelenichristopoulou/poc-cve-2026-20841

Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
exploitationphishingsocial-engineering+1
8 months ago
TokenFlare preview

TokenFlare

GitHubjumpseclabs/tokenflare

Serverless AITM Simulation Framework for Entra ID and M365
authenticationcloud-securitycommand-and-control+6
24310 months ago
CVE-2025-55903 preview

CVE-2025-55903

GitHubajansha/cve-2025-55903

Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…
exploitationphishingvulnerability-analysis+2
1 year ago
Leantime-POC preview

Leantime-POC

GitHubdead1nfluence/leantime-poc

CVE-2024-27474, CVE-2024-27476, CVE-2024-27477
exploitationphishingvulnerability-analysis+2
1 year ago
Roundcube-CVE-2024-42008-POC preview

Roundcube-CVE-2024-42008-POC

GitHubrpgsec/roundcube-cve-2024-42008-poc

Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
ctfeducationexploitation+3
1 year ago
CVE-2025-28073 preview

CVE-2025-28073

GitHubmlniumm/cve-2025-28073

Proof-of-concept for a reflected XSS vulnerability in phpList 3.6.15 via the /lists/dl.php endpoint, enabling session hijacking and arbitrary…
exploitationphishingvulnerability-analysis+2
1 year ago
CVE-2025-50363_BXSS_CVE preview

CVE-2025-50363_BXSS_CVE

GitHub1h3ll/cve-2025-50363_bxss_cve

Proof-of-concept for a blind XSS vulnerability in Maid Hiring Management System v1.0, capturing admin session cookies via a crafted application form…

exploitationpenetration-testingphishing+3
1 year ago
Previous123Next