
beef
 beefproject/beef
The Browser Exploitation Framework Project
command-and-controlexploitationexploit-frameworks+8
beefproject/beefThe Browser Exploitation Framework Project
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
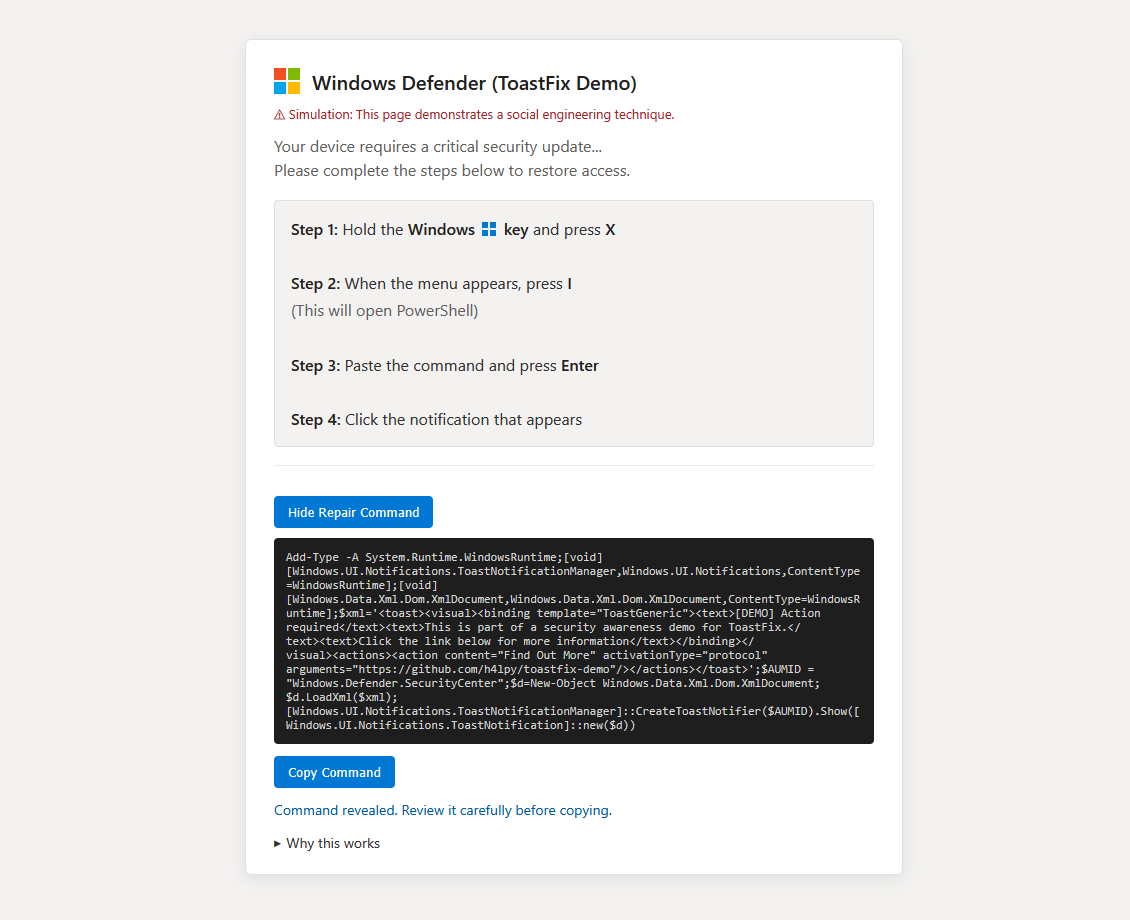 h4lpy/toastfix-demo
Proof-of-concept security demo illustrating how PowerShell can create trusted-looking Windows toast notifications chained together with…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 pescada-dev/cve-2025-22381
Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project
 ignitetch/advphishing
This is Advance Phishing Tool ! OTP PHISHING
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 dead1nfluence/leantime-poc
CVE-2024-27474, CVE-2024-27476, CVE-2024-27477
 1h3ll/cve-2025-50363_bxss_cve
Proof-of-concept for a blind XSS vulnerability in Maid Hiring Management System v1.0, capturing admin session cookies via a crafted application form…
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
 d4rks3c-group/hiddeneyereborn
HiddenEye Reborn in better shape than ever, rewritten from scratch and adapted to modern world
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 t4d/stalkphish
StalkPhish - The Phishing kits stalker, harvesting phishing kits for investigations.
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 undeadsec/socialfishmobile
📱 🐟 An app to remote control SocialFish.
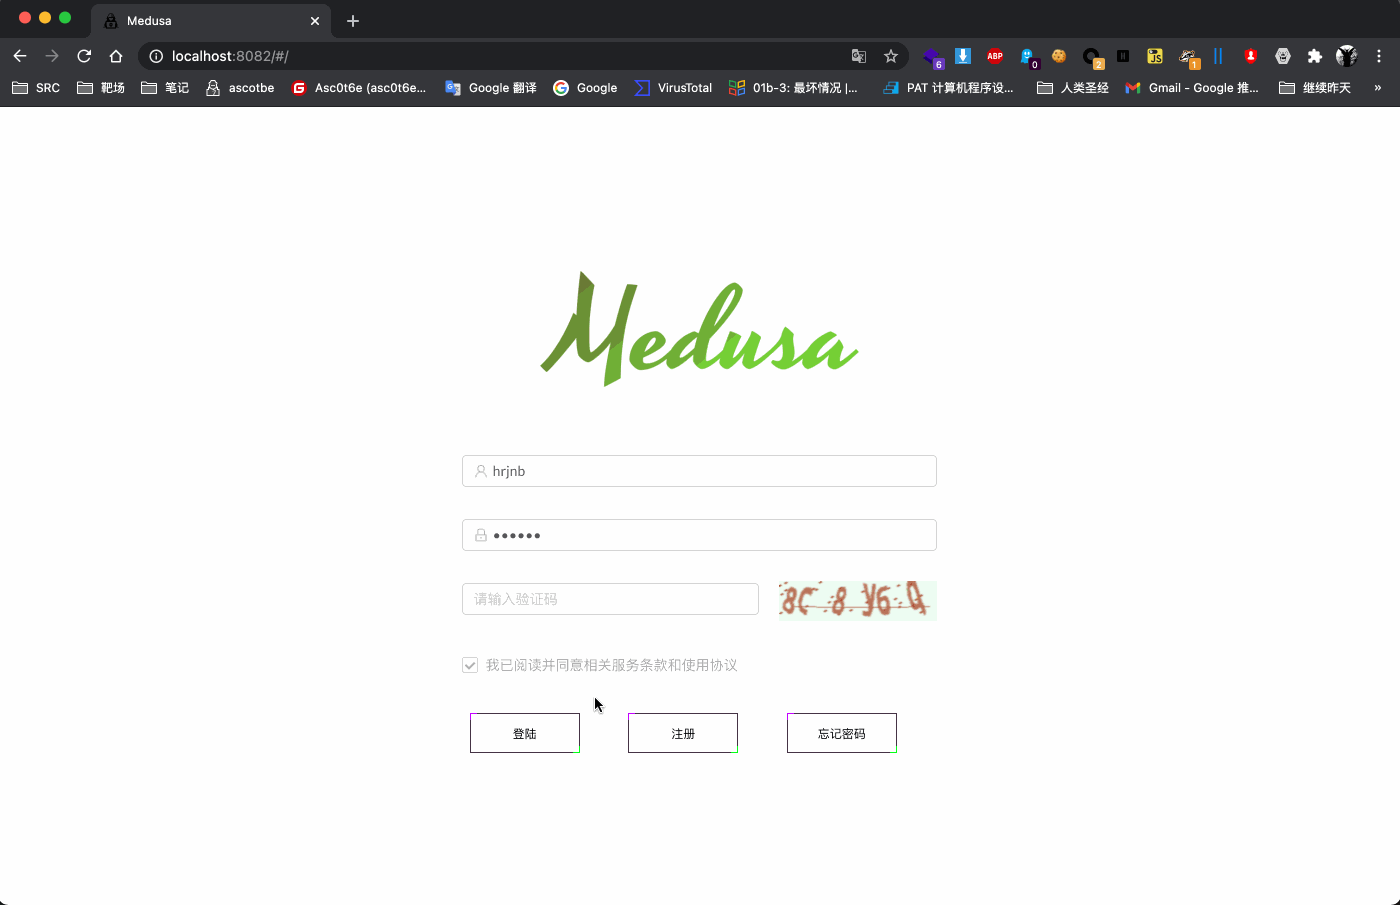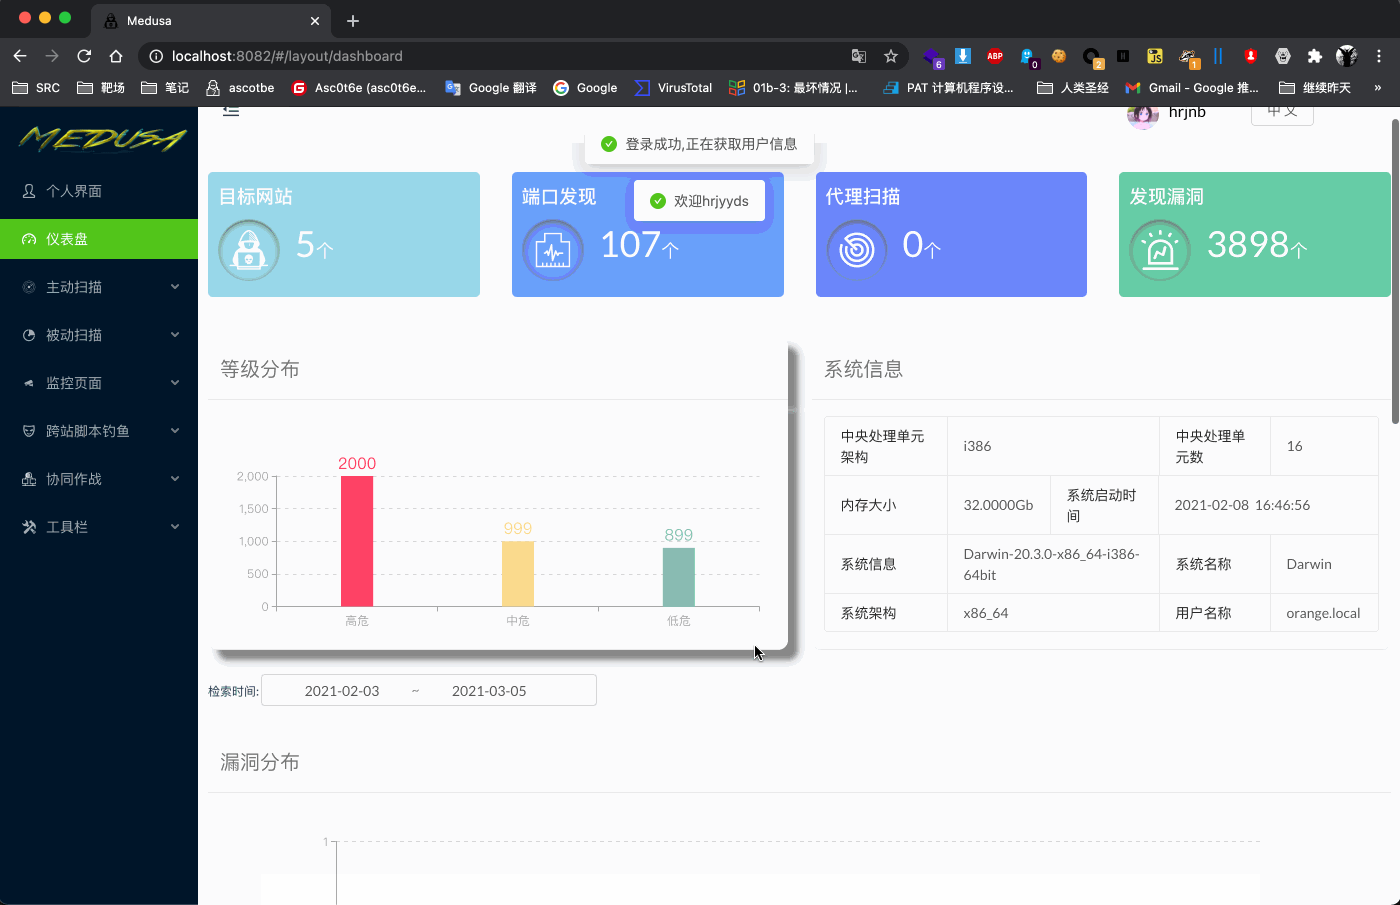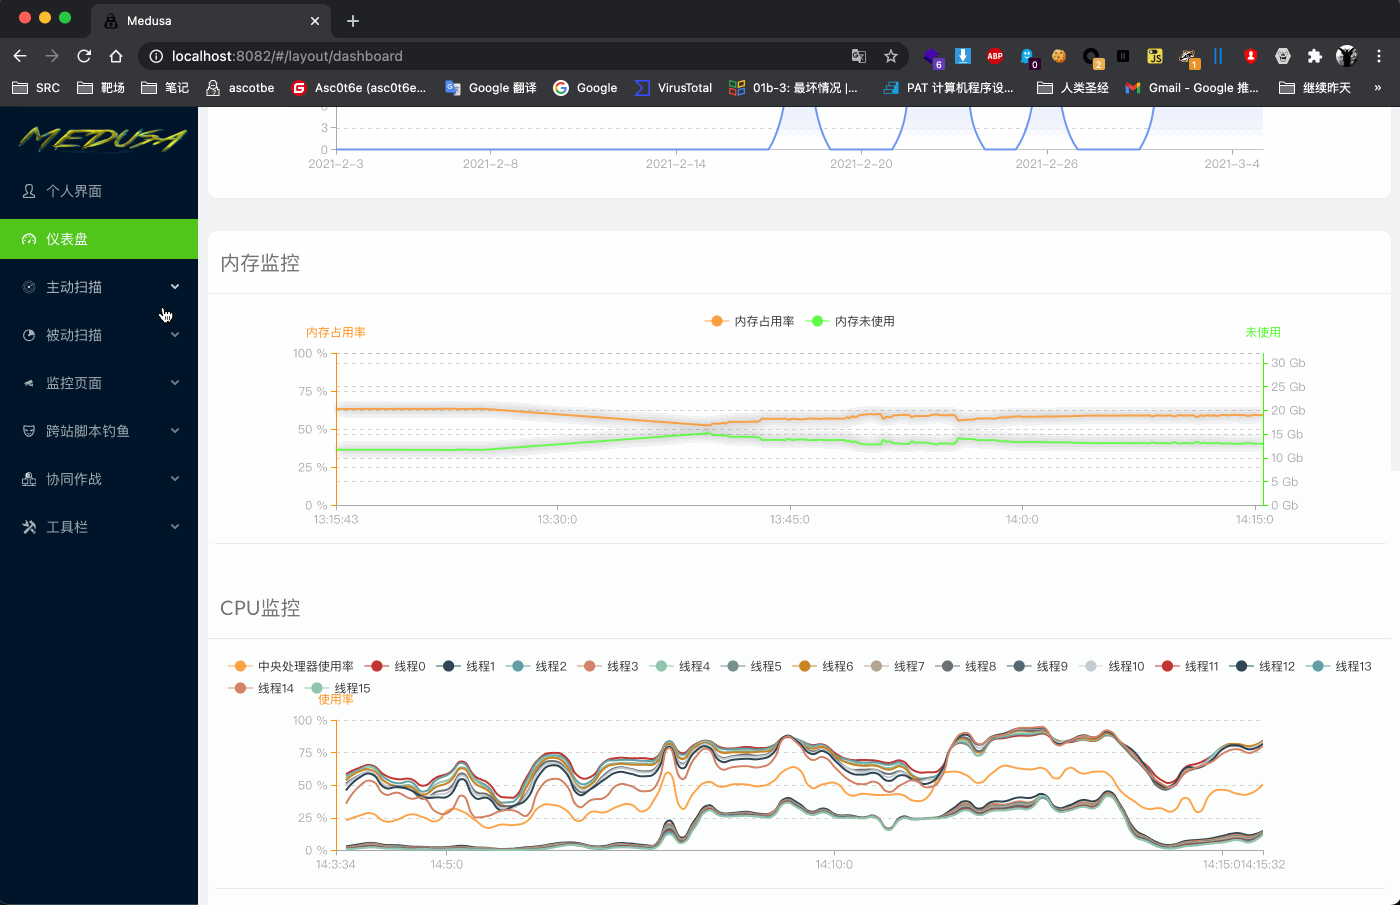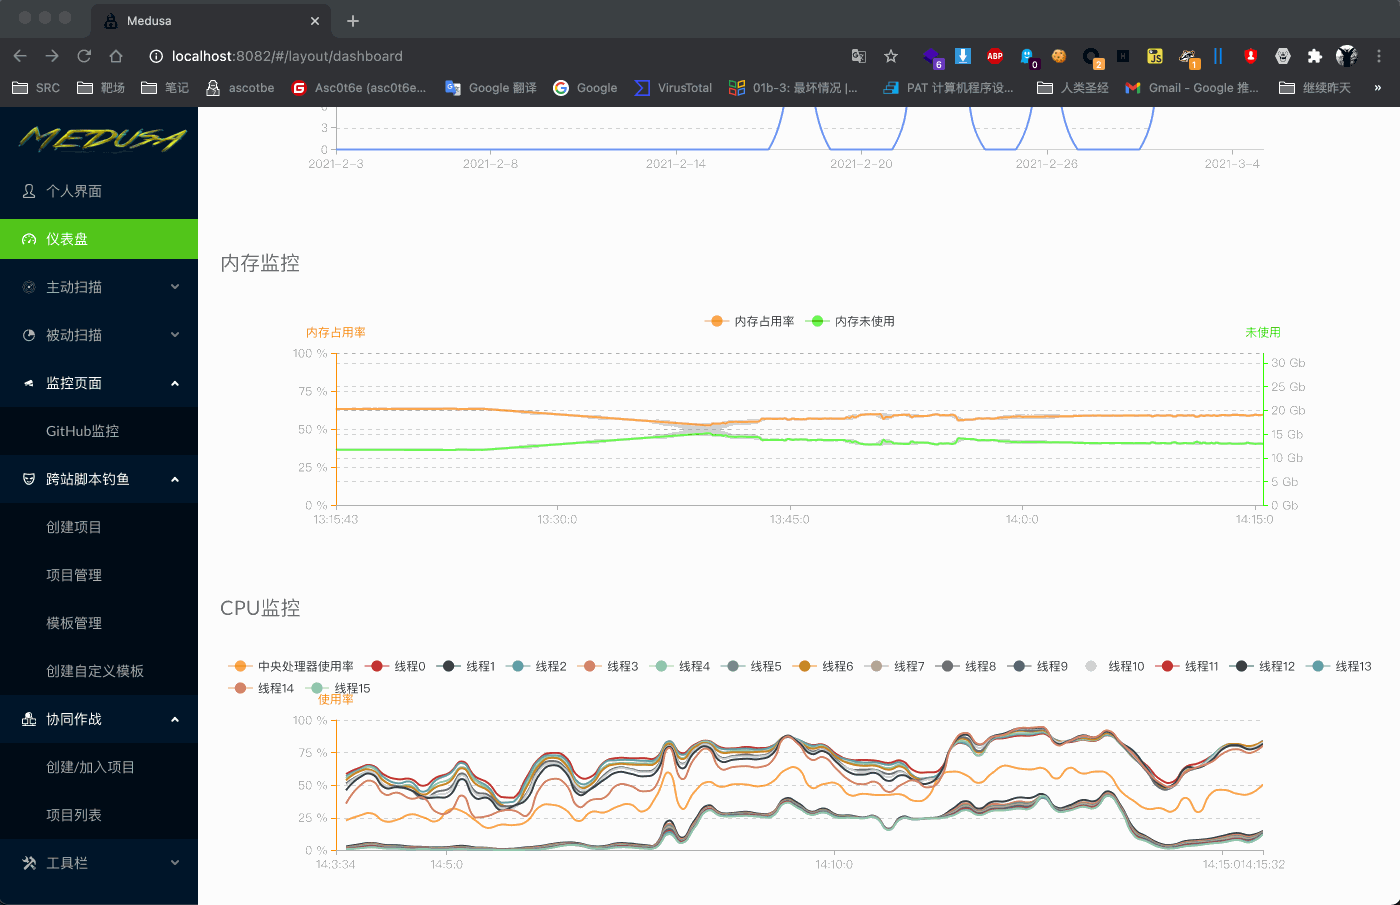 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中