CVE-2024-21413
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
email-securityexploitationpassword-cracking+3
dionissh/cve-2024-21413Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 joelgmsec/evilnovnc
Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 darkarp/chromepass
Chromepass - Hacking Chrome Saved Passwords
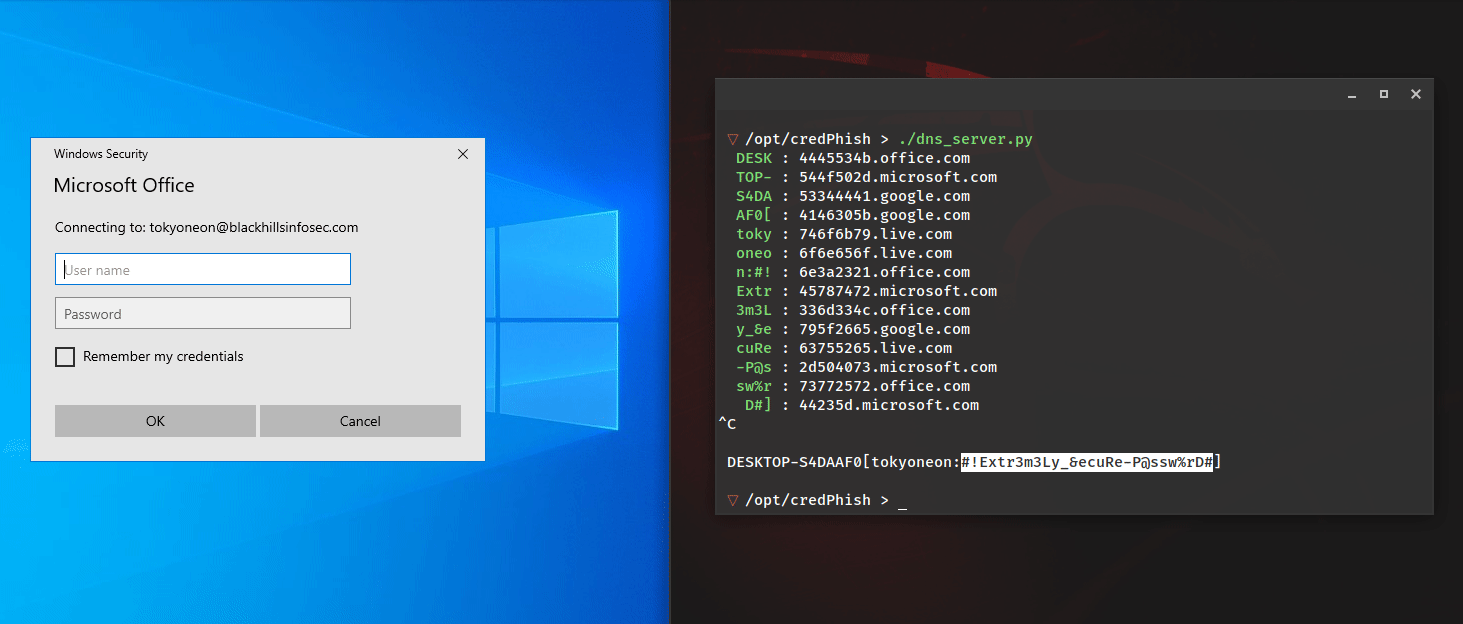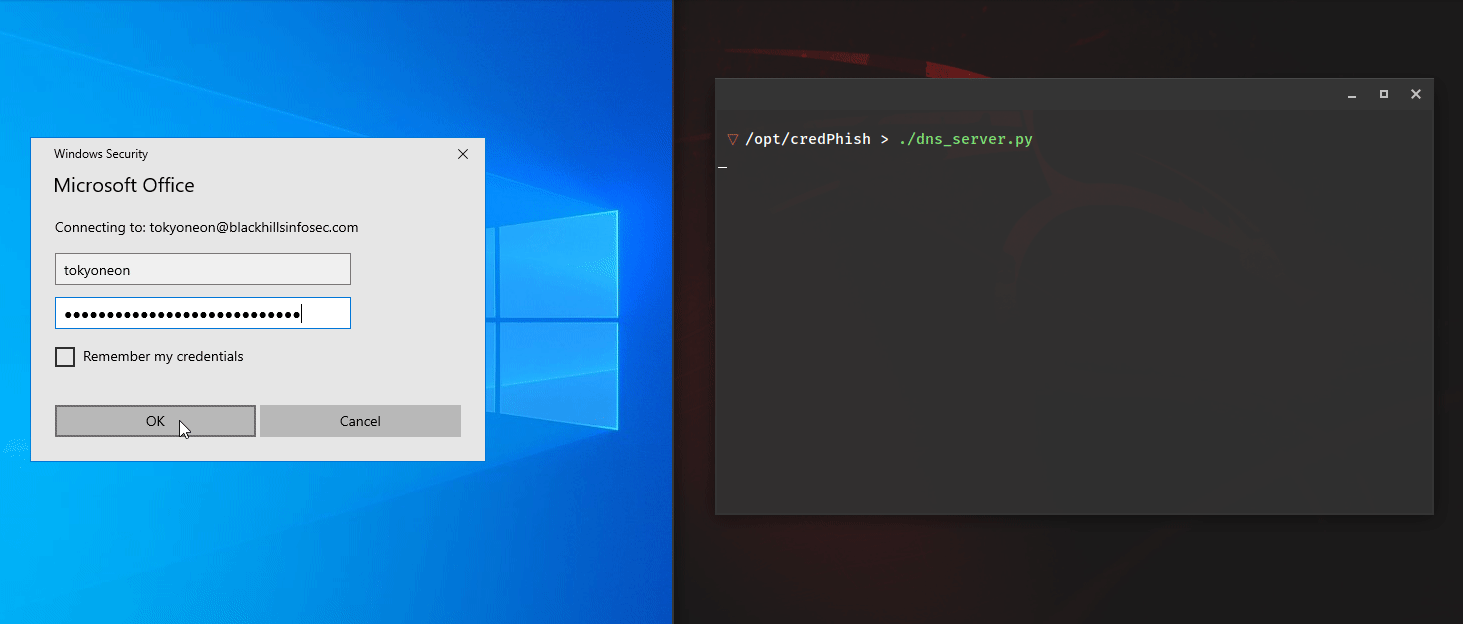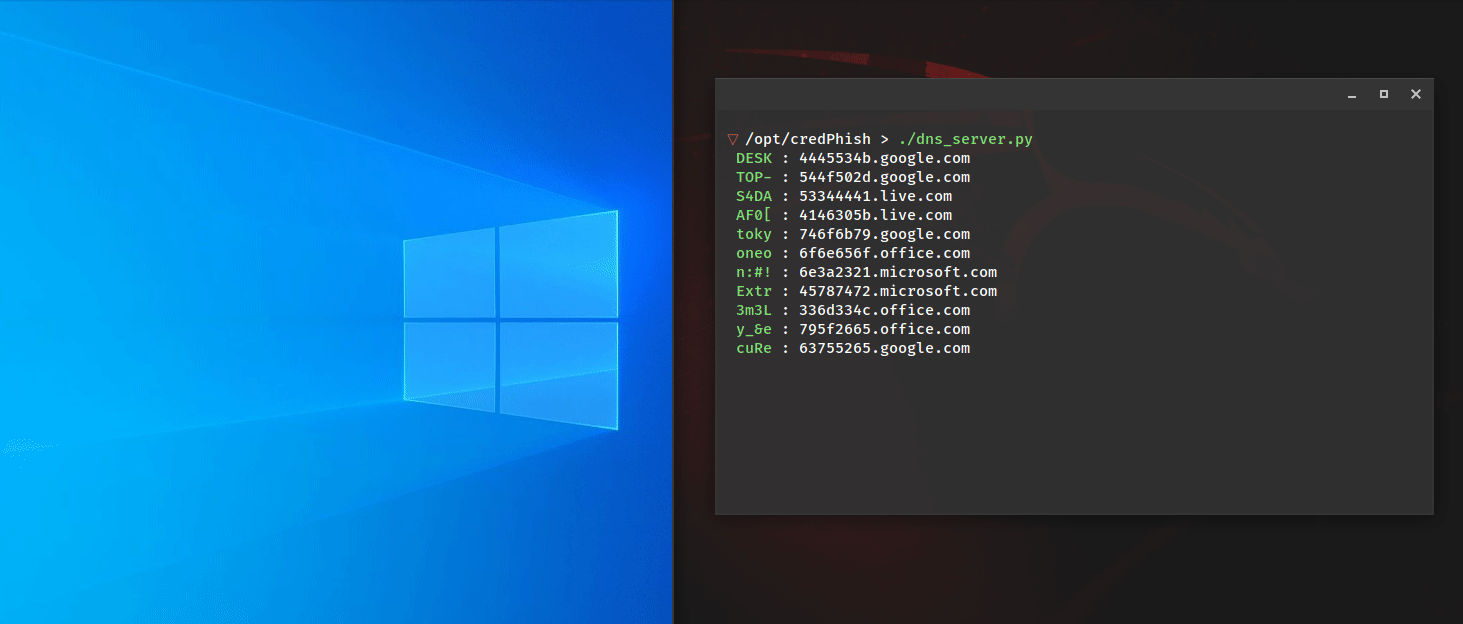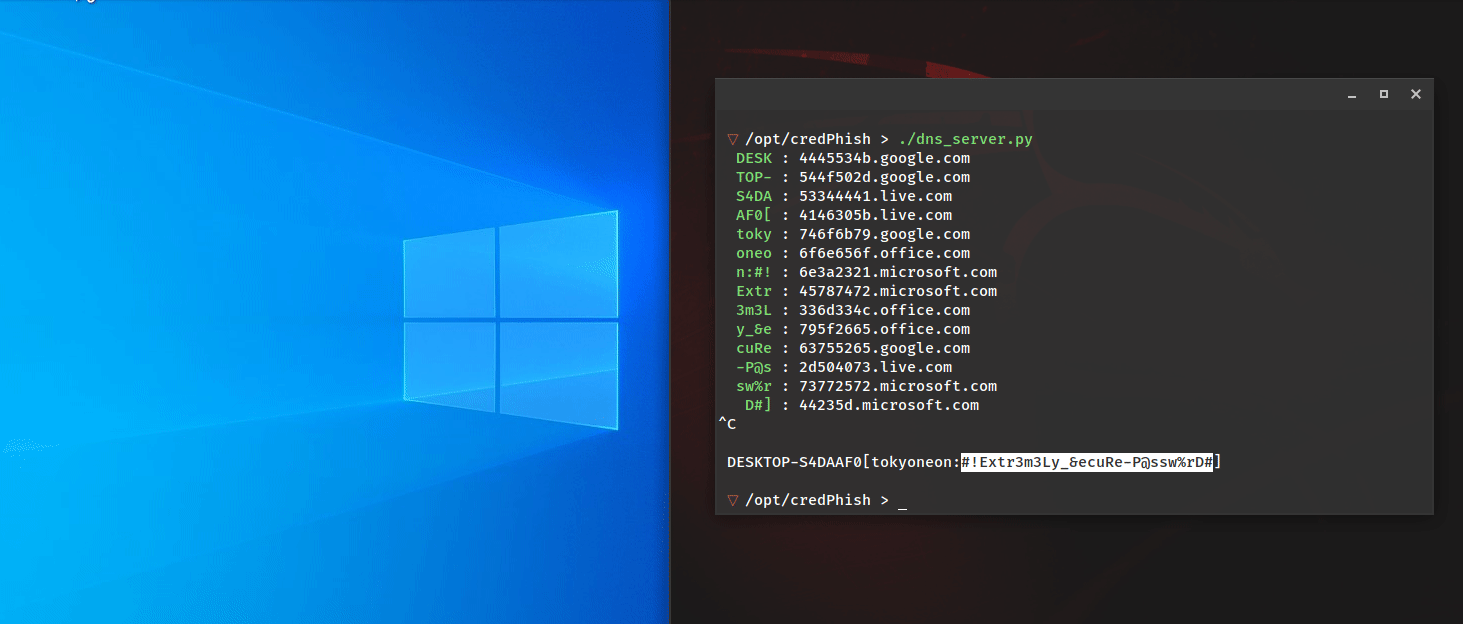 tokyoneon/credphish
PowerShell script that invokes legitimate credential prompts and exfiltrates captured passwords over DNS using CredentialPicker and Resolve-DnsName.
 atn1ght/fakeauth
Creates Fake Auth prompt to capture users plaintext passwords