
Evilginx3-Phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers

Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…

A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…

Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…

Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…

Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…

PoC of the phishing through setting browser in the fullscreen mode

TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…

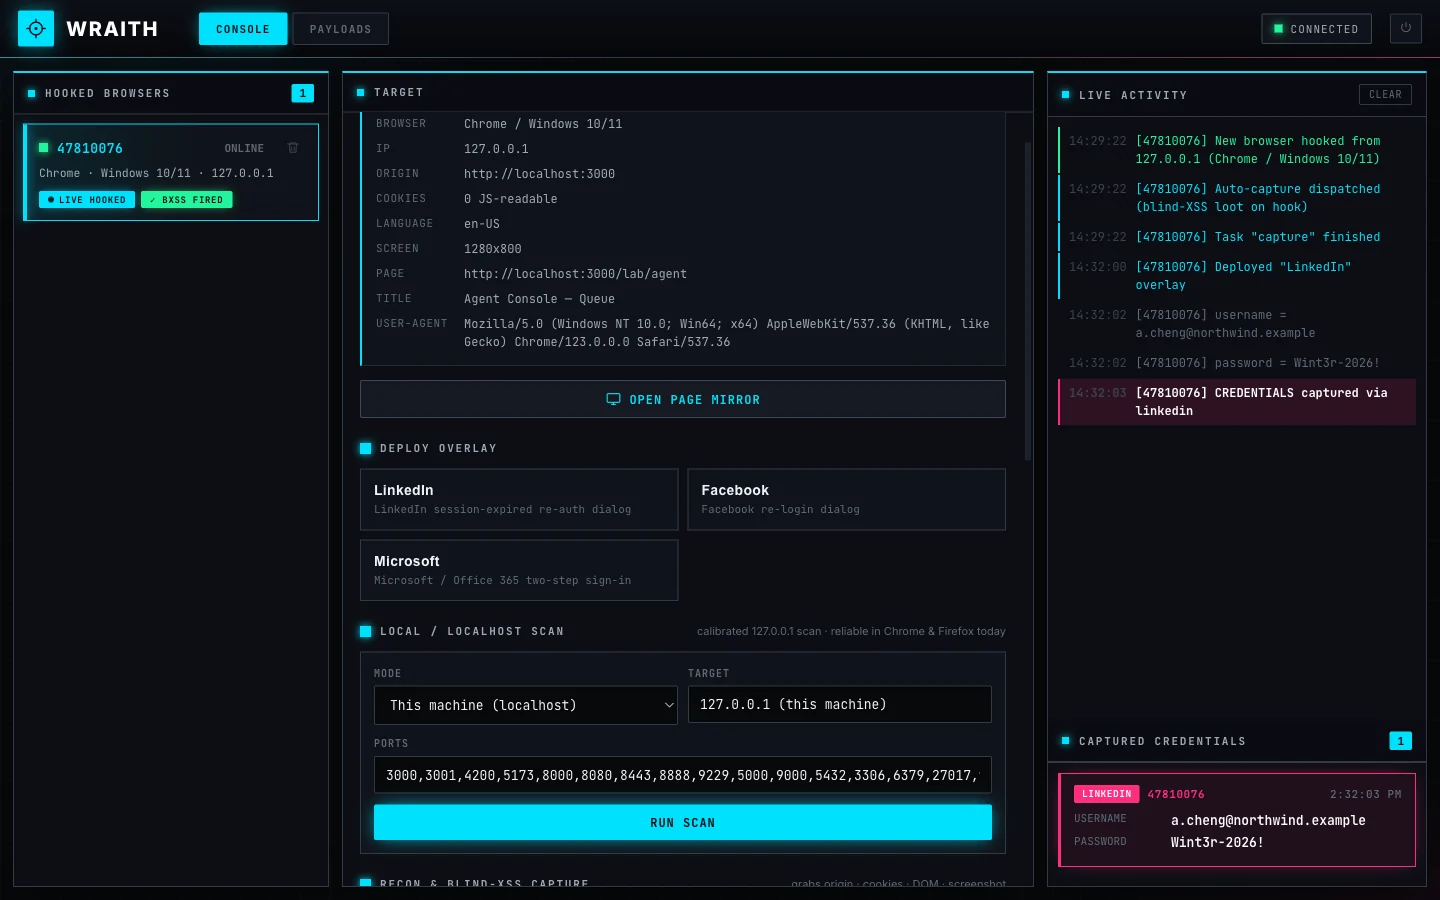
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…

CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…

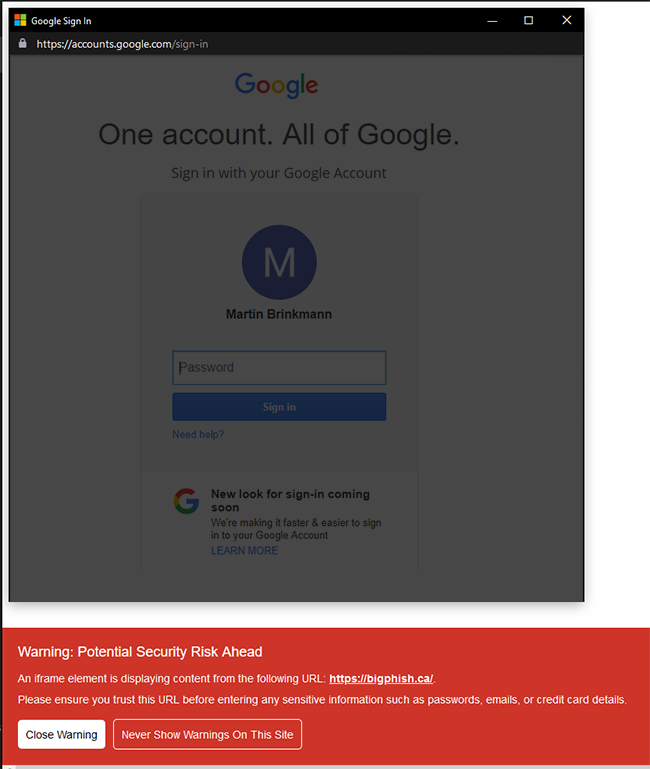
A lightweight extension to automatically detect and provide verbose warnings for embedded iframe elements in order to protect against…

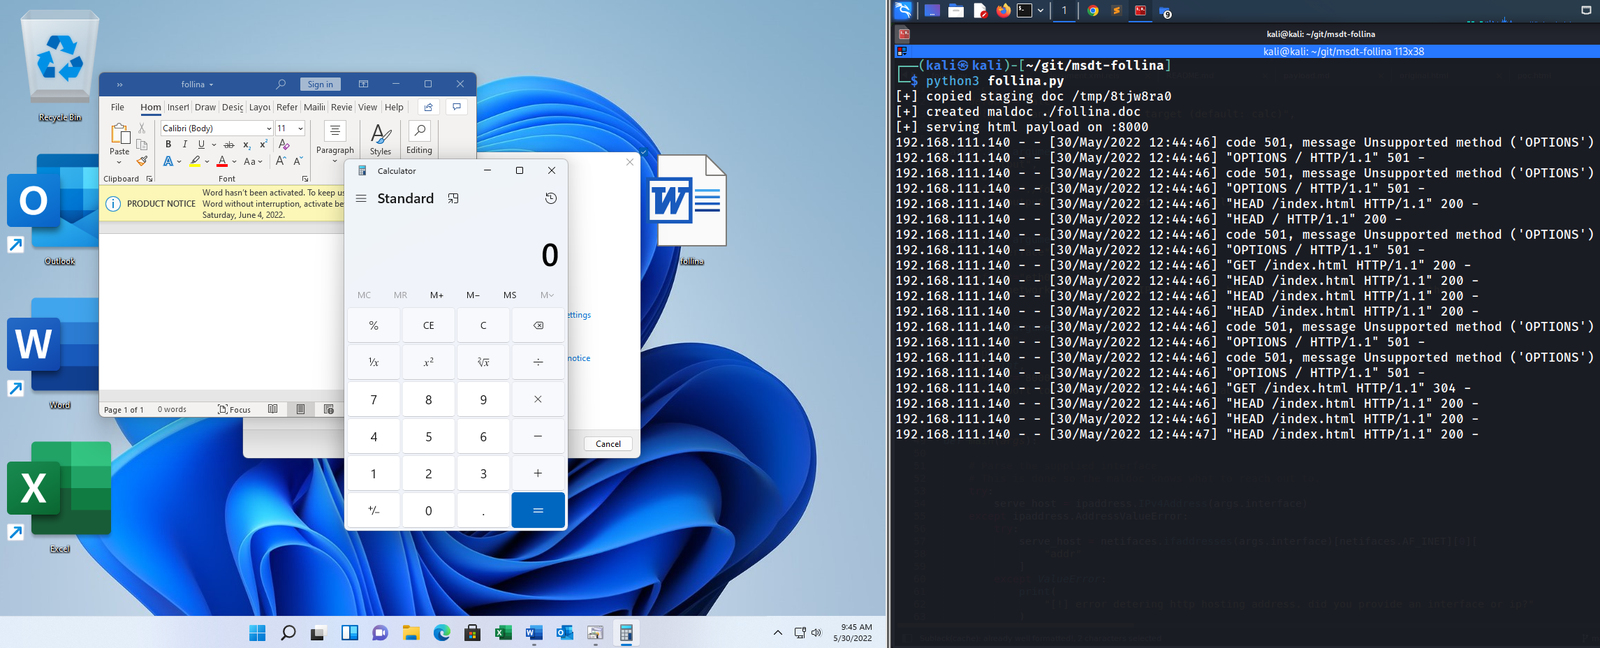
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…

Proof-of-concept exploit for unauthenticated SSRF and open email relay in Chamilo LMS via install.ajax.php, allowing internal network probing and…

Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…