

llm-security
 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
adversarial-attackai-securitycommand-and-control+7
2.1k
greshake/llm-securityProof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 alkimcoskun/yordam-kutuphane-otomasyonunda-coklu-html-enjeksiyonu
CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…
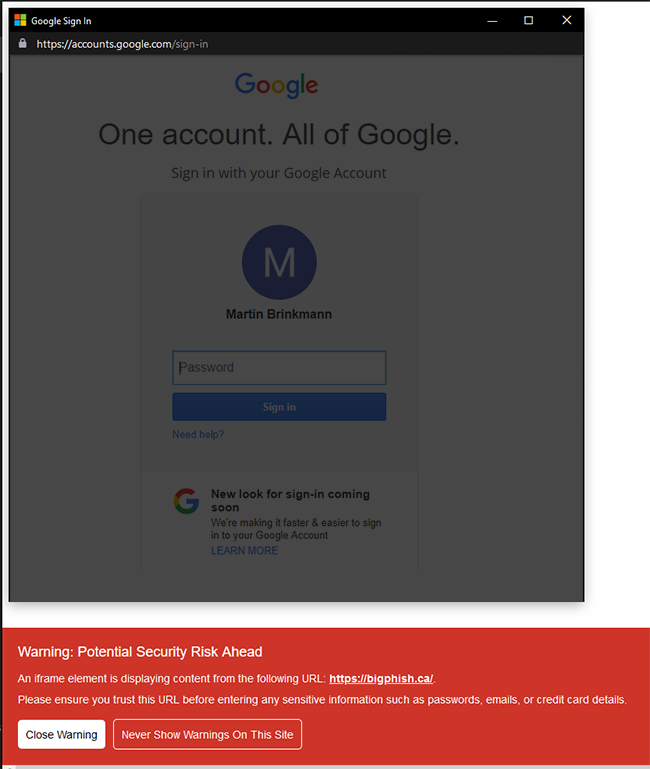 malwarecube/enhanced-iframe-protection
A lightweight extension to automatically detect and provide verbose warnings for embedded iframe elements in order to protect against…
 bluscreenofjeff/red-team-infrastructure-wiki
Wiki to collect Red Team infrastructure hardening resources
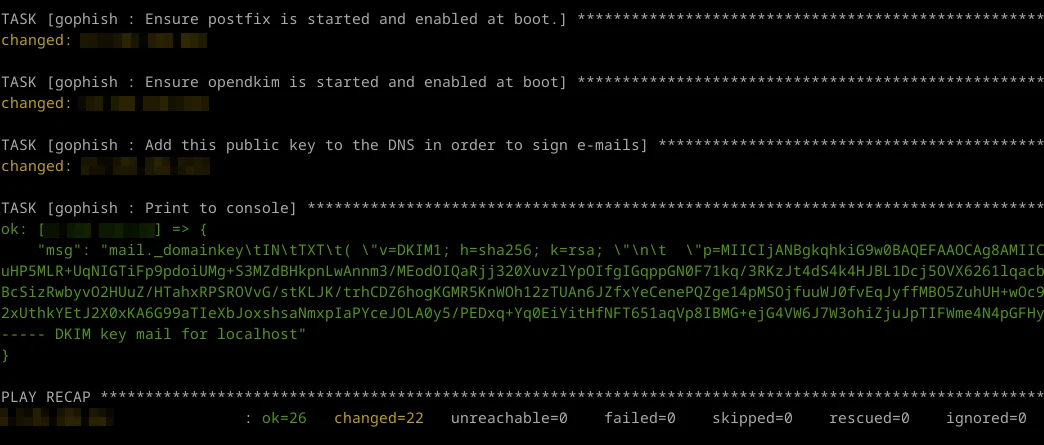 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
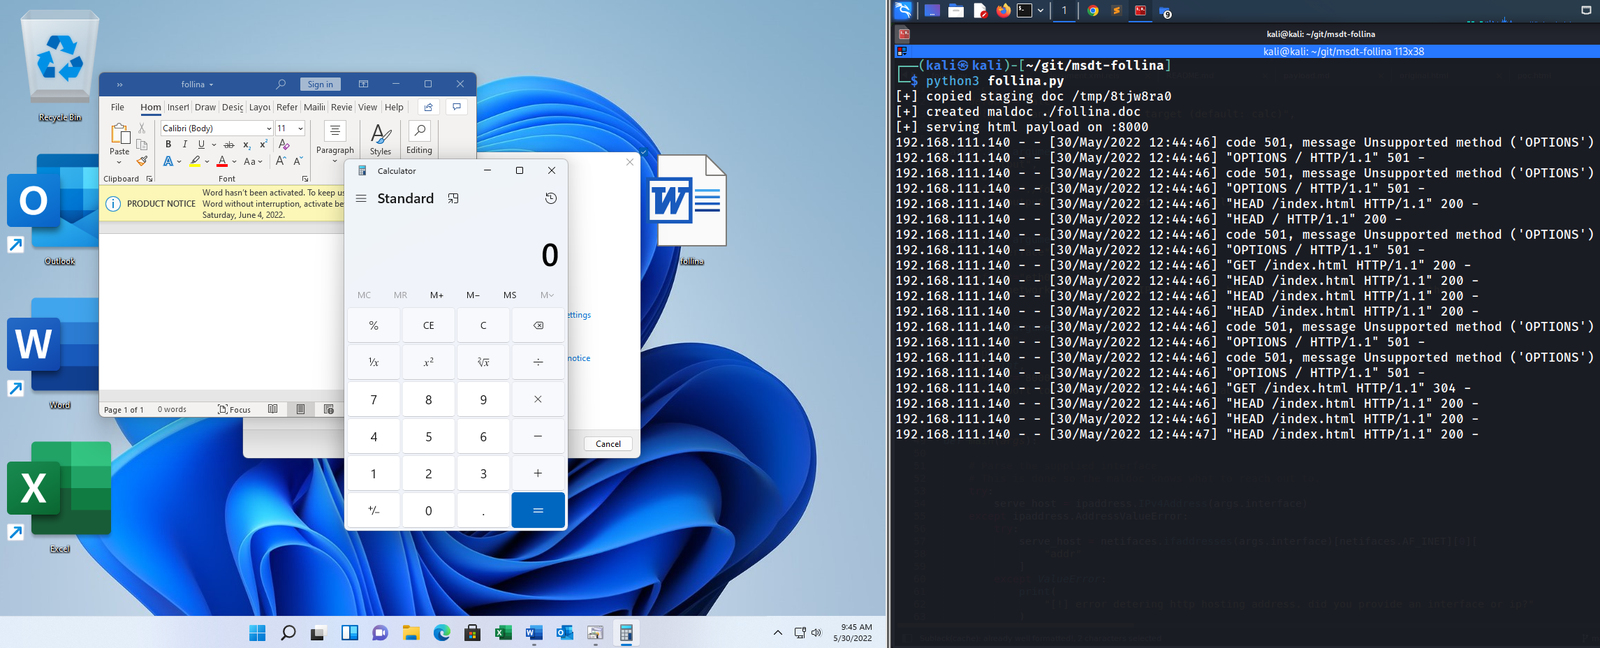 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
 romain-deperne/cve-2026-33715
Proof-of-concept exploit for unauthenticated SSRF and open email relay in Chamilo LMS via install.ajax.php, allowing internal network probing and…
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
 kimstars/ashwesker-cve-2026-21509
Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 ajansha/cve-2025-55903
Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…