npm-incident-response

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

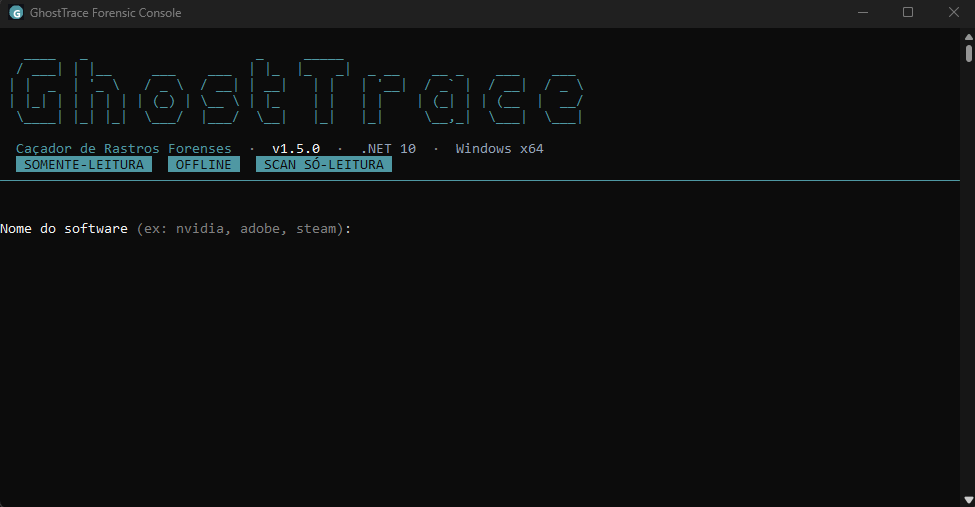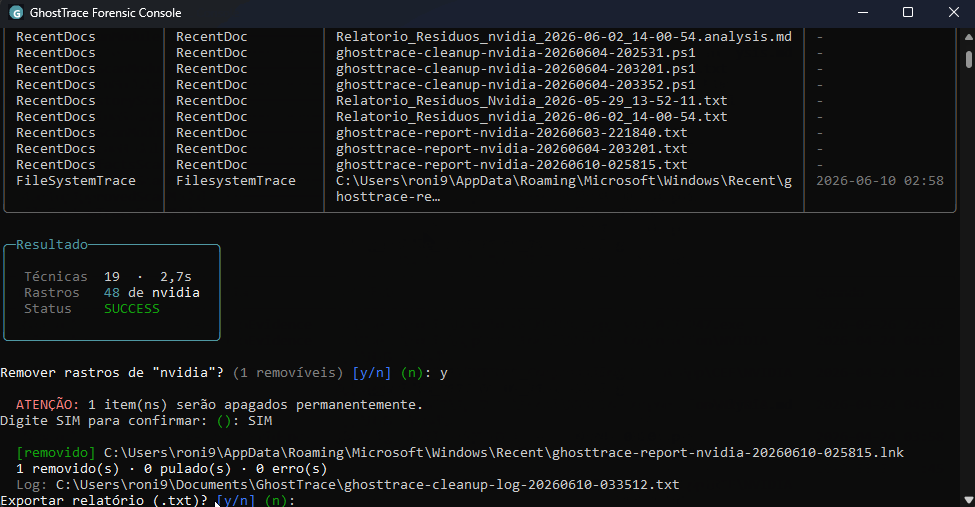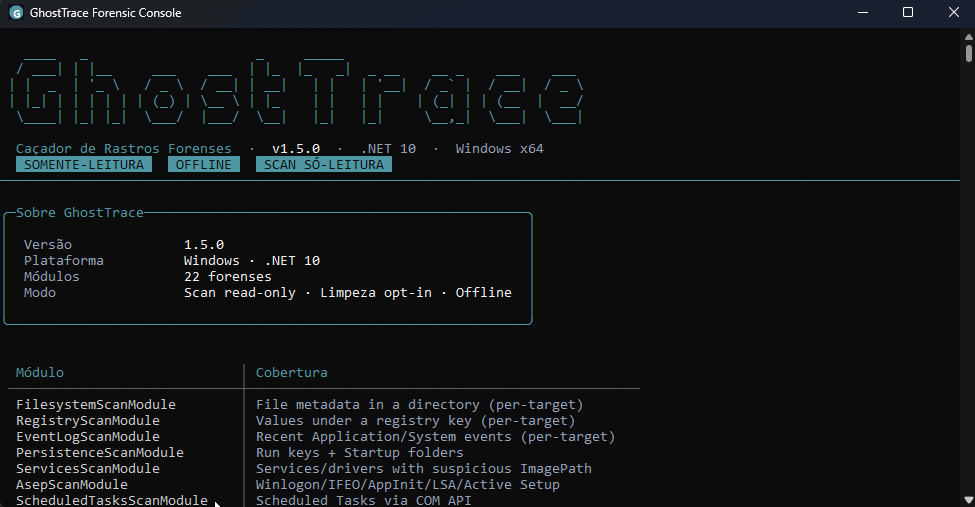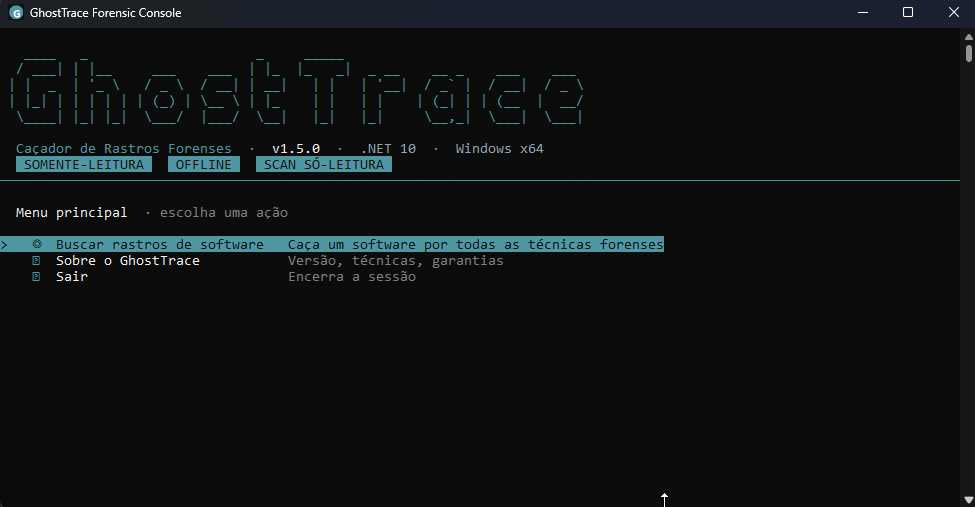
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)

The patching of Android kernel and Android system

Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…

Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

LKM rootkit for Linux Kernels 2.6.x-7.x (x86/x86_64 and ARM/ARM64)

An open-source post-exploitation framework for students, researchers and developers.

Attack and defend active directory using modern post exploitation adversary tradecraft activity

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…

📦 Make security testing of K8s, Docker, and Containerd easier.

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.