
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
487 results
PersistenceSniper preview

PersistenceSniper

GitHublast-byte/persistencesniper

Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
defensive-toolsforensicsincident-response+1
2.1k
1 year ago
Nimbo-C2 preview

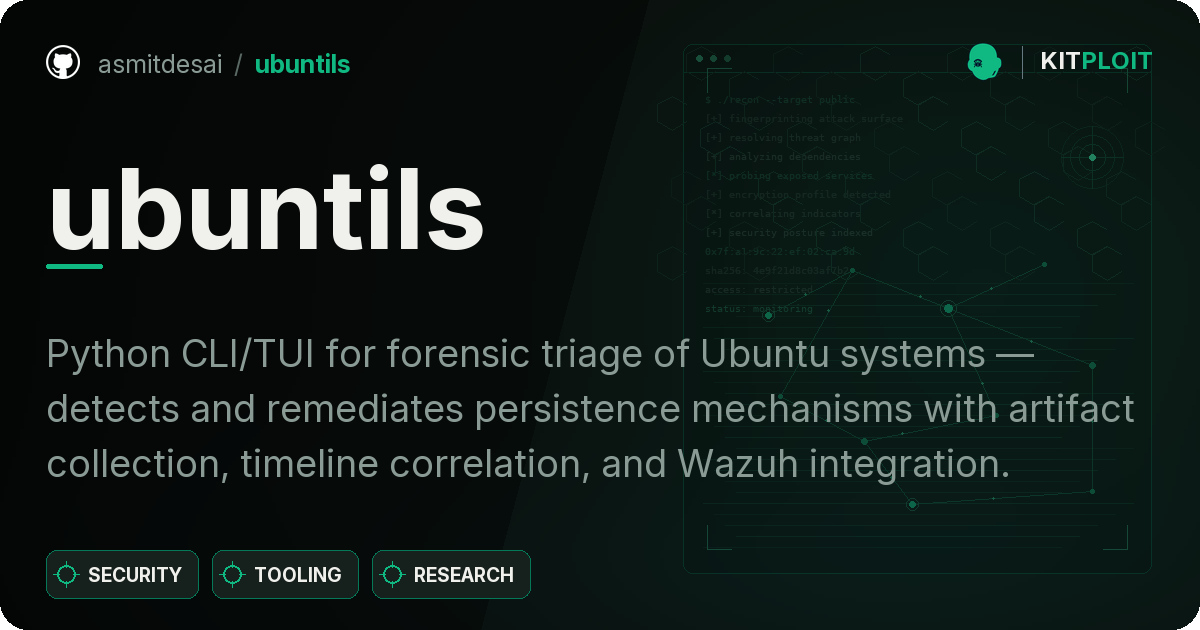
Nimbo-C2

GitHubitaymigdal/nimbo-c2

Nimbo-C2 is yet another (simple and lightweight) C2 framework

command-and-controlexploit-frameworkspayload-generation+5
4478 months ago
Pegasus-Gram preview

Pegasus-Gram

GitHubsobri3195/pegasus-gram

Python-based keylogger and surveillance tool with Telegram C2, capturing keystrokes, screenshots, webcam, audio, clipboard, and system activity for…

command-and-controldata-exfiltrationinformation-gathering+2
131 year ago
CVE-2024-31771 preview

CVE-2024-31771

GitHubrestdone/cve-2024-31771

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…

binary-exploitationexploitationlateral-movement+4
2 years ago
Lime-RAT preview
Archived

Lime-RAT

GitHubnyan-x-cat/lime-rat

LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)

command-and-controlcryptographydata-exfiltration+7
1.1k7 years ago
Cable preview

Cable

GitHublogangoins/cable

.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
authenticationconfiguration-auditingexploitation+8
4011 year ago
ubuntils preview

ubuntils

GitHubasmitdesai/ubuntils

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
configuration-auditingdefensive-toolsdigital-forensics+7
512 days ago
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
configuration-auditingdefensive-toolsincident-response+8
1 month ago
sqlwinds preview

sqlwinds

GitHubblue0x1/sqlwinds

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
configuration-auditingdatabase-securitydata-exfiltration+7
1 year ago
PowerUpSQL preview

PowerUpSQL

GitHubnetspi/powerupsql

PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server

configuration-auditingdatabase-securityexploitation+9
2.7k1 year ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
command-and-controldatabase-securitydata-exfiltration+20
39.1k1 day ago
APatch preview

APatch

GitHubbmax121/apatch

The patching of Android kernel and Android system

android-securitymobile-securitypayload-development+4
8.0k7 days ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.0k1 year ago
SQLC2 preview

SQLC2

GitHubnetspi/sqlc2

SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.

cloud-securitycommand-and-controldatabase-security+3
763 years ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

binary-analysiscommand-and-controldefensive-tools+6
1614 days ago
SmmBackdoor preview

SmmBackdoor

GitHubcr4sh/smmbackdoor

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
exploitationfirmware-analysishardware-hacking+4
6352 years ago
phantom-keylogger preview

phantom-keylogger

GitHubmattiaalessi/phantom-keylogger

Phantom Keylogger is an advanced, stealth-enabled keystroke and visual intelligence gathering system.

command-and-controldata-exfiltrationids-ips-evasion+6
779 months ago
WinRAR-CVE-2025-8088-Exploitation-Toolkit preview

WinRAR-CVE-2025-8088-Exploitation-Toolkit

GitHubxi0onamdev/winrar-cve-2025-8088-exploitation-toolkit

GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…

binary-exploitationeducationexploitation+7
10 months ago
Previous12…28Next