
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
98 results
Discord-Rat preview

Discord-Rat

GitHubgmh5225/discord-rat

Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…
command-and-controldata-exfiltrationencryption-decryption-tools+7
1 year ago
Snaffler preview

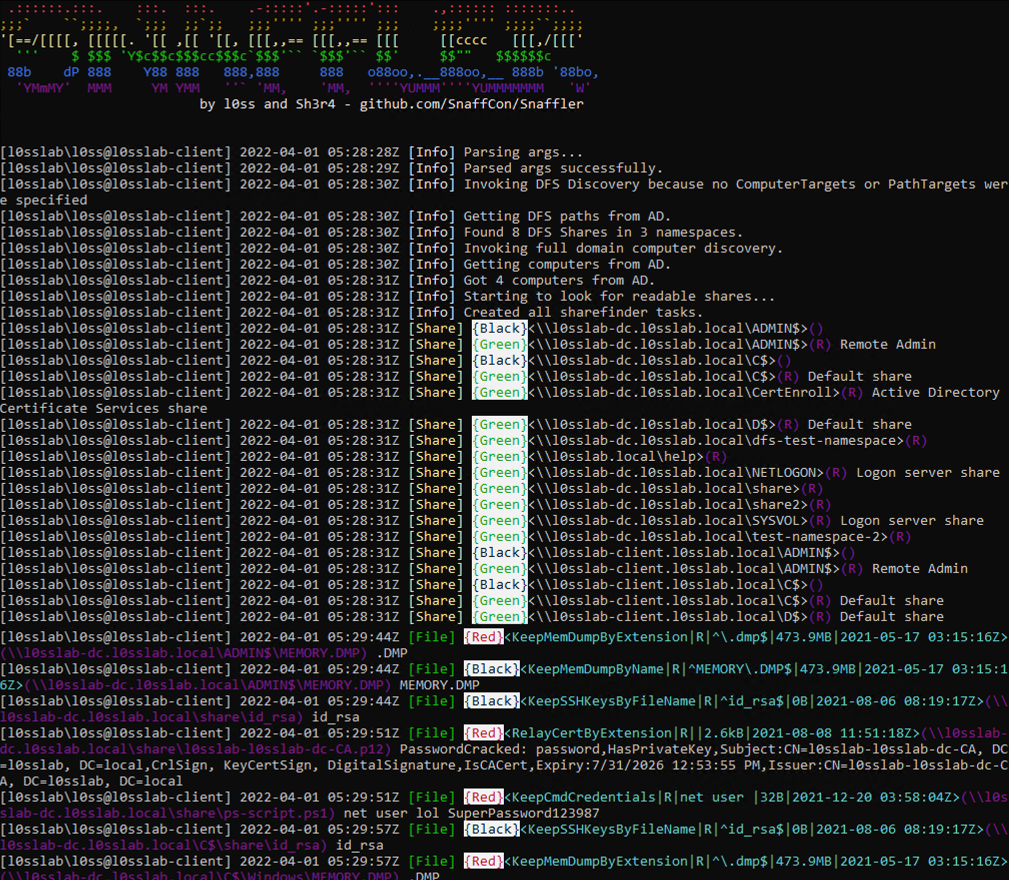
Snaffler

GitHubsnaffcon/snaffler

a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
information-gatheringlateral-movementpenetration-testing+4
3.0k7 months ago
libprocesshider preview

libprocesshider

GitHubgianlucaborello/libprocesshider

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
defensive-toolsinformation-gatheringmalware-analysis+4
1.1k7 years ago
Adrenaline preview

Adrenaline

GitHubatomiczsec/adrenaline

C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
command-and-controldefensive-toolsinformation-gathering+7
3181 month ago
FarsightAD preview

FarsightAD

GitHubqazeer/farsightad

PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…

forensicsincident-responseinformation-gathering+5
989 months ago
honeybits preview
Archived

honeybits

GitHub0x4d31/honeybits

A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

information-gatheringlateral-movementosint-social-engineering+5
2787 years ago
CVE-2017-9779 preview

CVE-2017-9779

GitHubhomjxi0e/cve-2017-9779

Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc

exploitationpayload-developmentpenetration-testing+3
9 years ago
SharpGPOAbuse preview

SharpGPOAbuse

GitHubreverseclabs/sharpgpoabuse

SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
exploitationlateral-movementpenetration-testing+4
1.4k5 years ago
FolkPatch preview

FolkPatch

GitHublyravoid/folkpatch

Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
android-securitymobile-securitypayload-development+3
1.2k4 days ago
PersistenceSniper preview

PersistenceSniper

GitHublast-byte/persistencesniper

Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…

defensive-toolsforensicsincident-response+1
2.1k1 year ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…

command-and-controlexploitationids-ips-evasion+8
5995 years ago
EDR-Preloader preview

EDR-Preloader

GitHubmalwaretech/edr-preloader

An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer

defensive-toolsids-ips-evasionpersistence-mechanisms+3
5562 years ago
AV-EDR-Killer preview

AV-EDR-Killer

GitHubxm0kht4r/av-edr-killer

AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
command-and-controlexploitationids-ips-evasion+5
2998 months ago
RATel preview

RATel

GitHubfrenchcisco/ratel

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
2765 years ago
SharpEventPersist preview

SharpEventPersist

GitHubimprosec/sharpeventpersist

Persistence by writing/reading shellcode from Event Log
payload-generationpersistence-mechanismspost-exploitation+1
3754 years ago
USP preview

USP

GitHubgrahamhelton/usp

Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)

payload-developmentpersistence-mechanismspost-exploitation+2
1532 years ago
MrKaplan preview

MrKaplan

GitHubidov31/mrkaplan

PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
defensive-toolsforensicsids-ips-evasion+3
2763 years ago
Windows-Python-RAT preview

Windows-Python-RAT

GitHubthe404hacking/windows-python-rat

A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.

api-securitycommand-and-controlpayload-development+3
1186 years ago
Previous123456Next