
DigiTrack
 skickar/digitrack
Attacks for $5 or less using Arduino
hardware-hackinginformation-gatheringpersistence-mechanisms+2
skickar/digitrackAttacks for $5 or less using Arduino
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
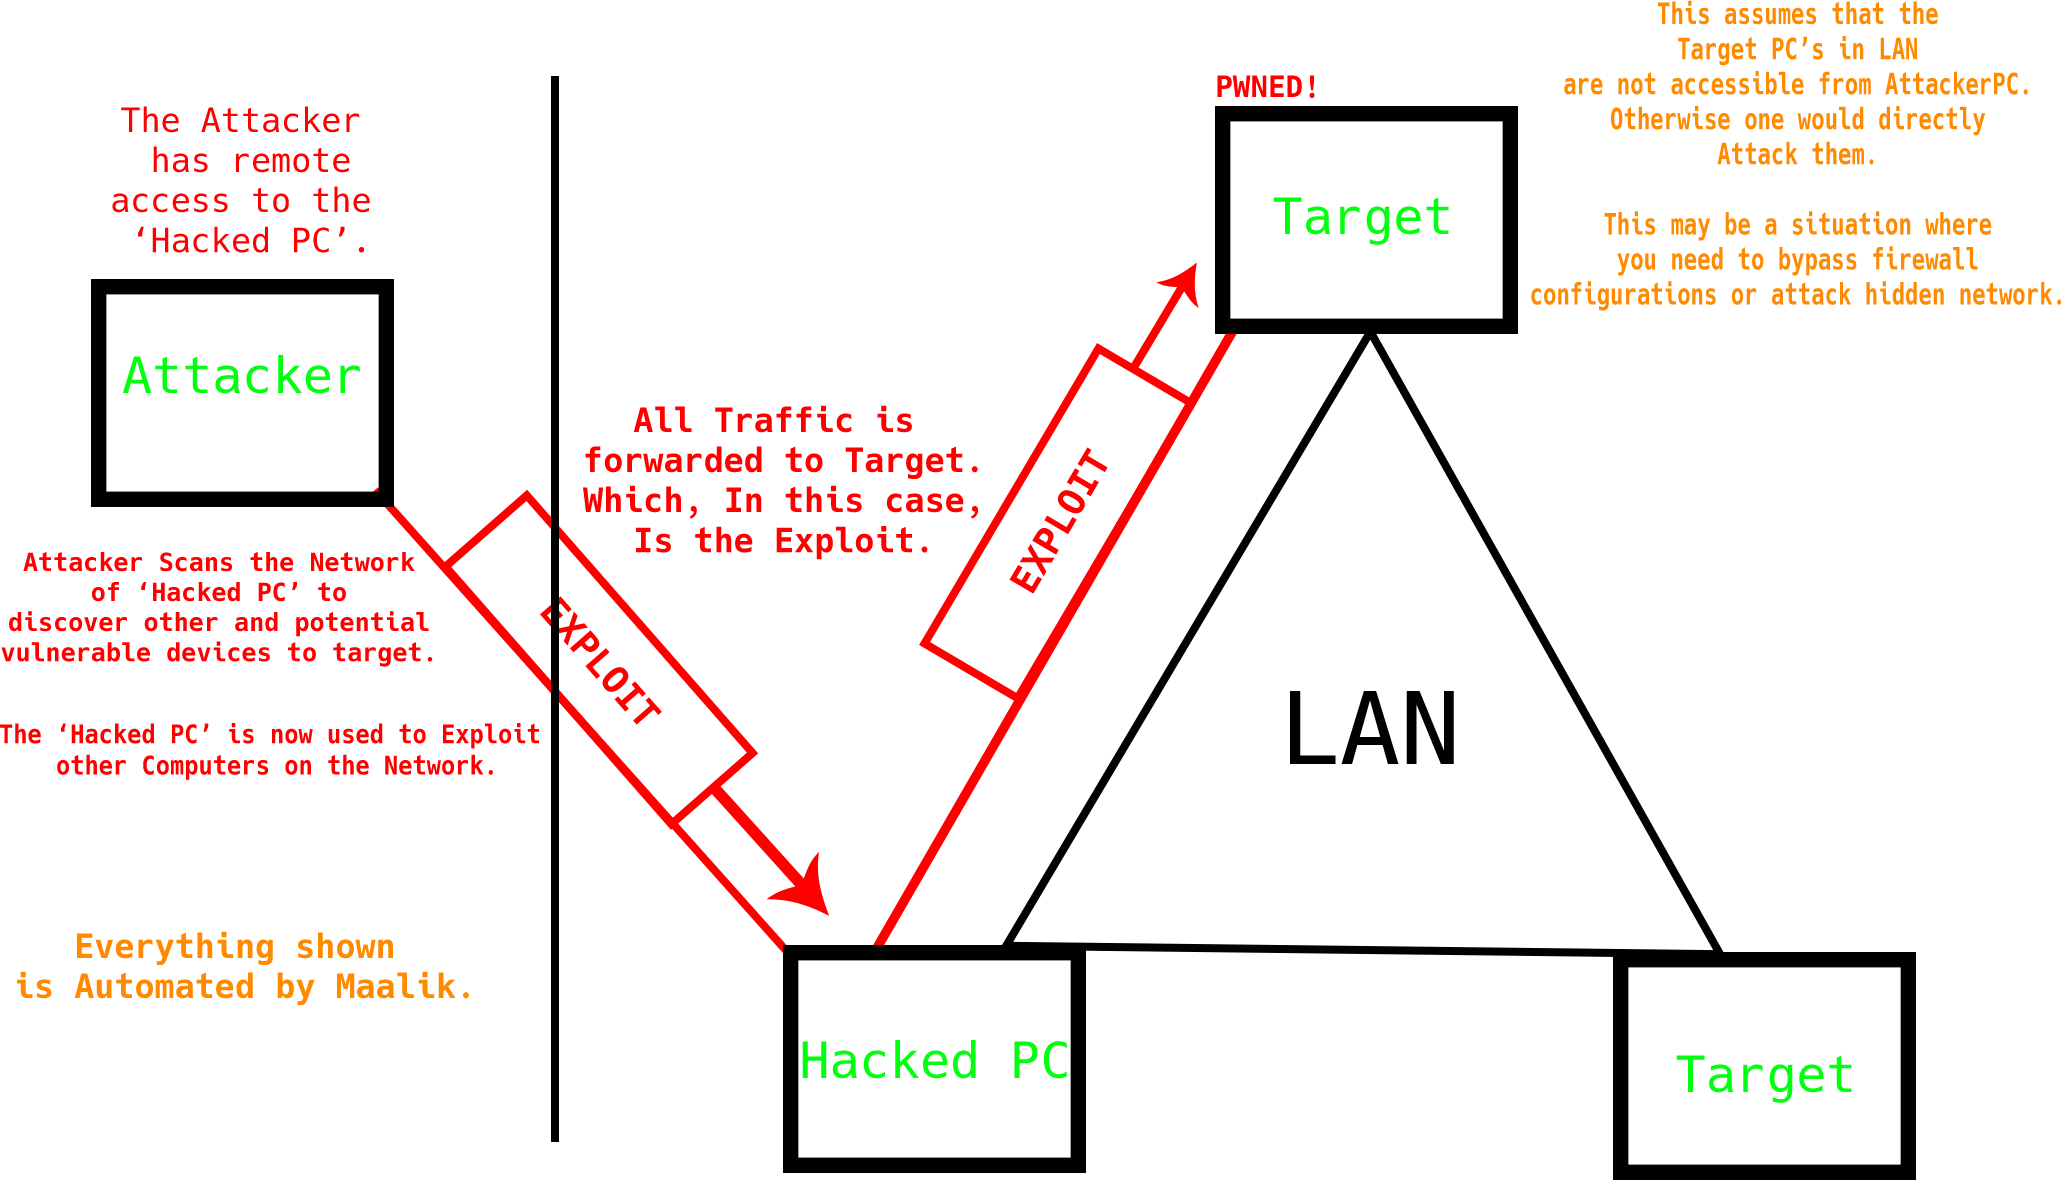 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
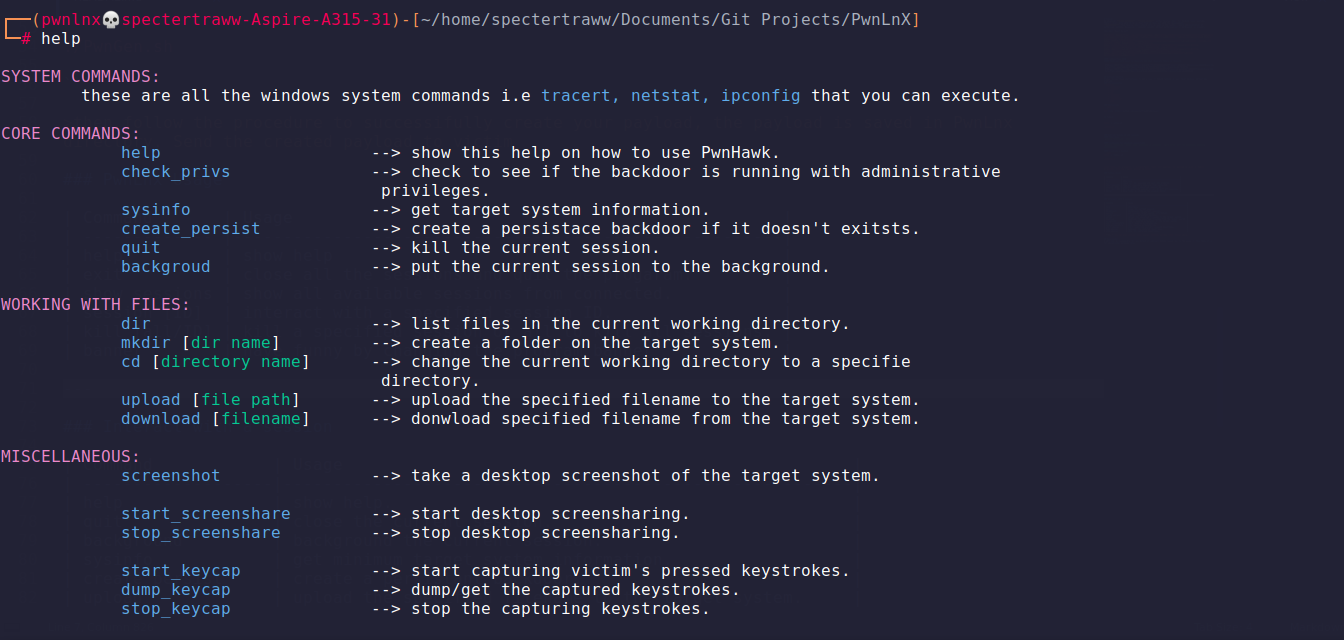 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
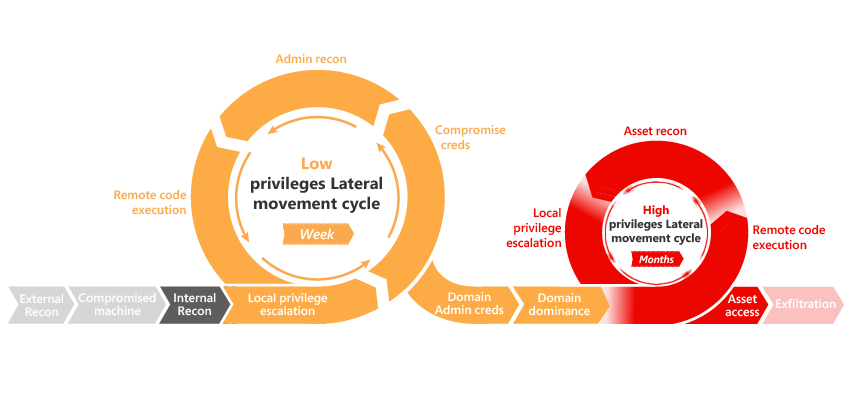 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
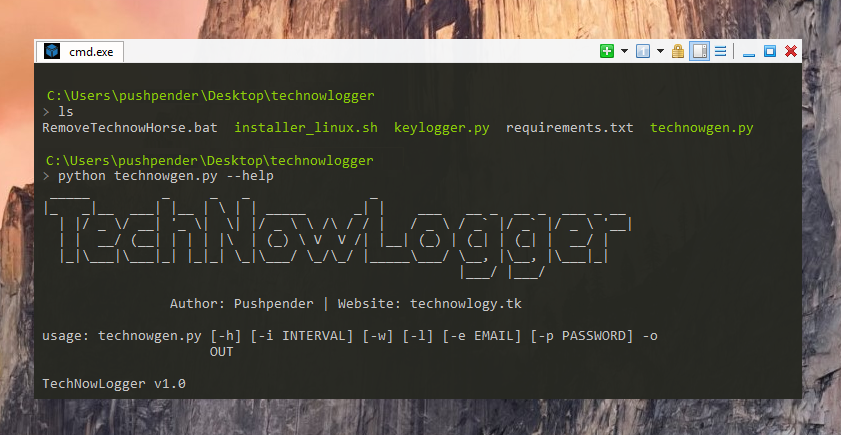 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
 thegeekht/loki.rat
Loki.Rat is a fork of the Ares RAT, it integrates new modules, like recording , lockscreen , and locate options. Loki.Rat is a Python Remote Access…
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 gentilkiwi/mimikatz
A little tool to play with Windows security