
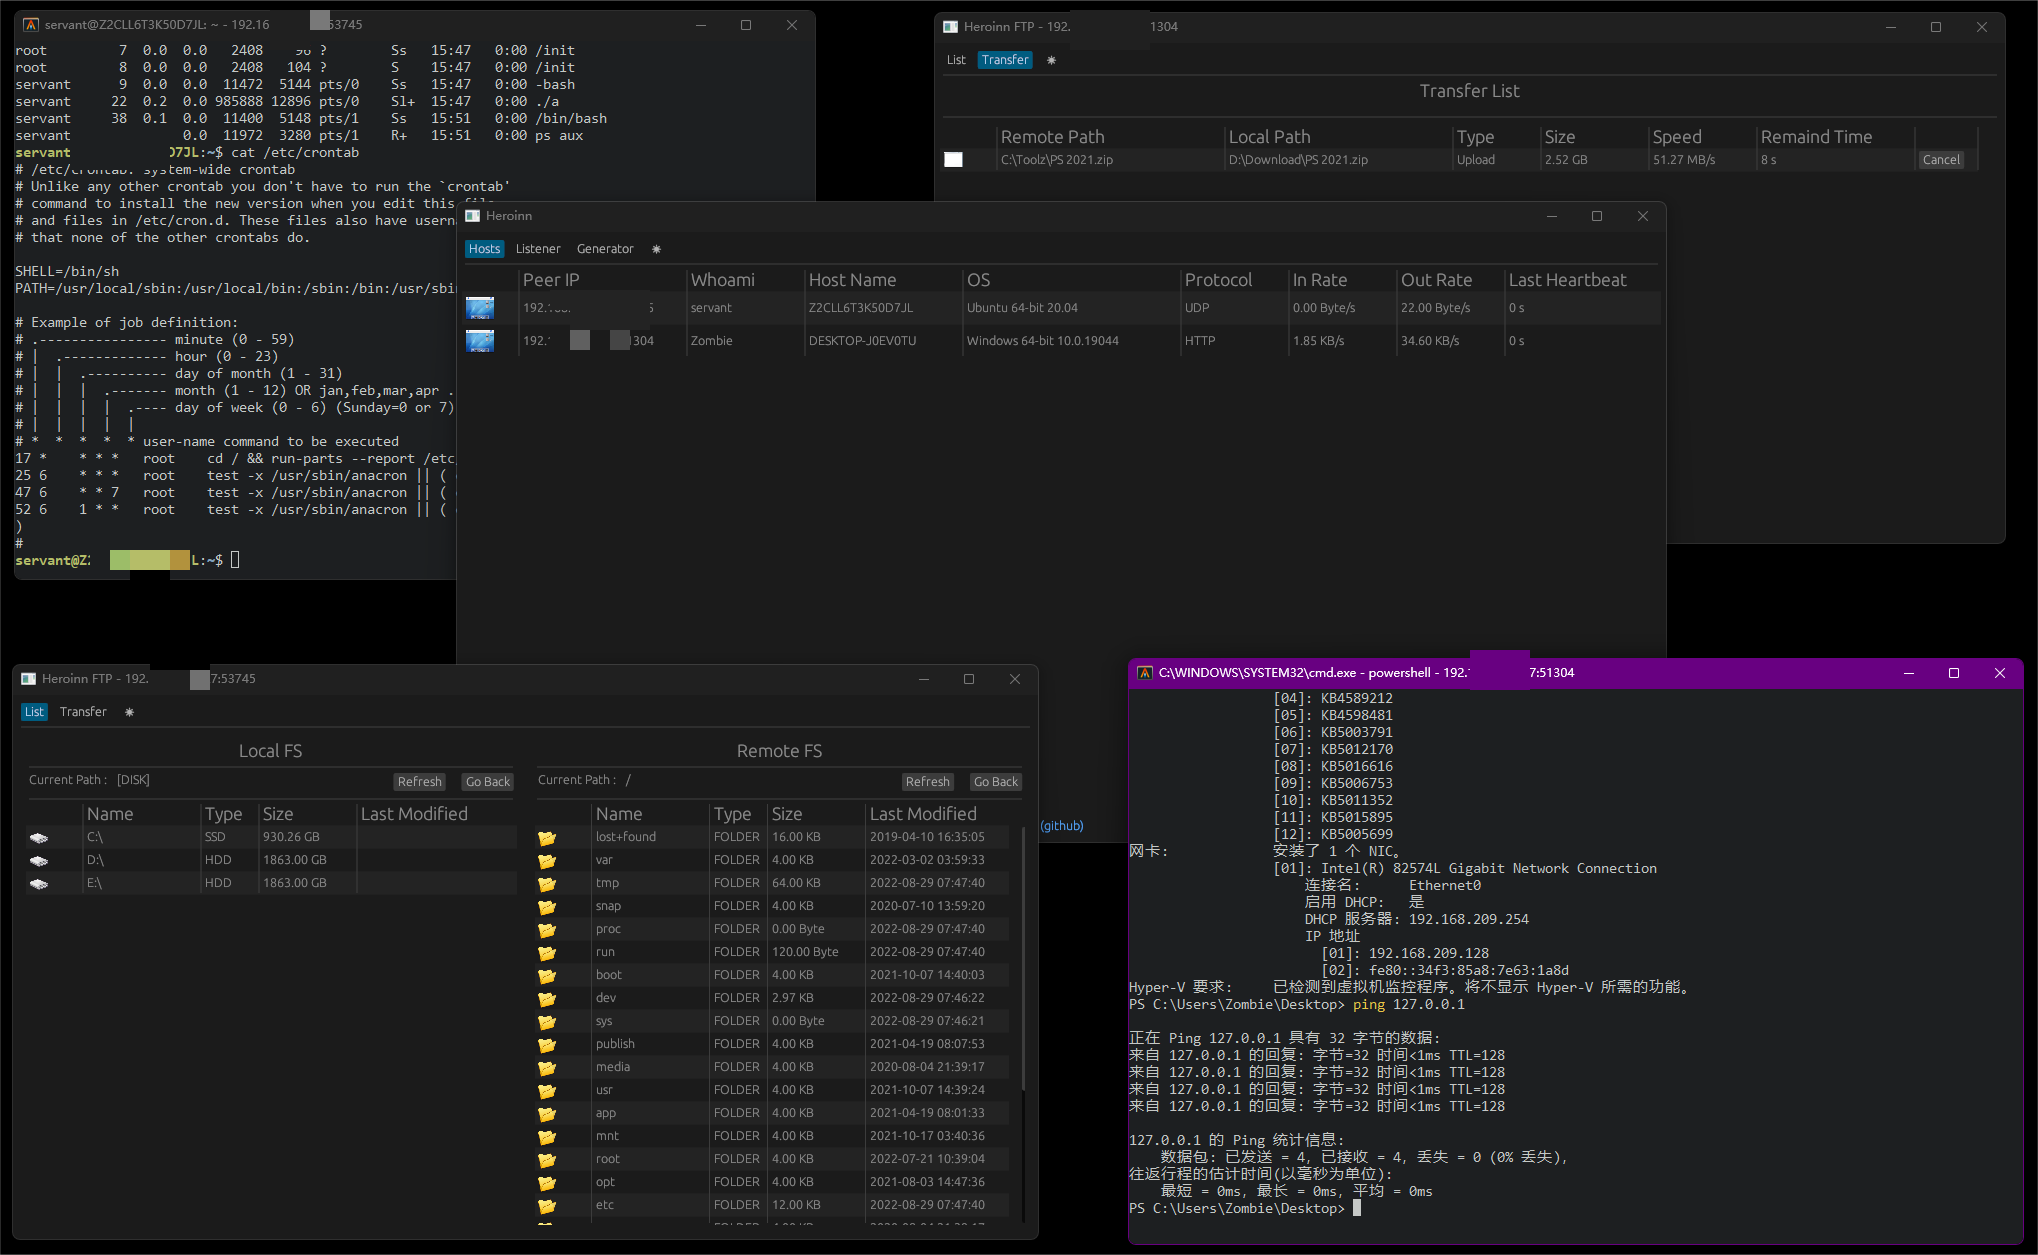
Heroinn
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
command-and-controldata-exfiltrationlateral-movement+8
b23r0/heroinnA cross platform C2/post-exploitation framework.
 calebstewart/pwncat
Post-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
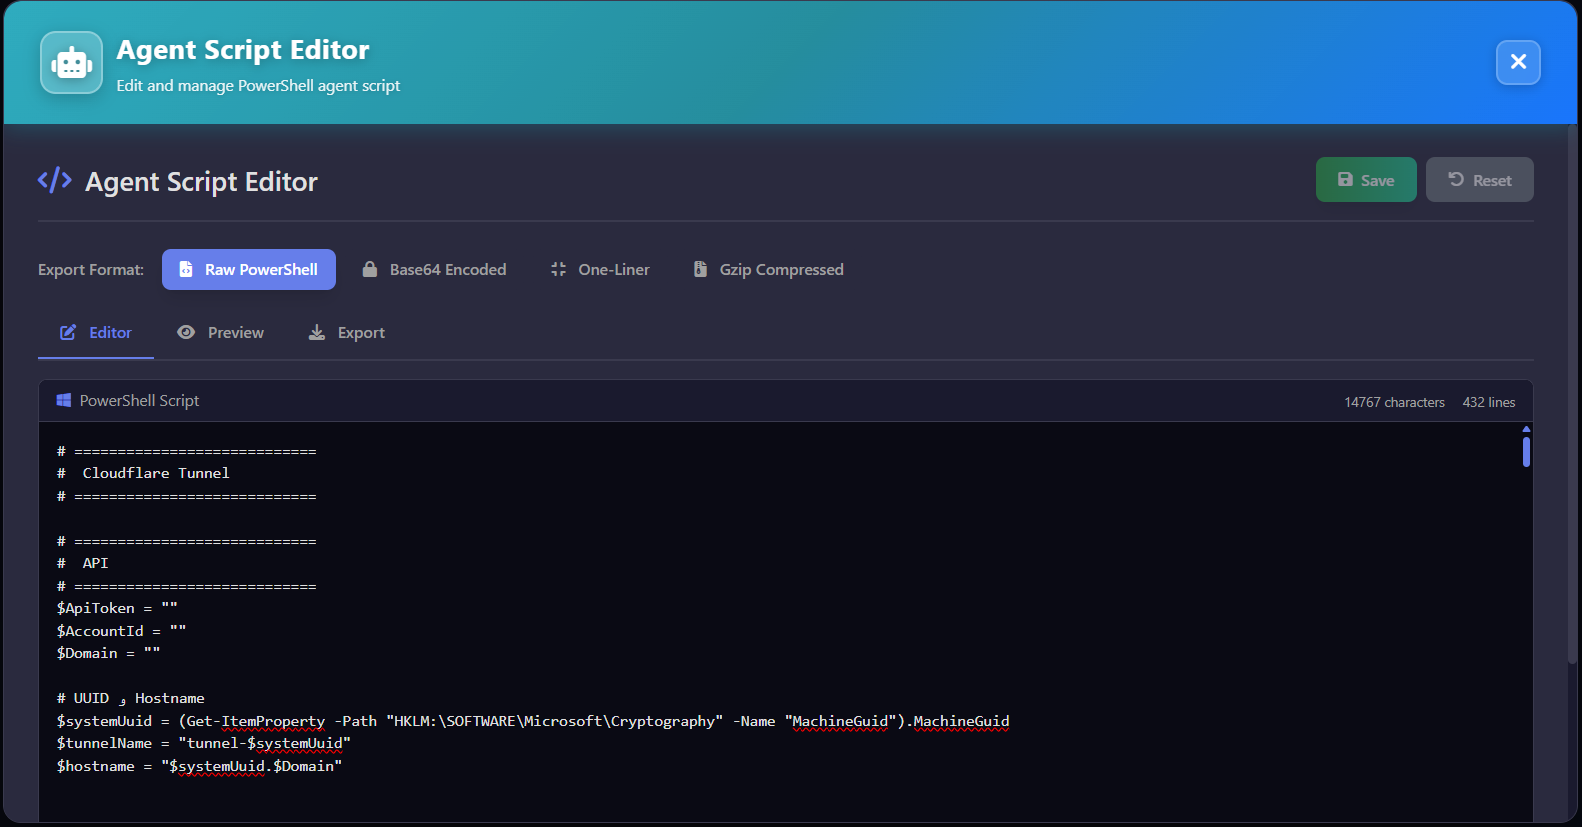 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 machine1337/pyfud
CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)
 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 bishopfox/sliver
Adversary Emulation Framework
 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
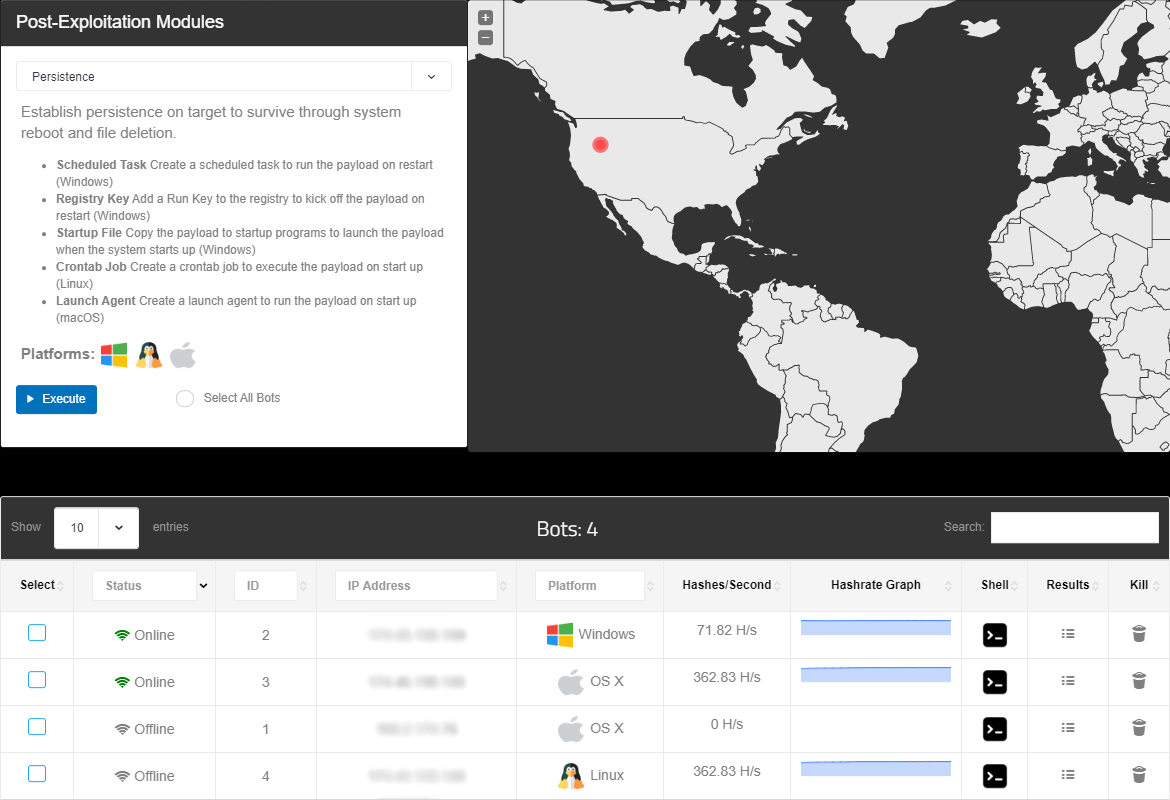 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
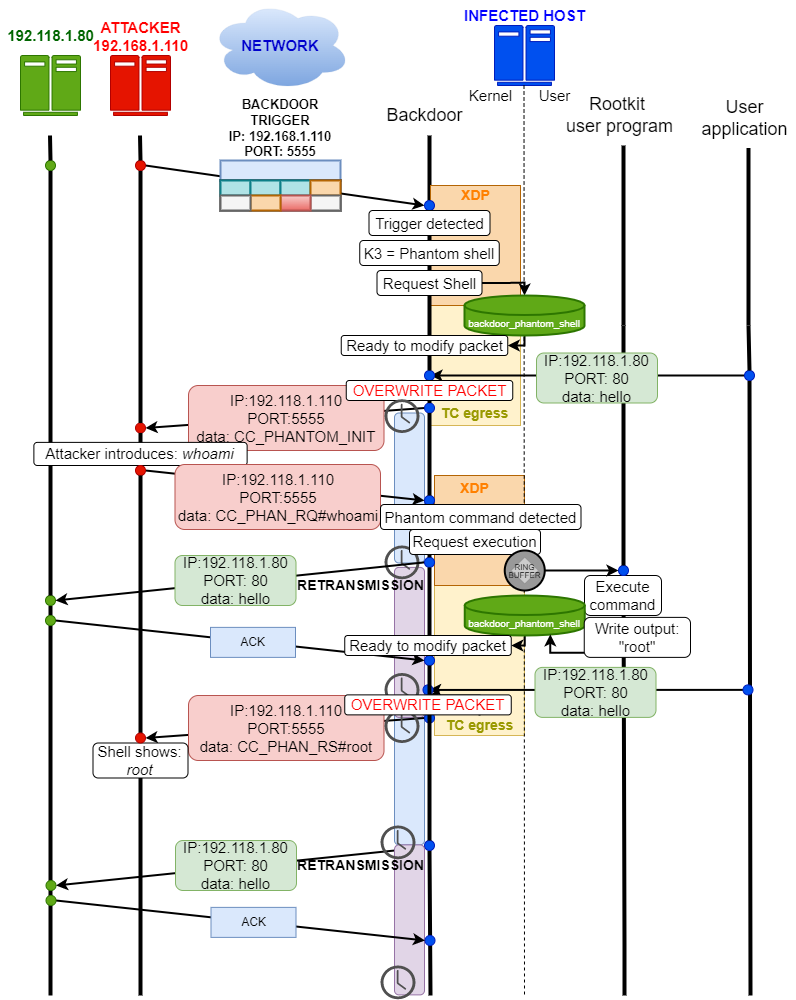 h3xduck/triplecross
A Linux eBPF rootkit with a backdoor, C2, library injection, execution hijacking, persistence and stealth capabilities.
 chokepoint/azazel
Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…