
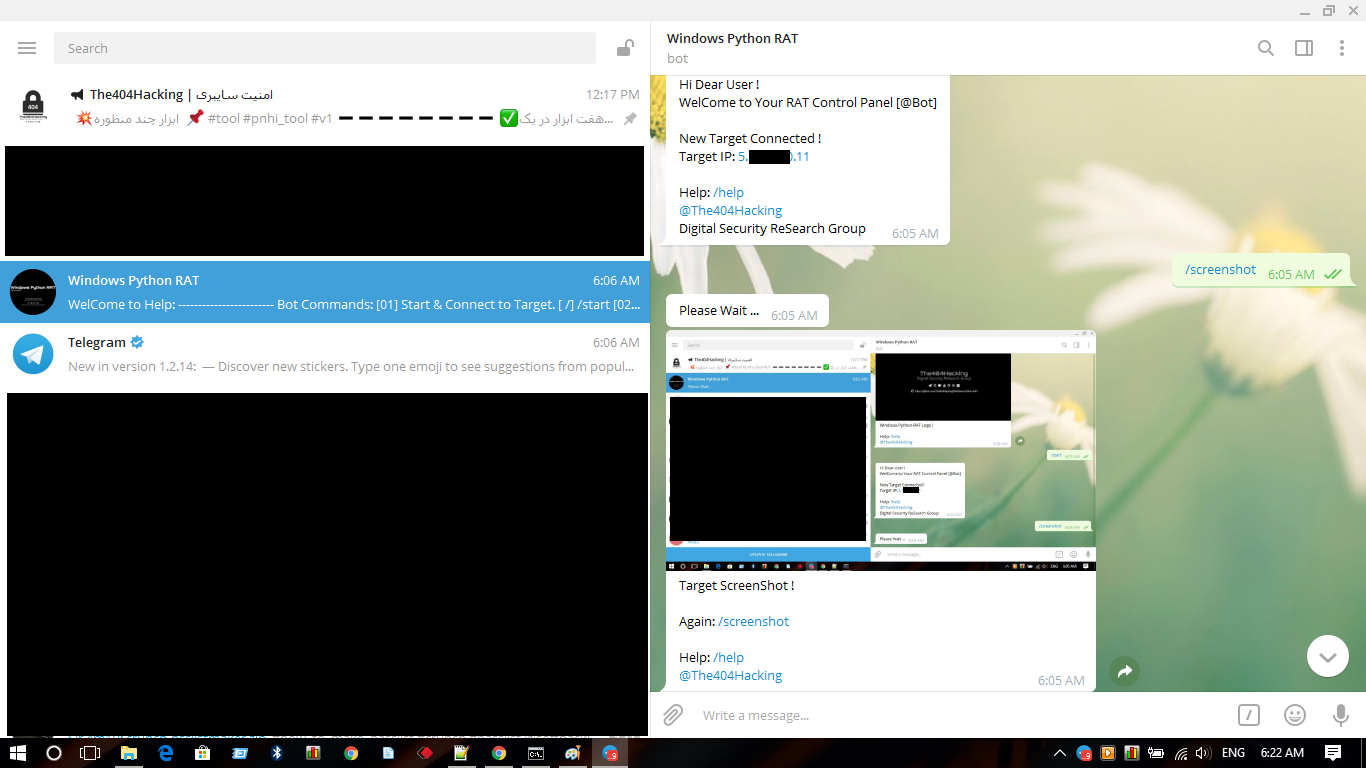
Windows-Python-RAT
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
api-securitycommand-and-controlpayload-development+3
118
the404hacking/windows-python-ratA New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 praetorian-inc/swarmer
A tool to convert windows registry export files into windows hive files that can be used to replace NTUSER.MAN
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
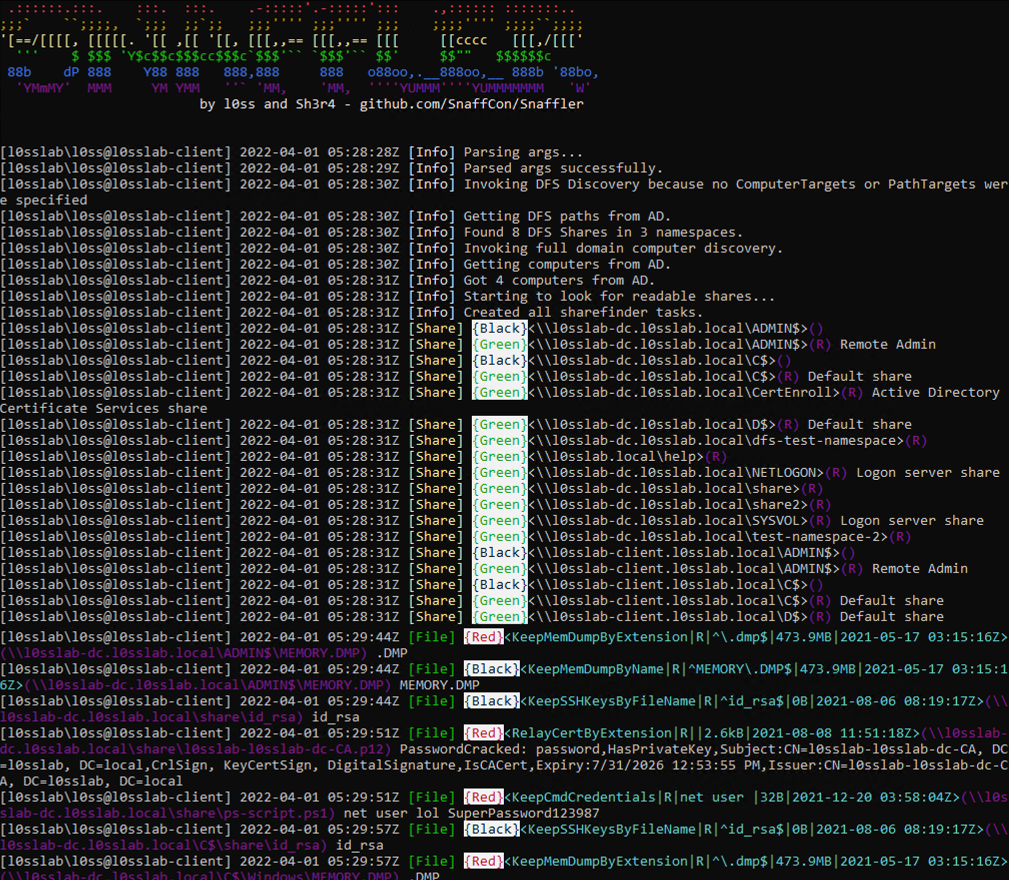 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
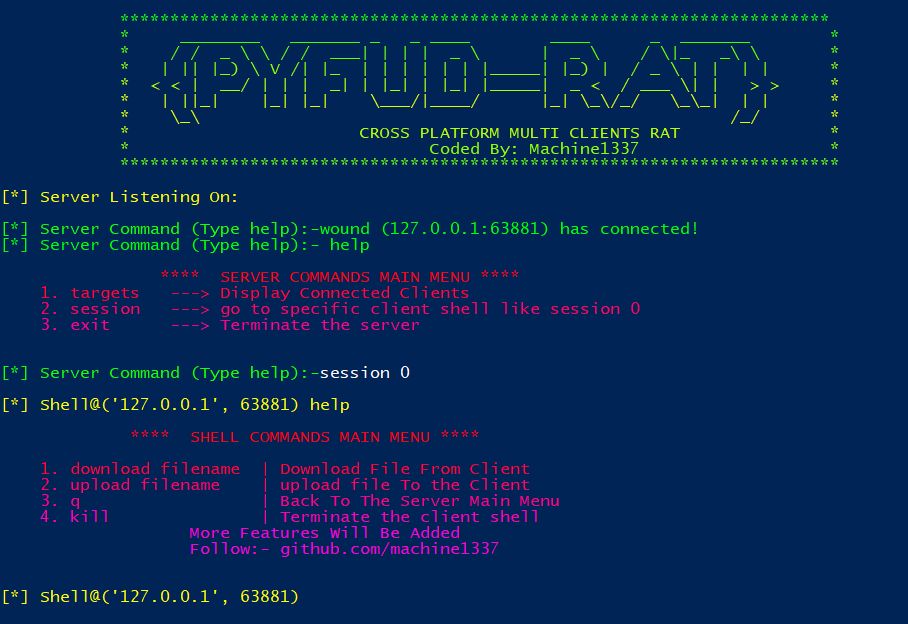 machine1337/pyfud
CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)
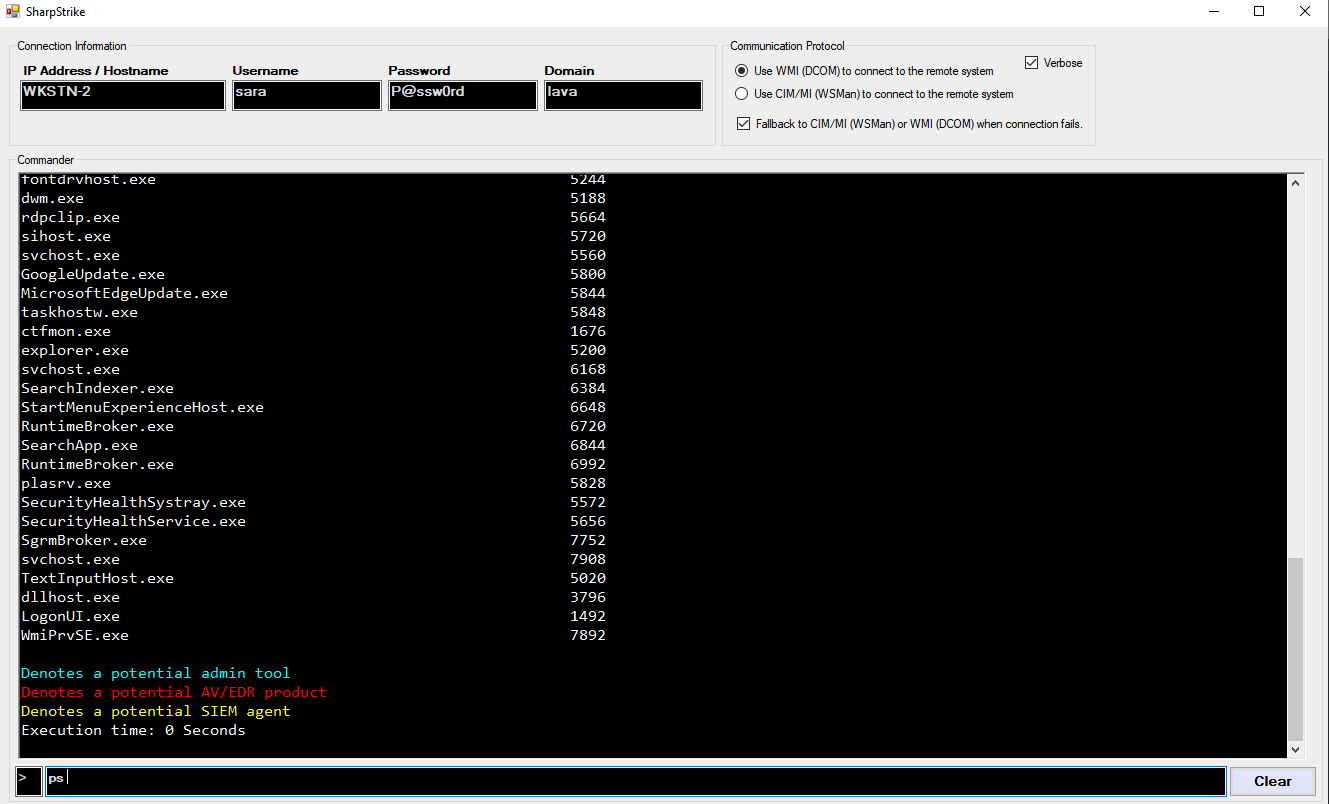 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 nccgroup/kubetcd
Post-exploit a compromised etcd, gain persistence and remote shell to nodes.
 bishopfox/sliver
Adversary Emulation Framework
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
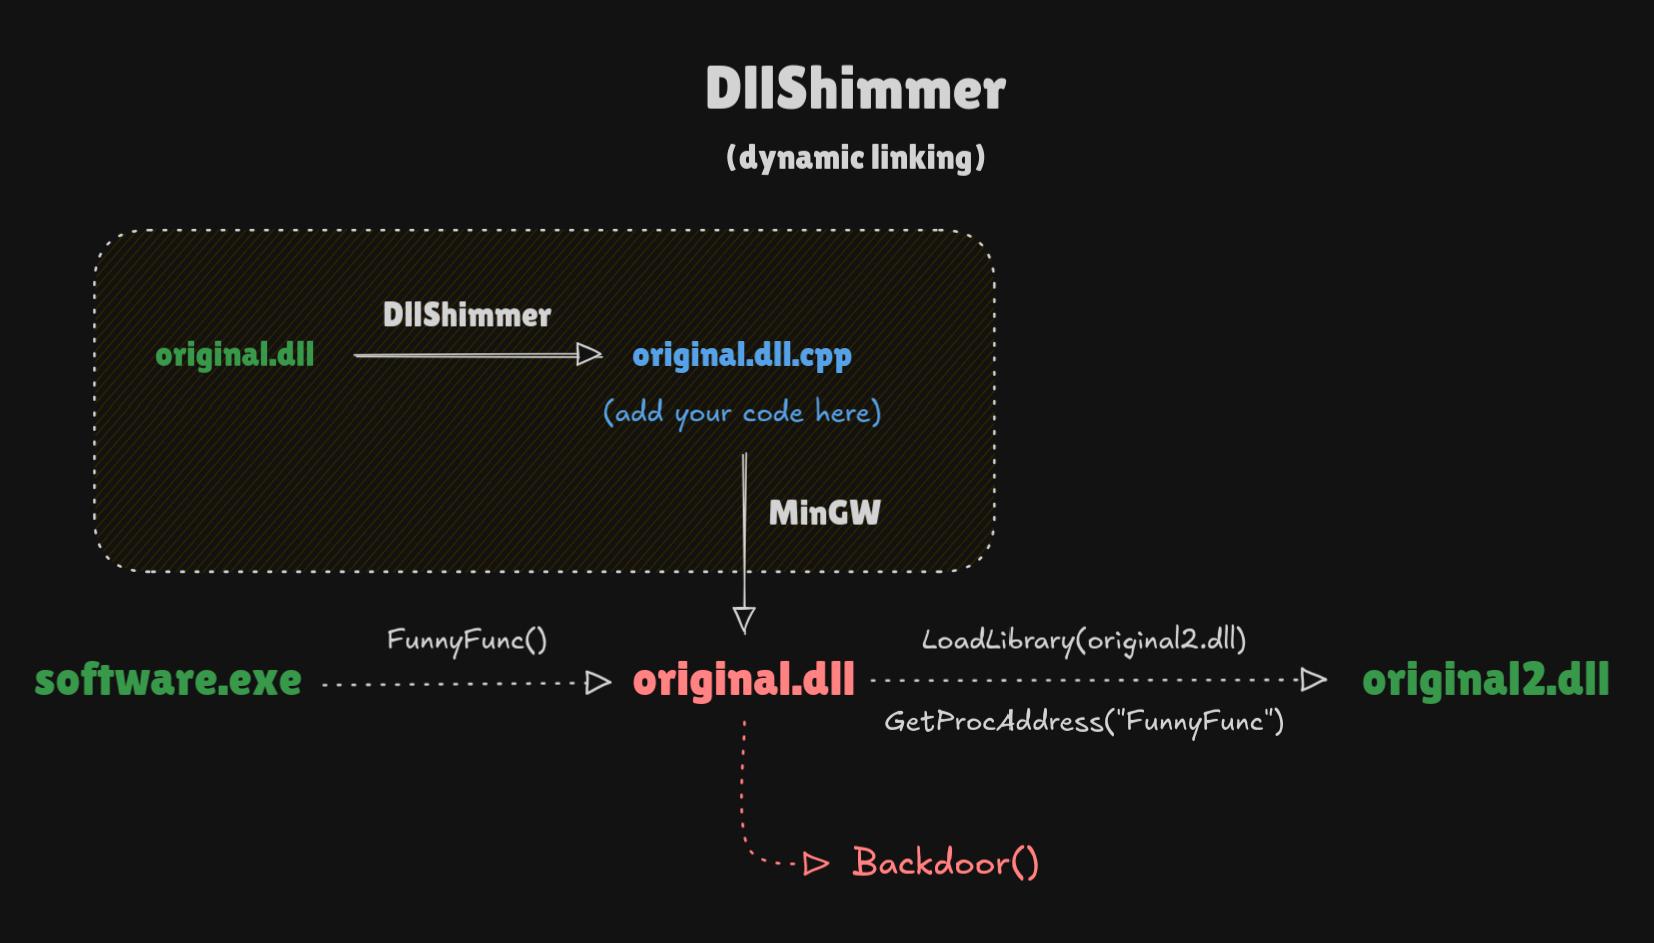 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
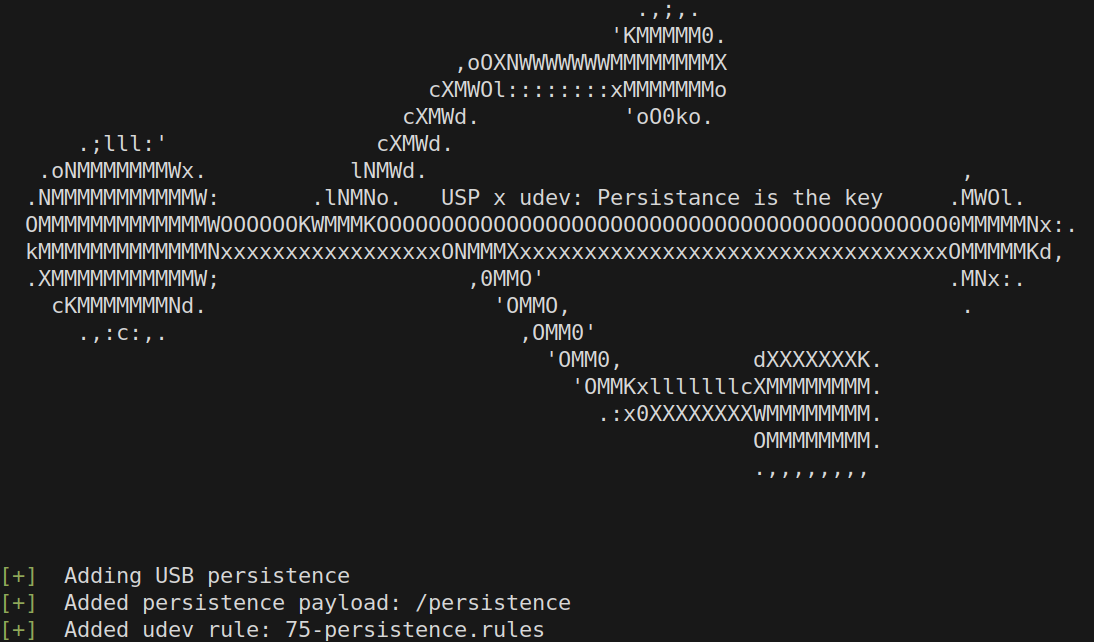 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)