mimikatz-missing-manual

Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…

Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…

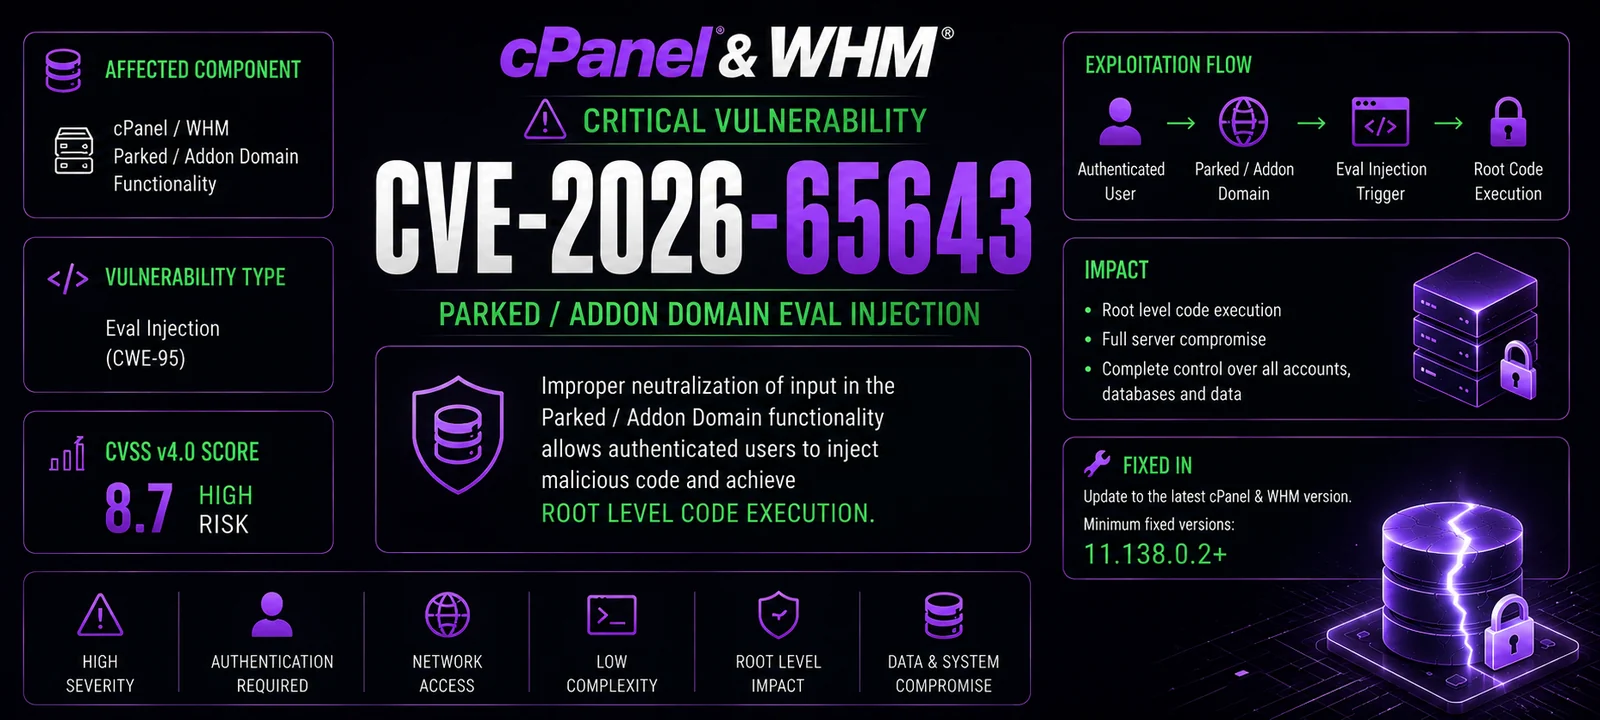
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

LSTAR - CobaltStrike Translated to EN

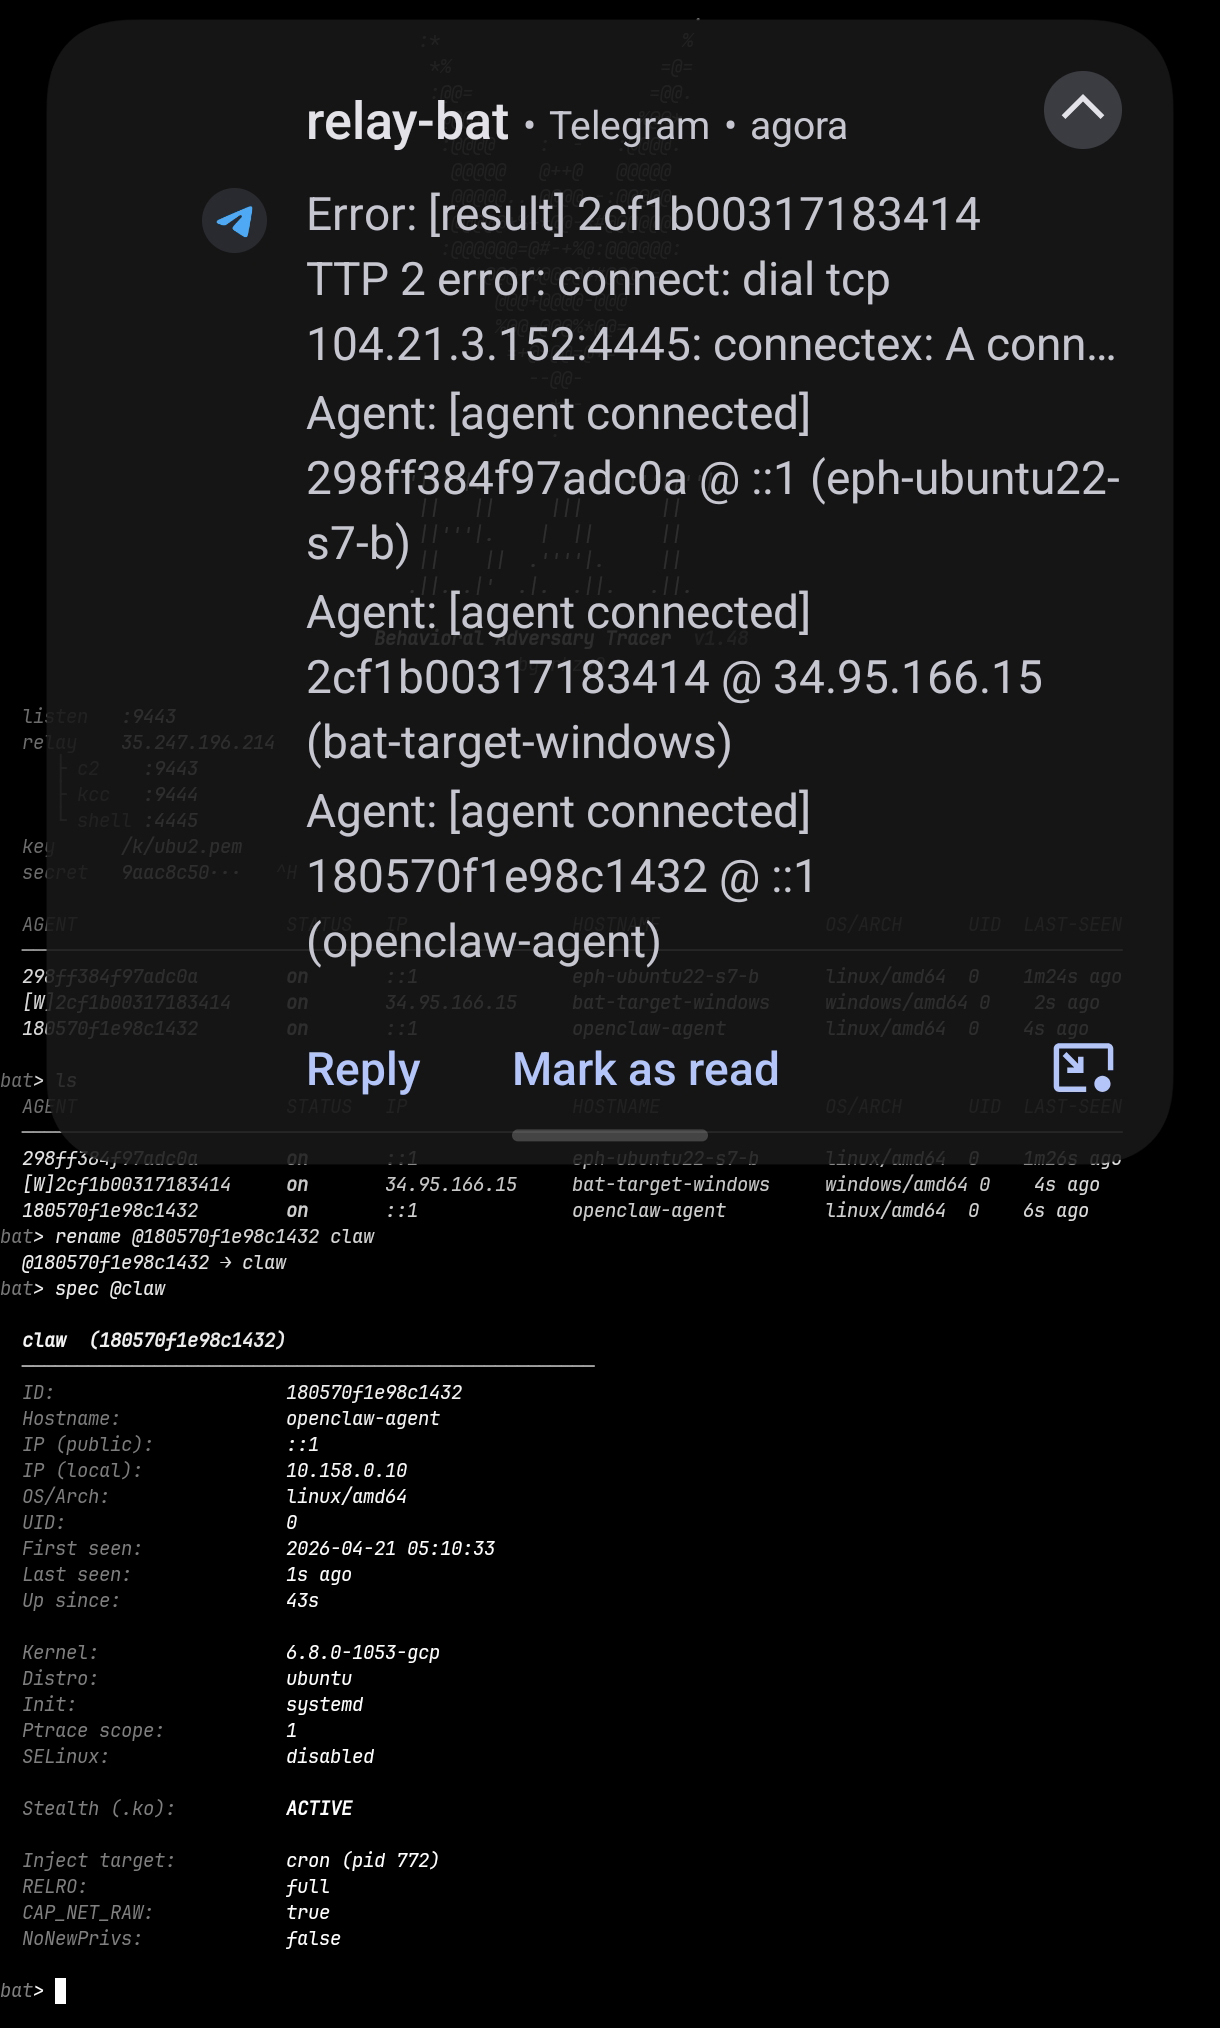
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

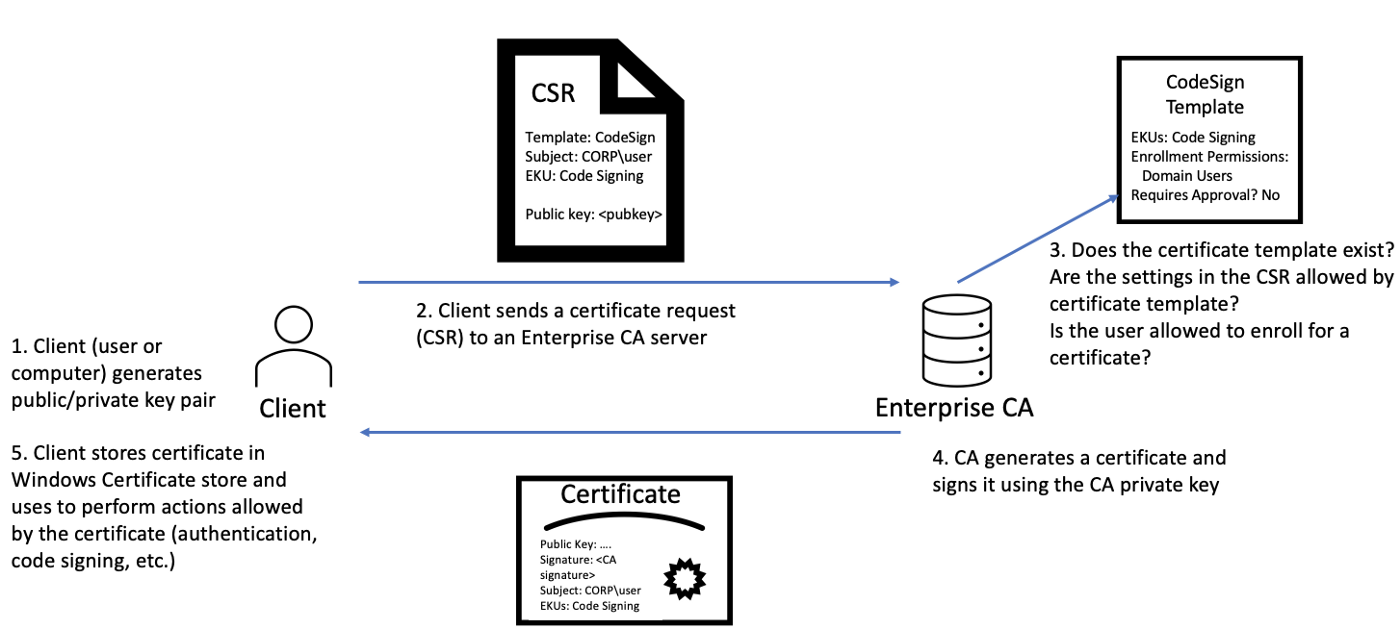
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…

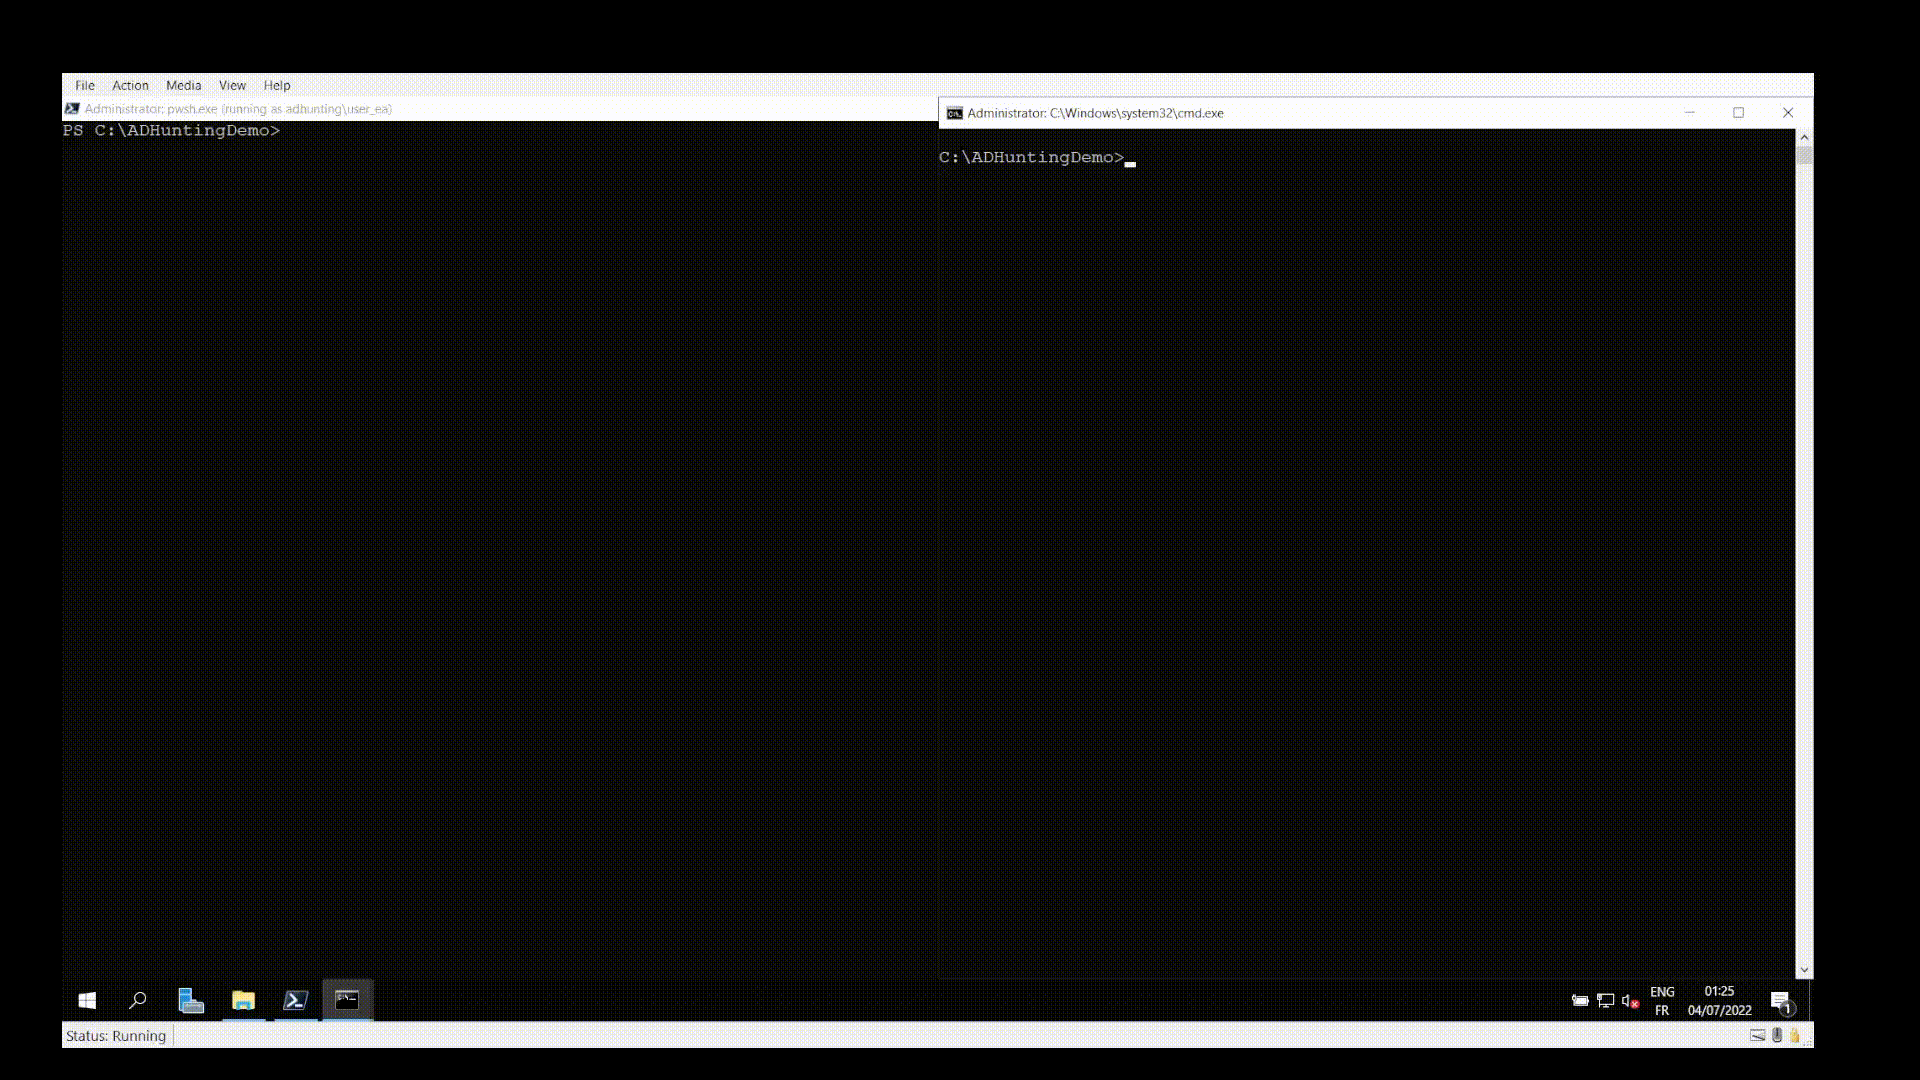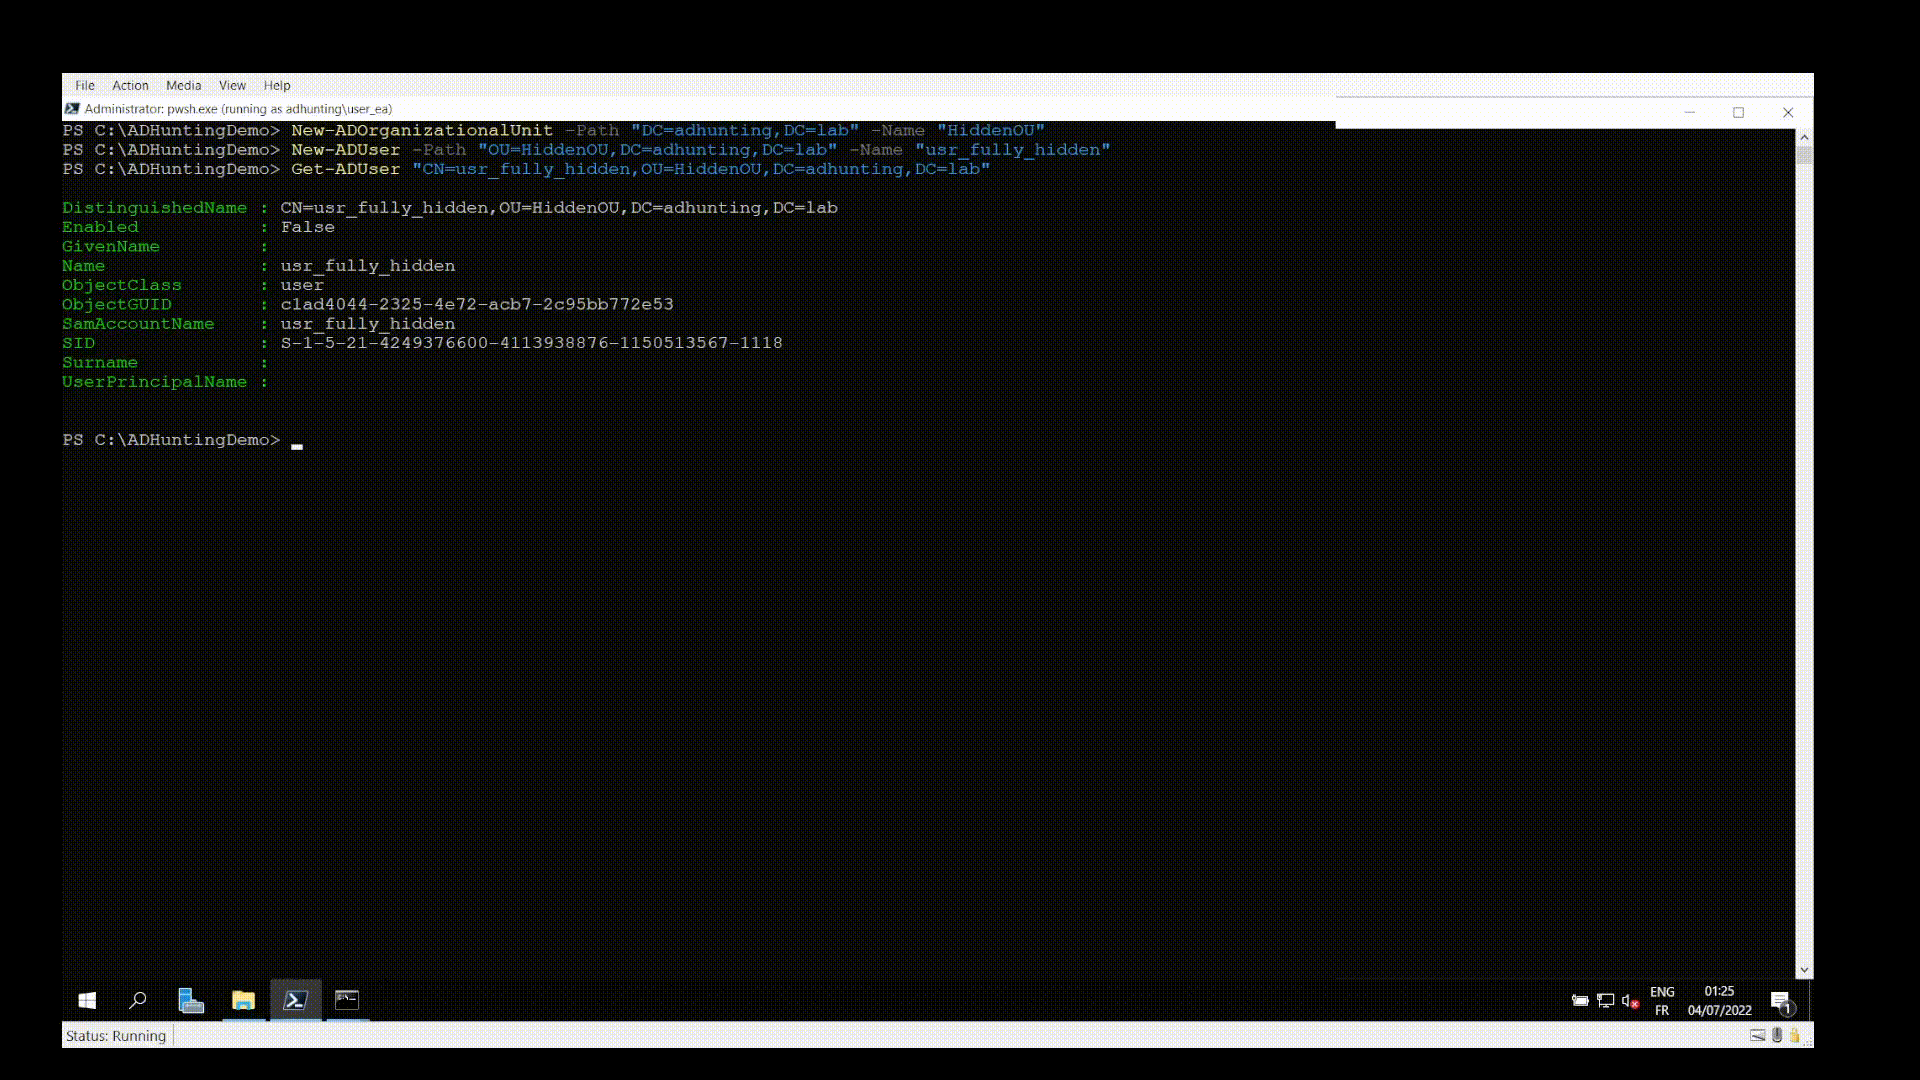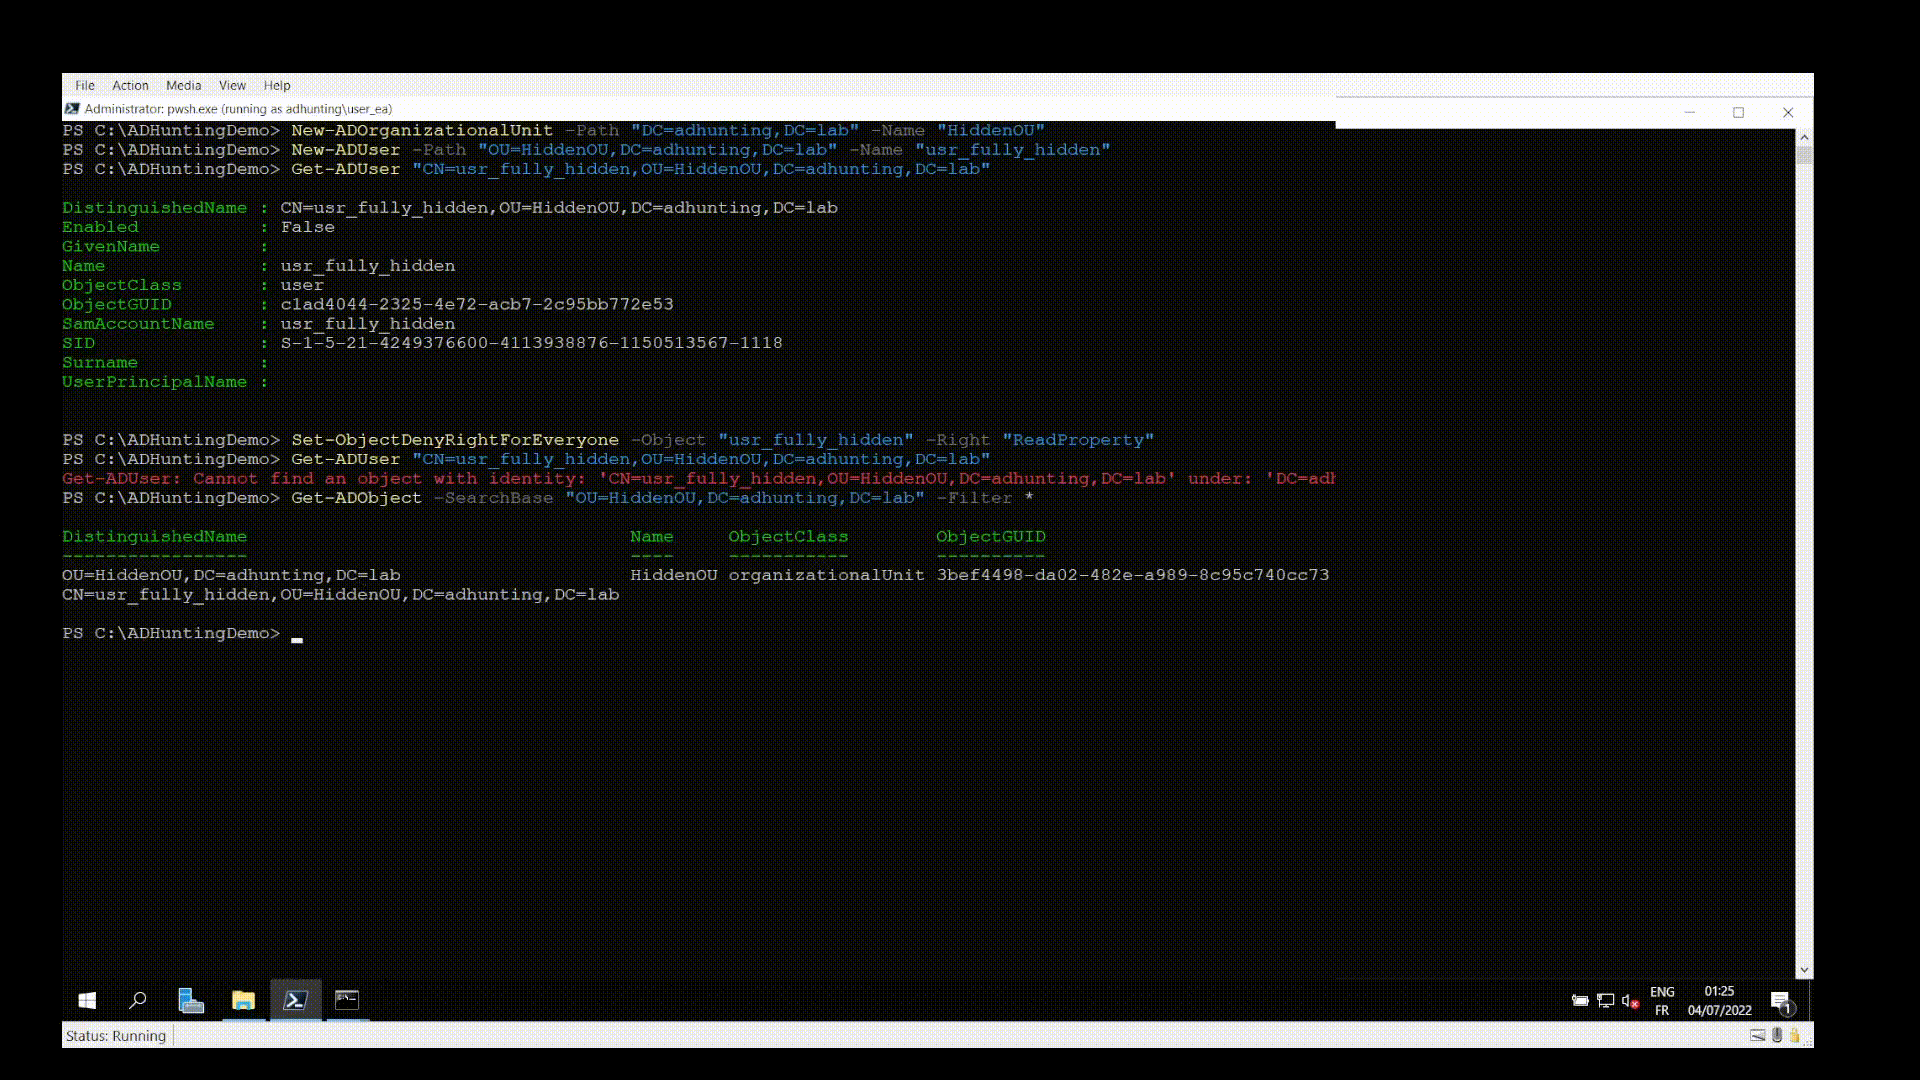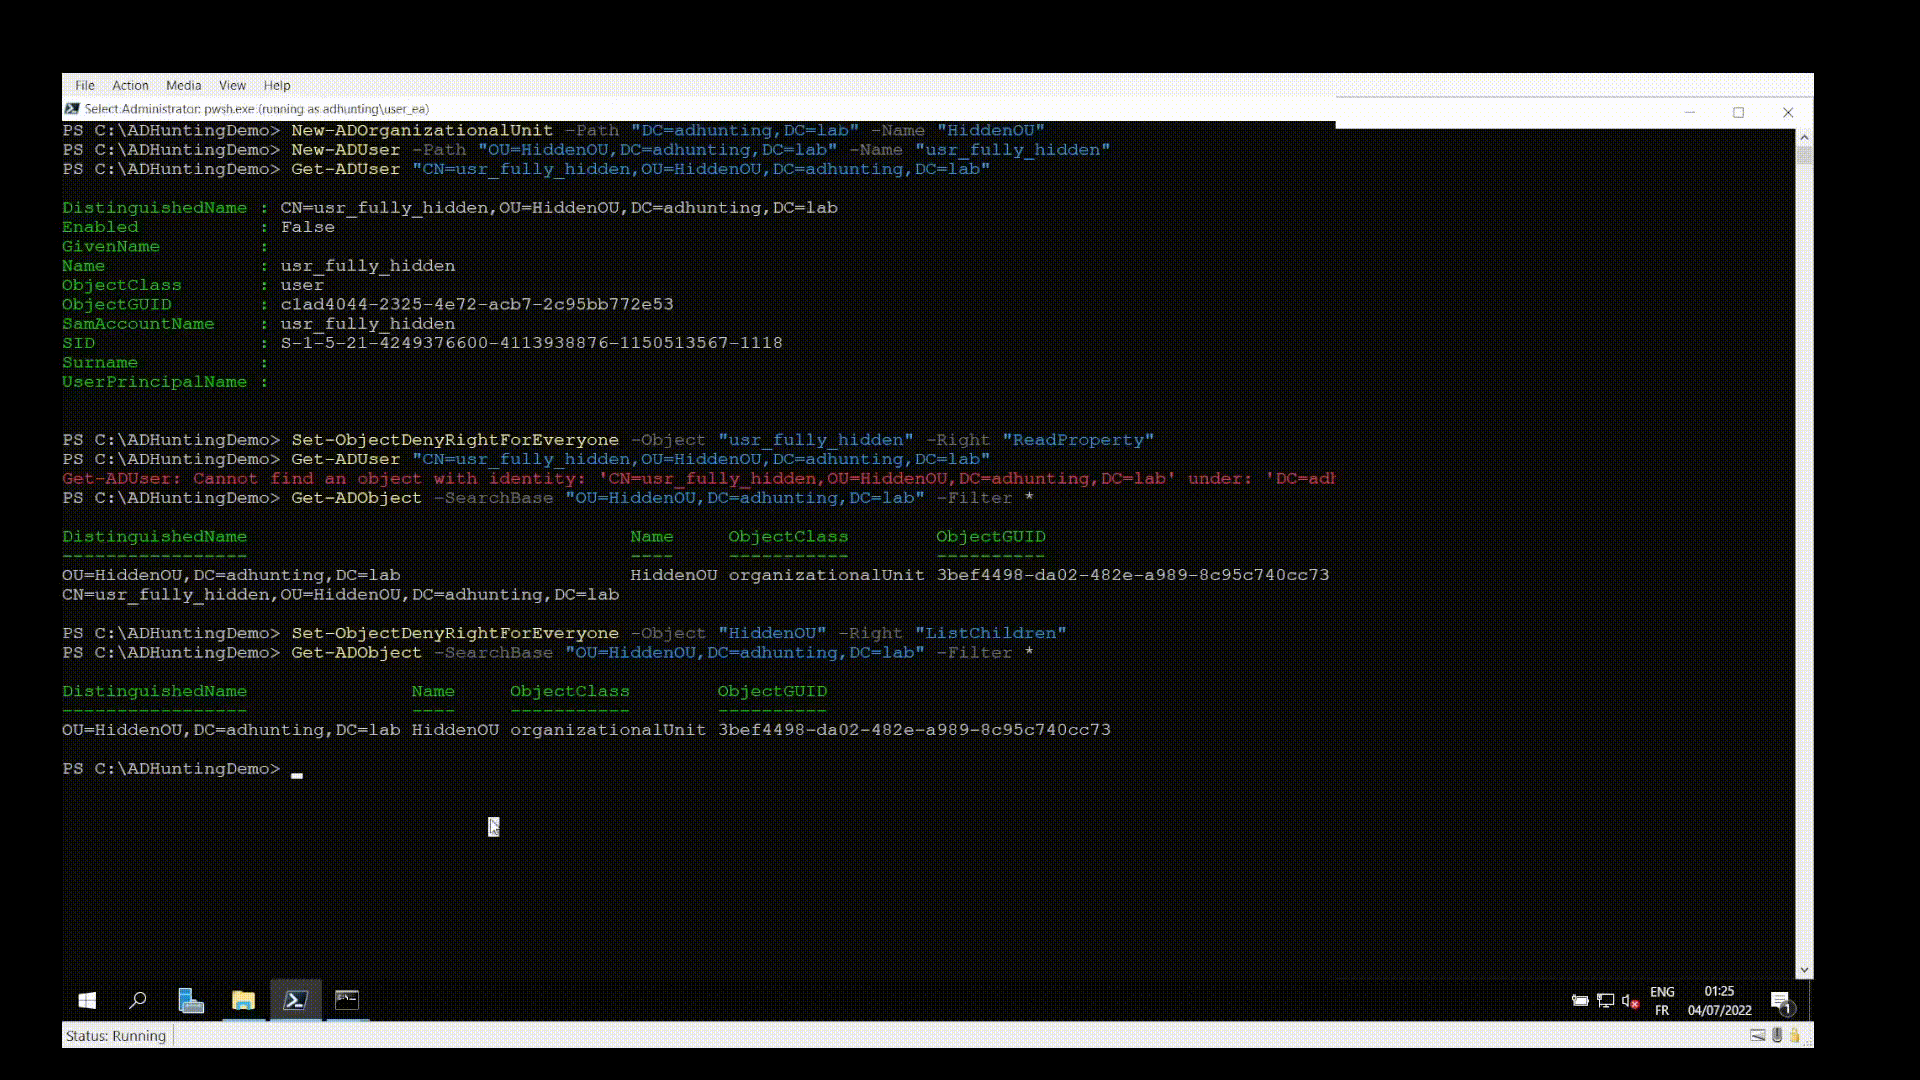
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Attack and defend active directory using modern post exploitation adversary tradecraft activity

Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…

Trying to tame the three-headed dog.

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.

Various Cobalt Strike BOFs

Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

DLL Password Filter Implant with Exfiltration Capabilities

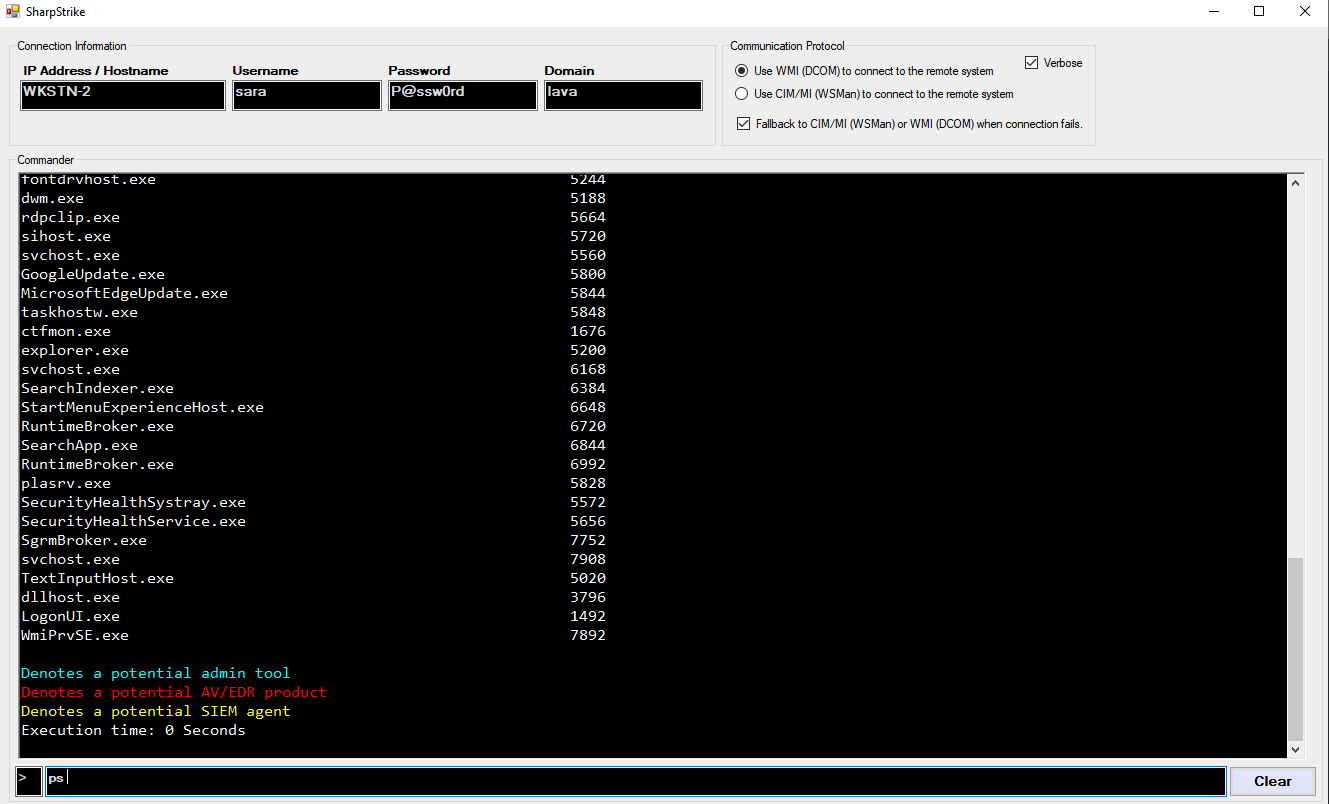
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.