
CDK
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
cloud-securitycontainer-escapecontainer-security+7
cdk-team/cdk📦 Make security testing of K8s, Docker, and Containerd easier.
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 ash1996x/cve-2025-54914-poc
Exploit for CVE-2025-54914 in Azure Networking, creating malicious routes with evasion, persistence, multi-target scanning, and reporting for…
 fazaroot/cve-2025-2539---file-away-wordpress-plugin-arbitrary-file-read
Authenticated arbitrary file read exploit for the File Away WordPress plugin (CVE-2025-2539). Includes PoC, attack flow, detection signatures, and…
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

 bishopfox/sliver
Adversary Emulation Framework
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 kill1234545/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
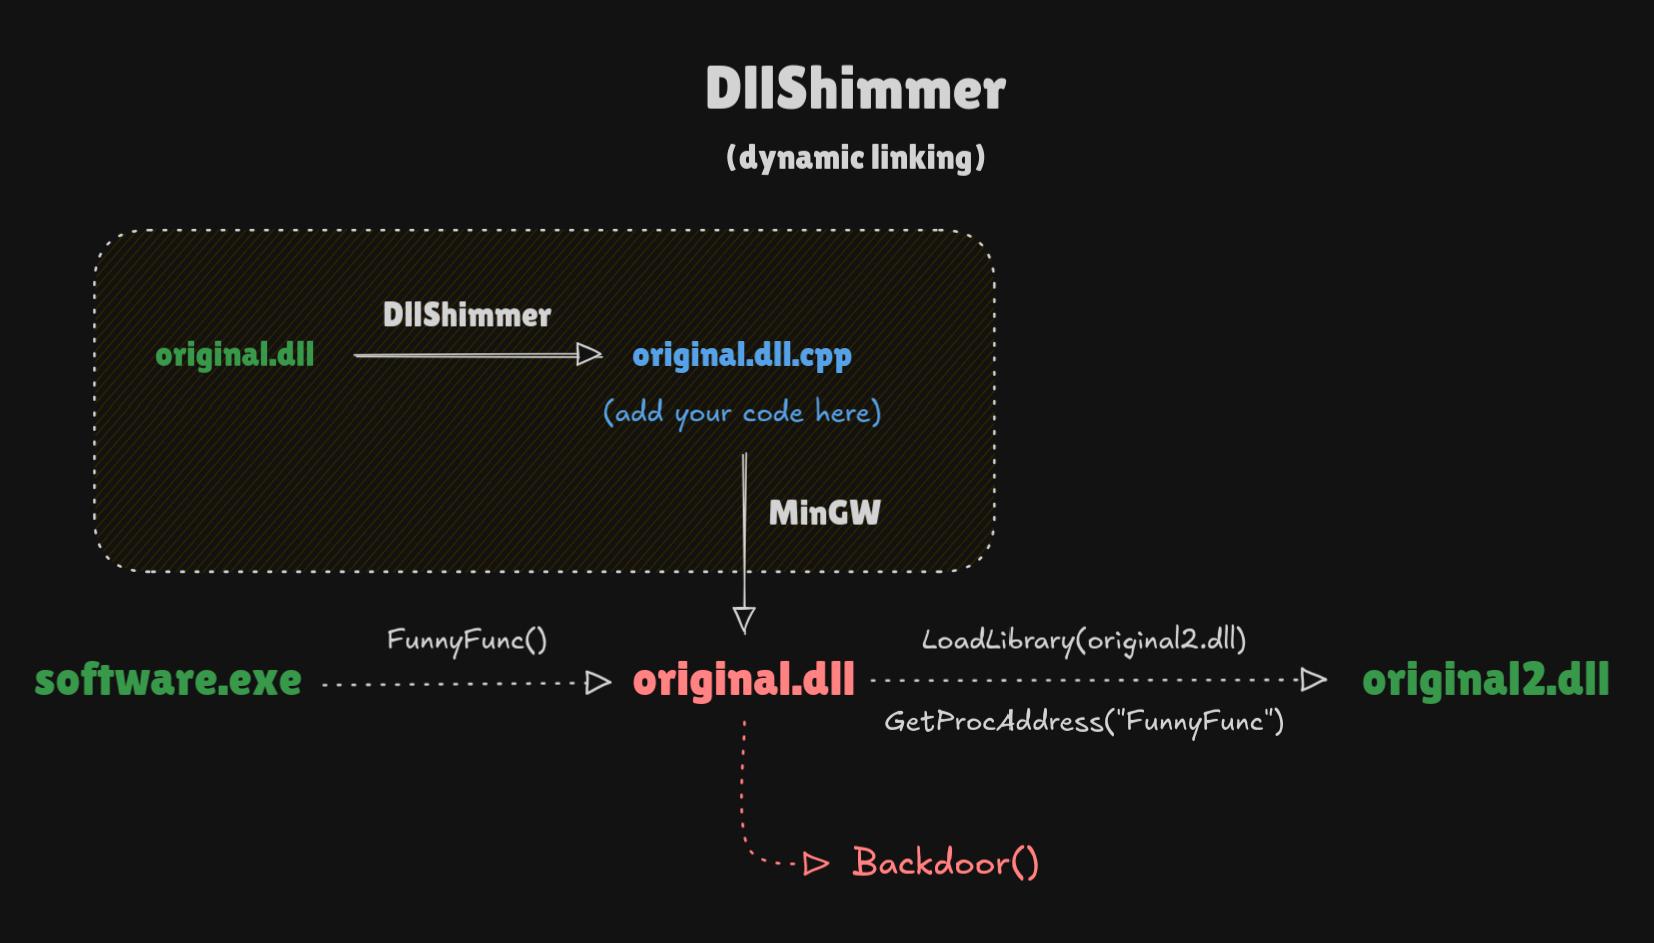 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…