
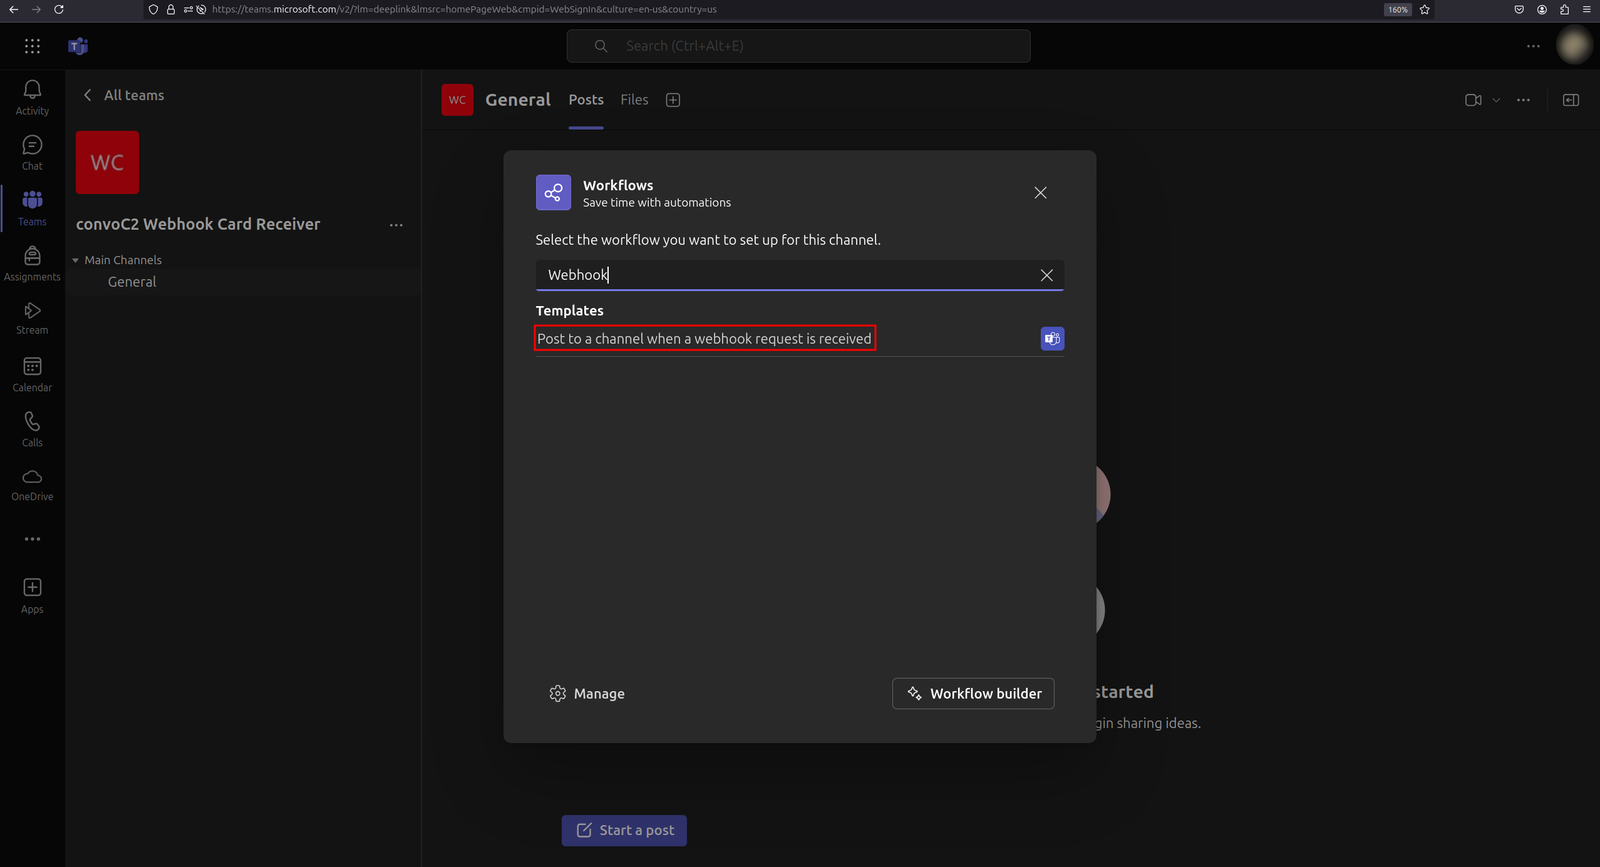
convoC2
 cxnturi0n/convoc2
C2 infrastructure over Microsoft Teams.
command-and-controldata-exfiltrationids-ips-evasion+6
cxnturi0n/convoc2C2 infrastructure over Microsoft Teams.
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
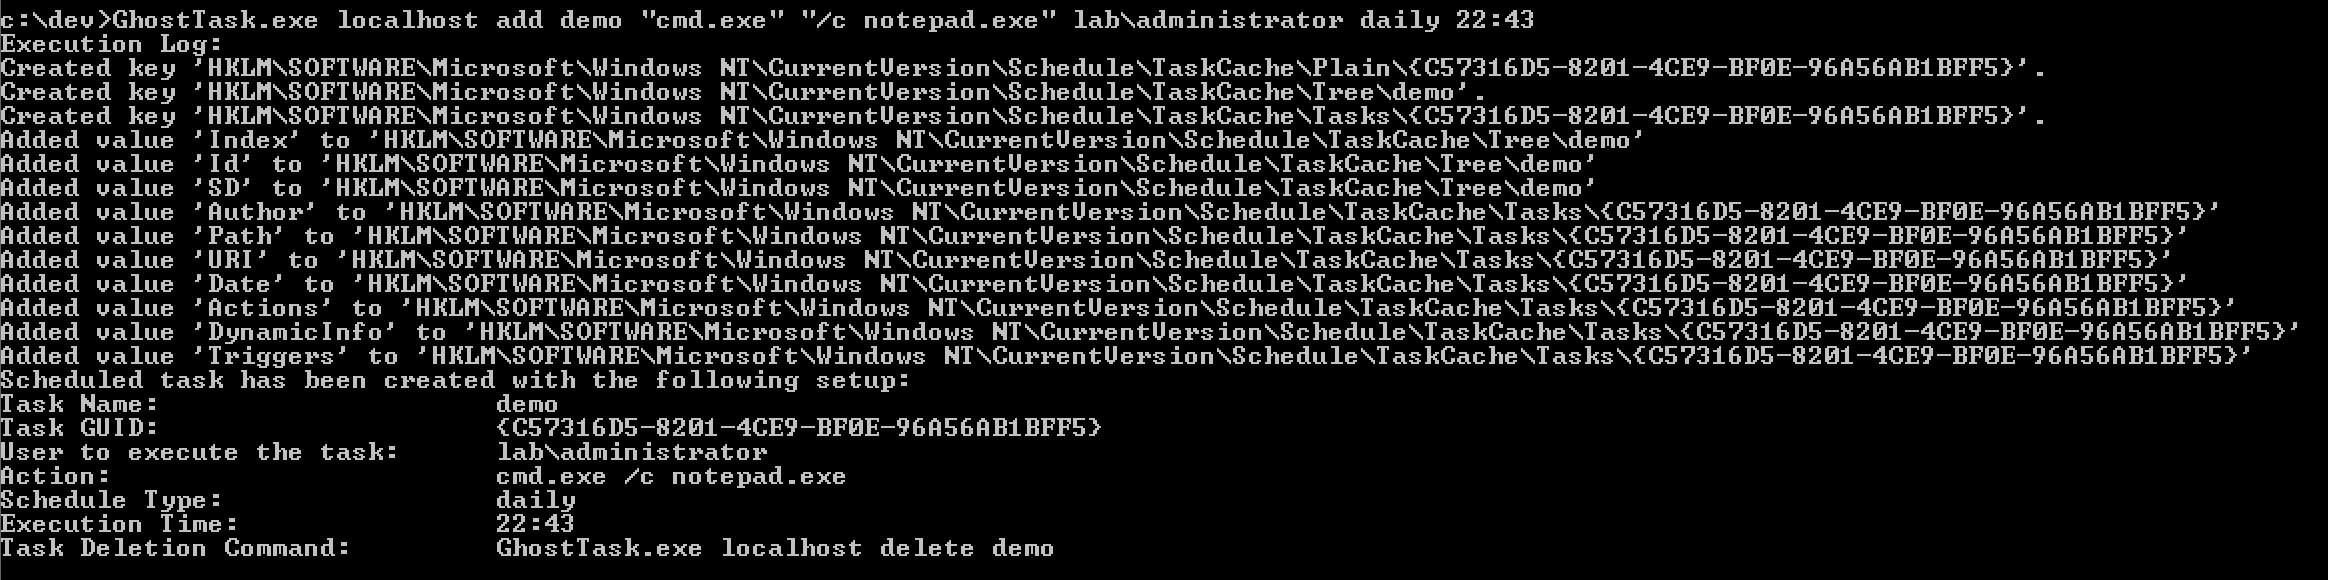 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 enzolovesbacon/inficere
Mac OS X rootkit - for learning purposes
 thesecretclub/sandboxbootkit
Bootkit for Windows Sandbox to disable DSE/PatchGuard.
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
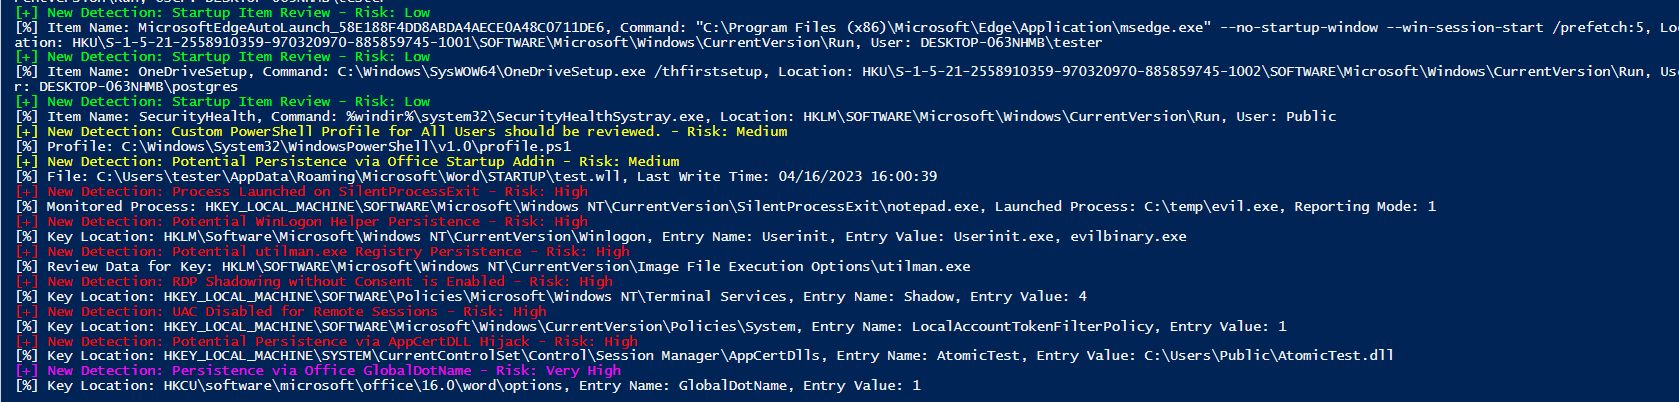 joeavanzato/trawler
PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
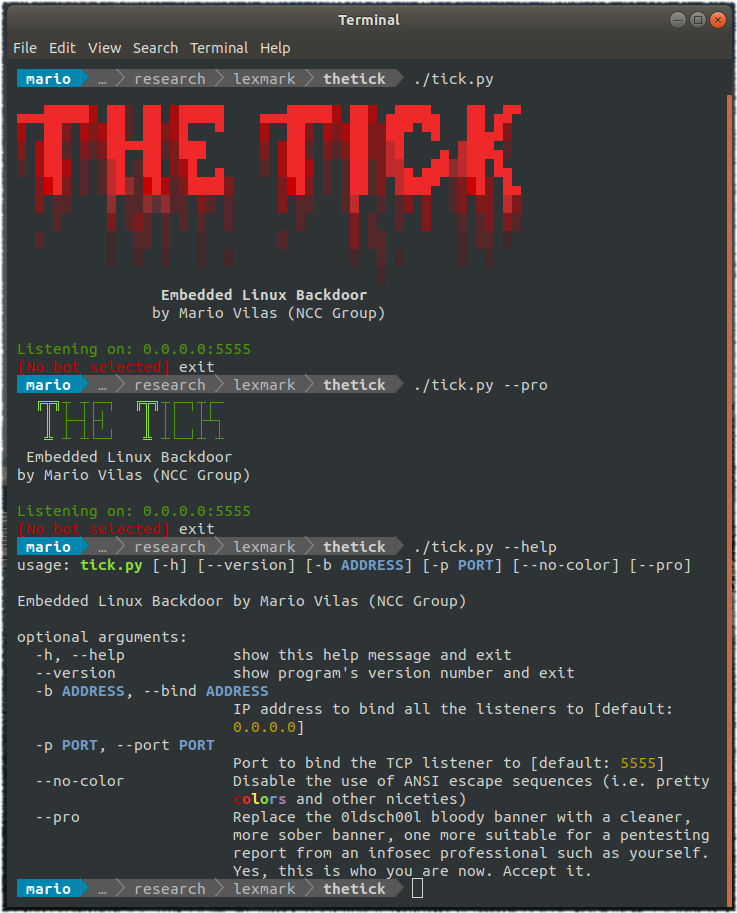 nccgroup/thetick
A simple embedded Linux backdoor.
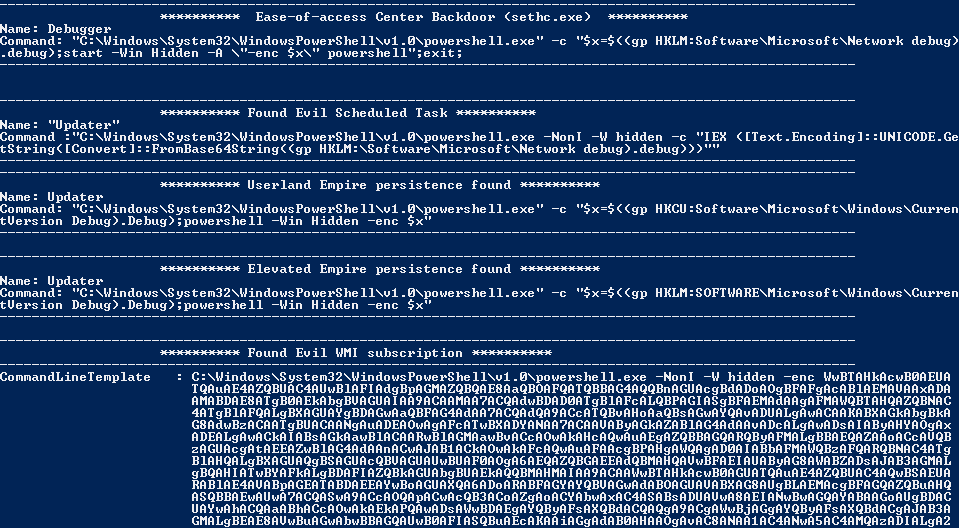 n00py/norknork
Powershell Empire Persistence finder
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 cyborgsecurity/poisonapple
CLI tool for applying and removing macOS persistence mechanisms, designed for threat emulation and red team operations. Supports 17 techniques…
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
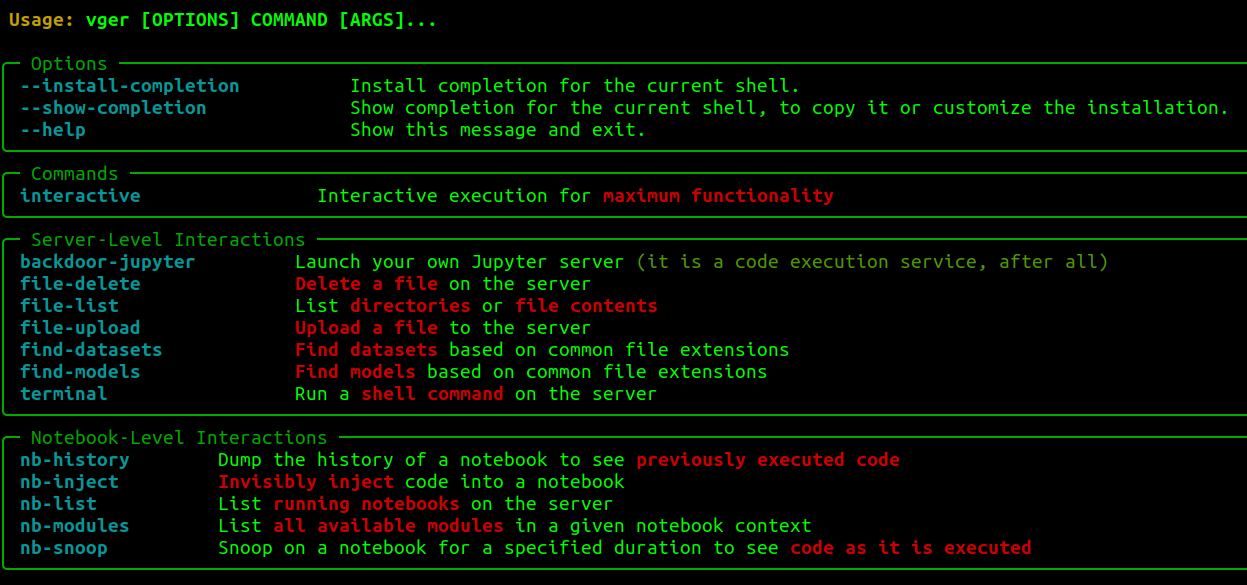 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 neofito/cve-2020-1337
CVE-2020-1048 bypass: binary planting PoC