PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

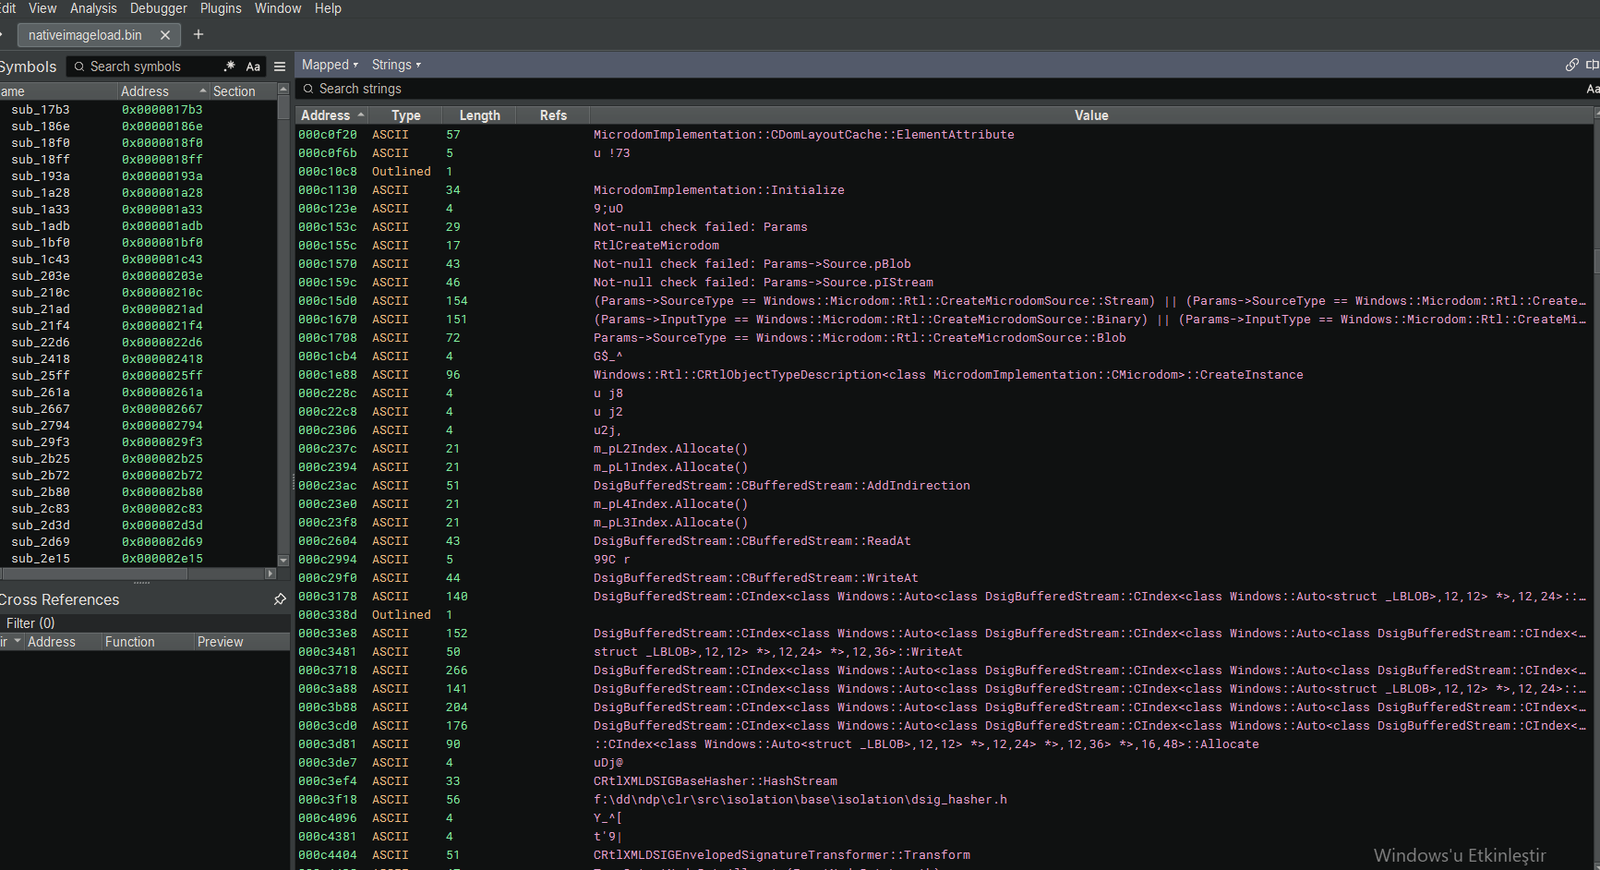
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

Tool for extracting information from newly spawned processes

HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…

Customizable Linux Persistence Tool for Security Research and Detection Engineering.

LKM rootkit for Linux Kernels 2.6.x-6.x (x86/x86_64 and ARM/64)

Linux Persistence Detection, Hunting and Artifact Collection script

Phantom Keylogger is an advanced, stealth-enabled keystroke and visual intelligence gathering system.

Experimental proof-of-concept demonstrating .bashrc manipulation using figlet to create terminal persistence and privilege-escalation vulnerabilities…

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…

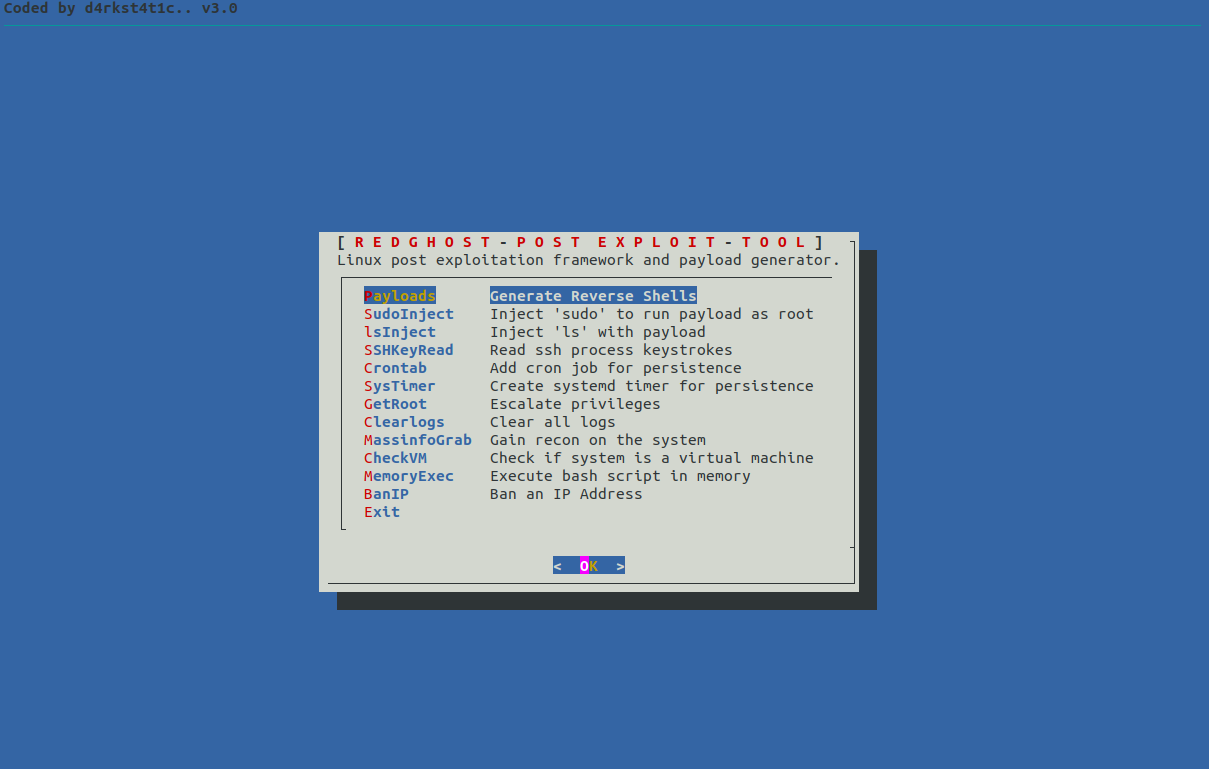
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…

GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…

This repo documents a vulnerability in Siri Shortcuts and Shared Web Credentials (SWC) allowing malformed payloads to persistently execute, trigger…

Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.

Control a system remotely via telegram

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.

This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…

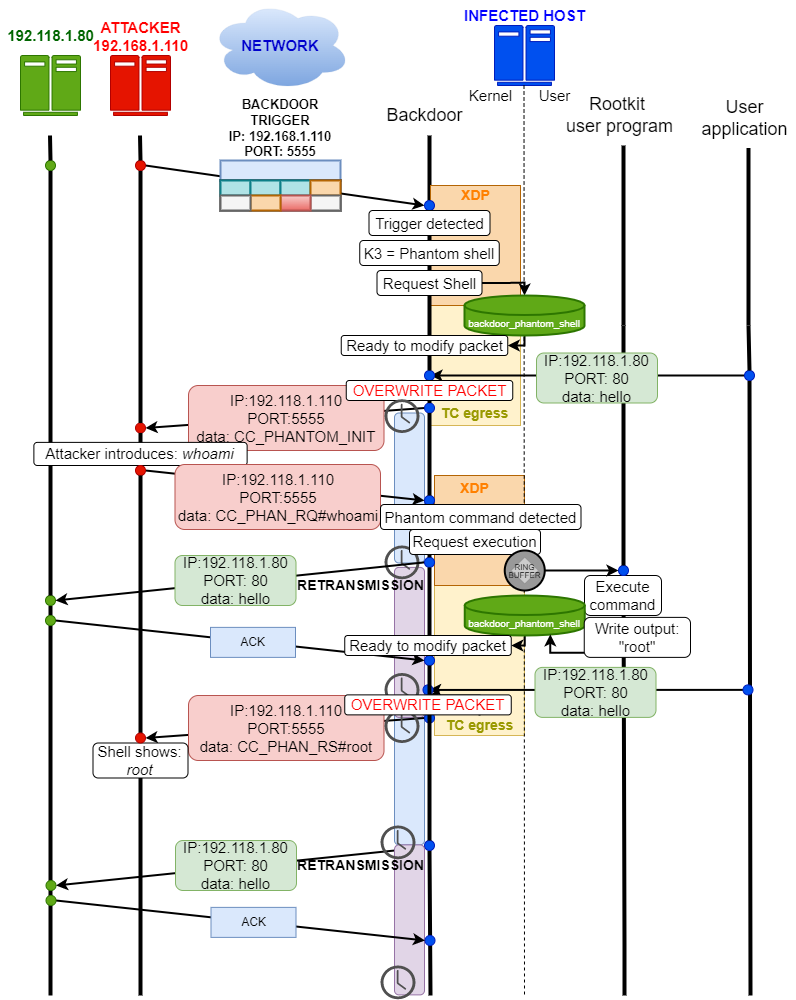
A Linux eBPF rootkit with a backdoor, C2, library injection, execution hijacking, persistence and stealth capabilities.