
PurpleSharp
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
adversarial-attackeducationlateral-movement+4
mvelazc0/purplesharpPurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 treehacks/botnet-hackpack
Build a basic Command & Control botnet in C
 daem0nc0re/vectorkernel
PoCs for Kernelmode rootkit techniques research.
 darkoperator/mimikatz-missing-manual
Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
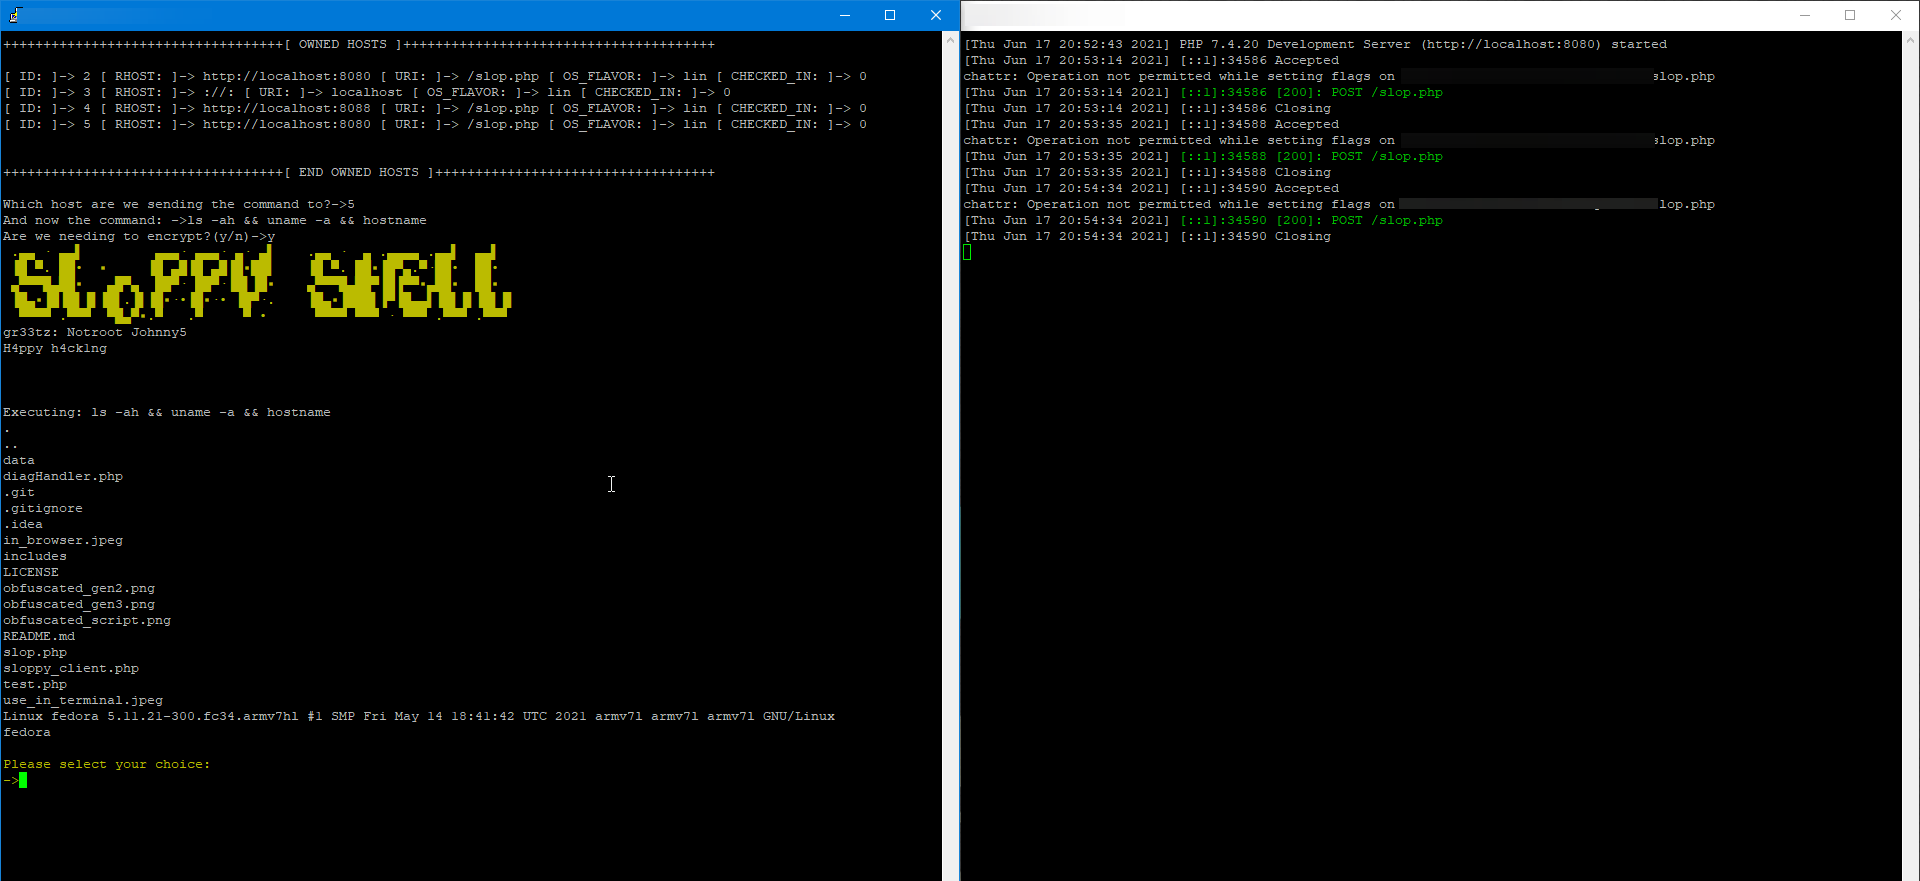 oldkingcone/slopshell
the only php webshell you need.
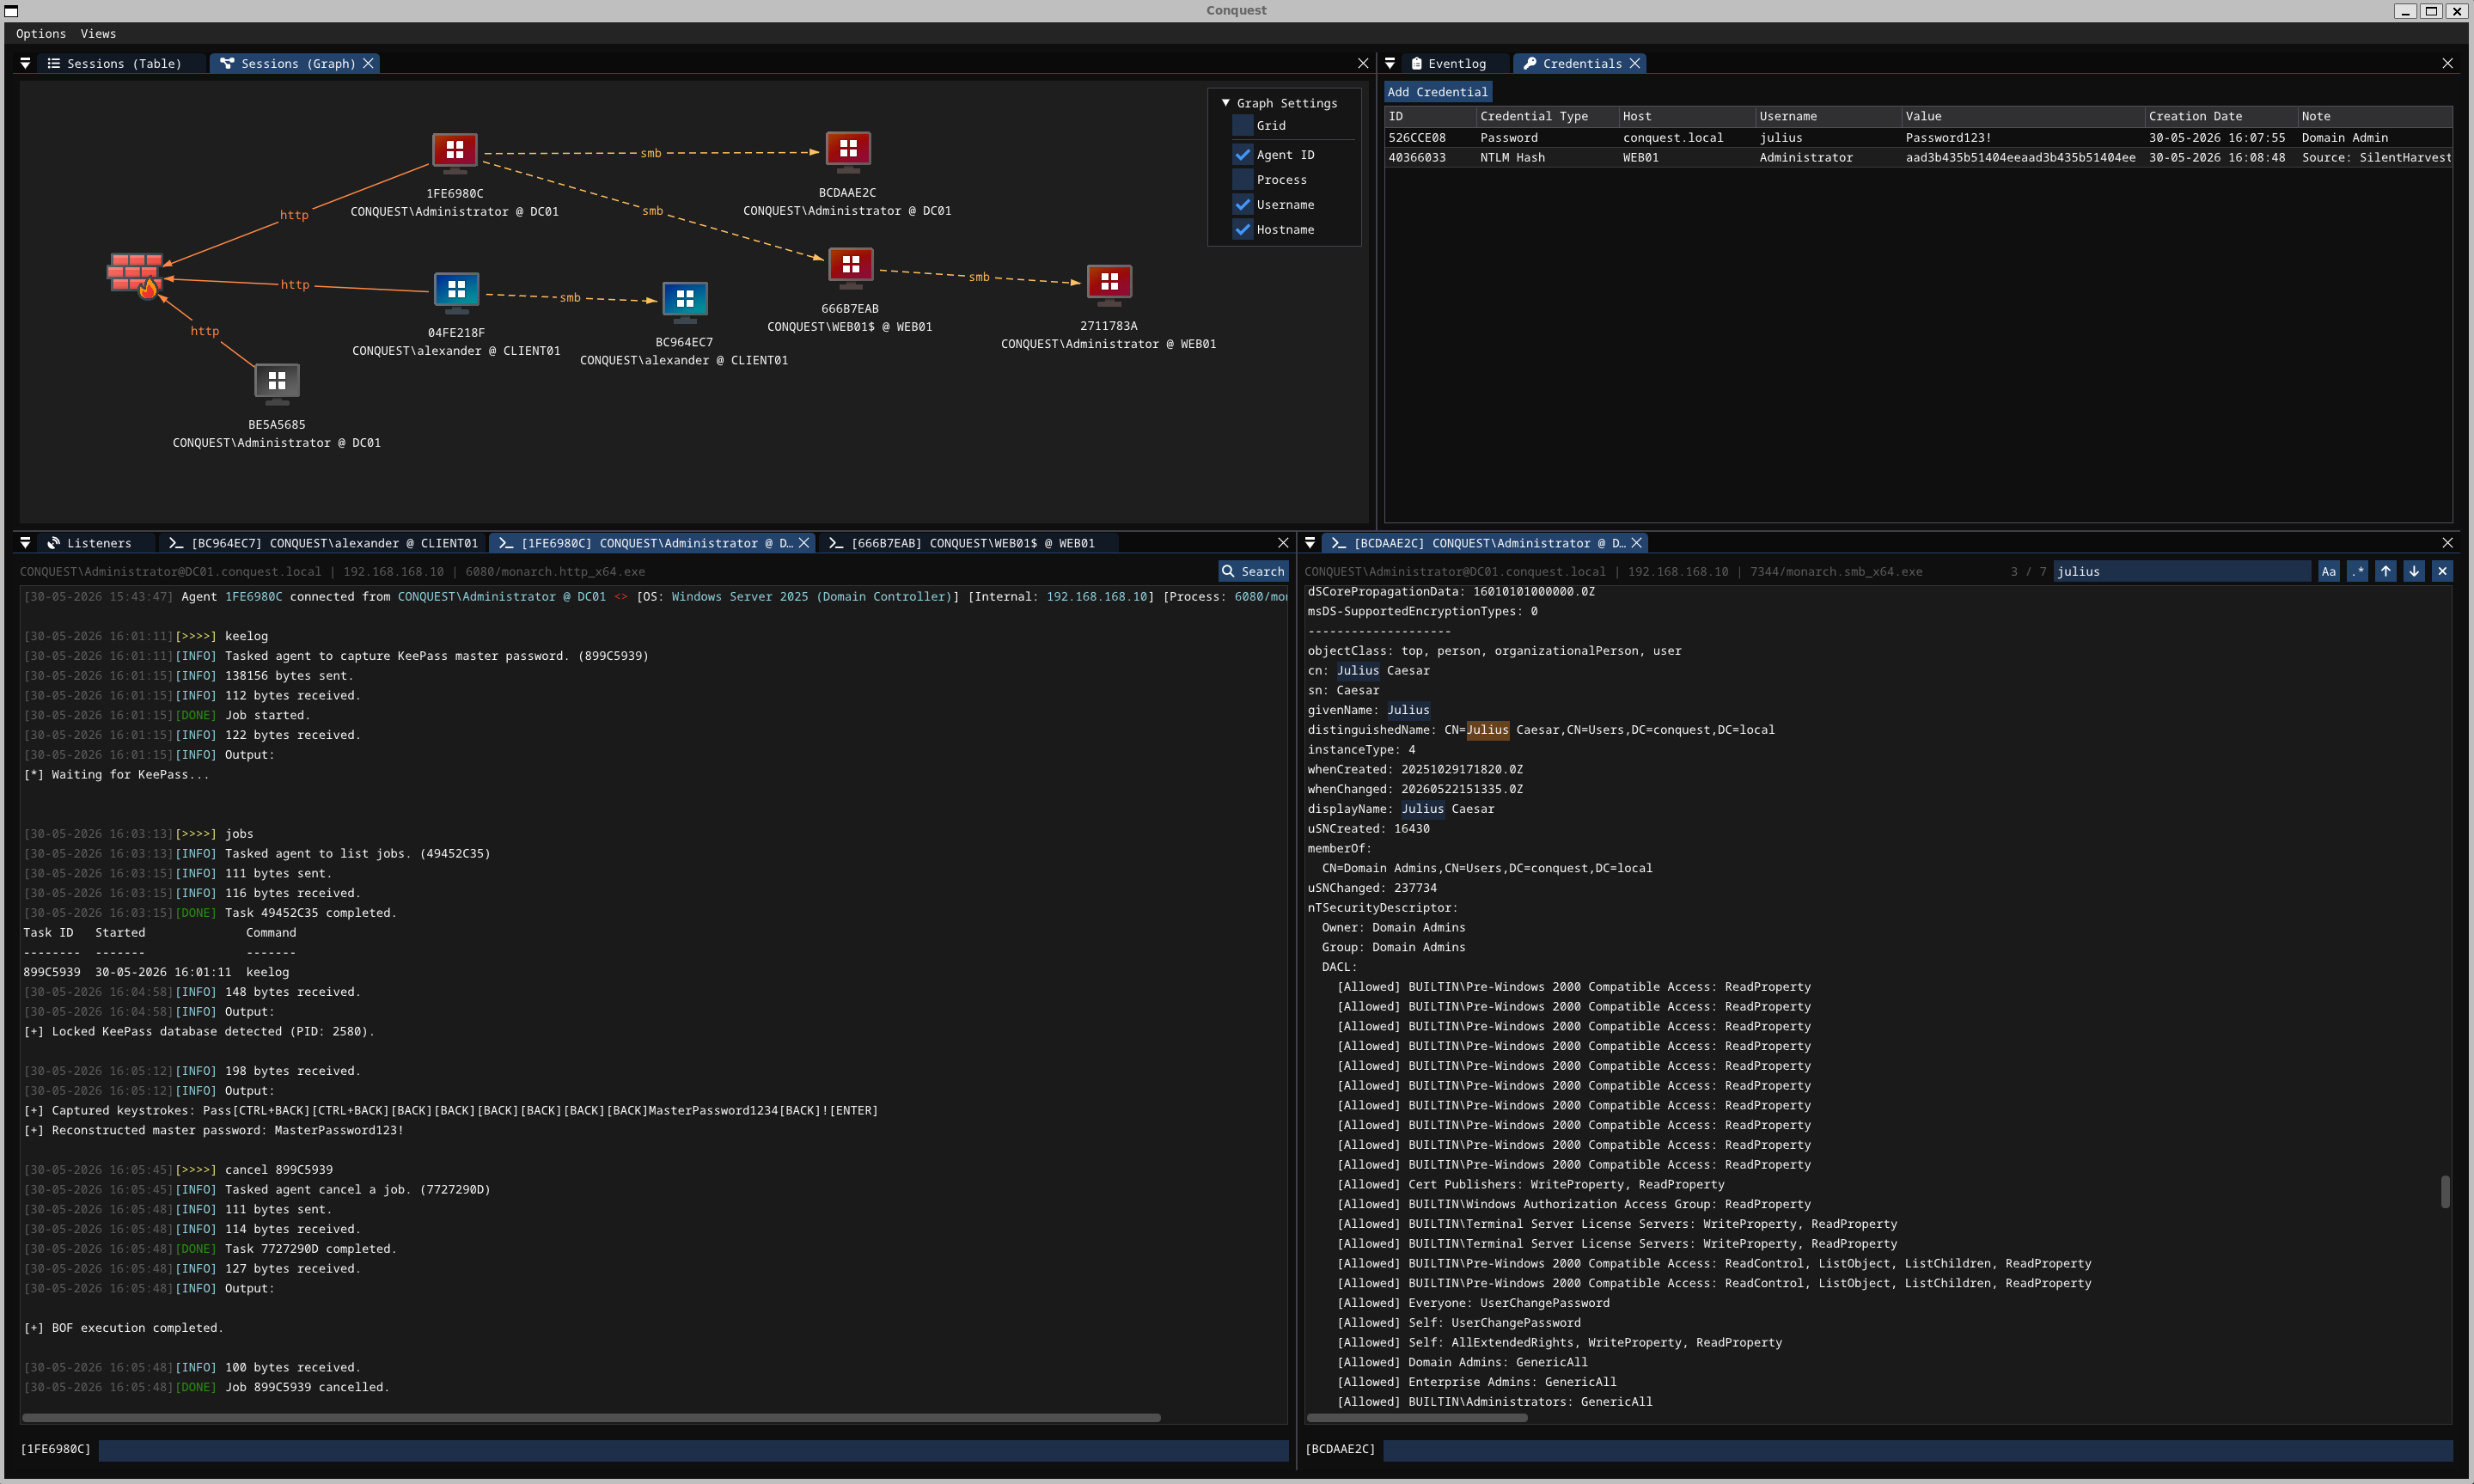 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
 enzolovesbacon/inficere
Mac OS X rootkit - for learning purposes
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
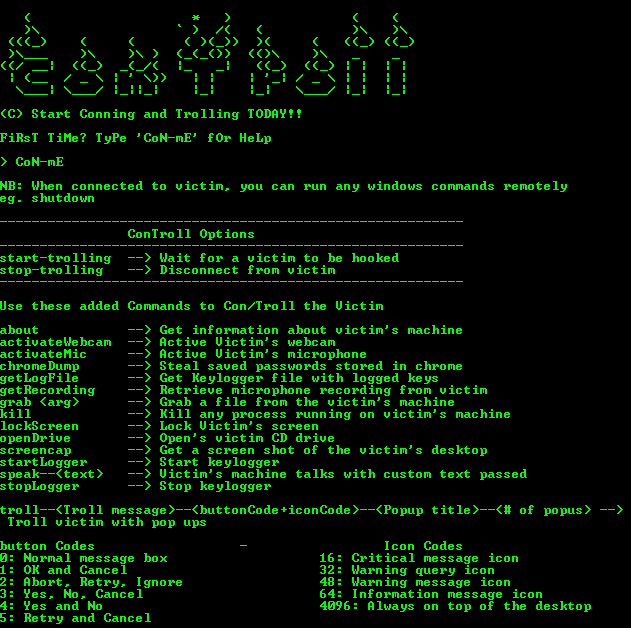 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 xcellerator/freebsd_kernel_hacking
Learning FreeBSD Kernel Hacking - Exercises
 i014n/righthand-persistence
COM Windows Persistence Technique
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 yo-yo-yo-jbo/macos_sandbox
Blog post exploring macOS App Sandbox, entitlements via codesign, and sandbox escape techniques using launchd, LaunchAgents, and quarantine…