honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.

EGESPLOIT is a golang library for malware development

Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…

PowerSploit - A PowerShell Post-Exploitation Framework

DNS covert channel implant for Red Teams.

👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]

HERCULES is a special payload generator that can bypass antivirus softwares.

A simple python reverse shell written just for fun.

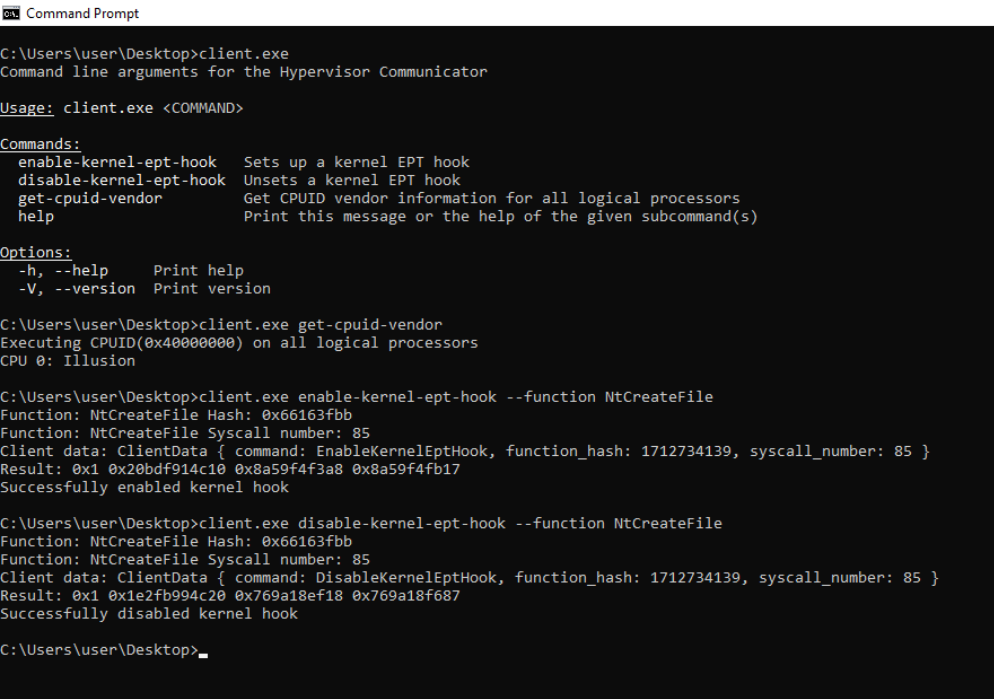
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)

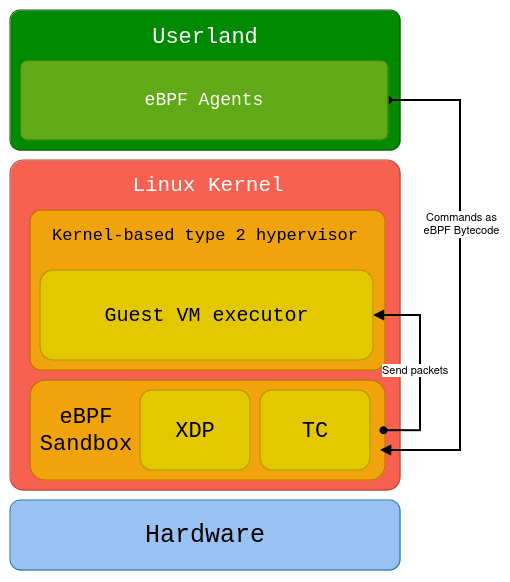
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

Untethered + Unsandboxed code execution haxx as root on iOS 14 - iOS 14.8.1.

A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side

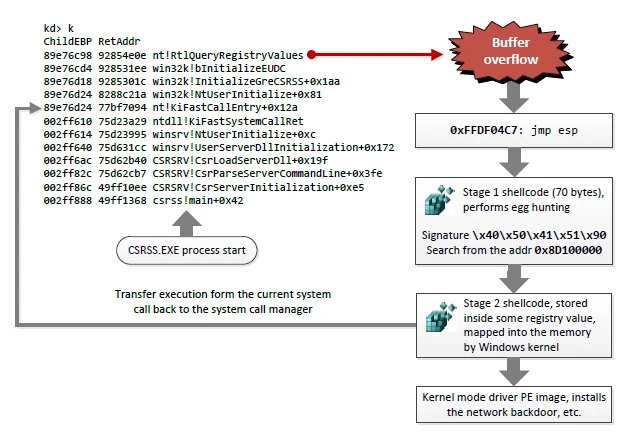
Kernel rootkit, that lives inside the Windows registry values data