metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…

Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

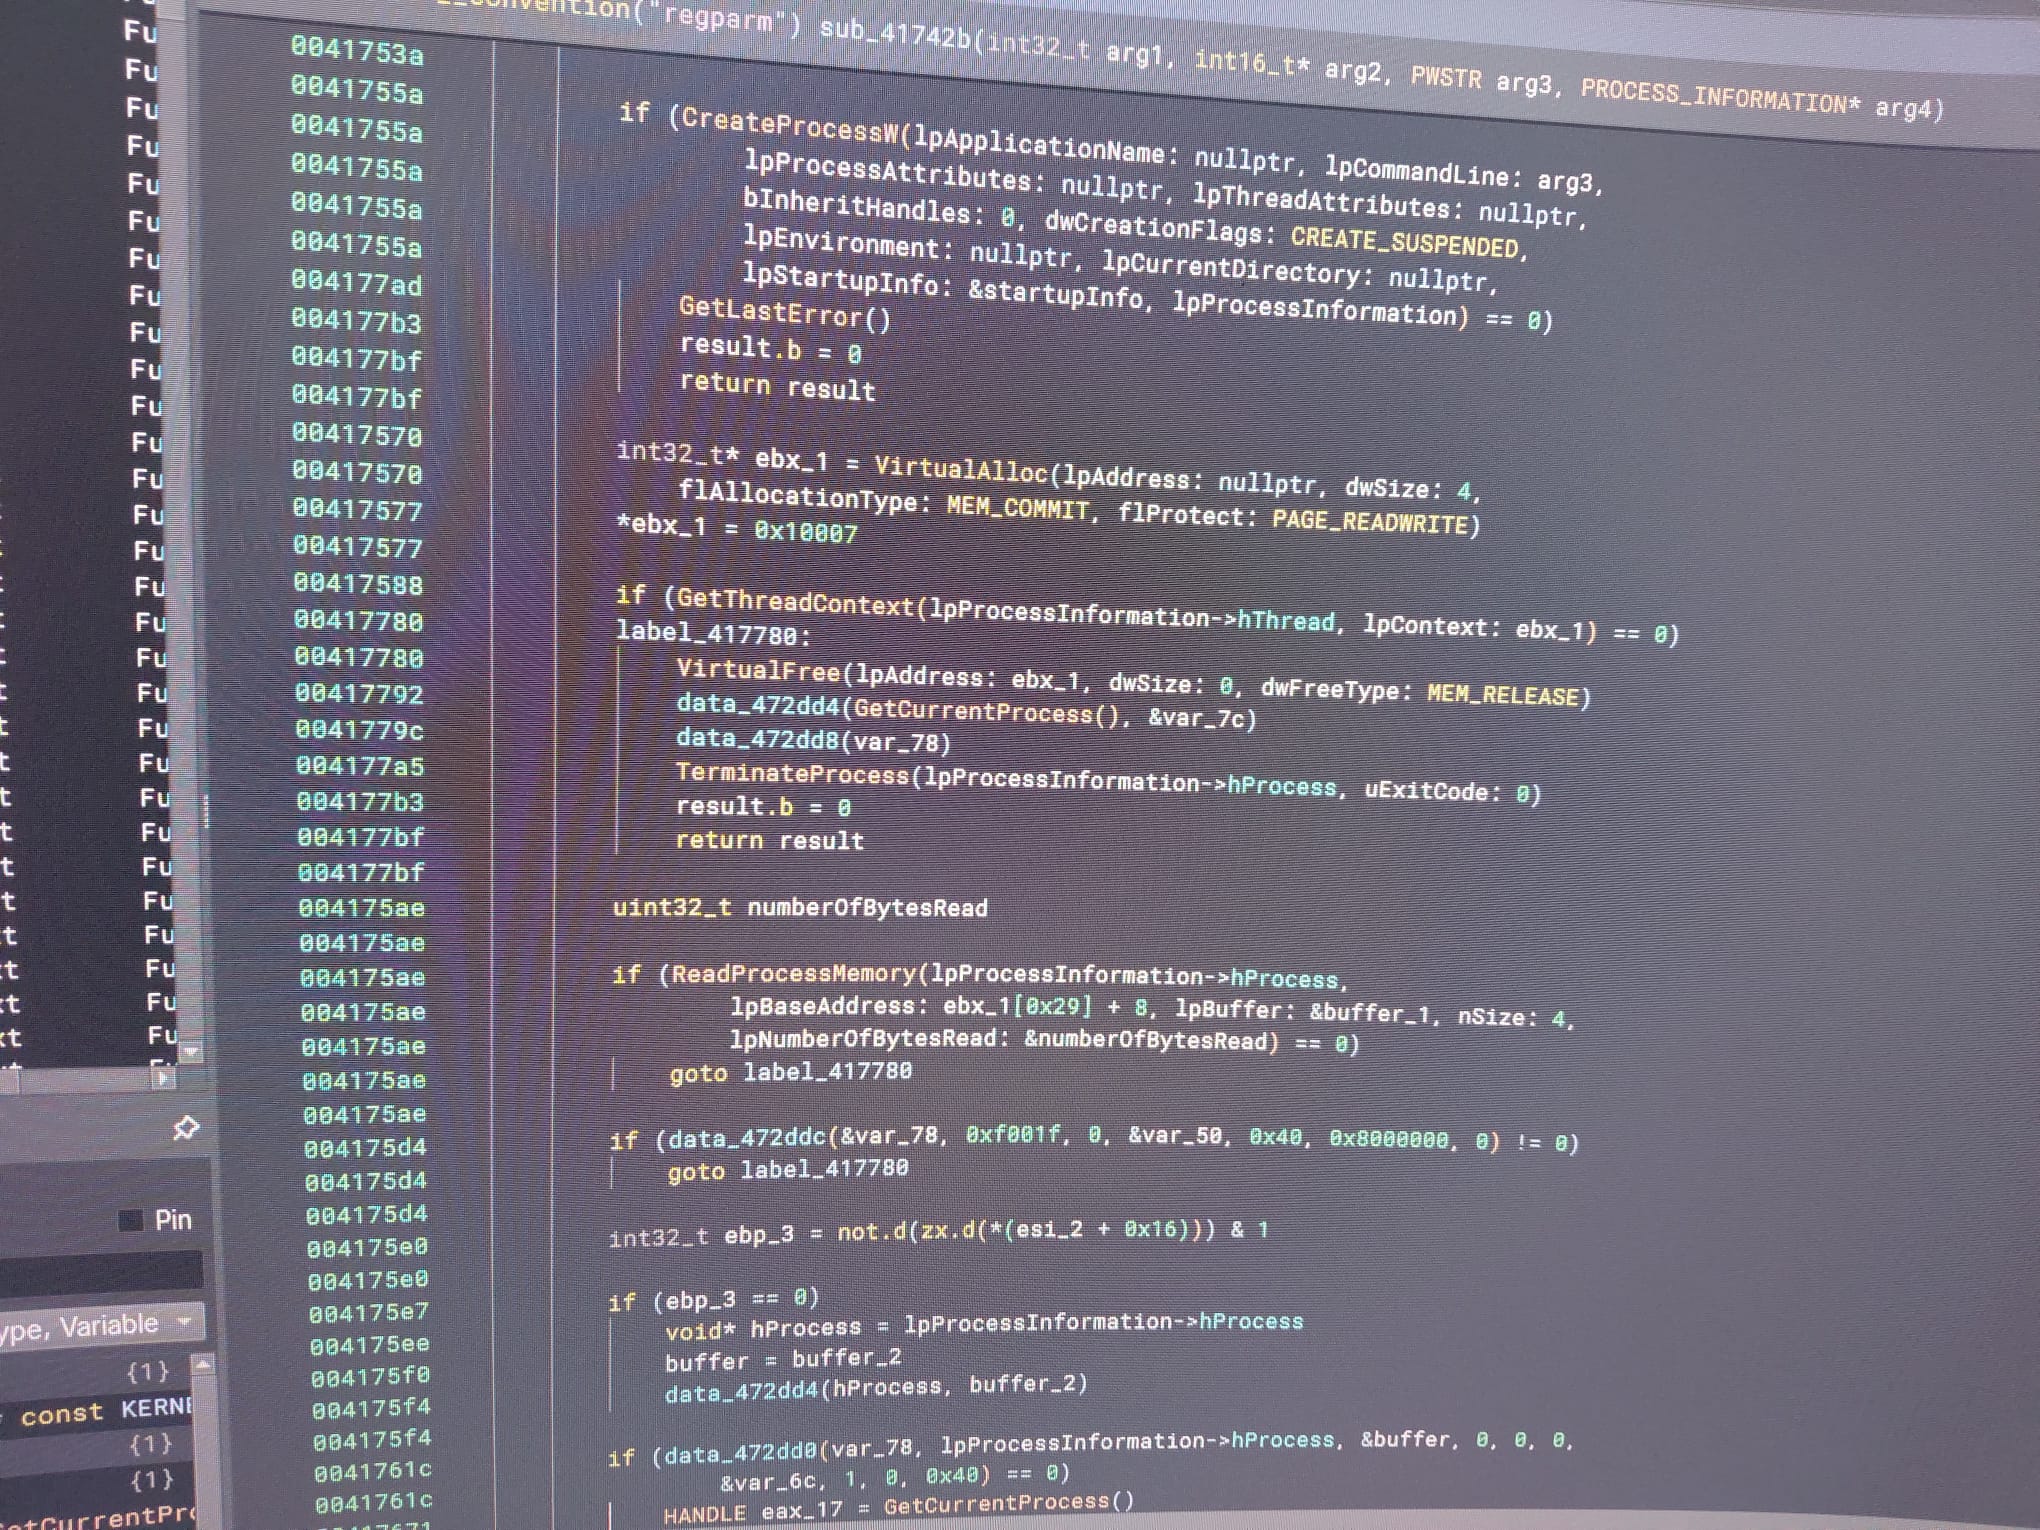
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

CVE-2026-33017 - Langflow Unauthenticated RCE Exploit

UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

Exploit for Apache Kyuubi path traversal (CVE-2026-52680) achieving unauthenticated arbitrary file write and code execution via profile.d shell…

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…