
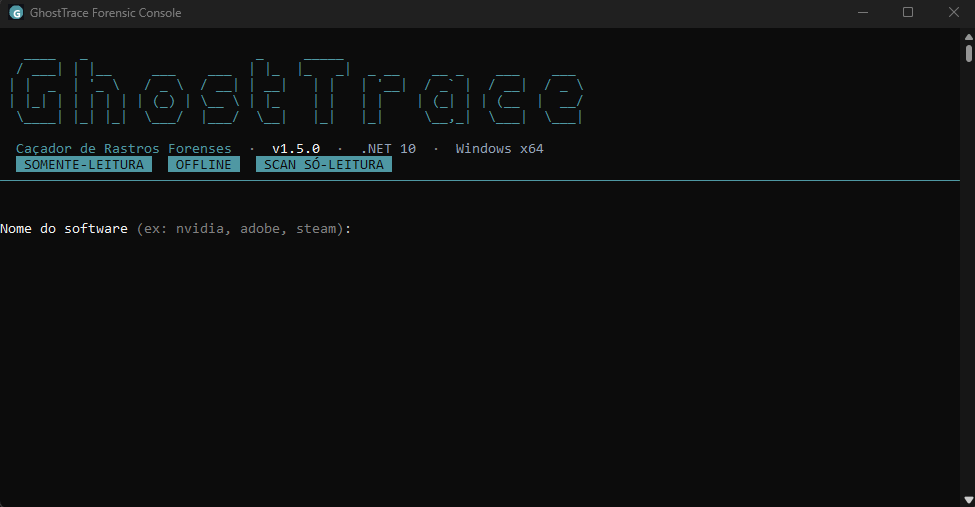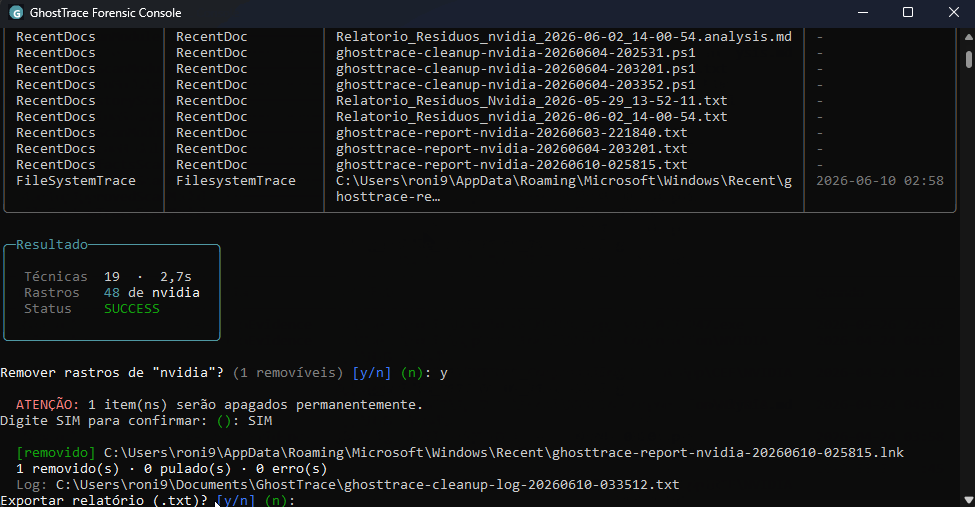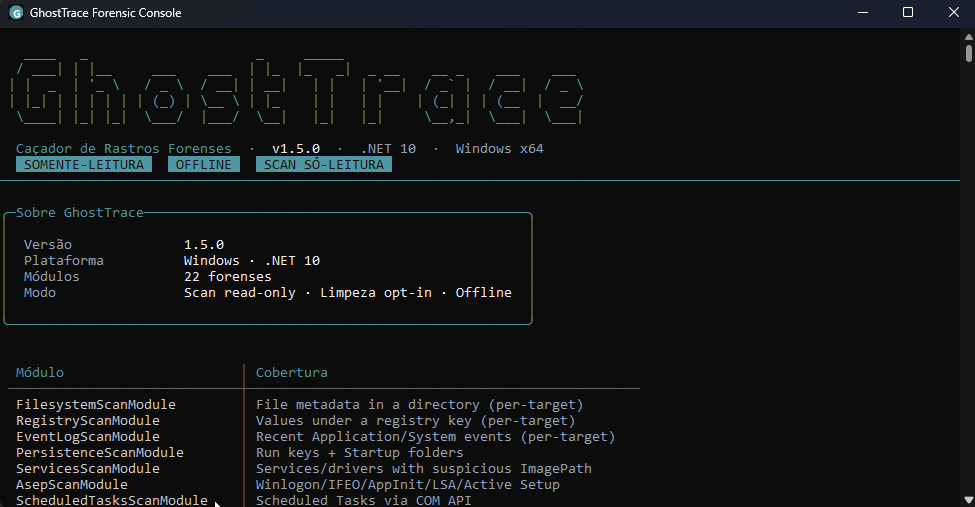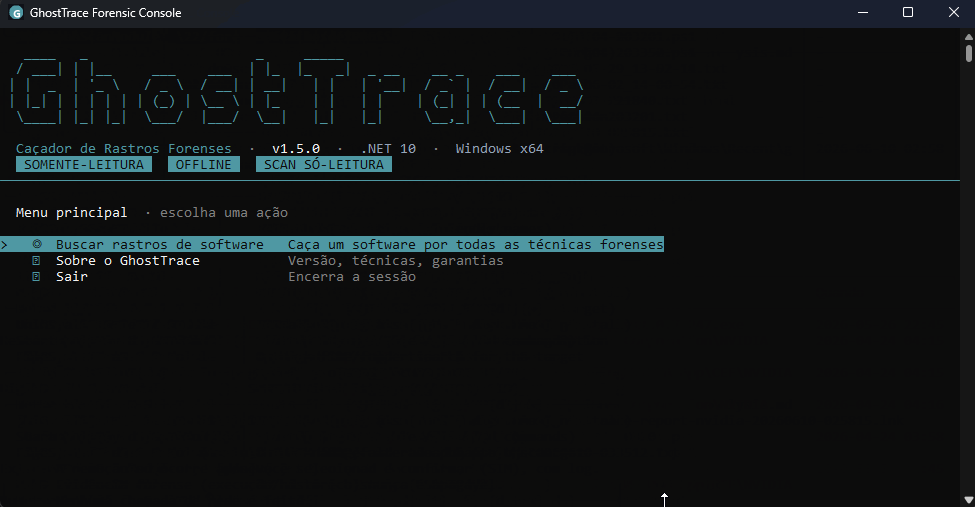
GhostTrace
 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
digital-forensicsforensicsincident-response+3
devzinh/ghosttraceRead-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
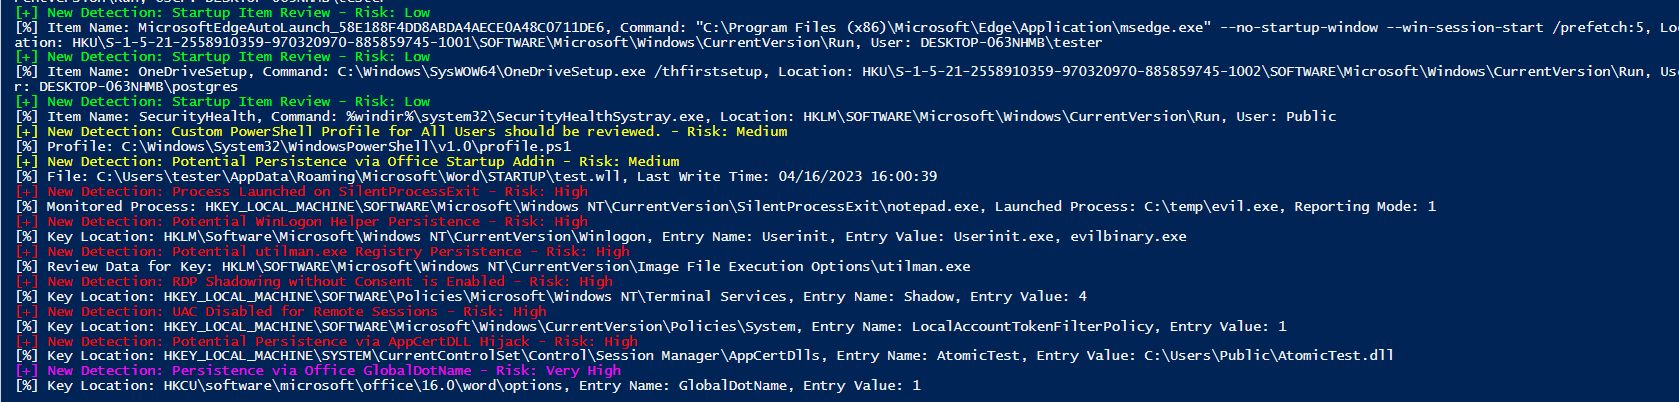 joeavanzato/trawler
PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
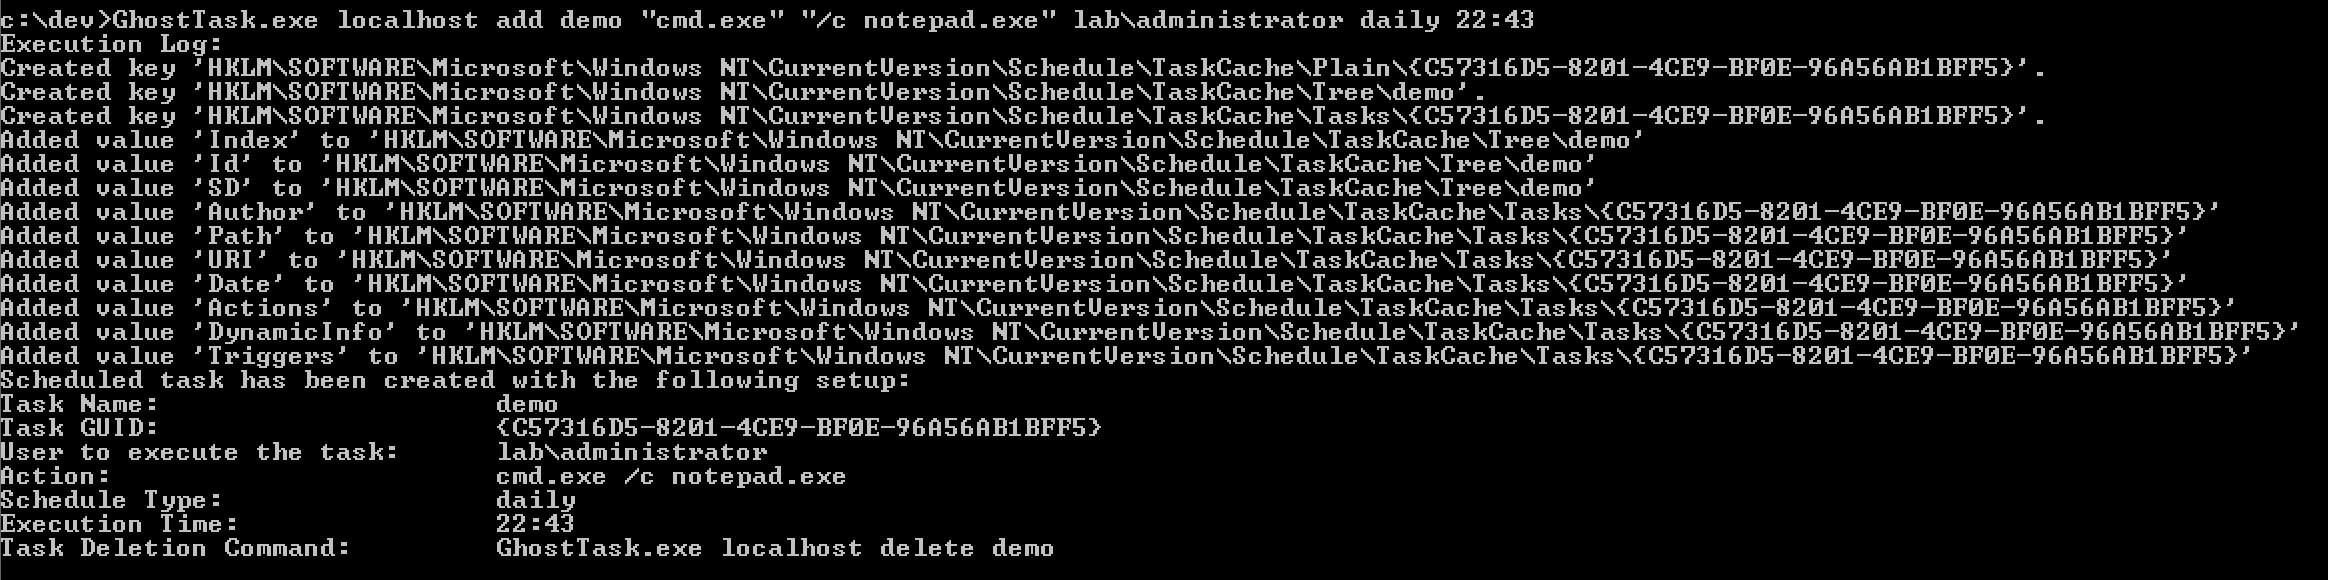 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 0xthirteen/sharpstay
.NET tool for installing Windows persistence via registry keys, scheduled tasks, services, WMI events, COM hijacks, and LNK backdoors, supporting…
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
 mandiant/sharpersist
C# toolkit for establishing and managing Windows persistence via registry keys, scheduled tasks, services, startup folders, KeePass configs, and…
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 0xthirteen/staykit
Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…
 dagrz/aws_pwn
A collection of AWS penetration testing junk