
kli-ex
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
binary-analysiscryptographydefensive-tools+4
34
gmh5225/kli-exExtended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
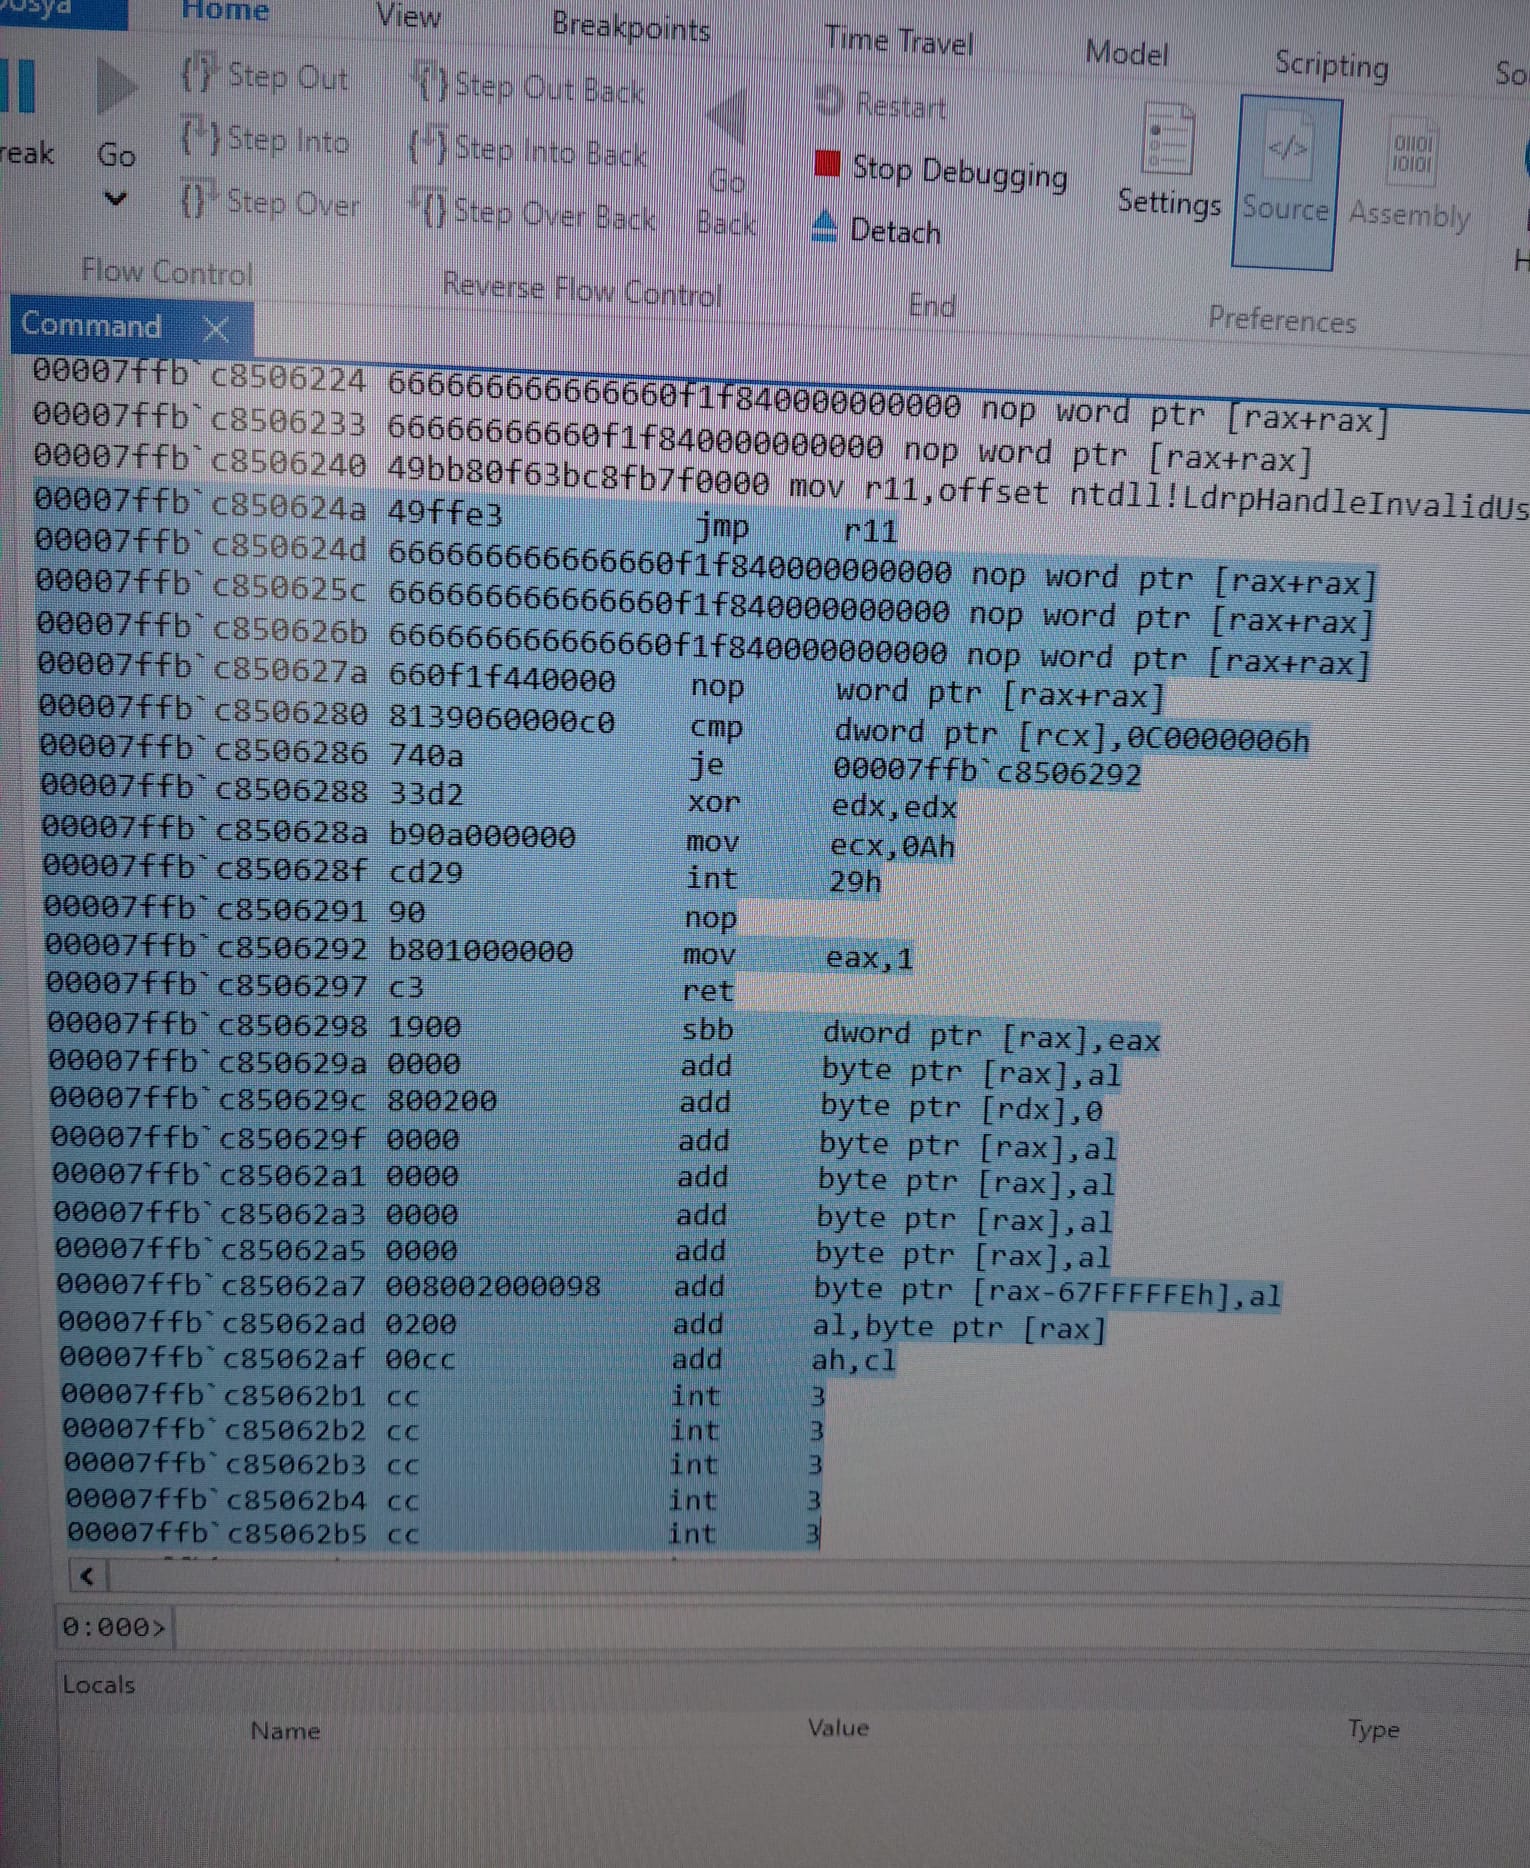 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.