

AdStrike
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
ai-securitycommand-and-controlexploitation+7
capture0x/adstrikeAI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 xforcered/scmkit
Source Code Management Attack Toolkit
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
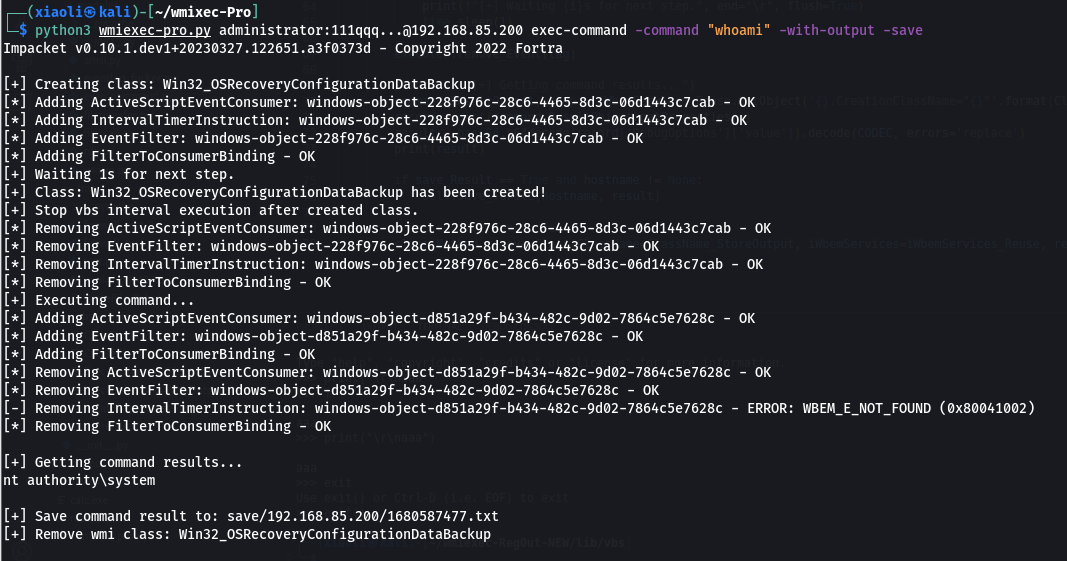 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 synacktiv/extloader
A chromium extension exploitation toolkit
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
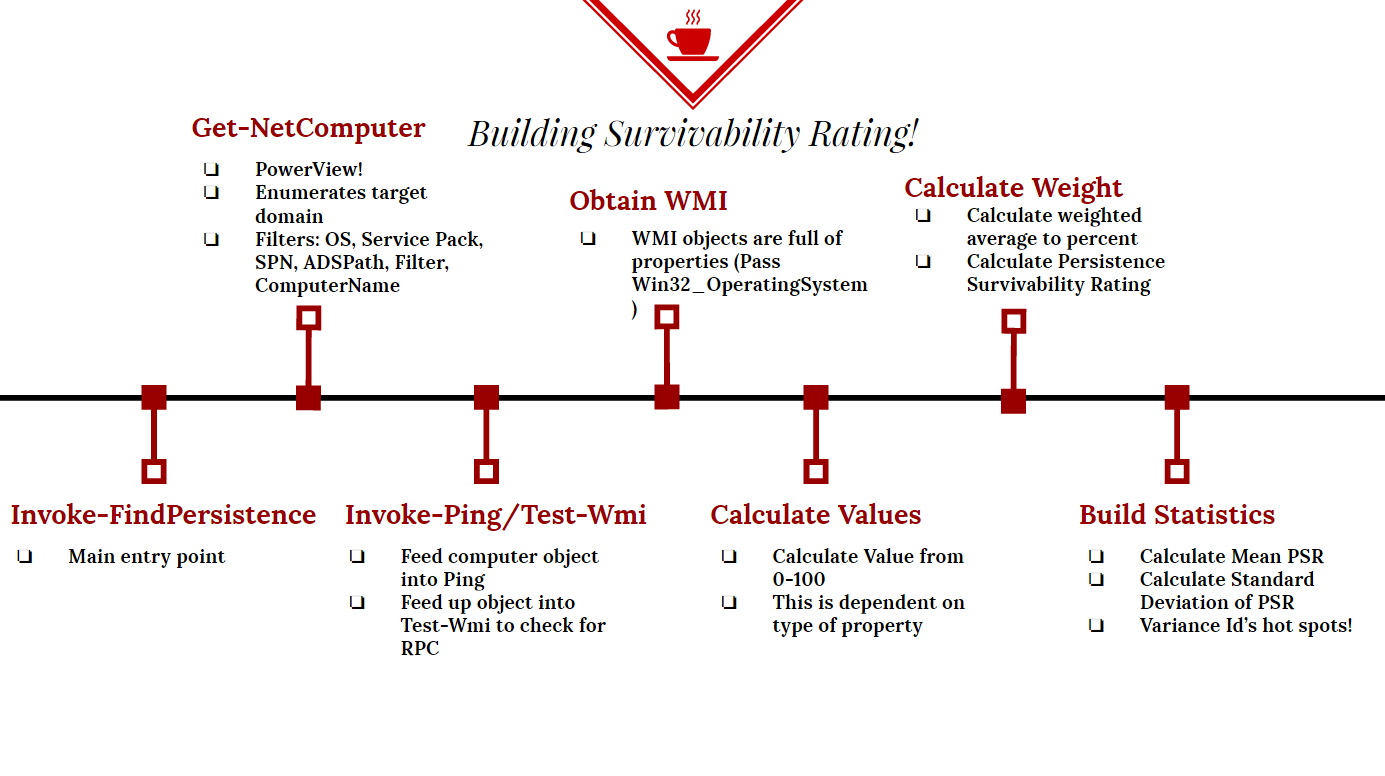 killswitch-gui/persistence-survivability
Powershell Persistence Locator
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
 sw4mpf0x/powerlurk
Malicious WMI Events using PowerShell
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources