

KDU
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k
hfiref0x/kduWindows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
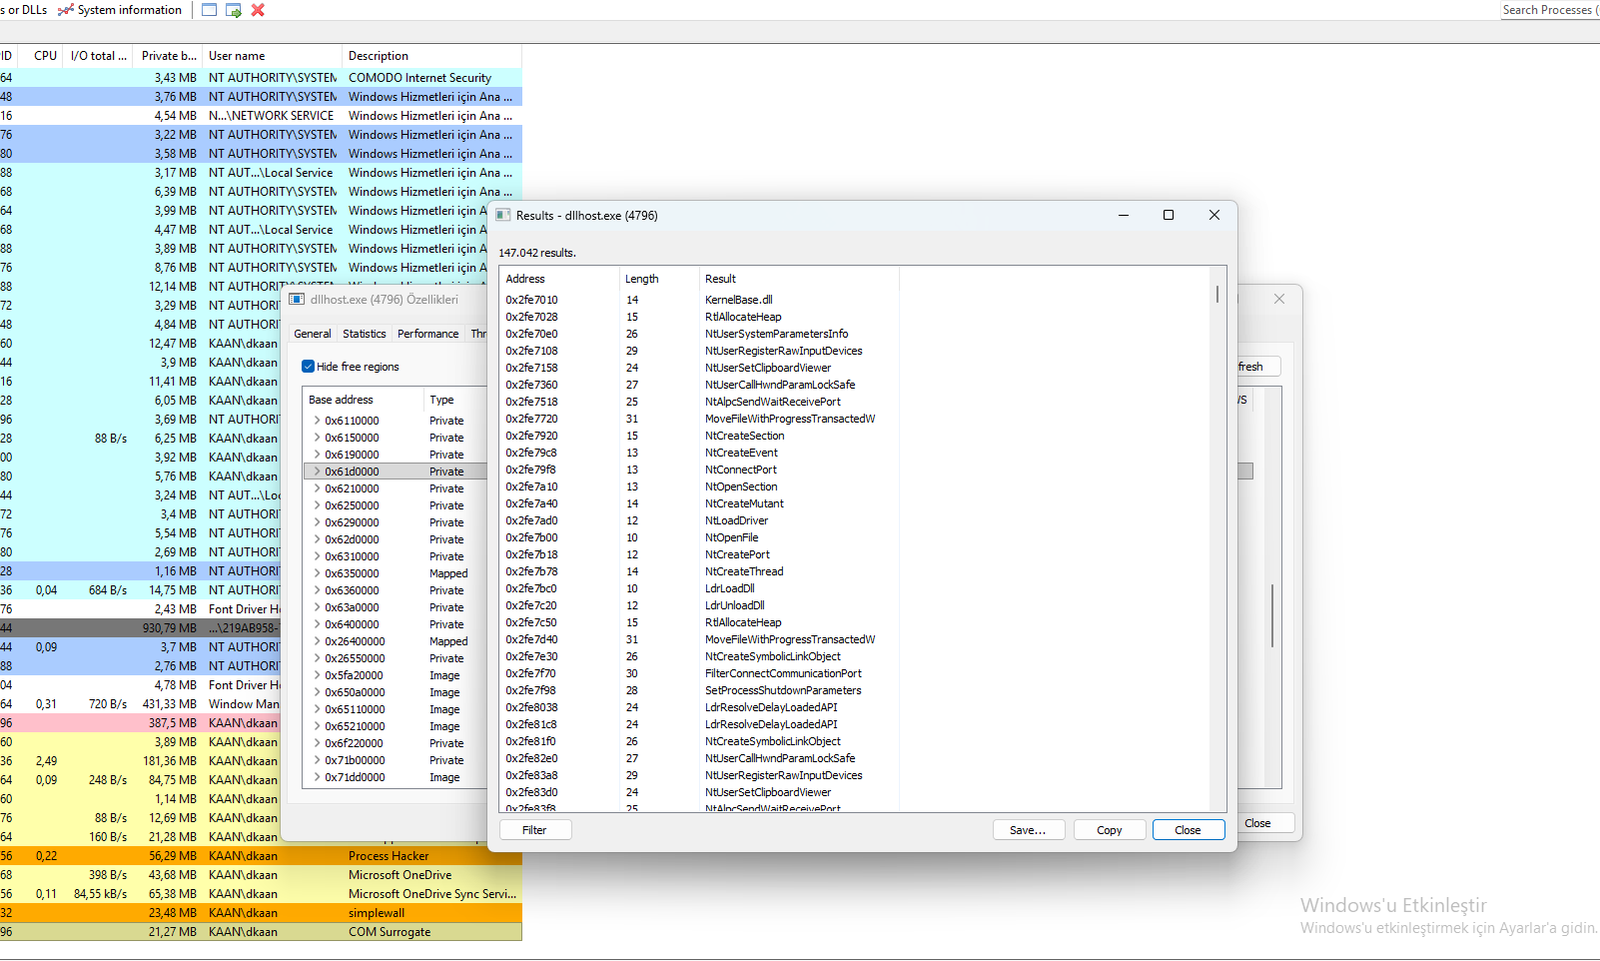 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 netbiosx/checklists
Red Teaming & Pentesting checklists for various engagements
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
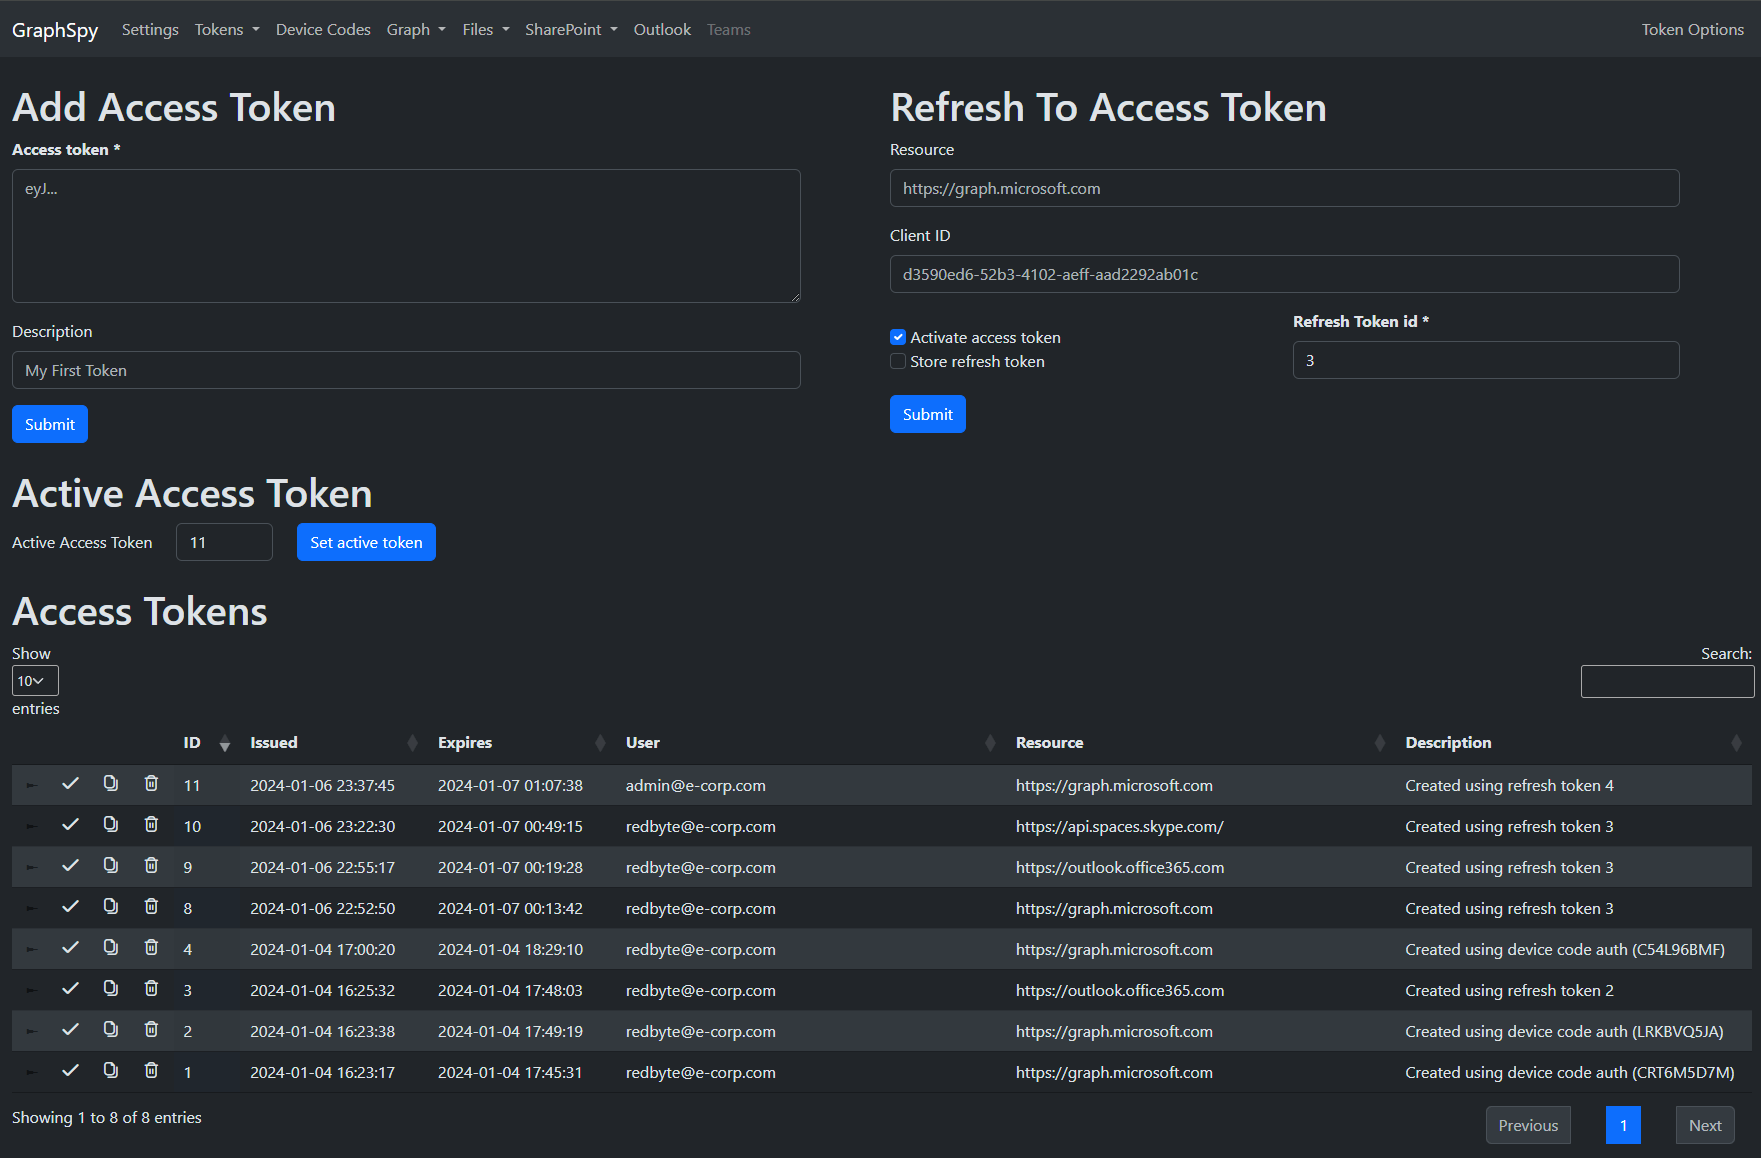 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 asekon/rootkit
A rootkit for ubuntu-16.04.6 (Linux 4.4). Can hide a process, give root access and hide itself
 malwaretech/edr-preloader
An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
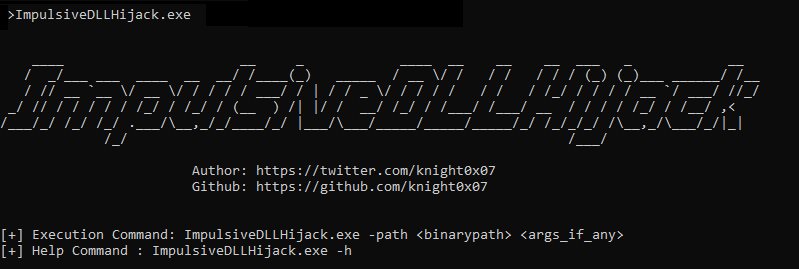 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…