
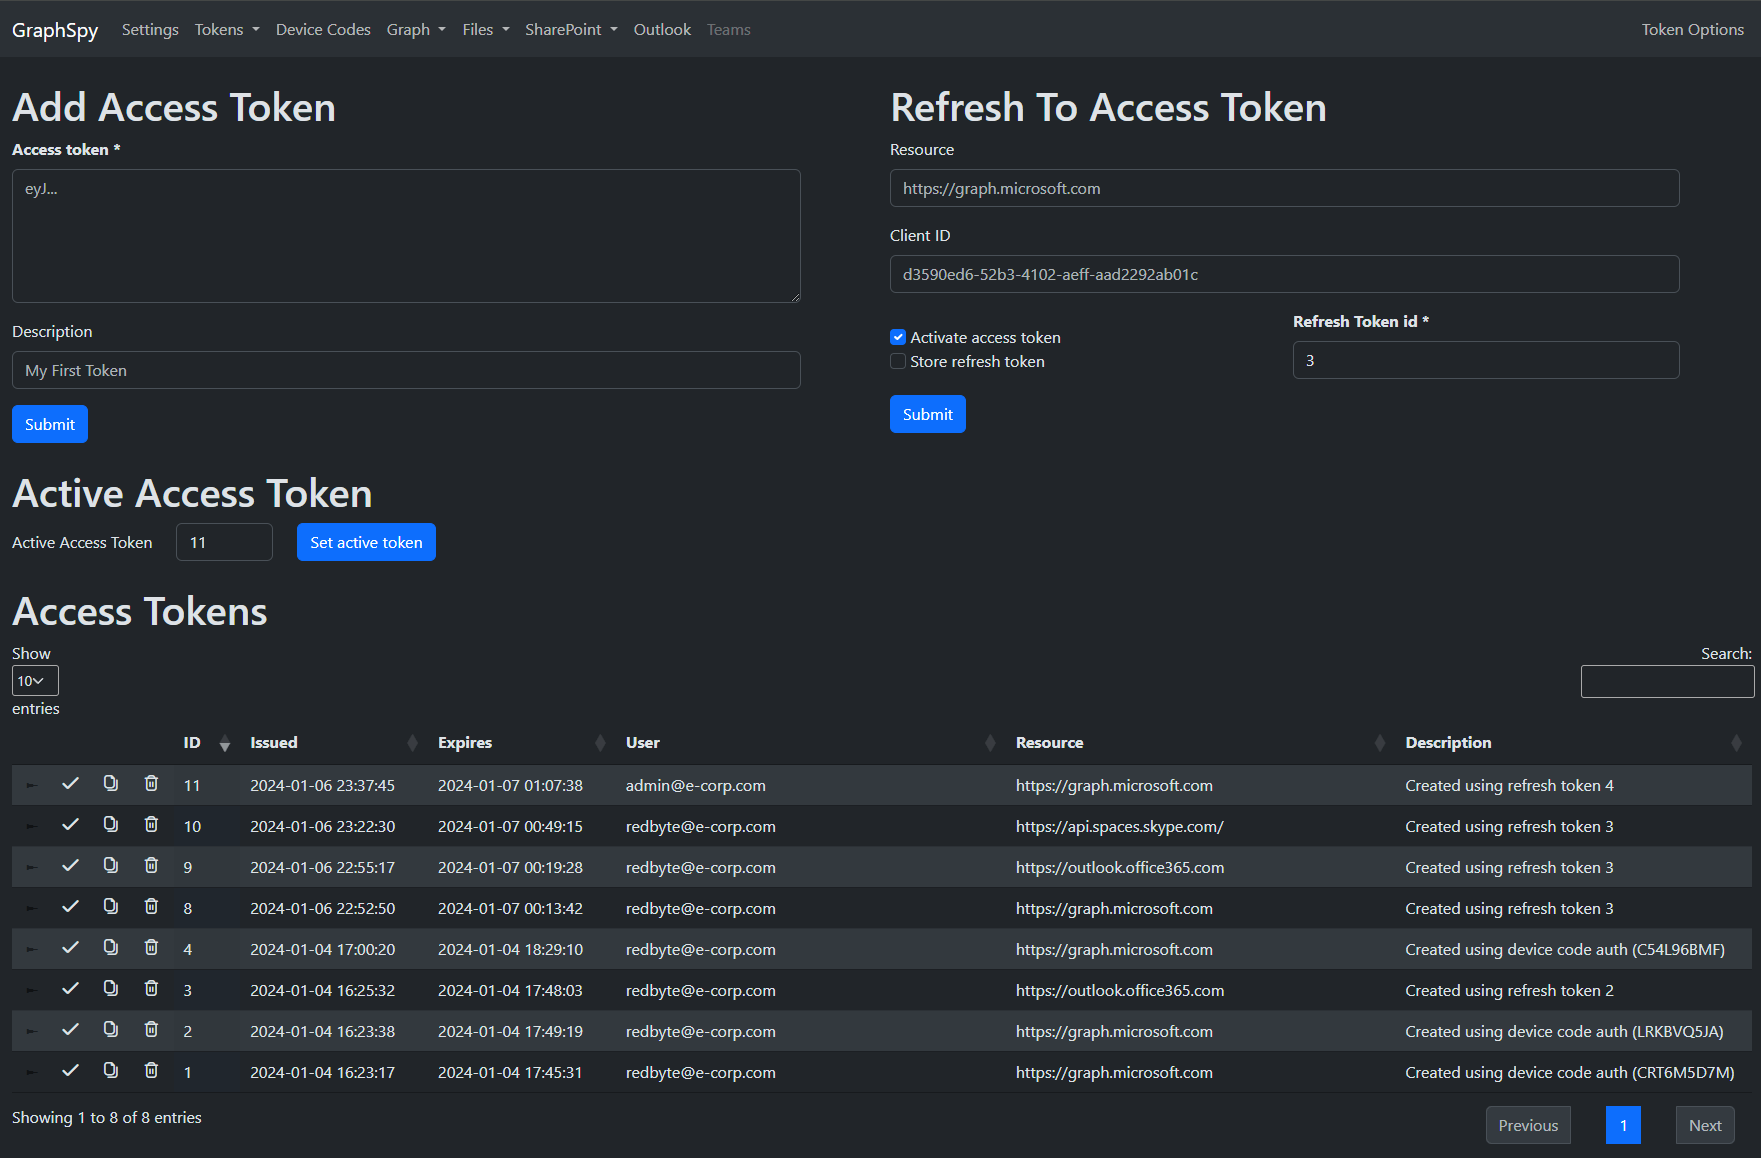
GraphSpy
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
authenticationcloud-securitydata-exfiltration+6
1.4k1 month ago
redbyte1337/graphspyInitial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 ash1996x/cve-2025-54914-poc
Exploit for CVE-2025-54914 in Azure Networking, creating malicious routes with evasion, persistence, multi-target scanning, and reporting for…